
Py-RDP-Patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…

Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…

Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/

SSH spreading made easy for red teams in a hurry

Windows Session Hijacking via COM

Check for valid credentials across a network over SMB

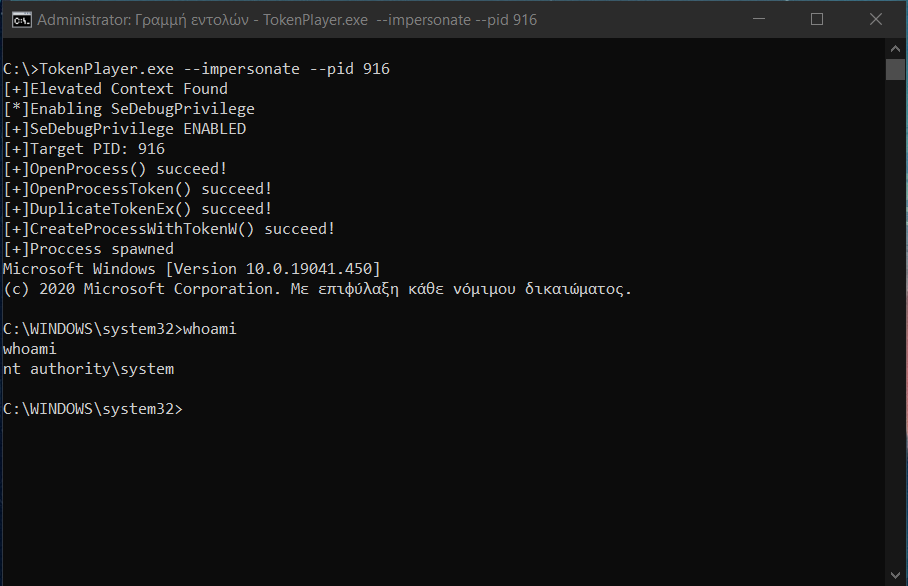
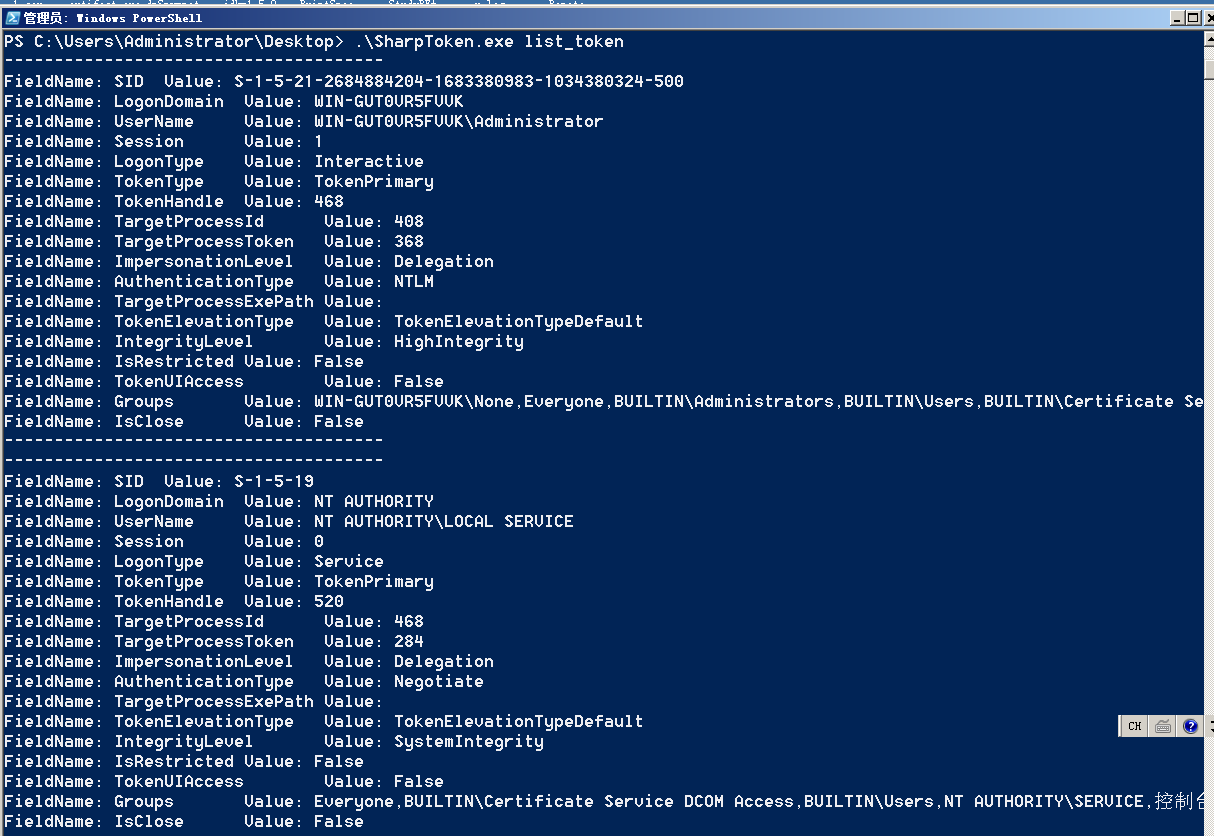
Manipulating and Abusing Windows Access Tokens.

.Net port of the remote SAM + LSA Secrets dumping functionality of impacket's secretsdump.py

The Shadow Attack Framework

Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…

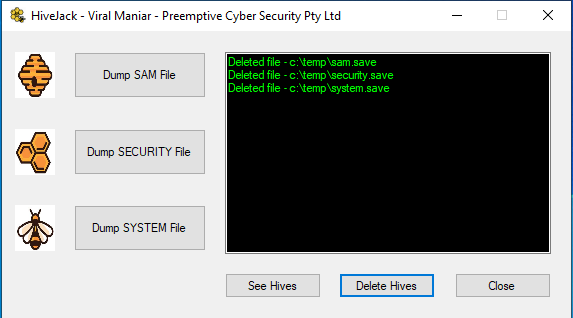
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…

Targeted evil twin attacks against WPA2-Enterprise networks. Indirect wireless pivots using hostile portal attacks.

A windows token impersonation tool

HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386

PowerSploit - A PowerShell Post-Exploitation Framework

RunasCs - Csharp and open version of windows builtin runas.exe

Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…

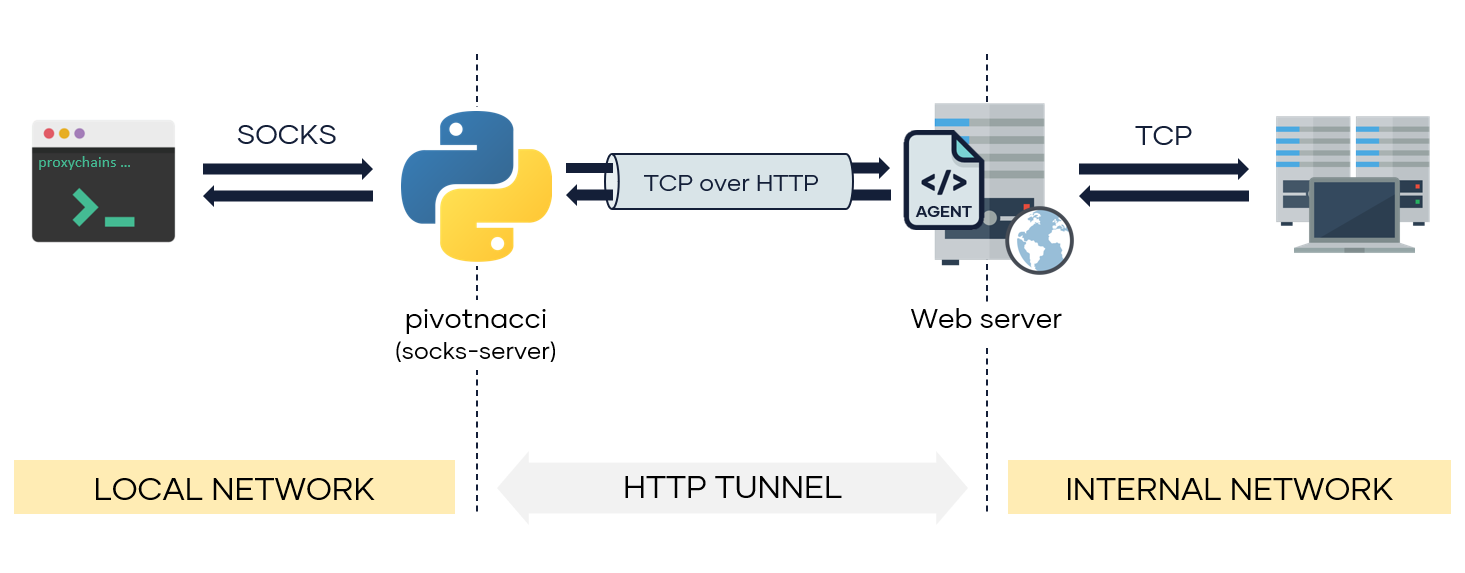
A tool to make socks connections through HTTP agents