metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

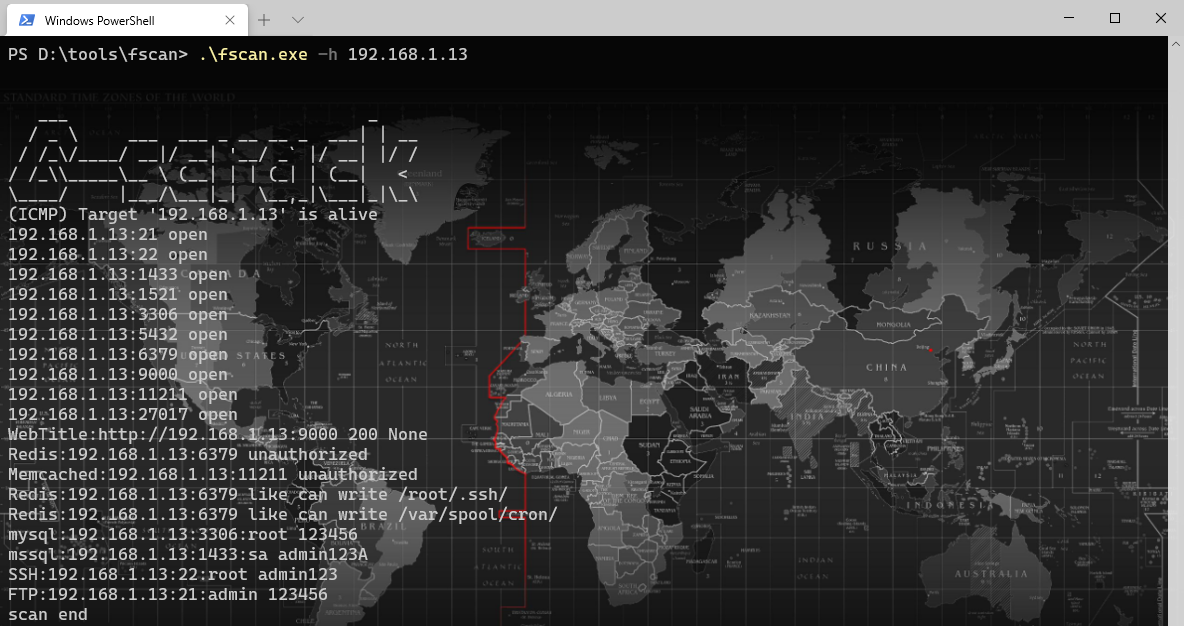
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

This repo documents a vulnerability in Siri Shortcuts and Shared Web Credentials (SWC) allowing malformed payloads to persistently execute, trigger…

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.

Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier

Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…

CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13

Proof-of-concept for CVE-2026-4480, a Samba print job name command injection vulnerability. Demonstrates exploitation via malicious print job names…

Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…

Curated repository of CVEs with PoCs, articles, and detailed descriptions for vulnerability research and exploitation.

Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…

Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…

Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…

Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…

Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…

Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.