

CVE-2026-18322
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
exploitationlabs-practicepapers-research+7
i3it/cve-2026-18322Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 bahartanir/wp2shell-scanner
CVE-2026-63030 / CVE-2026-60137 - WordPress pre-auth RCE scanner
 anggatechi/mass-scanner-cve-2026-3891
Python-based mass scanner for validating a specific WordPress AJAX behavior in authorized environments, supporting URL normalization, endpoint…
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 cved-sources/cve-2019-9978
Docker container providing a vulnerable environment for CVE-2019-9978 (WordPress Social Networks Auto Poster RCE) for security training and…
 ivanbg2004/odh-bricksbuilder-cve-2024-25600-thm
OD&H's scanner for CVE-2024-25600 vulnerability in the Bricks Builder WordPress plugin. For use in Try Hack Me (THM) environments.
 heisenbergh4x/cve-2008-1930
CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 hassham1/cve-2026-87902
WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
 hassham1/cve-2026-89274-wp-recipe-maker-poc
Docker validation lab and Python PoC for CVE-2026-89274, proving arbitrary shortcode execution in WP Recipe Maker <= 10.8.1 via rating-comment…
 codeb0ssx/ultimate-wp2shell
wp2shell — Pre-authentication RCE in WordPress Core (CVE-2026-60137 + CVE-2026-63030). Chains an SQL injection in author__not_in with batch-route…
 imbios/lab-cve-2025-3515
CVE-2025-3515 WordPress lab for Drag and Drop Multiple File Upload for CF7: Dockerized PoC & Nuclei testing
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
 dinosn/givewp-cve-2026-82222-rce-lab
Authorized Docker lab and clean PoC for validating CVE-2026-82222 RCE in GiveWP 4.16.5.1 and the 4.16.7.2 fix.
 abraxas/cve-2026-81294
Proof-of-concept and lab reproduction for CVE-2026-81294, an unauthenticated privilege escalation in the WordPress Authorizer plugin via unverified…
 abraxas/cve-2026-81648
Proof-of-concept exploit and lab for CVE-2026-81648, an unauthenticated arbitrary file deletion flaw in the WordPress CryptoPayment Gateway plugin.
 abraxas/cve-2026-19952
Proof-of-concept and disclosure pack for CVE-2026-19952, an unauthenticated arbitrary file deletion in the WordPress Frontend Admin plugin, with lab…
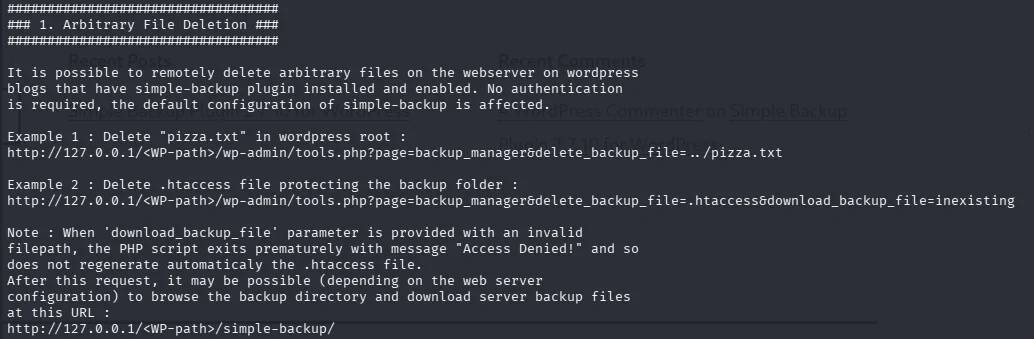 capivara-research/wordpress-path-traversal-cve-2019-11447
Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…