
ninjasworkout
 effortlessdevsec/ninjasworkout
Deliberately vulnerable Node.js web application containing 19+ security bugs (XSS, SSRF, Prototype Pollution, RCE) for hands-on penetration testing…
educationlabs-practicepenetration-testing+2
98
effortlessdevsec/ninjasworkoutDeliberately vulnerable Node.js web application containing 19+ security bugs (XSS, SSRF, Prototype Pollution, RCE) for hands-on penetration testing…
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 syriusbughunt/cve-2018-14667
All about CVE-2018-14667; From what it is to how to successfully exploit it.
 10t4/poc-fix-jenkins-rce_cve-2024-23897
on this git you can find all information on the CVE-2024-23897
 vigilante-1337/cve-2024-11635
The WordPress File Upload plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 4.24.12 via the…
 threatradarai/trai-001-critical-rce-vulnerability-in-apache-parquet-cve-2025-30065-simulation
A CVSS 10.0-rated vulnerability in the parquet-avro Java module allows remote code execution via unsafe deserialization when parsing schemas. Tracked…
 mycompanyorganization/react2shell-kingdom
"Once upon a time, the Castle of Reactland trusted all Flight messages... until The Imposter arrived." A storytelling CVE-2025-55182 (React2Shell)…
 j3kz/cve-2021-44228-poc
Self-contained lab environment that runs the exploit safely, all from docker compose
 wwwiesel/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
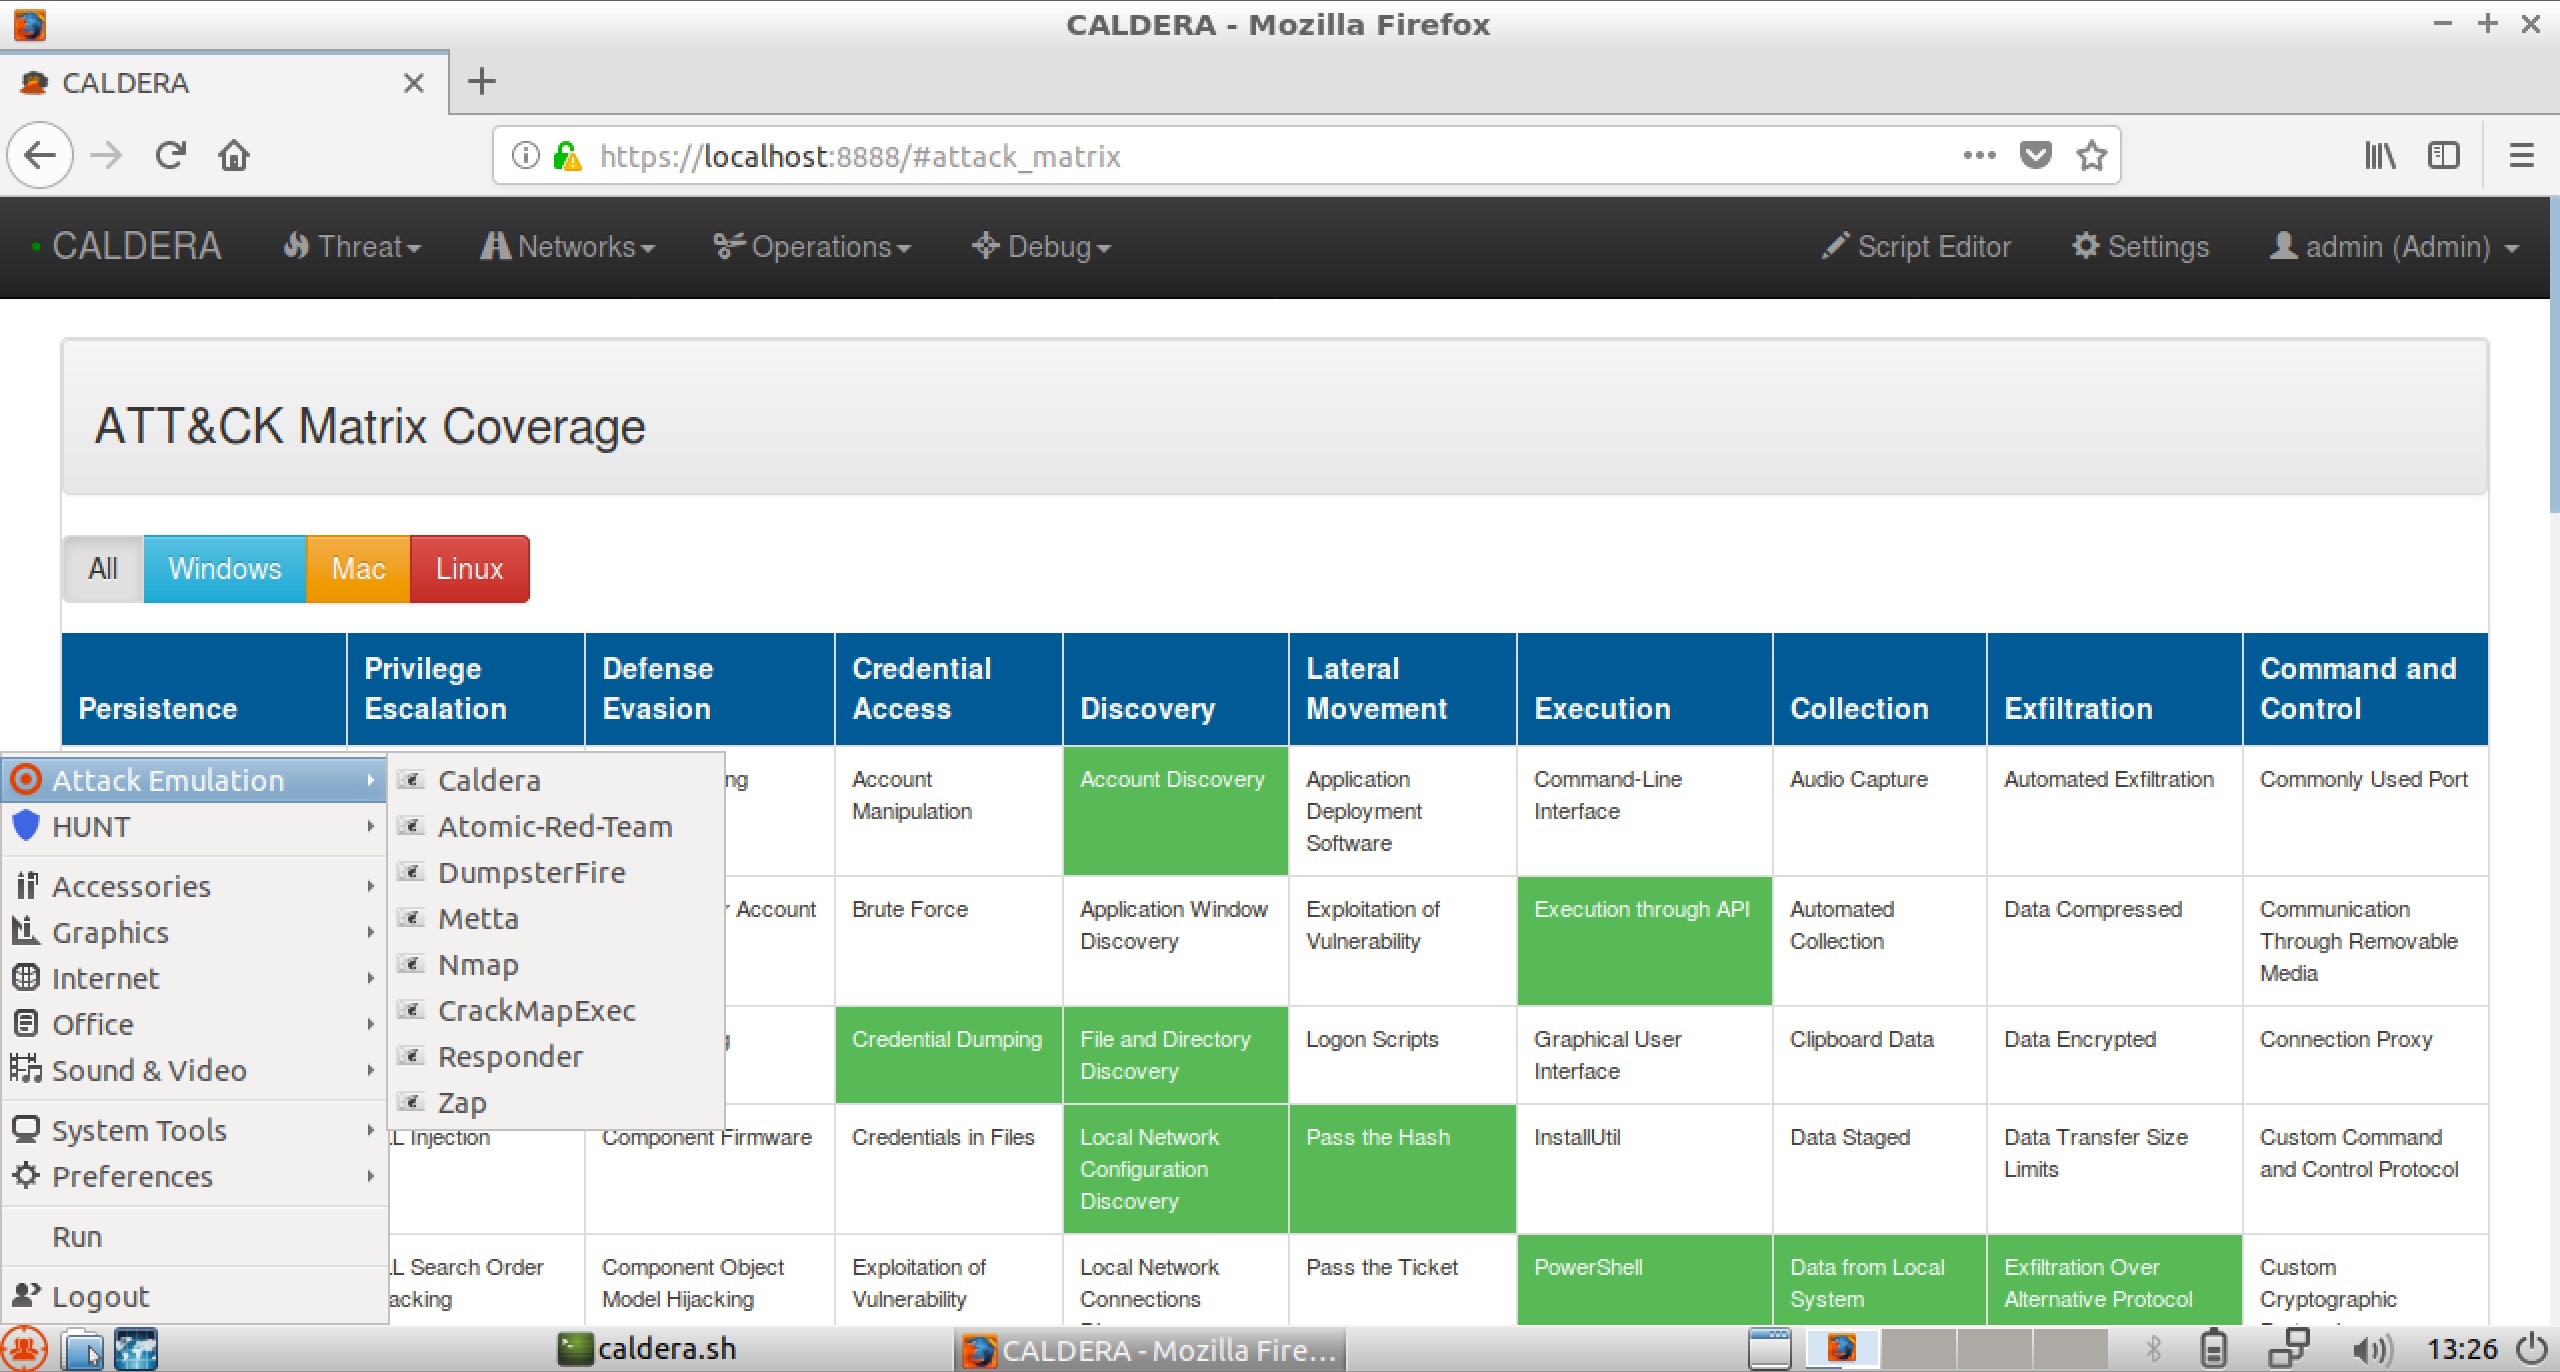 redhuntlabs/redhunt-os
Virtual Machine for Adversary Emulation and Threat Hunting
 hydragyrum/cve-2021-41773-playground
Some docker images to play with CVE-2021-41773 and CVE-2021-42013
 biitts/cve-2026-44789-n8n-prototypepollution-rce
CVE-2026-44789 — n8n <1.123.43 HTTP Request pagination prototype pollution to RCE (NODE_OPTIONS runner-spawn gadget). Lab + automated PoC, verified…
 immersive-labs-sec/proxylogon
Chaining CVE-2021-26855 and CVE-2021-26857 to exploit Microsoft Exchange
 av4nth1ka/jinjava-cve-2026-25526-poc
Step-by-step exploit harness and proof-of-concept for CVE-2026-25526 in Jinjava, demonstrating file read, file creation, and info disclosure with…