
CVE-2026-17532-lab
 kalhoralireza/cve-2026-17532-lab
Docker lab demonstrating CVE-2026-17532, an unauthenticated reflected XSS in Seraphinite Accelerator that chains to RCE via admin session, with…
educationexploitationlabs-practice+3
kalhoralireza/cve-2026-17532-labDocker lab demonstrating CVE-2026-17532, an unauthenticated reflected XSS in Seraphinite Accelerator that chains to RCE via admin session, with…
 r4y-br/cve-2022-22963
Python automation script that reproduces CVE-2022-22963, a critical SpEL injection in Spring Cloud Function, enabling reverse shell in authorized lab…
 ahmedshamsddin/cve-2025-55182
Python exploit for CVE-2025-55182 in React Server Components, injecting a shell into Next.js 16.0.6 applications. Includes a vulnerable app for…
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 eagle-nett/react2shell-poc-cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Includes a scanner for vulnerable hosts and a…
 experience-rookie/struts-s2-052-deserialization-rce-lab
Proof-of-Concept exploit for Apache Struts S2-052 (CVE-2017-9805) XML Deserialization Remote Code Execution. Created while solving the INE eWPTX…
 liusec/wp-cve-2016-10033
Docker-based lab environment for WordPress <= 4.6 remote code execution via PHPMailer (CVE-2016-10033), including PoC, webshell upload, and reverse…
 ikarolaborda/cve2026-42926
Controlled NGINX HTTP/2 frame injection lab for CVE-2026-42926 patch validation and defensive research
 0xtas/cve-2012-2982
Exploits CVE-2012-2982 in Webmin with a Rust PoC that delivers a configurable TCP reverse shell and optional Netcat listener.
 jakabakos/cve-2023-39362-cacti-snmp-command-injection-poc
Proof-of-concept exploit for CVE-2023-39362, an authenticated command injection in Cacti's SNMP options. Includes a vulnerable Docker environment for…
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 yanghyperdata/logj4_pocshell_cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 asepsaepdin/cve-2021-42013
Exploit for Apache 2.4.49/2.4.50 path traversal and RCE (CVE-2021-42013). Includes Docker setup and script to test path traversal, execute commands,…
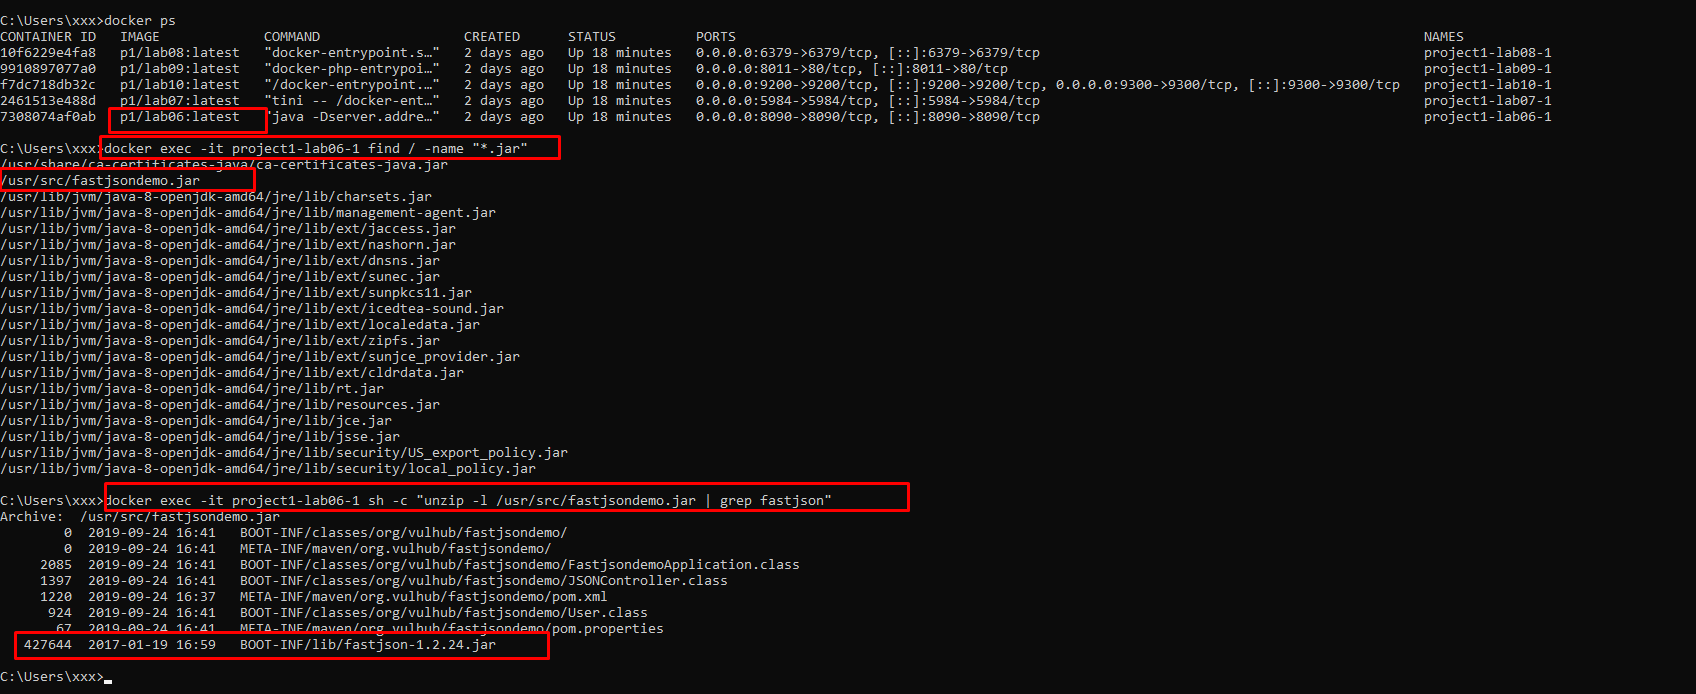 dungsocool/cve-2017-18349
Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 ret0x2a/cve-2025-8625
Proof-of-concept exploit for CVE-2025-8625 targeting WordPress, with Docker-based isolated lab environment and demonstration web shell for…