

mutillidae
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
ctfeducationlabs-practice+3
1.5k
webpwnized/mutillidaeOWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
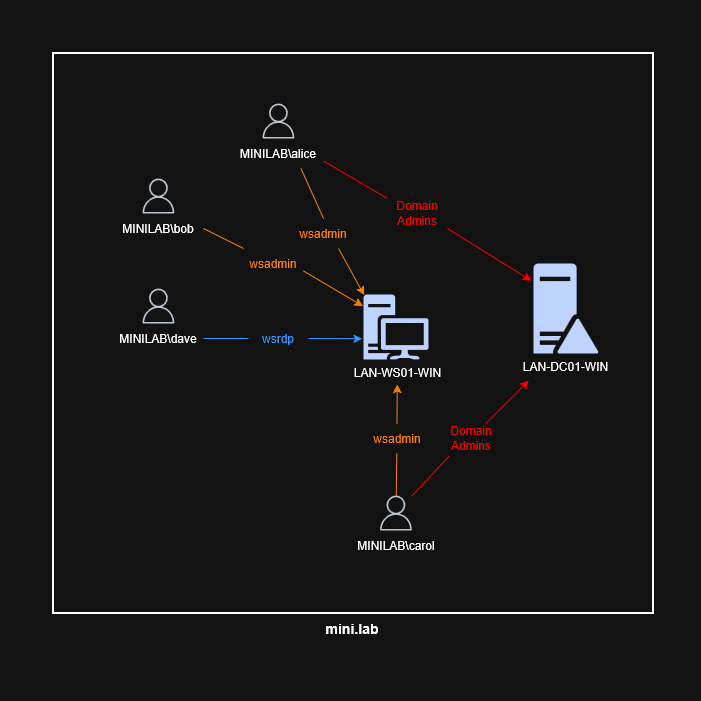 0xmr007/lab4purplesec
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 cved-sources/cve-2018-1273
Docker container for CVE-2018-1273 exploitation lab, part of the Cved vulnerable environment management framework for security training and testing.
 cved-sources/cve-2019-10678
Docker container providing a vulnerable environment for CVE-2019-10678, designed for security training and exploitation practice within the Cved…
 cved-sources/cve-2018-15877
Docker container providing a pre-configured vulnerable environment for CVE-2018-15877, designed for security training and exploit practice within the…
 hackmelocal/cve-2025-31486-simulation
Containerized lab environment to simulate and exploit CVE-2025-31486, a path traversal vulnerability in Vite's development server, with step-by-step…
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 cved-sources/cve-2016-8869
Dockerized vulnerable environment for CVE-2016-8869 (Joomla privilege escalation) used for security training and exploitation practice.
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 digininja/dvwa
Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…
 goultarde/cve-2025-55182-react2shell-lab
CTF lab environment exploiting CVE-2025-55182 (RCE in React Server Components) with vulnerable Next.js blog, detection scripts, and manual exploit…
 cved-sources/cve-2019-9978
Docker container providing a vulnerable environment for CVE-2019-9978 (WordPress Social Networks Auto Poster RCE) for security training and…
 dileepdkumar/layarkacasiber-cve-2021-41773
Docker-based lab environment for practicing CVE-2021-41773 (Apache HTTP Server 2.4.49 path traversal and RCE) with step-by-step setup instructions…
 layarkacasiber/cve-2021-42013
Docker-based lab environment for exploiting CVE-2021-42013 (Apache HTTP Server path traversal and RCE) with step-by-step setup instructions for…
 imbas007/poc-cve-2026-58048
Security research project
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…