
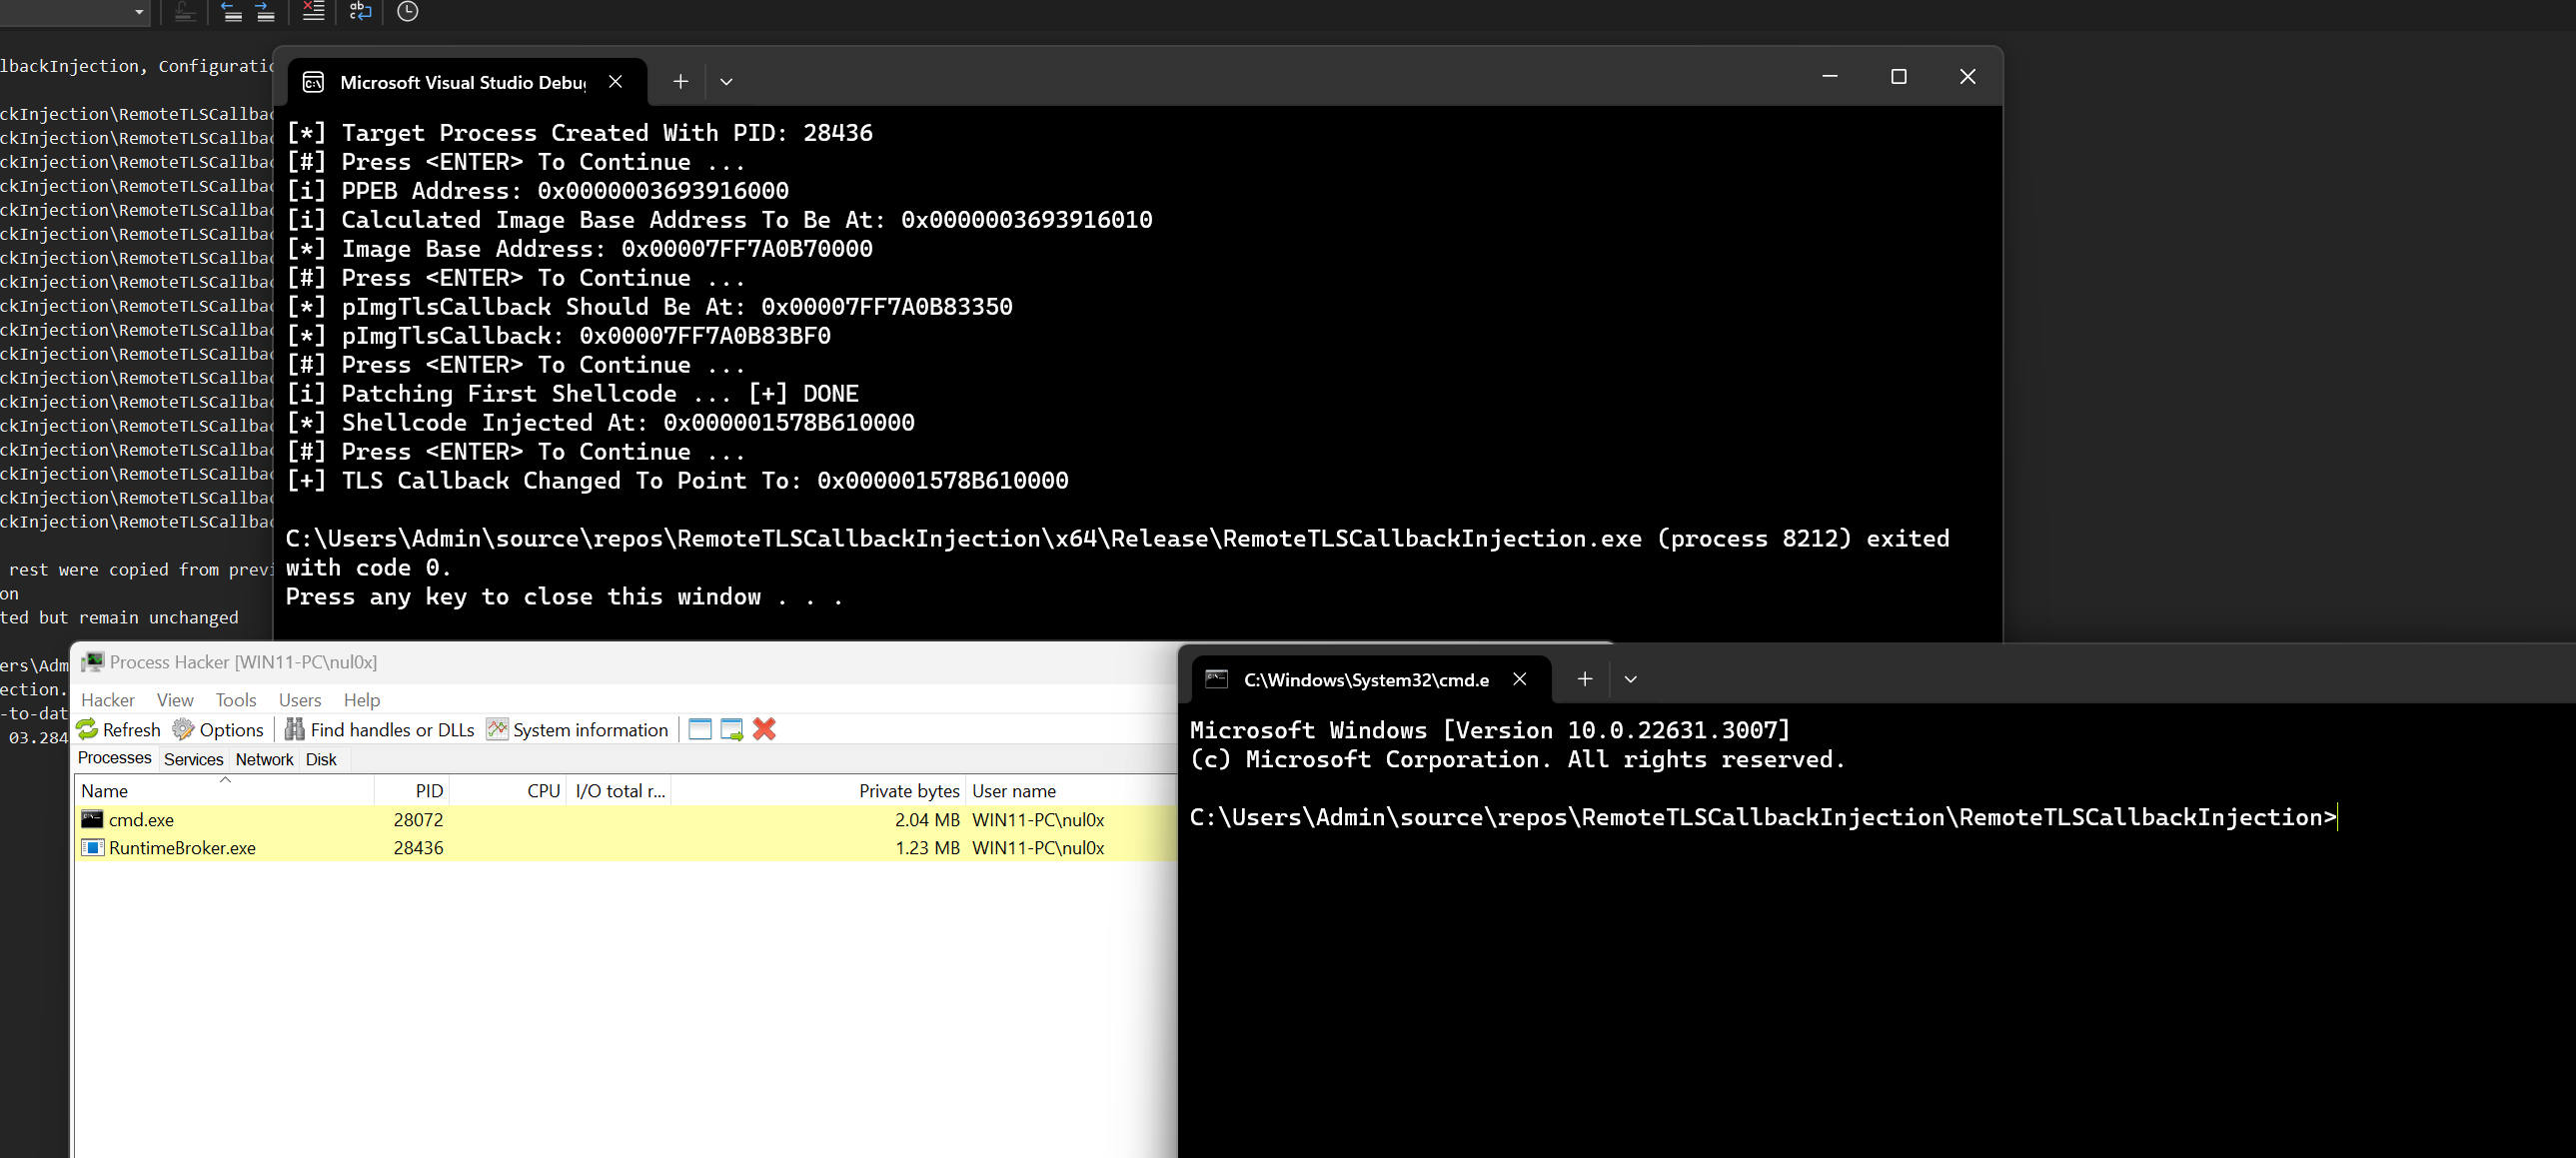
RemoteTLSCallbackInjection
 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
binary-exploitationeducationlabs-practice+1
maldev-academy/remotetlscallbackinjectionUtilizing TLS callbacks to execute a payload without spawning any threads in a remote process
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…