
TarantuBench
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
authentication-authorizationctfeducation+6
34 months ago
trivulzianus/tarantubenchThe full repo of all the labs available as part of the benchmark
 george0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection
POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
 ne0zer01/cve-2024-27198_lab
Docker-based lab for CVE-2024-27198 TeamCity authentication bypass. Includes exploit reproduction, IoC hunting with Sigma/Suricata rules, and…
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
 flame-11/cve-2018-15133-laravel-framework
Reproducible Docker lab for CVE-2018-15133 (Laravel Framework token unserialize RCE) with a known APP_KEY and a /poc route for testing exploit…
 lazybear8372/cve-2023-41898_lab
Walk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…
 lucastran05/cve-2026-29000
Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 lucastran05/cve-2023-48223
Proof-of-concept demonstrating JWT algorithm confusion in fast-jwt library. Includes vulnerable server, token forging script, and verification fix…
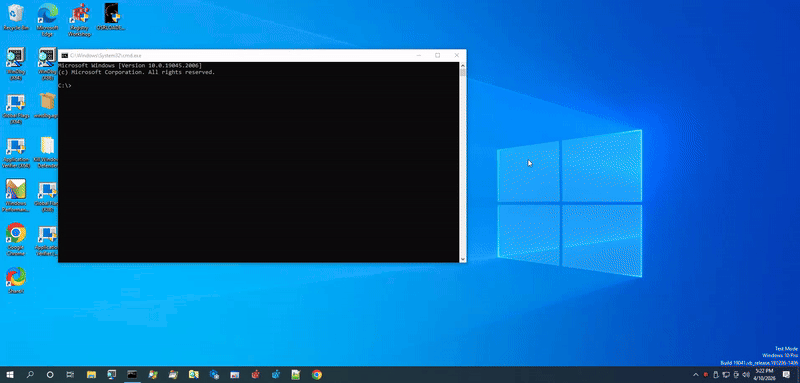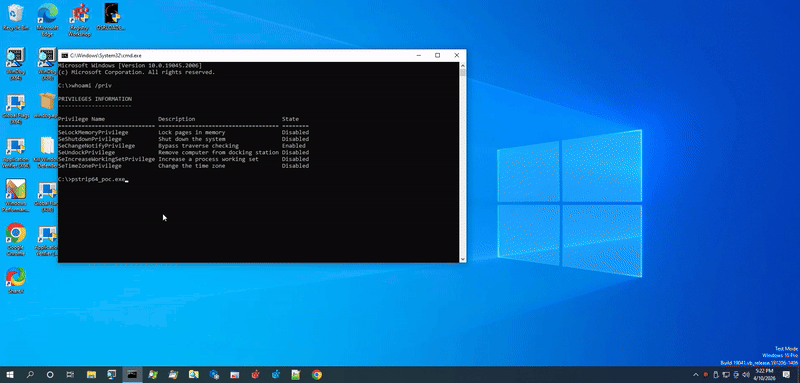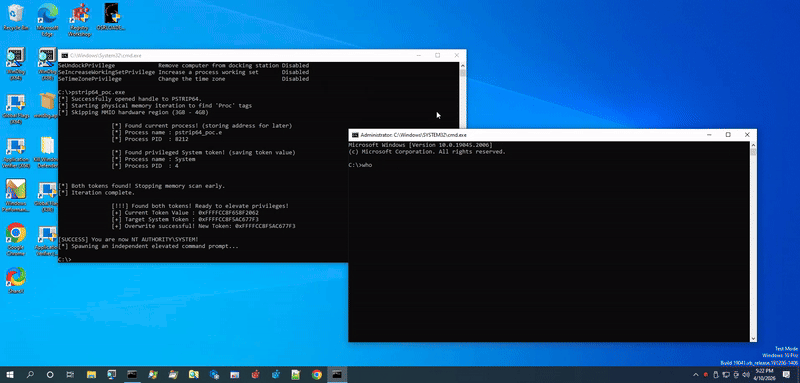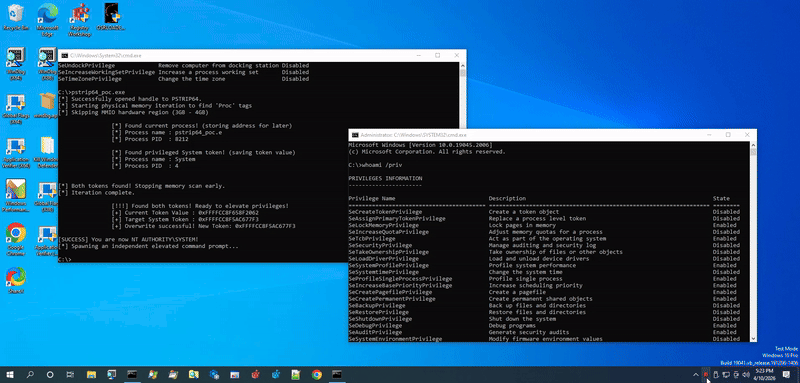 athenasec16/cve-2026-29923
Proof-of-concept exploit for CVE-2026-29923, a BYOVD privilege escalation in pstrip64.sys. Demonstrates physical memory read/write via IOCTL to steal…
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 jeanback1/cve-2025-2304-exploit
Python exploit script for CVE-2025-2304, a mass assignment privilege escalation in Camaleon CMS. Automates CSRF token parsing and role parameter…
 db-ol/cuaharm
Benchmark for evaluating safety risks of computer-using agents, with 104 realistic misuse scenarios across seven malicious categories, supporting…
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
 sabbu143s/cve_2020_35848
CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…
 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
 0xdaeras/flowise-cve-2025-58434-chain-59528
FlowiseAI CVE-2025-58434 & CVE-2025-59528 exploit PoC, demonstrating unauthenticated ATO via reset token leakage, followed by authenticated RCE.…
 jweny/shiro-cve-2020-17523
Analysis of two authentication bypass techniques for Apache Shiro (CVE-2020-17523) with a reproducible exploit environment and detailed root cause…