
NodeGoat
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
educationlabs-practicelearning-paths-courses+3
2.1k
owasp/nodegoatThe OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
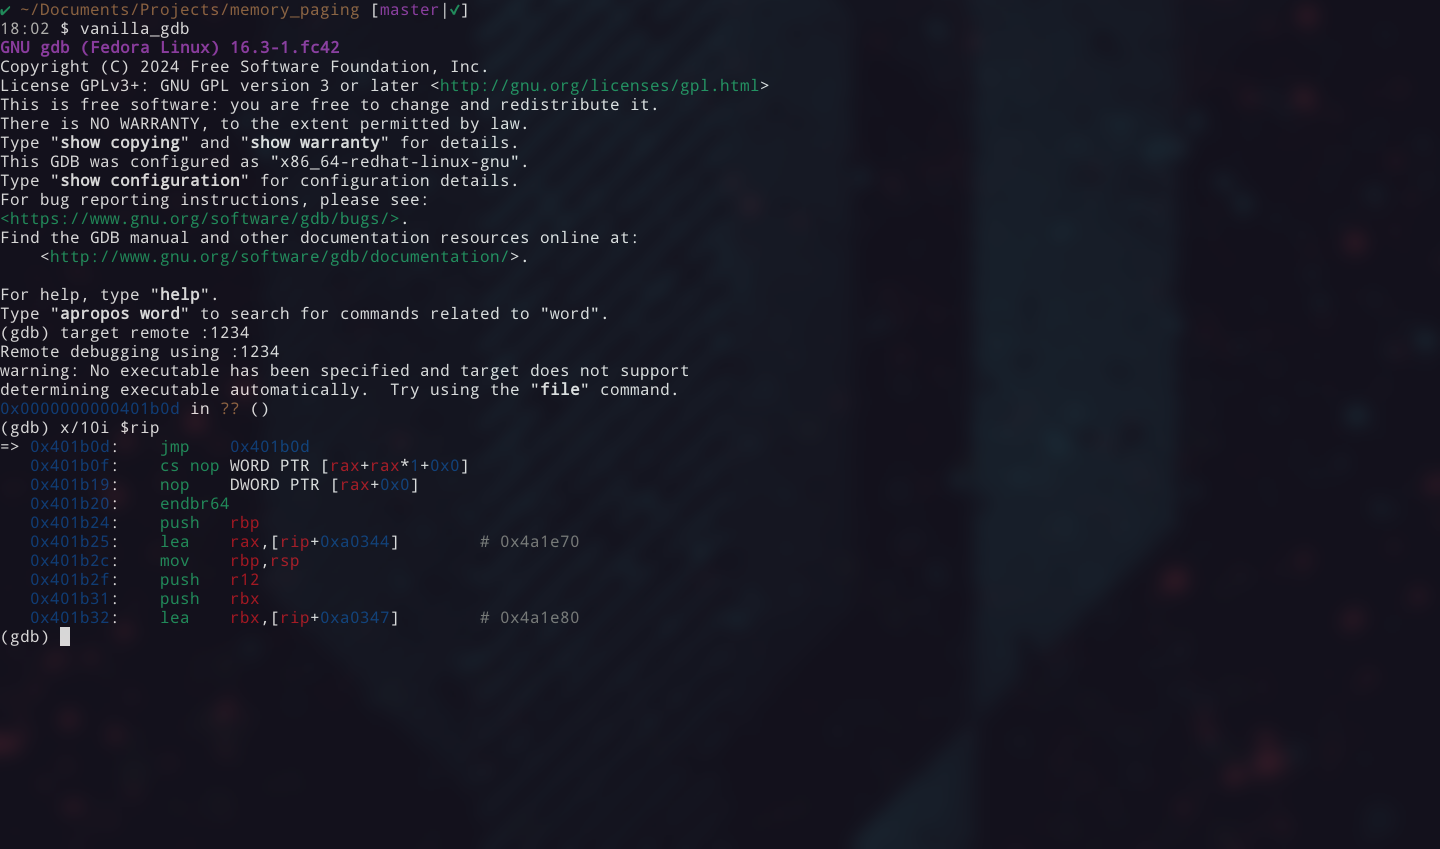 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 joaovicdev/exploit-cve-2026-22778
Proof-of-concept exploit for CVE-2026-22778, an unauthenticated RCE in vLLM's video processing, demonstrating heap address disclosure and a heap…
 f2u0a0d3/cve-2026-42945-nginx-rift-poc
PoC for CVE-2026-42945 (nginx Rift) — heap buffer overflow in ngx_http_rewrite_module. Includes detect/probe/exploit modes, dual-fixture Docker lab,…
 dinosn/cve-2026-42945-nginx32-lab
CVE-2026-42945 nginx 32-bit exploit lab ASLR enabled
 acceis/exploit-cve-2023-38490
Kirby < 3.9.6 XML External Entity exploit
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
 vfa-tuannt/cve-2025-14847
Remake of CVE-2025-14847 MongoDB vulnerability demonstration