
kernel-debug-lab-for-virtual-box
 xalicex/kernel-debug-lab-for-virtual-box
How to set up 2 VirtualBox VM to debug kernel driver using windbg
debuggerseducationlabs-practice
xalicex/kernel-debug-lab-for-virtual-boxHow to set up 2 VirtualBox VM to debug kernel driver using windbg
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
 onion2203/lab_reportlab
This lab was set up to test CVE-2023-33733
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
 rishipatidar/cve-2023-30212-poc-docker-file
This repository provides a Docker container for simulating the CVE-2023-30212 vulnerability, allowing you to practice and understand its impact. It…
 alexs18/cve-2021-4773
Step-by-step tutorial demonstrating how to set up a vulnerable Apache 2.4.49 environment and exploit CVE-2021-41773 path traversal using Kali Linux…
 lorenzodegiorgi/setup-cve-2015-8562
Docker-compose to set up a test environment for exploiting CVE-2015-8562
 cyb3rmik3/prompt-injection-email-samples
Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…
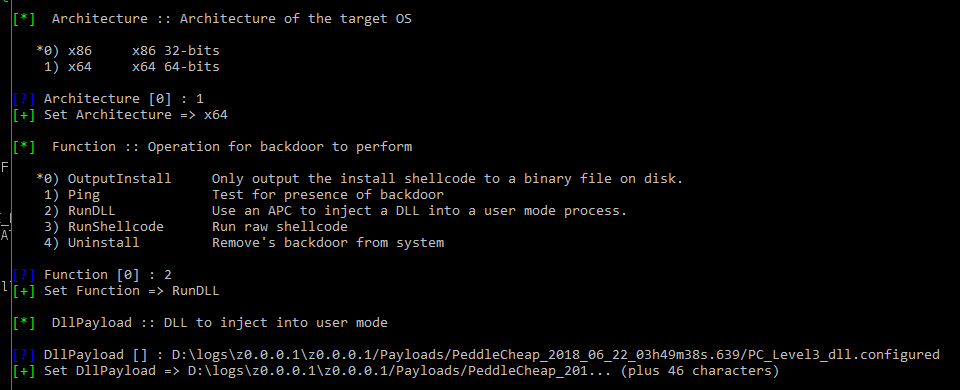 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 jeffaf/cve-2026-32746
CVE-2026-32746 - GNU InetUtils telnetd LINEMODE SLC Buffer Overflow PoC (pre-auth RCE, CVSS 9.8)
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
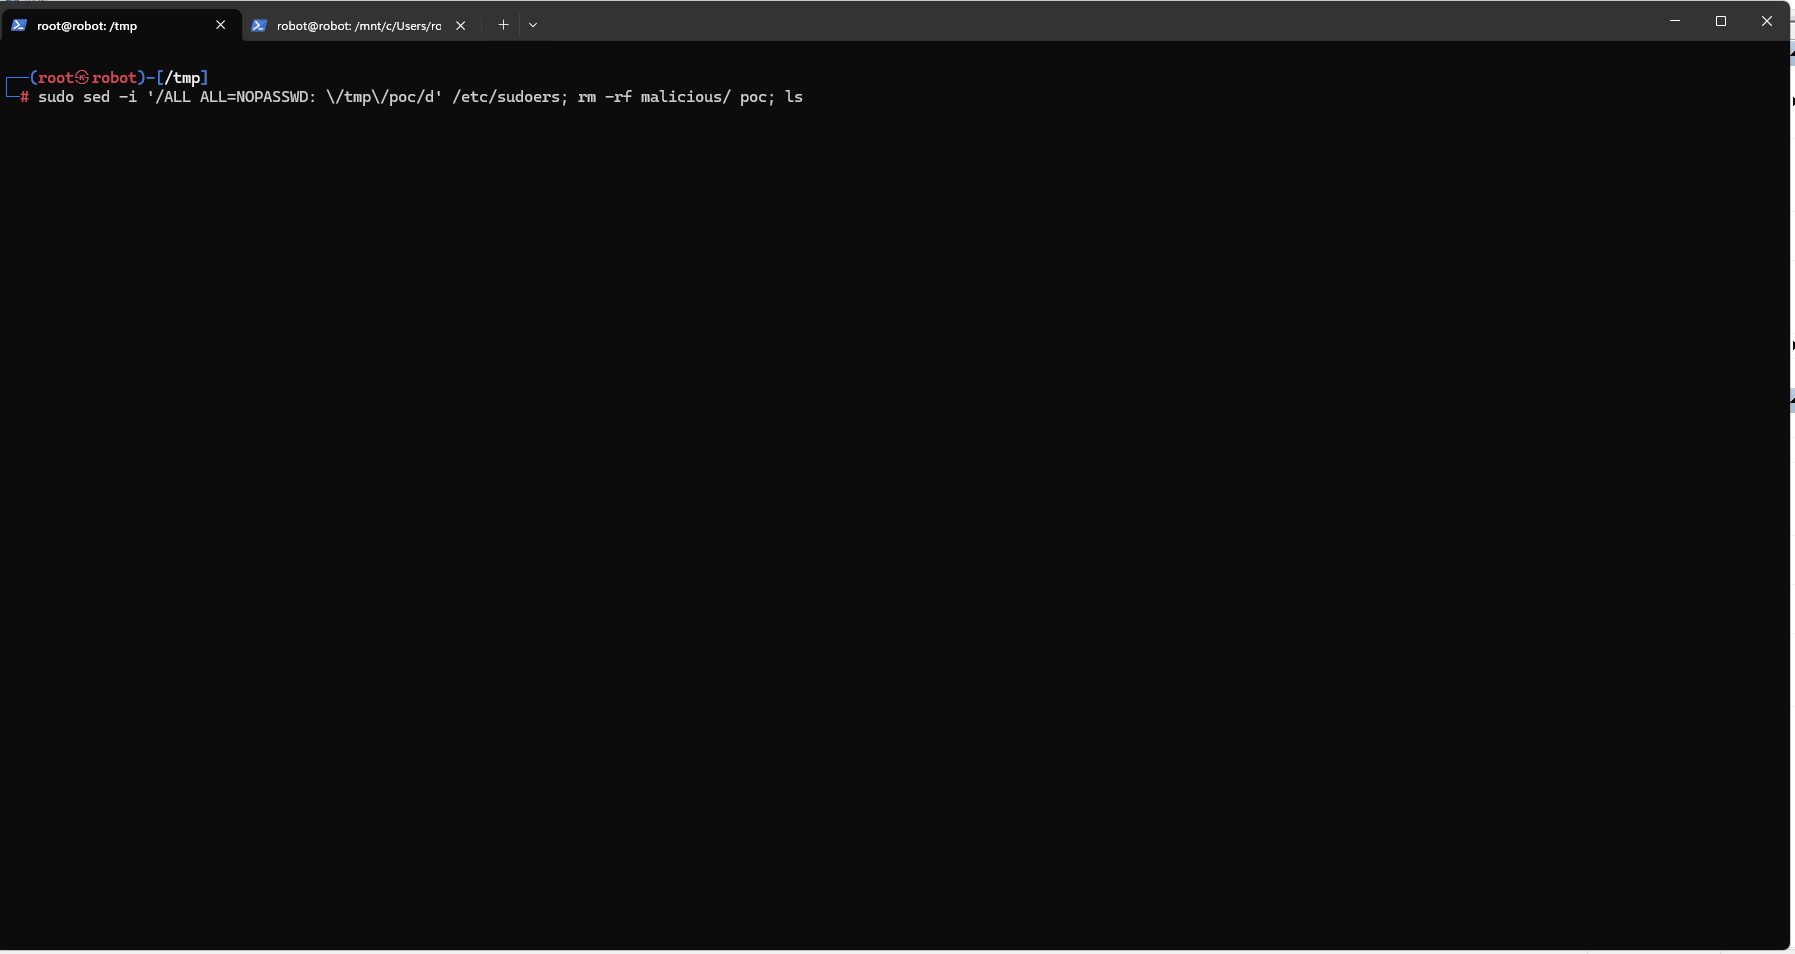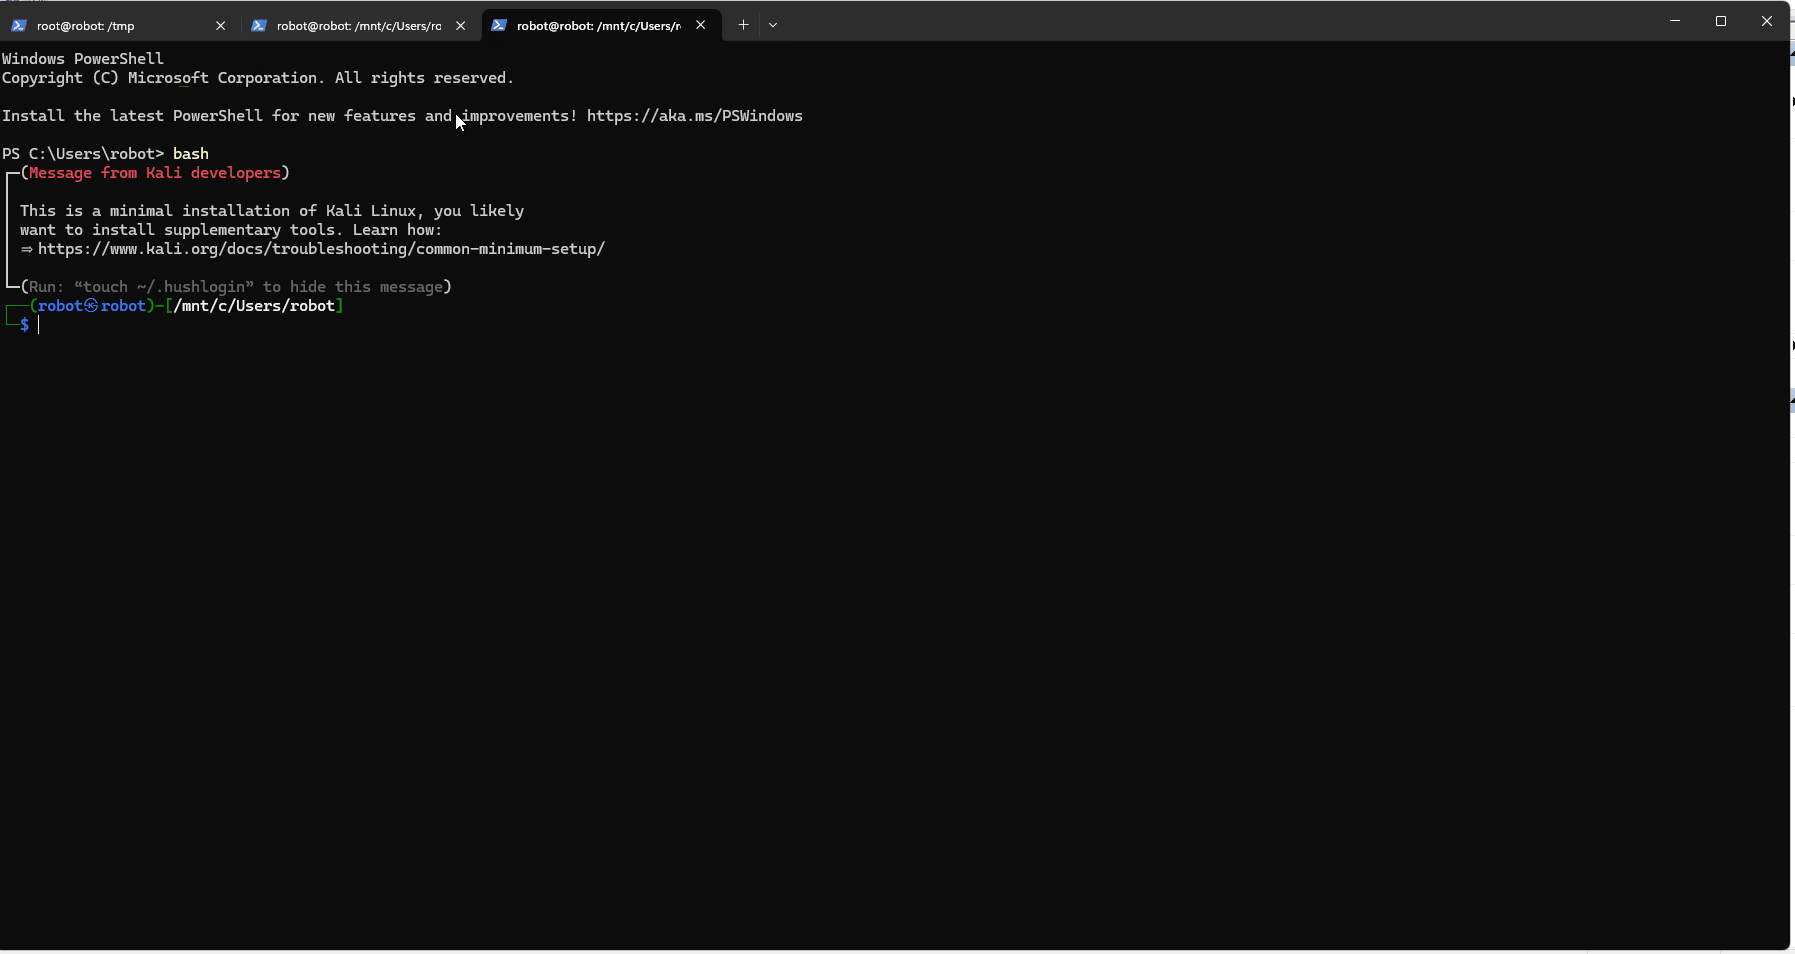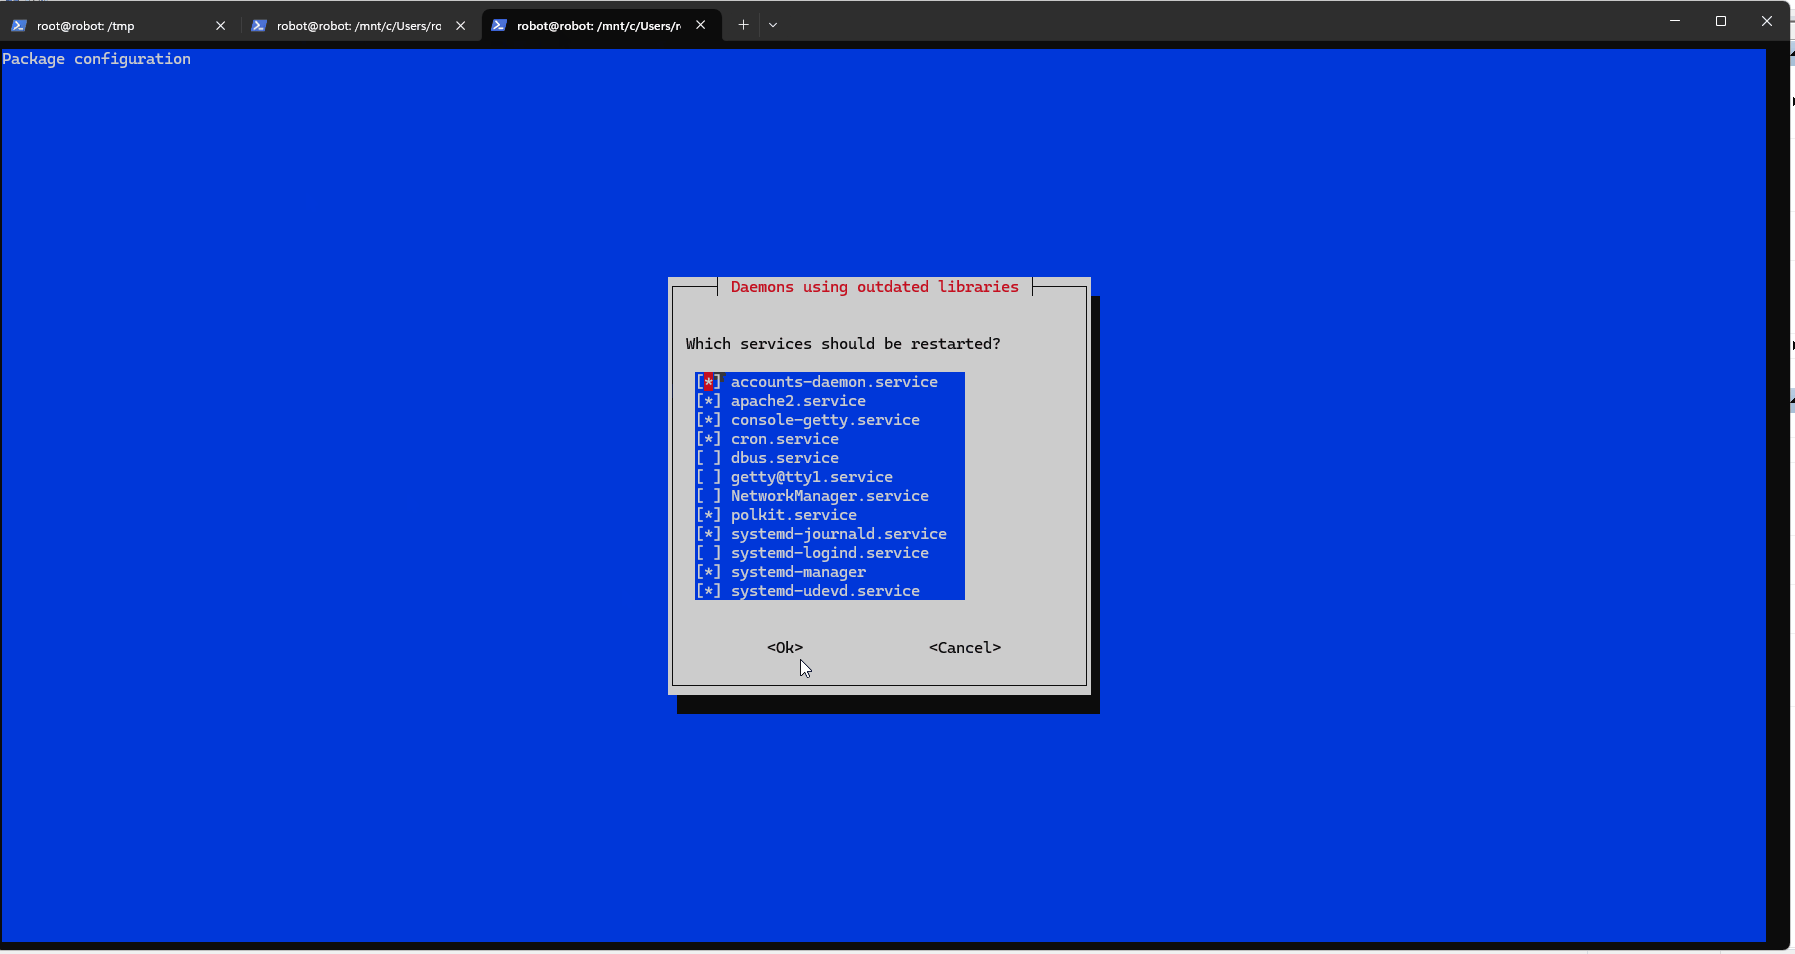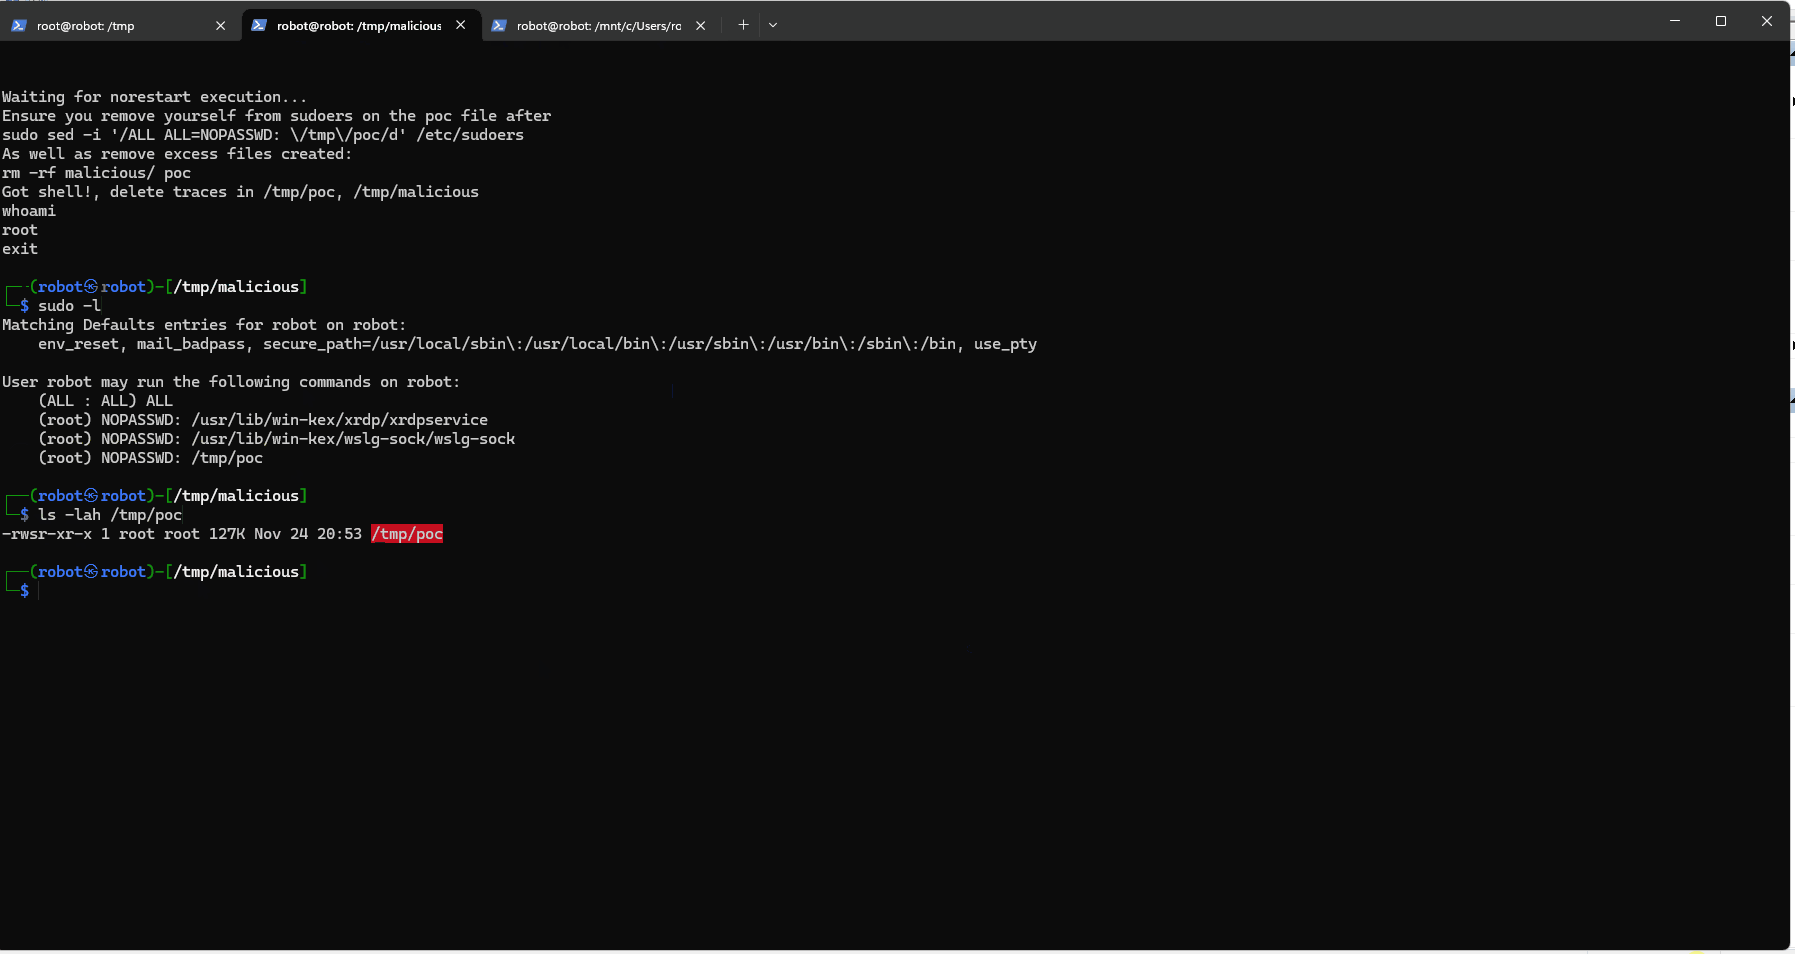 pentestfunctions/cve-2024-48990-poc-testing
Testing POC for use cases
 dungsocool/cve-2025-7384
Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
 buiduchoang24/cve-2023-33733
This project aims at re-analyzing and PoC about CVE-2023-33733. Reportlab up to v3.6.12 allows attackers to execute arbitrary code via supplying a…