

Dirty-COW-CVE-2016-5195-
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
container-escapeeducationexploitation+3
zakariamaaraki/dirty-cow-cve-2016-5195-Exploit the dirtycow vulnerability to login as root
 the-viper-one/pentest-everything
A collection of CTF write-ups, pentesting topics, guides and notes. Notes compiled from multiple sources and my own lab research. Topics also support…
 elsvital/cve-2022-33891-fix
Educational lab demonstrating CVE-2022-33891 exploitation and patch application for Apache Spark with ACL authentication, including PoC verification…
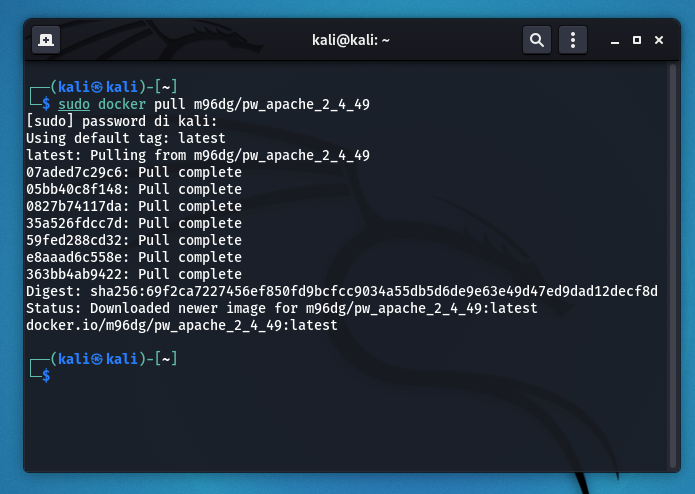 m96dg/cve-2021-41773-exercise
Hands-on lab to exploit Apache 2.4.49 path traversal (CVE-2021-41773) using Docker, Nmap scanning, and curl to retrieve a flag.
 mightysai1997/cve-2021-41773-i-
Proof-of-concept exploit for Apache HTTP Server 2.4.49 path traversal (CVE-2021-41773) with Docker-based lab environment and patch diff analysis.