
Solar-exploiting-log-4j
 lathika-3006/solar-exploiting-log-4j
Step-by-step TryHackMe walkthrough for exploiting the Log4Shell vulnerability (CVE-2021-44228) to achieve remote code execution and capture flags.
educationexploitationlabs-practice+6
2
lathika-3006/solar-exploiting-log-4jStep-by-step TryHackMe walkthrough for exploiting the Log4Shell vulnerability (CVE-2021-44228) to achieve remote code execution and capture flags.
 ibadovulfat/cve-2025-24893
A critical remote code execution (RCE) vulnerability (CVE‑2025‑24893) exists in the XWiki Platform, specifically in the SolrSearch RSS feed endpoint.
 maanvader/cve-2023-22527-poc
Atlassian Confluence Remote Code Execution(RCE) Proof Of Concept
 opsxcq/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution exploit and vulnerable container
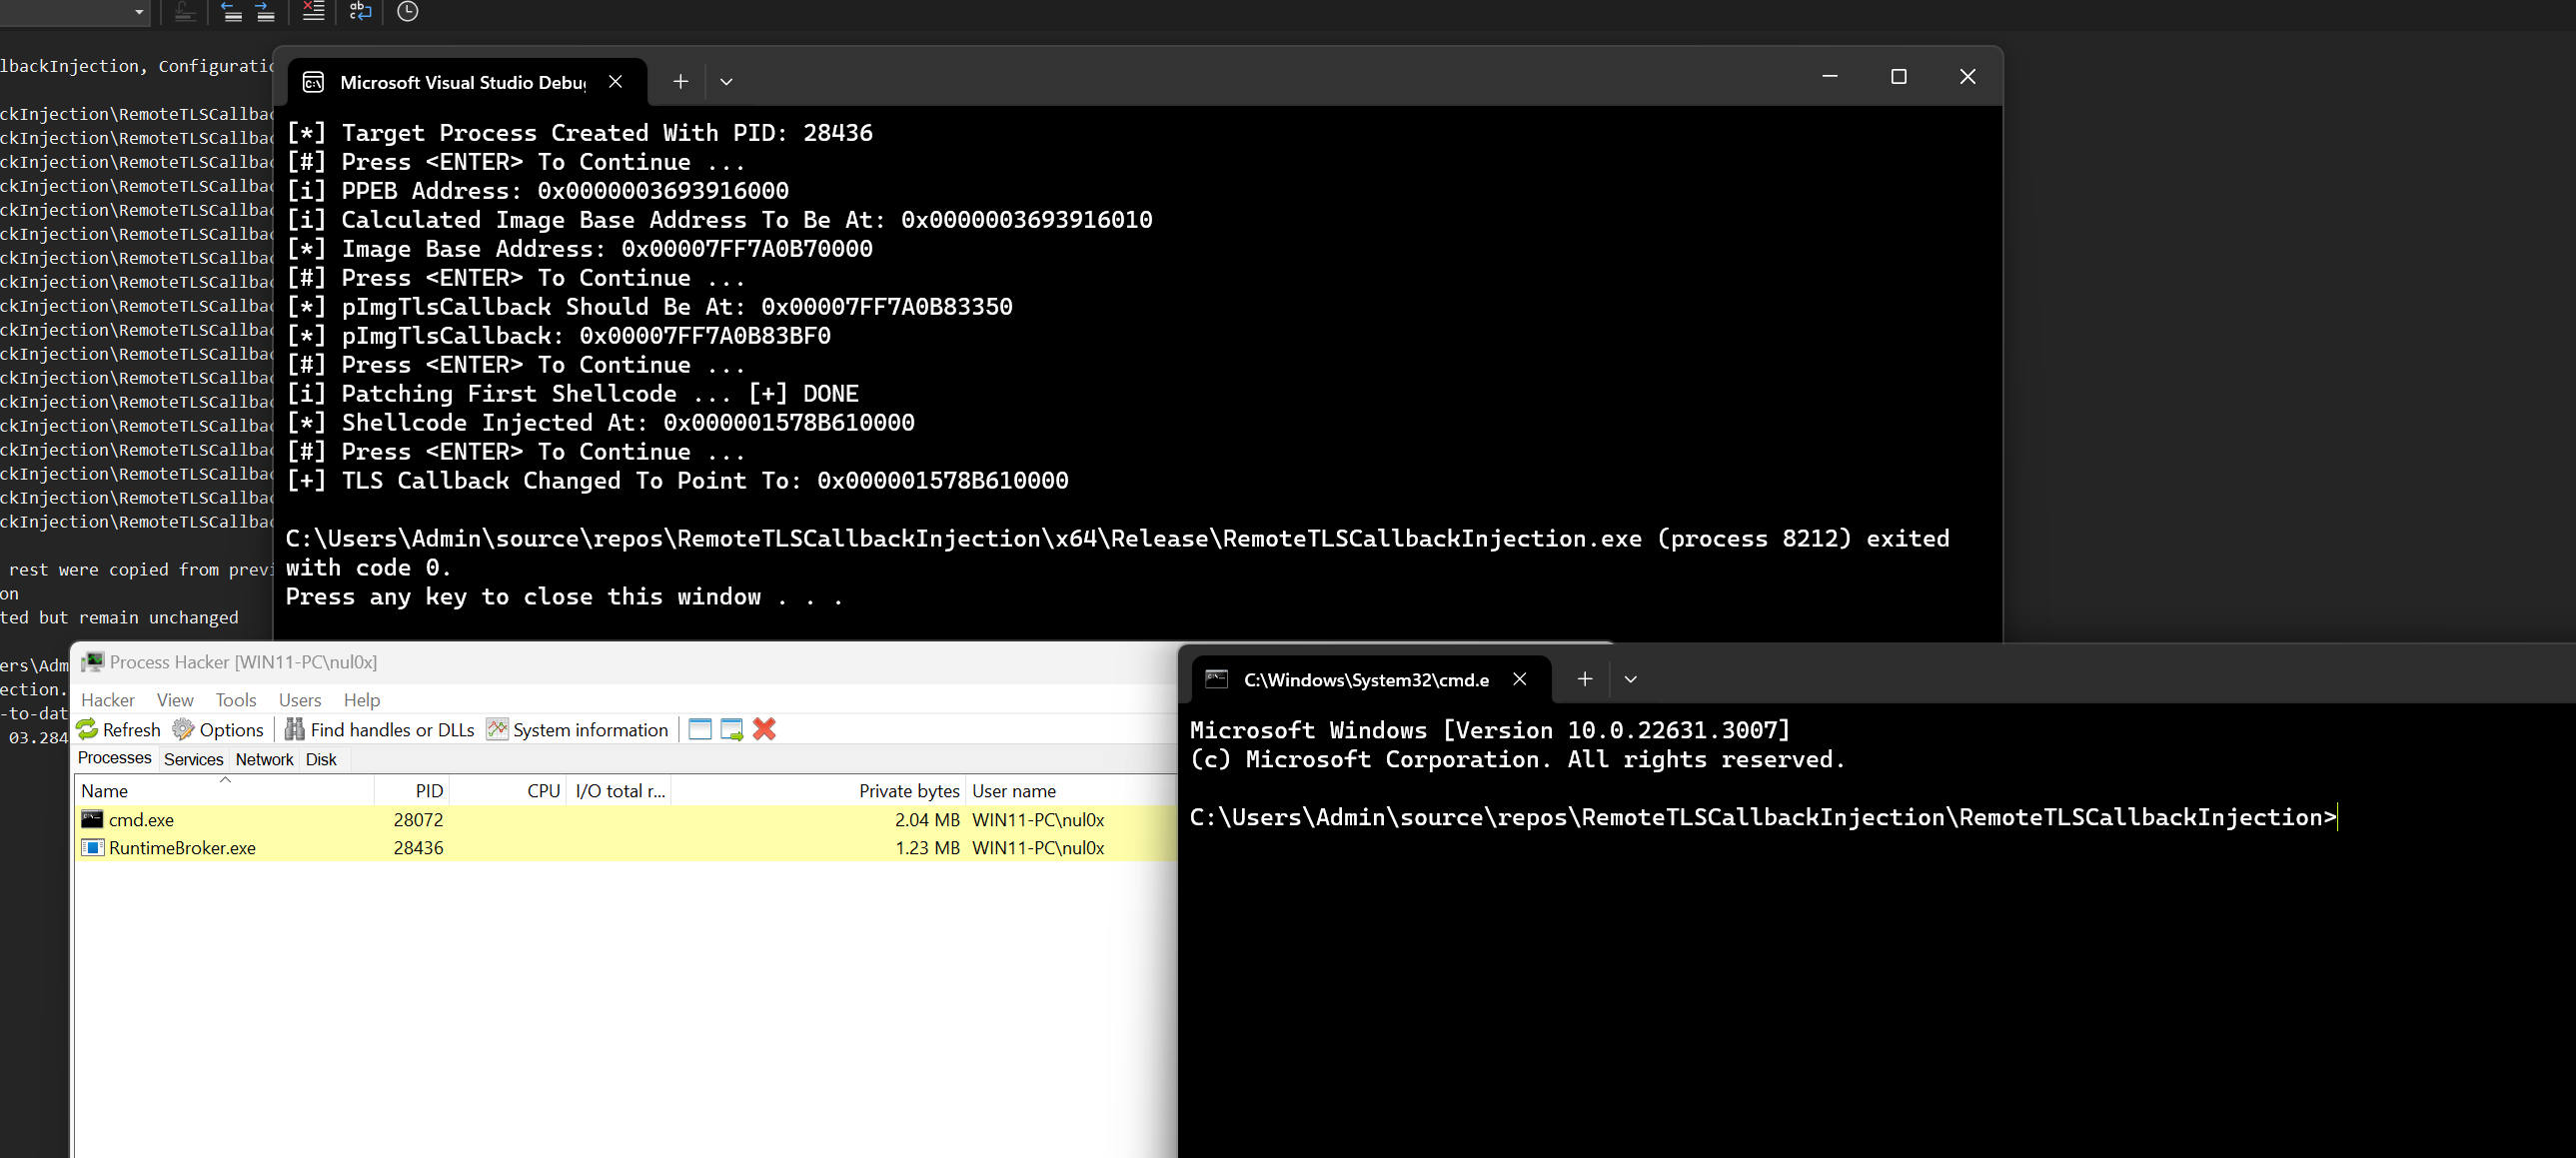 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
 t0kx/exploit-cve-2015-3306
ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container
 doocop/cve-2022-30190
Reproduction of CVE-2022-30190 (Follina) remote code execution vulnerability in Microsoft Office Word via malicious docx/rtf files with ms-msdt…
 lucasamorimca/cve-2020-8163
CVE-2020-8163 - Remote code execution of user-provided local names in Rails
 farisv/pil-rce-ghostscript-cve-2018-16509
PoC + Docker Environment for Python PIL/Pillow Remote Shell Command Execution via Ghostscript CVE-2018-16509
 fairyming/cve-2020-8840
PoC exploit for CVE-2020-8840: JNDI injection leading to remote code execution in FasterXML jackson-databind. Includes environment setup, exploit…
 t0kx/exploit-cve-2015-1427
Elasticsearch 1.4.0 < 1.4.2 Remote Code Execution exploit and vulnerable container
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
 themehackers/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
 koadt/poc-cve-2025-55182
This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…
 eqstlab/cve-2025-1302
JSONPath-plus Remote Code Execution
 pizz33/spring-cloud-function-spel
Reproduction environment and proof-of-concept for Spring Cloud Function SpEL injection leading to remote code execution, with a runnable Java 11 demo…
 codeb0ssx/ultimate-wp2shell
wp2shell — Pre-authentication RCE in WordPress Core (CVE-2026-60137 + CVE-2026-63030). Chains an SQL injection in author__not_in with batch-route…
 twseptian/cve-2022-24112
Apache APISIX < 2.12.1 Remote Code Execution and Docker Lab