
CVE-2018-7602
 kastellanos/cve-2018-7602
Drupalgeddon3 RCE exploit lab with Docker-based vulnerable environment and Metasploit integration for hands-on CVE-2018-7602 exploitation training.
educationexploitationlabs-practice+3
1
kastellanos/cve-2018-7602Drupalgeddon3 RCE exploit lab with Docker-based vulnerable environment and Metasploit integration for hands-on CVE-2018-7602 exploitation training.
 walnutsecurity/cve-2022-36804
A critical command injection vulnerability was found in multiple API endpoints of the Atlassian Bit bucket Server and Data center. This vulnerability…
 imbas007/atlassian-bitbucket-cve-2022-36804
Python exploit for CVE-2022-36804 command injection in Atlassian Bitbucket Server, enabling remote code execution and reverse shell with customizable…
 roticagas/cve-2021-44228-demo
Demo project for testing and proving the Log4Shell (CVE-2021-44228) zero-day exploit, including verification of vulnerable dependencies and multiple…
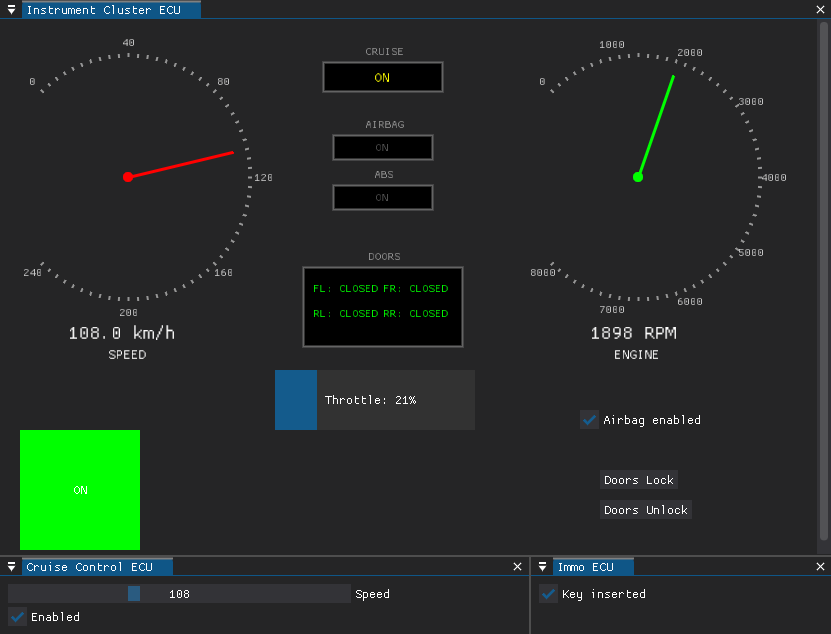 infobyte/doggie_workshop
CAN Bus vehicle simulator for practicing offensive automotive security attacks. Emulates multiple ECUs to enable sniffing, injection, and…
 the-viper-one/pentest-everything
A collection of CTF write-ups, pentesting topics, guides and notes. Notes compiled from multiple sources and my own lab research. Topics also support…
 mavrick-1/cve-2024-23113-test-env
Docker-based test environment for validating CVE-2024-23113 Nuclei templates against simulated vulnerable FortiOS instances, supporting multiple…