
CTFs
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
binary-exploitationcryptographyctf+9
85410 months ago
adamkadaban/ctfsCTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
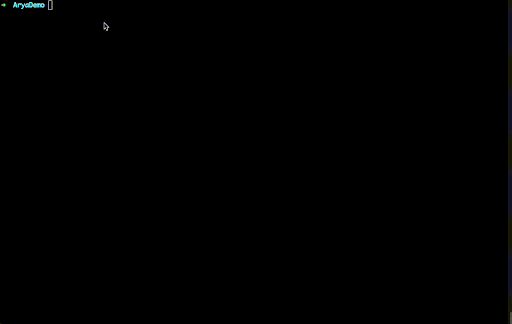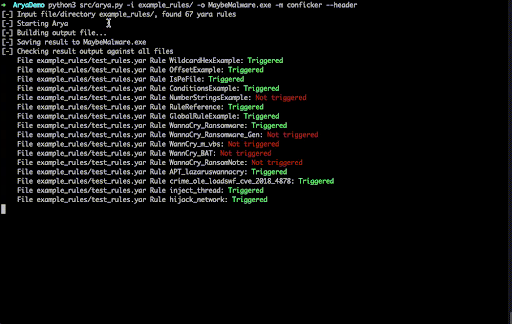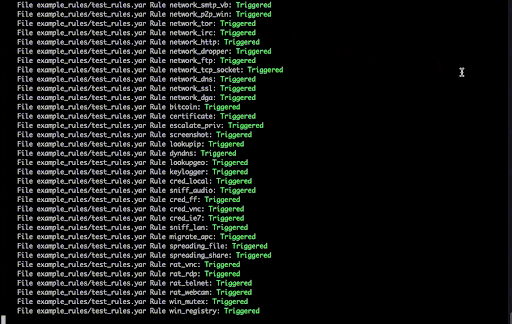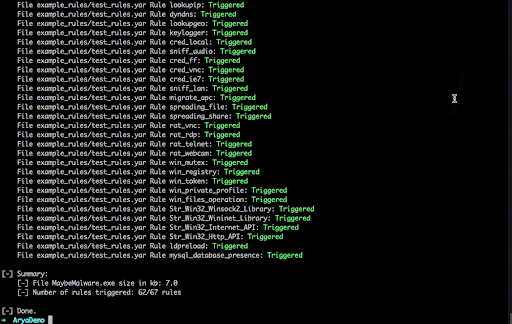 claroty/arya
Generates pseudo-malicious files from YARA rules to trigger AV/EDR detection, enabling malware research, rule QA, and network sensor pressure testing…
 doocop/cve-2022-30190
Reproduction of CVE-2022-30190 (Follina) remote code execution vulnerability in Microsoft Office Word via malicious docx/rtf files with ms-msdt…
 cxiao/rust-reversing-workshop-recon-2024
Slides and files for the Reversing Rust Binaries: One step beyond strings workshop at REcon 2024, presented on June 28, 2024.
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
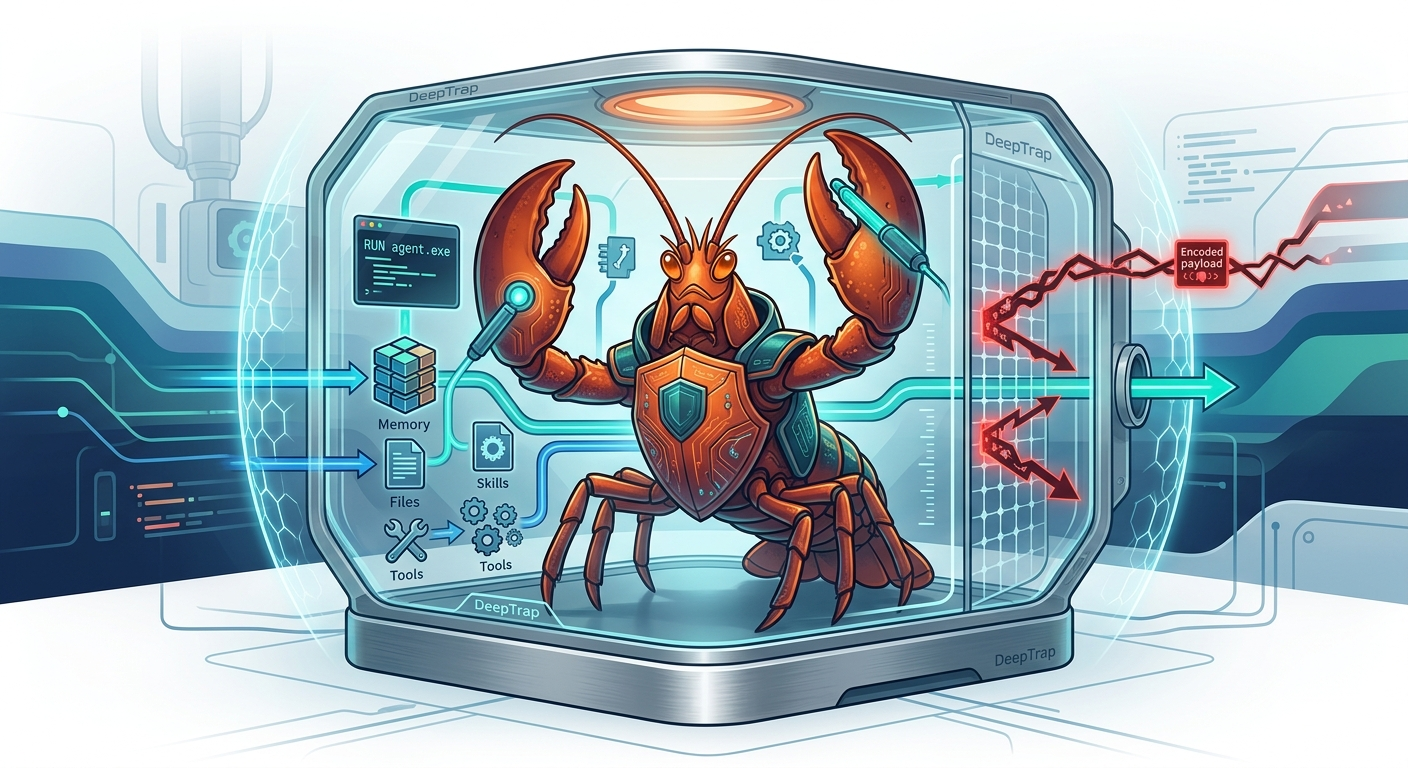 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 anantaakotal/agentcyte
Generates reproducible CORE network topologies from XML scenario files for cybersecurity training and experimentation. Provides Web GUI and CLI for…
 vanigori/cve-2023-38545-sample
Dockerfile containing all the necessary setup files to demo the exploit
 rufflabs/ludus_crushftp_cve-2025-31161_sim
Ansible role that simulates a realistic CrushFTP CVE-2025-31161 exploitation scenario with rotating sensitive data files and automated defender…
 benedictejepu/cve-2026-46300-fragnesia---tryhackme-lab-project
The project documents the completion and analysis of the Fragnesia (CVE-2026-46300) TryHackME lab, which demonstrates a Linux kernel page -cache…
 wallyschag/cve-2025-41656
This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656
 visdev23/vulnerable-docker--cve-2023-30212-
This contains the necessary files and Docker to replicate A vulnerability in OURPHP that has a XSS Vulnerability (CVE-2023-30212)
 abokormahammadmousse/cve-2025-25279-mattermost-path-traversal
Proof-of-concept exploit for CVE-2025-25279, a Mattermost Focalboard path traversal enabling authenticated arbitrary file read and exfiltration of…
 canpilayda/n8n-rce-cve-2025-68613
Lab report analyzing CVE-2025-68613 expression injection in n8n, demonstrating sandbox escape via crafted payloads to access sensitive server files,…
 olowostandard1/cve-2023-38831-winrar-vulnerability-analysis
This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…
 mkway/cve-2026-3304
Reproduction lab for CVE-2026-3304, a Multer async fileFilter race condition causing disk exhaustion via orphaned temp files. Includes vulnerable and…