
Archived
XSSChallengeWiki
 cure53/xsschallengewiki
Community-maintained wiki cataloging XSS challenges and solutions, providing curated hands-on exercises for learning cross-site scripting…
ctfcurated-resourceseducation+5
cure53/xsschallengewikiCommunity-maintained wiki cataloging XSS challenges and solutions, providing curated hands-on exercises for learning cross-site scripting…
 abraxas/vbox-guestctrl-copyfrom-dotdot
VirtualBox 7.2.20 - High - Local - File write - Guest Control copy-from DOTDOT
 abraxas/opnsense-firmware-mirror-sed
OPNsense 26.7.6 - High - Remote - Privilege leftover - custom firmware mirror sed-skips pkg fingerprints
 abraxas/vbox-ovf-href-dest-escape
VirtualBox 7.2.20 - High - Local - File write - OVF href dest escape
 abraxas/sqlite-xfer-auth
SQLite 3.53.4 - High - Local - Privilege leftover - INSERT SELECT xfer skips source READ
 abraxas/spark-history-store-path
Apache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID
 abraxas/mysql-mysqlbinlog-raw-path
MySQL Community Server 26.7.0 - High - mysqlbinlog --raw Rotate path leftover - client file write
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 abraxas/pfsense-api-enroll-json-ssh
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - example-add-devices.py JSON into SSH
 ankitpandey383/roundcube-cve-2025-49113-lab
Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.
 tranphuc2005/cve-2019-3396
Step-by-step analysis and exploitation guide for CVE-2019-3396, a critical SSTI vulnerability in Confluence Server & Data Center, including debugging…
 raytran54/cve-2018-7600
Step-by-step analysis and exploitation lab for Drupal CVE-2018-7600 remote code execution vulnerability, including debugging, exploit code, and…
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 sakib570/cve-2018-1263-demo
Educational exploit demo for CVE-2018-1263 (phpMyAdmin RCE/LFI). Includes vulnerable environment setup via Docker and step-by-step attack walkthrough…
 nccgroup/rustproofing-linux
Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
 h3st4k3r/cve-2025-30065
Java-based research harness for studying CVE-2025-30065, an RCE vulnerability in Apache Parquet via Avro schema deserialization, intended for…
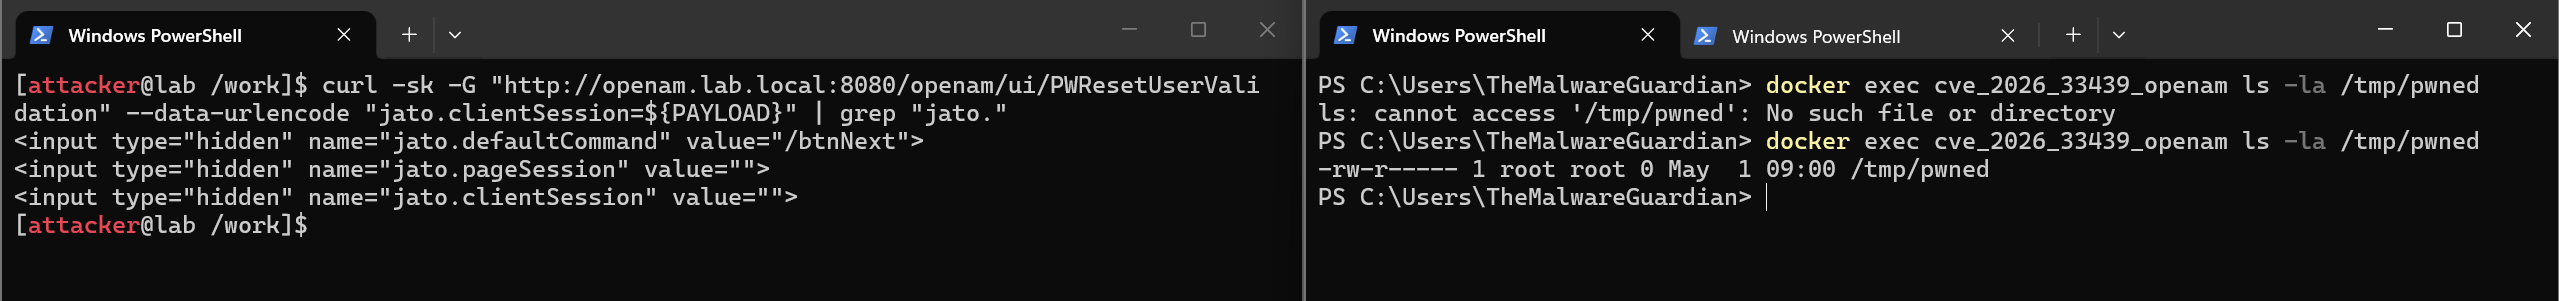 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).