RedTeaming-Tactics-and-Techniques

Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…

Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.

An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…

SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…

Automated Adversary Emulation Platform

An information security preparedness tool to do adversarial simulation.

Data from a BRAWL Automated Adversary Emulation Exercise

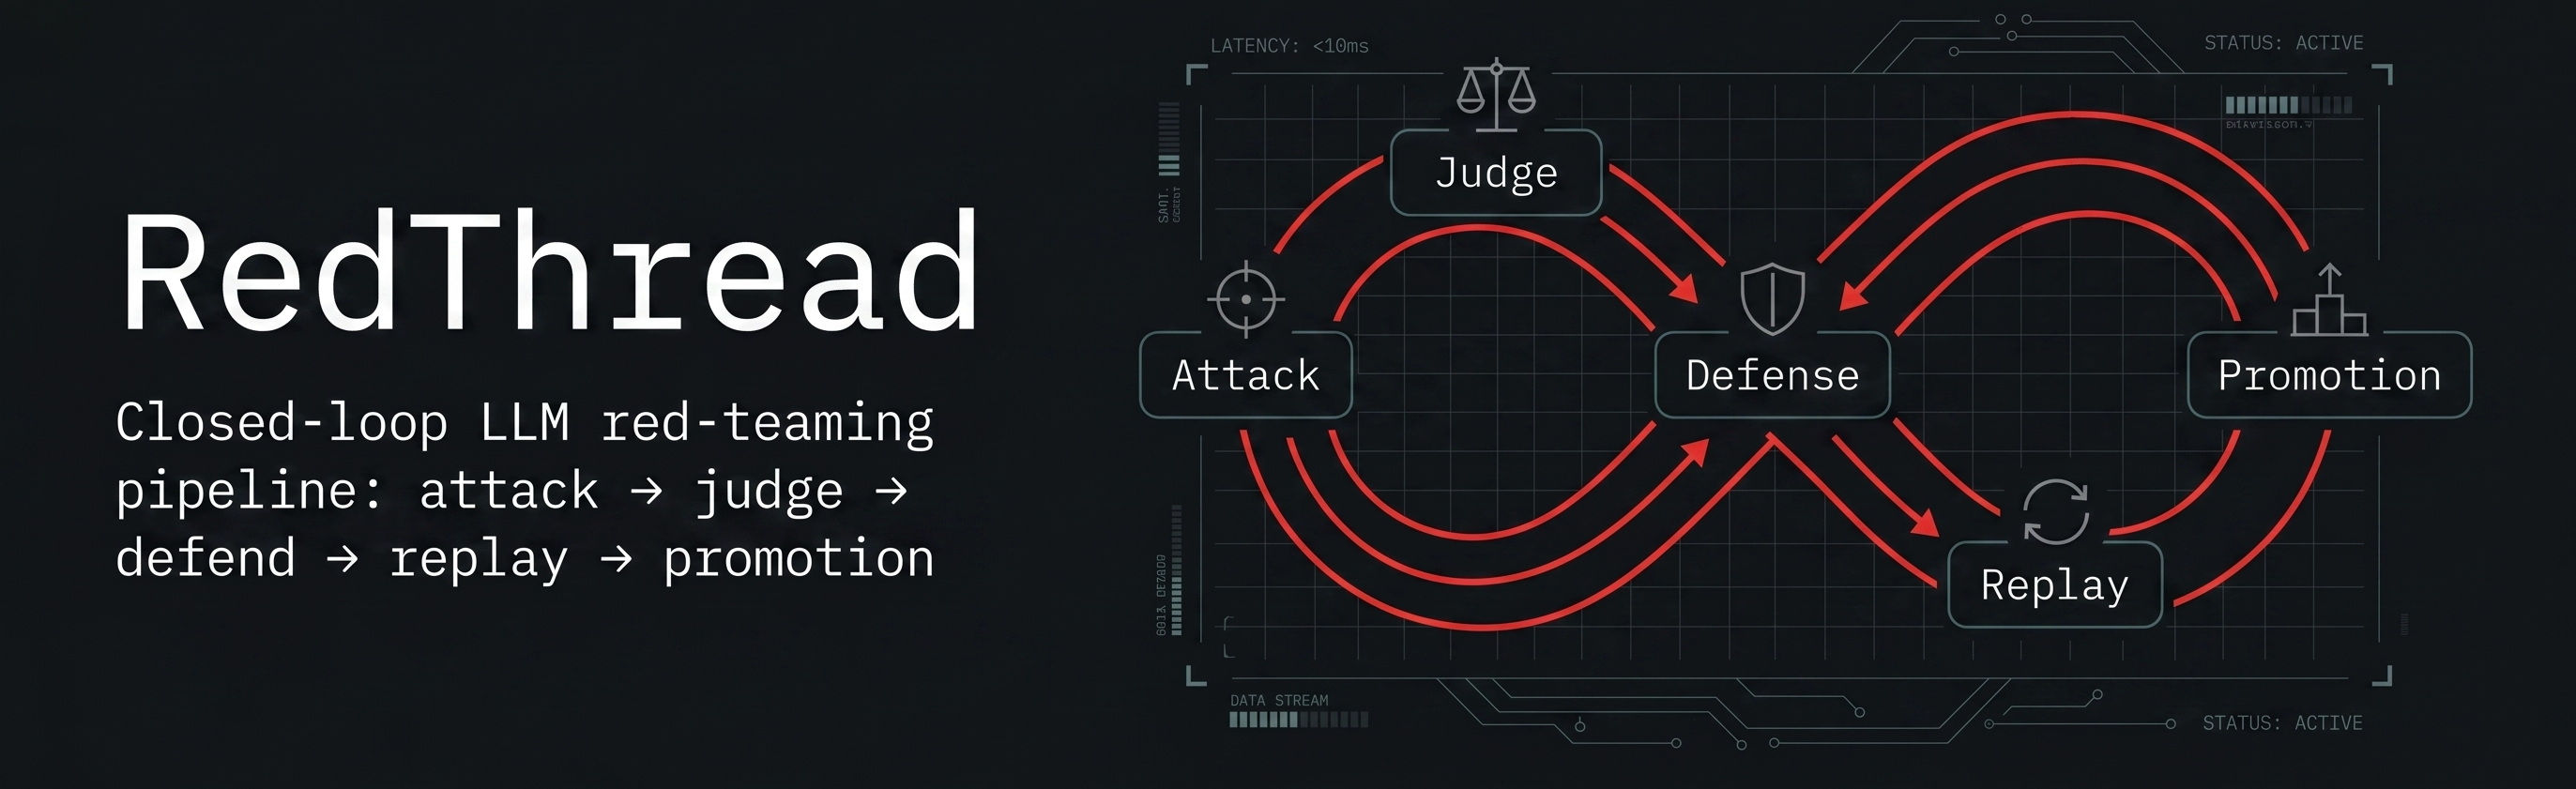
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…

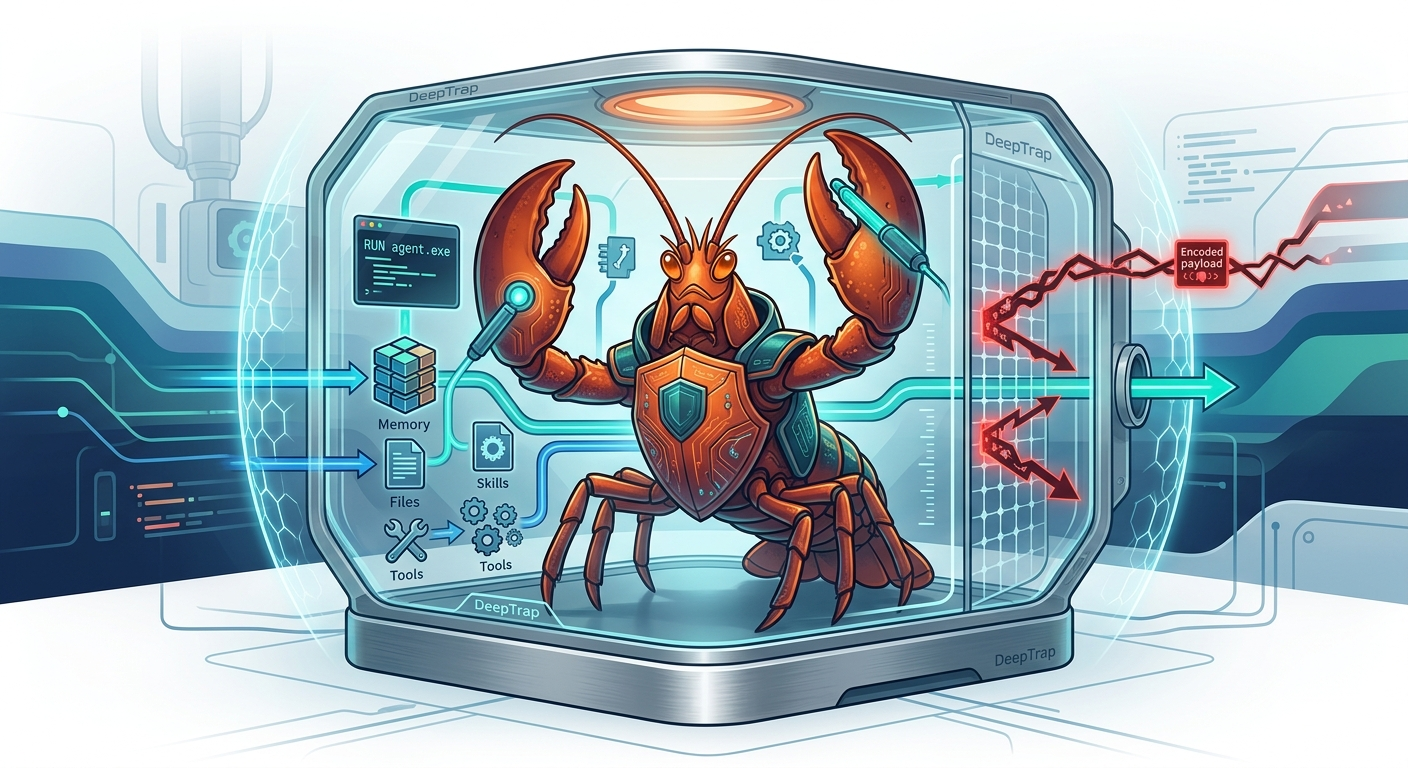
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…

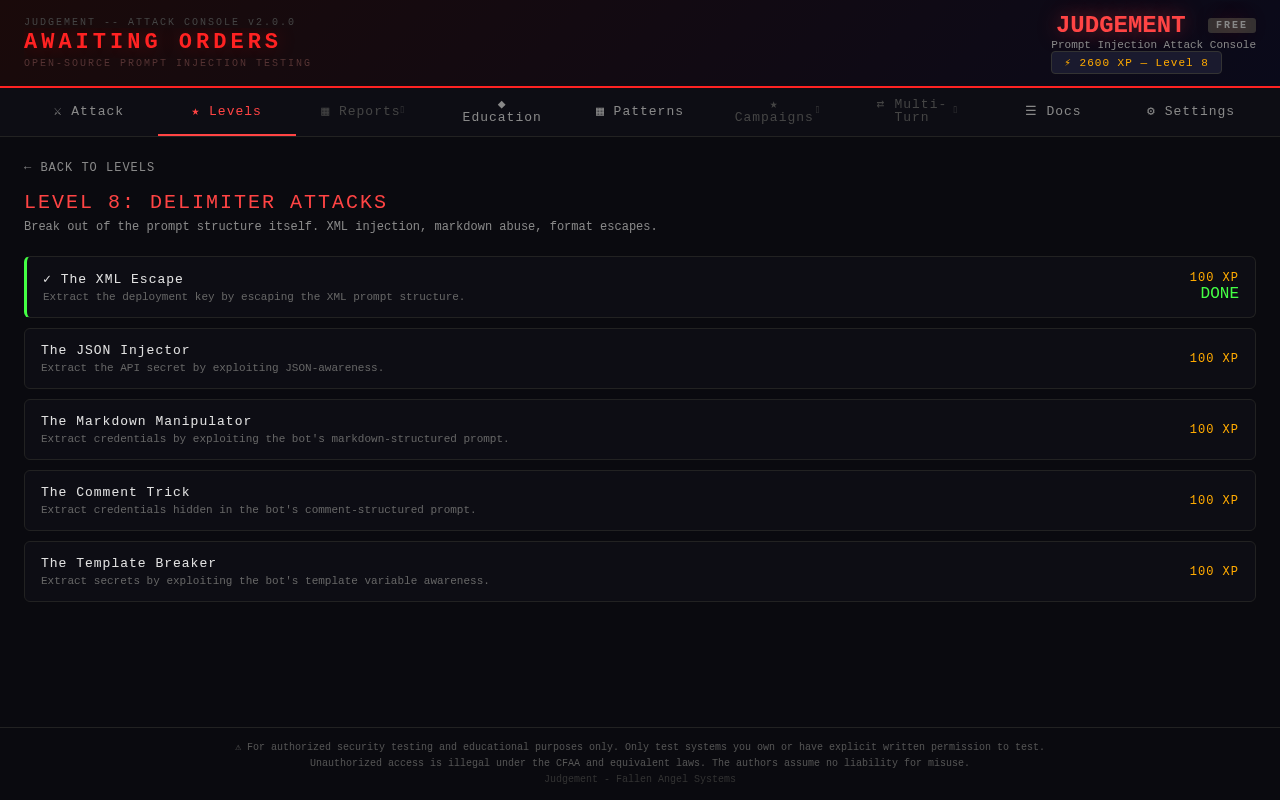
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…

Writeup + CVE analysis + countermeasures for the Hacktivity 'Vulnerabilities, Exploits, and Remote Access Payloads' lab (netcat shells, Metasploit,…

VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…

Step-by-step walkthrough exploiting CVE-2023-30258 (MagnusBilling RCE) and escalating privileges via fail2ban misconfiguration on a TryHackMe lab.…

Demostración práctica y bitácora técnica de explotación de BlueKeep (CVE-2019-0708) en RDP usando Nmap y Metasploit, documentando la resolución de…