

mariadb-13-rce-lab
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
binary-exploitationdatabase-securityexploitation+5
67
dinosn/mariadb-13-rce-labMariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
 euph00/zoneclaw-code
Benchmark and defense code for persistent memory attacks on OpenClaw-style computer-use agents, with memory-zoning mitigation, attack scenarios, and…
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 cybfar/cve-2021-42013-httpd
CVE: 2021-42013 Tested on: 2.4.49 and 2.4.50 Description: Path Traversal or Remote Code Execution vulnerabilities in Apache 2.4.49 and 2.4.50
 edyekomu/cve-2017-12615-poc
PoC environment and exploit for the Apache Tomcat on Windows Remote Code Execution Vulnerability
 ahmedmansour93/event-id-217-rule-name-soc254-apache-ofbiz-auth-bypass-and-code-injection-0day-cve-2023-51467-
🚨 Just completed an incident report on Event ID 217: Apache OFBiz Auth Bypass and Code Injection 0-Day (CVE-2023-51467). This critical vulnerability…
 vigilante-1337/cve-2024-11635
The WordPress File Upload plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 4.24.12 via the…
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 dexsemon/cve-2026-35194
Proof-of-concept exploit and Docker lab for CVE-2026-35194, an Apache Flink SQL code injection enabling remote code execution on TaskManagers via the…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 codeb0ssx/ultimate-wp2shell
wp2shell — Pre-authentication RCE in WordPress Core (CVE-2026-60137 + CVE-2026-63030). Chains an SQL injection in author__not_in with batch-route…
 kevthehermit/cve-2020-10560
Docker-based lab environment and proof-of-concept scripts for exploiting CVE-2020-10560, an arbitrary file read vulnerability in OSSN. Includes PHP…
 olowostandard1/cve-2023-38831-winrar-vulnerability-analysis
This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…
 amusedx/cve-2026-22686
CTF challenge focused on sandbox escape via source code review of a JavaScript execution environment, designed for hands-on vulnerability analysis…
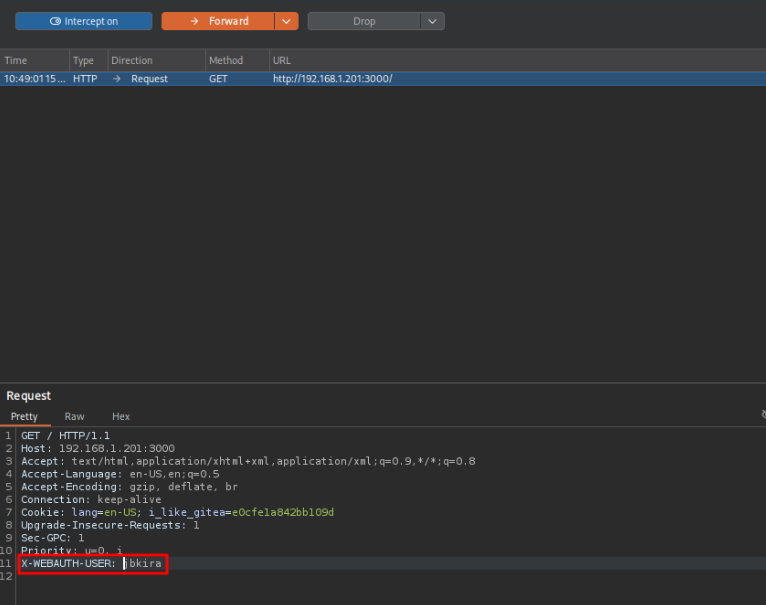 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 lazarus0x1337/cve-2026-25632
CVE-2026-25632 — Fix Unsafe JSON Deserialization Leading to Remote Code Execution
 dhananjayakumarn/cve-2025-55182-lab
A hands-on lab for understanding and exploiting CVE-2025-55182 (React2Shell) - Remote Code Execution in React Server Components
 fishyyh/cve-2025-48384-poc
Proof-of-concept exploit for CVE-2025-48384, demonstrating remote code execution via a crafted git clone operation on vulnerable Git versions.