
CVE-2024-28000
 alihzsec/cve-2024-28000
Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
educationexploitationlabs-practice+5
alihzsec/cve-2024-28000Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 fortbridge-uk/cve-2026-75604
Reproduction lab and exploit tooling for CVE-2026-75604, a path traversal in Next.js incremental cache leading to unauthenticated RCE on Windows.…
 dhananjayasj/cve-2026-3844-breeze-cache-wordpress-plugin-remote-code-execution
Docker lab and manual exploitation guide for CVE-2026-3844, a critical unauthenticated arbitrary file upload vulnerability in the Breeze Cache…
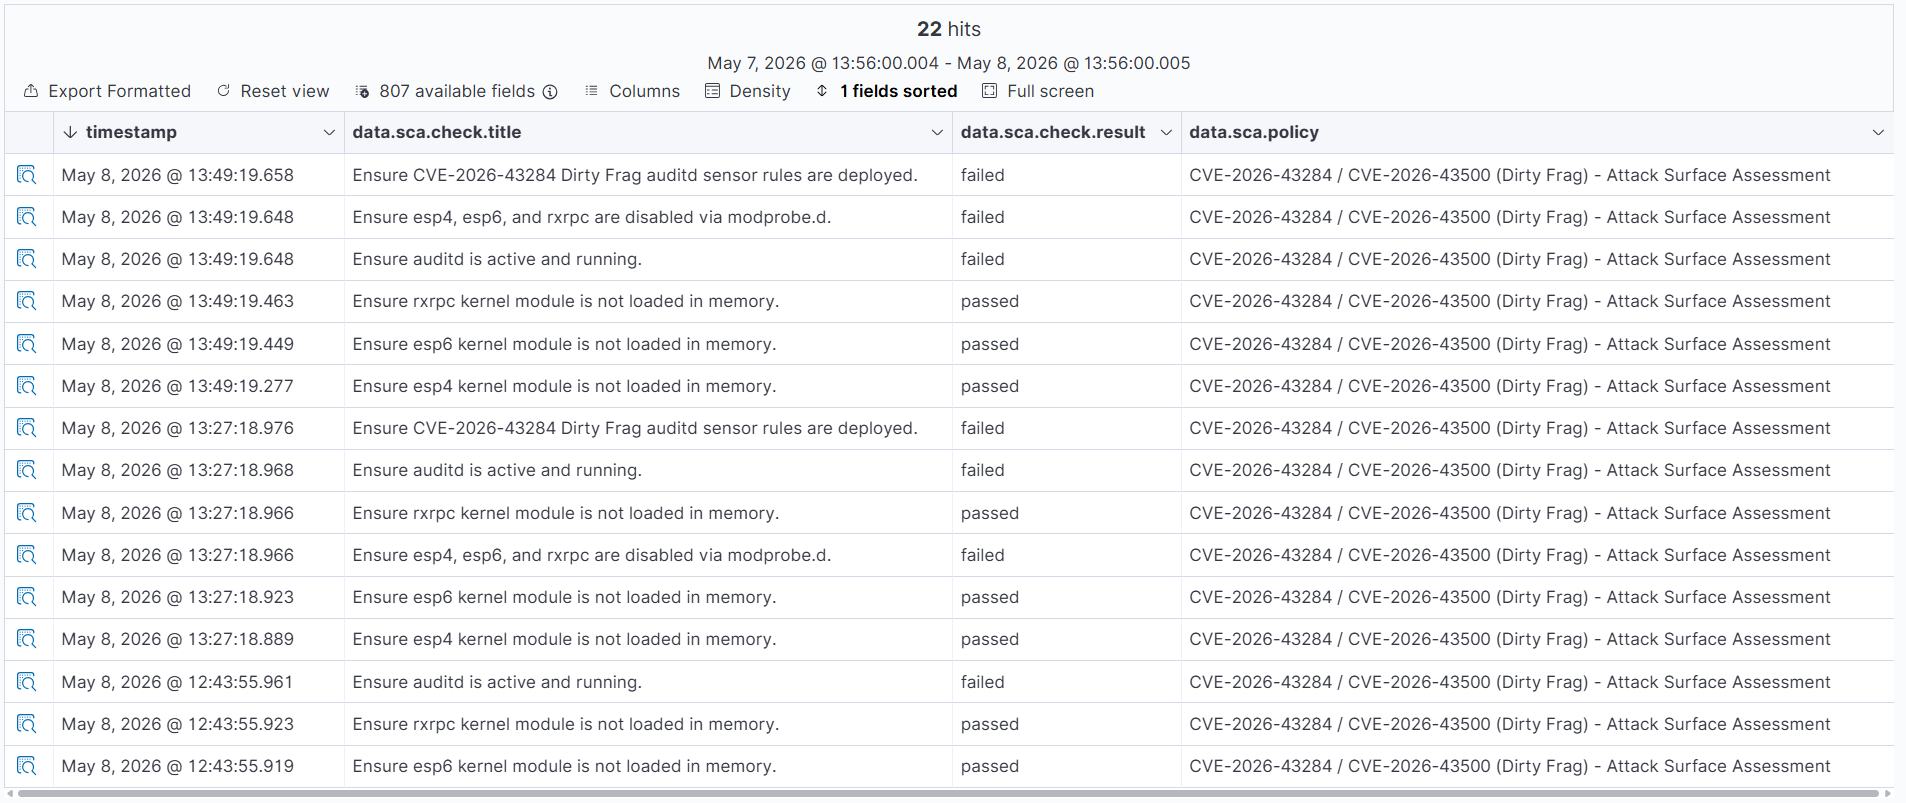 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 rootdirective-sec/cve-2026-3844-lab
Local Docker lab for reproducing CVE-2026-3844, an unauthenticated arbitrary file upload to RCE in the WordPress Breeze Cache plugin. Compares…
 0xcyberstan/cve-2026-31694-poc
Linux kernel FUSE readdir cache out-of-bounds write (CVE-2026-31694): a malicious FUSE server overflows a page-cache page by 24 bytes. PoC plus an…
 pulentoski/cve-2026-31431
Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…
