
Healer
 glease/healer
Patch up CVE-2021-44228 for minecraft forge 1.7.10 - 1.12.2
educationexploitationlabs-practice+2
glease/healerPatch up CVE-2021-44228 for minecraft forge 1.7.10 - 1.12.2
 hophtien/cve-2025-54424
CVE-2025-54424: 1Panel TLS client cert bypass enables RCE via forged CN 'panel_client' using a bundled scanning and exploitation tool. Affected: <=…
 abraxas/cve-2026-13447
Proof-of-concept exploit for CVE-2026-13447, a critical authentication bypass in the WordPress MStore API plugin via forged Firebase JWT tokens, with…
 fortbridge-uk/cve-2026-75604
Reproduction lab and exploit tooling for CVE-2026-75604, a path traversal in Next.js incremental cache leading to unauthenticated RCE on Windows.…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
 shirouuu/gitea-template-sync-path-traversal-privilege-escalation-cve-2026-38526-
PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…
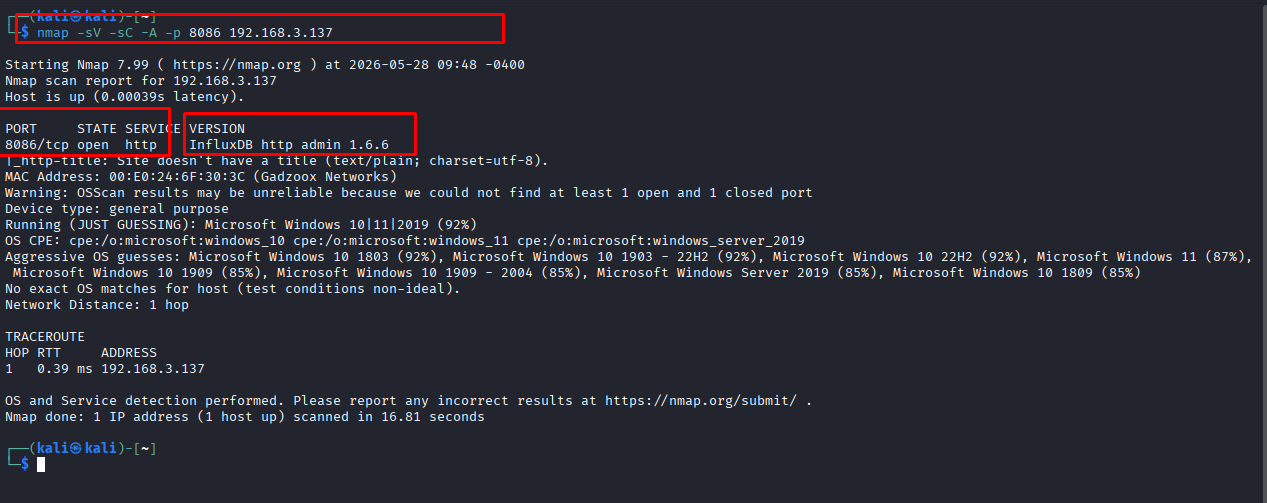 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…
 heisenbergh4x/cve-2008-1930
CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…
 saretawa/cve-2015-9357-poc
Proof-of-concept exploit for CVE-2015-9357: stored XSS in WordPress smiley parser that bypasses wp_kses, chains nonce forgery to create admin…