
renode
 renode/renode
Open-source simulation framework for developing, testing, and debugging unmodified software for multi-node embedded and IoT systems, supporting ARM,…
educationembedded-systems-securityfirmware-analysis+3
3.0k
renode/renodeOpen-source simulation framework for developing, testing, and debugging unmodified software for multi-node embedded and IoT systems, supporting ARM,…
 ashemery/exploitation-course
Offensive Software Exploitation Course
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
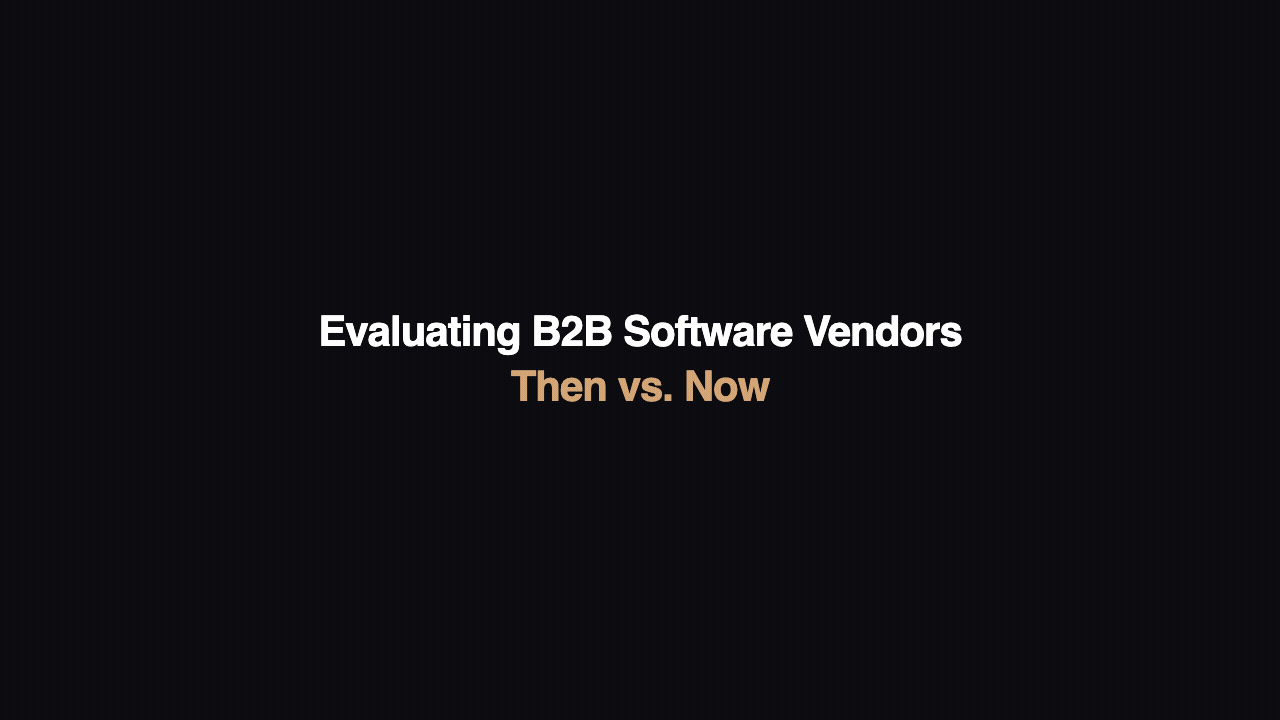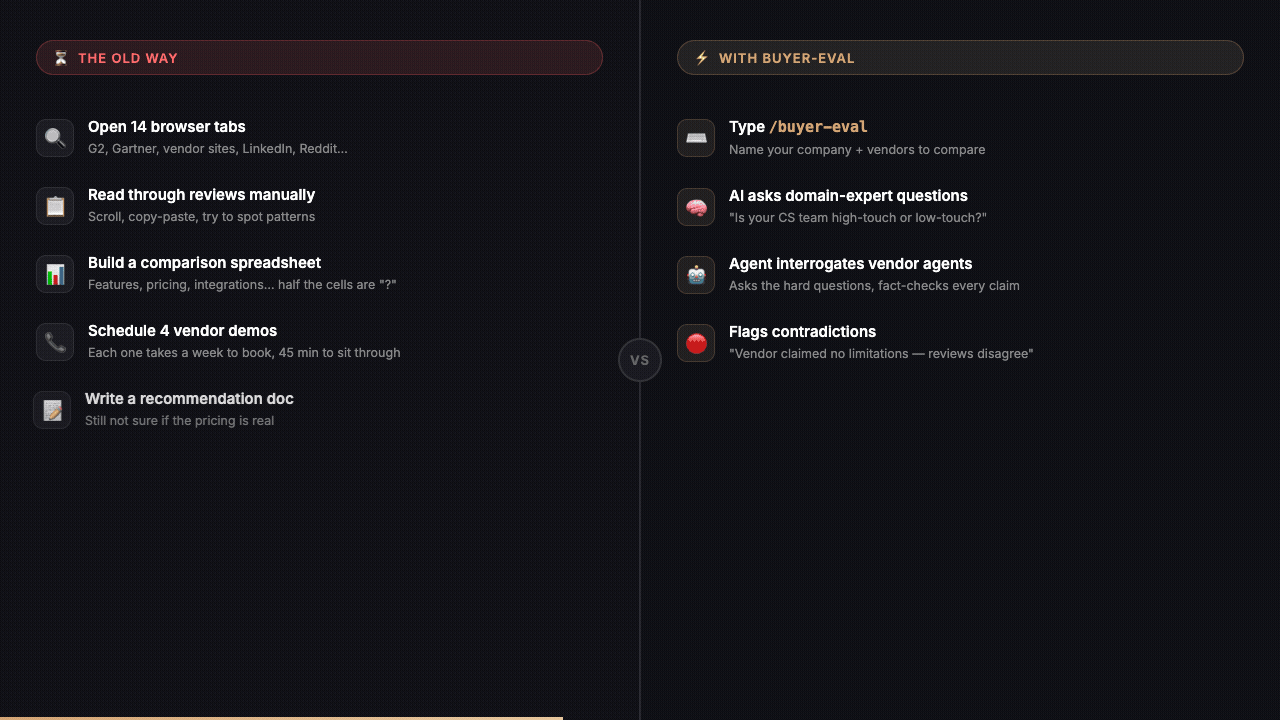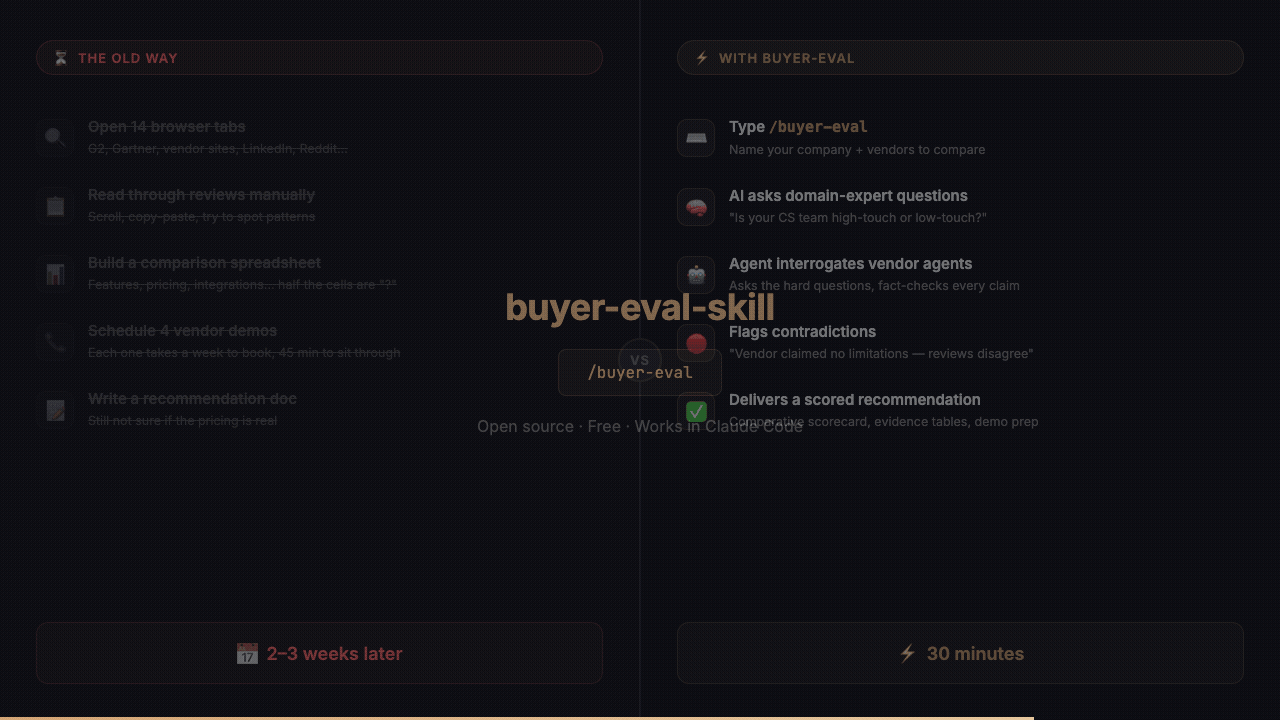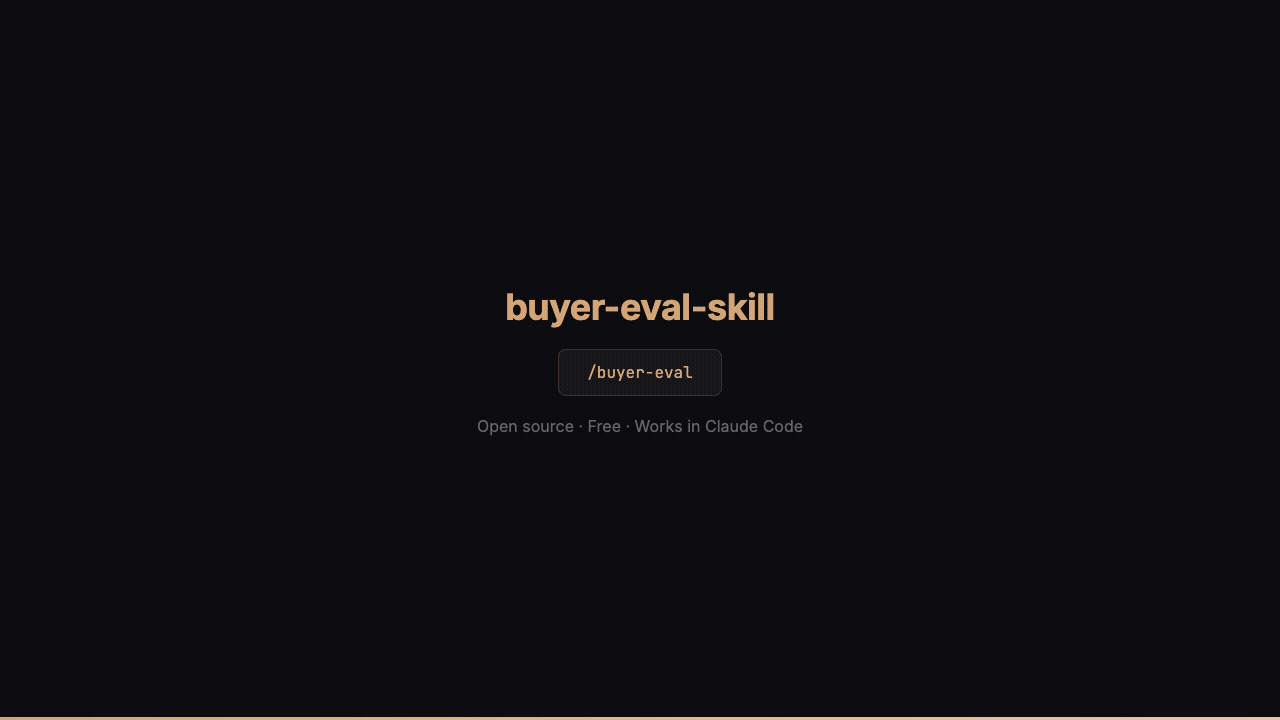 salespeak-ai/buyer-eval-skill
B2B software vendor evaluation skill for Claude Code — domain-expert questions, vendor AI agent conversations, evidence-based scoring
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 anilkashyap01/binary-exploitation-and-kernel-escalation
Secured root-level access by identifying and exploiting misconfigurations and outdated software. Buffer overflow vulnerability in an outdated version…
 religan/cve-2023-20198
A cybersecurity case study analysing CVE-2023-20198 in Cisco IOS XE, covering vulnerability exploitation, mitigation strategies, secure software…
 milad-rafie/pwnkit-local-privilege-escalation-vulnerability-discovered-in-polkit-s-pkexec-cve-2021-4034
Software Vulnerabilities and mitigation university course, to show exploitation and remediation caused by this vulnerability
 rainhawk13/added-pentest-ground-to-vulnerable-websites-for-training
CVE-2017-0089 Learn more at National Vulnerability Database (NVD) • CVSS Severity Rating • Fix Information • Vulnerable Software Versions • SCAP…
 blackhillsinfosec/wififorge
Automated WiFi hacking lab environment using mininet-wifi to simulate wireless attack vectors for pentester training, eliminating hardware overhead.
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 mayca369/cve-2025-55182
Demonstrates CVE-2025-55182 RCE exploit in React Server Functions to highlight insecure prototype references in Next.js, with educational simulation…
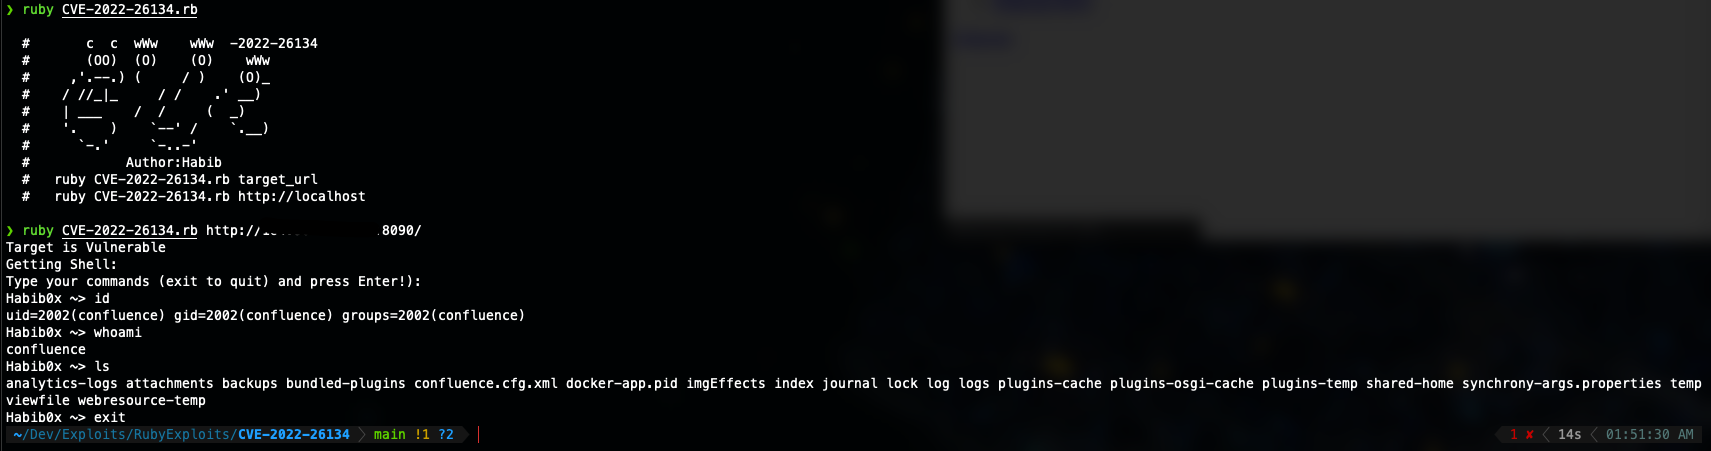 habib0x0/cve-2022-26134
Atlassian Confluence- Unauthenticated OGNL injection vulnerability (RCE)
 probablysecure/triage-cve-2021-44228-log4shell-log4j-
Goal is to triage well known attack and learn how security teams quickly respond.
 tsiddiquea/cve-reproduction-lab
Cybersecurity lab demonstrating Apache CVE-2021-41773 path traversal vulnerability with vulnerable server simulation, scanner, and security reporting.
 kaylertee/computer-security-equifax-2017
A hands-on simulation of CVE-2017-5638 (Apache Struts2 RCE), showcasing exploit reproduction, OS-level command execution, and mitigations such as…