CVE-Exploit-Research-Development

A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…

A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…

Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…

scanner/exploiter CVE-2026-24061 & CVE-2026-32746

vsftpd 2.0.5 - 'CWD' (Authenticated) Remote Memory Consumption

A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…

OSINT tool researched and designed to hunt down IG handles

An information security preparedness tool to do adversarial simulation.

Python exploit script for CVE-2024-23897 (Jenkins RCE) with an automated Docker-based vulnerable lab for controlled security testing and education.

Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…

A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk

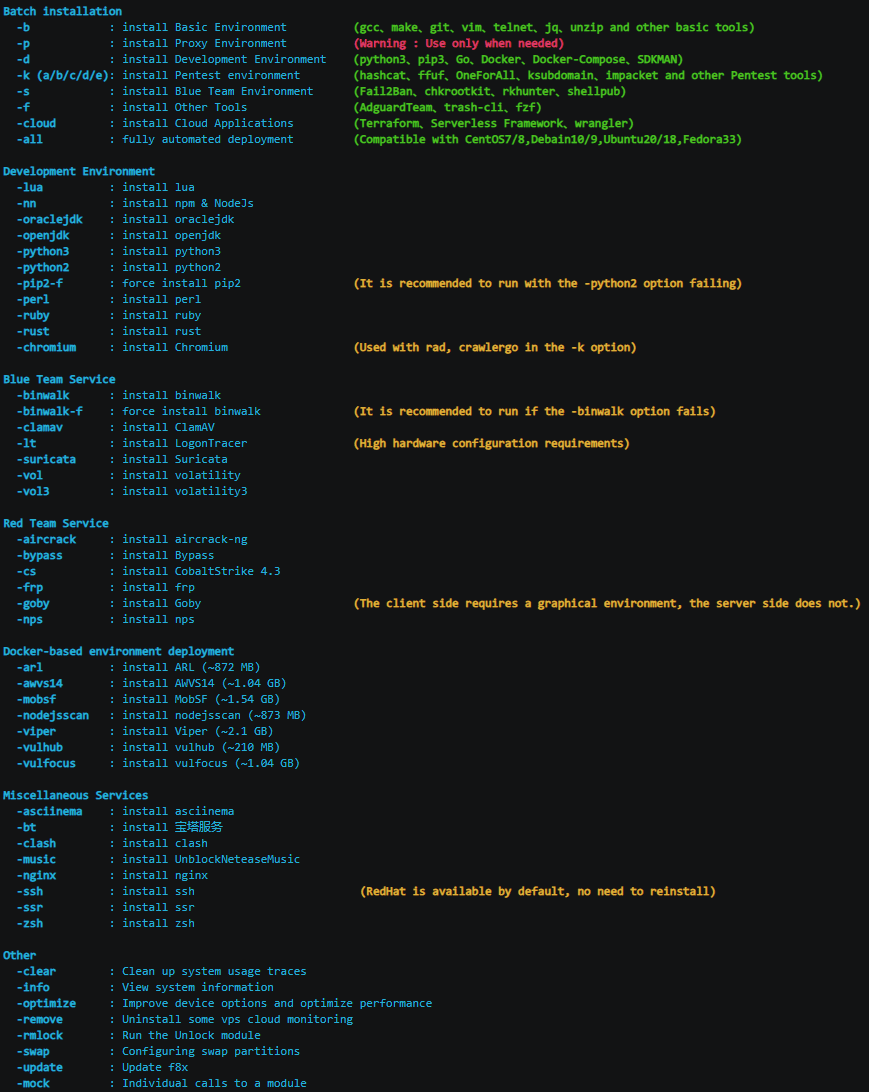
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!

POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…

🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…

a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…

Docker-based lab to validate CVE-2021-44228 (Log4Shell) in Java apps, test mitigations, and simulate RCE via LDAP and HTTP payloads.

Exploit for CVE-2025-55182 targeting Next.js React Server Components via prototype pollution, enabling remote code execution with command execution…