
0l4bs
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
ctfeducationlabs-practice+1
tegal1337/0l4bsCross-site scripting labs for web application security enthusiasts
 libasmon/exploite-cve-2023-30212-vulnerability
Docker environment and exploit the CVE-2023-30212 vulnerabilityVE-2023-30212 is a security vulnerability that affects versions of OURPHP prior to or…
 dungsocool/cve-2014-3120
Step-by-step lab guide demonstrating CVE-2014-3120 exploitation against Elasticsearch 1.1.1, covering vulnerability analysis, RCE via MVEL scripting,…
 pierfrancescoconti/leaflet-cve-2025-69993
Proof-of-concept for CVE-2025-69993: Cross-Site Scripting in Leaflet's bindPopup() method. Includes advisory, impact analysis, and a demo Angular…
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 libasv/exploite-cve-2023-30212-vulnerability
Docker-based lab environment to exploit CVE-2023-30212, a cross-site scripting (XSS) vulnerability in OURPHP <= 7.2.0, with step-by-step setup and…
 libas7994/cve-2023-30212
Docker environment and exploit the CVE-2023-30212 is a security vulnerability that affects versions of OURPHP prior to or equal to 7.2.0 .This…
 libasmon/-create-a-vulnerable-docker-environment-that-is-susceptible-to-cve-2023-30212
Docker environment and exploit the CVE-2023-30212 vulnerabilityVE-2023-30212 is a security vulnerability that affects versions of OURPHP prior to or…
 cpyre/cve-2012-2982
Practice POC scripting in Tryhackme’s intro poc scripting room (For Linux)
 cure53/xsschallengewiki
Community-maintained wiki cataloging XSS challenges and solutions, providing curated hands-on exercises for learning cross-site scripting…
 lauleysen/cve-2024-46538
based on [EQSTLab](https://github.com/EQSTLab)
 0xtas/cve-2012-2982
Exploits CVE-2012-2982 in Webmin with a Rust PoC that delivers a configurable TCP reverse shell and optional Netcat listener.
 saku0512/cve-2026-9086-poc
CVE-2026-9086 proof-of-concept for Keycloak client URI validation bypass using mixed-case javascript: and data: XSS payloads, with Docker-based…
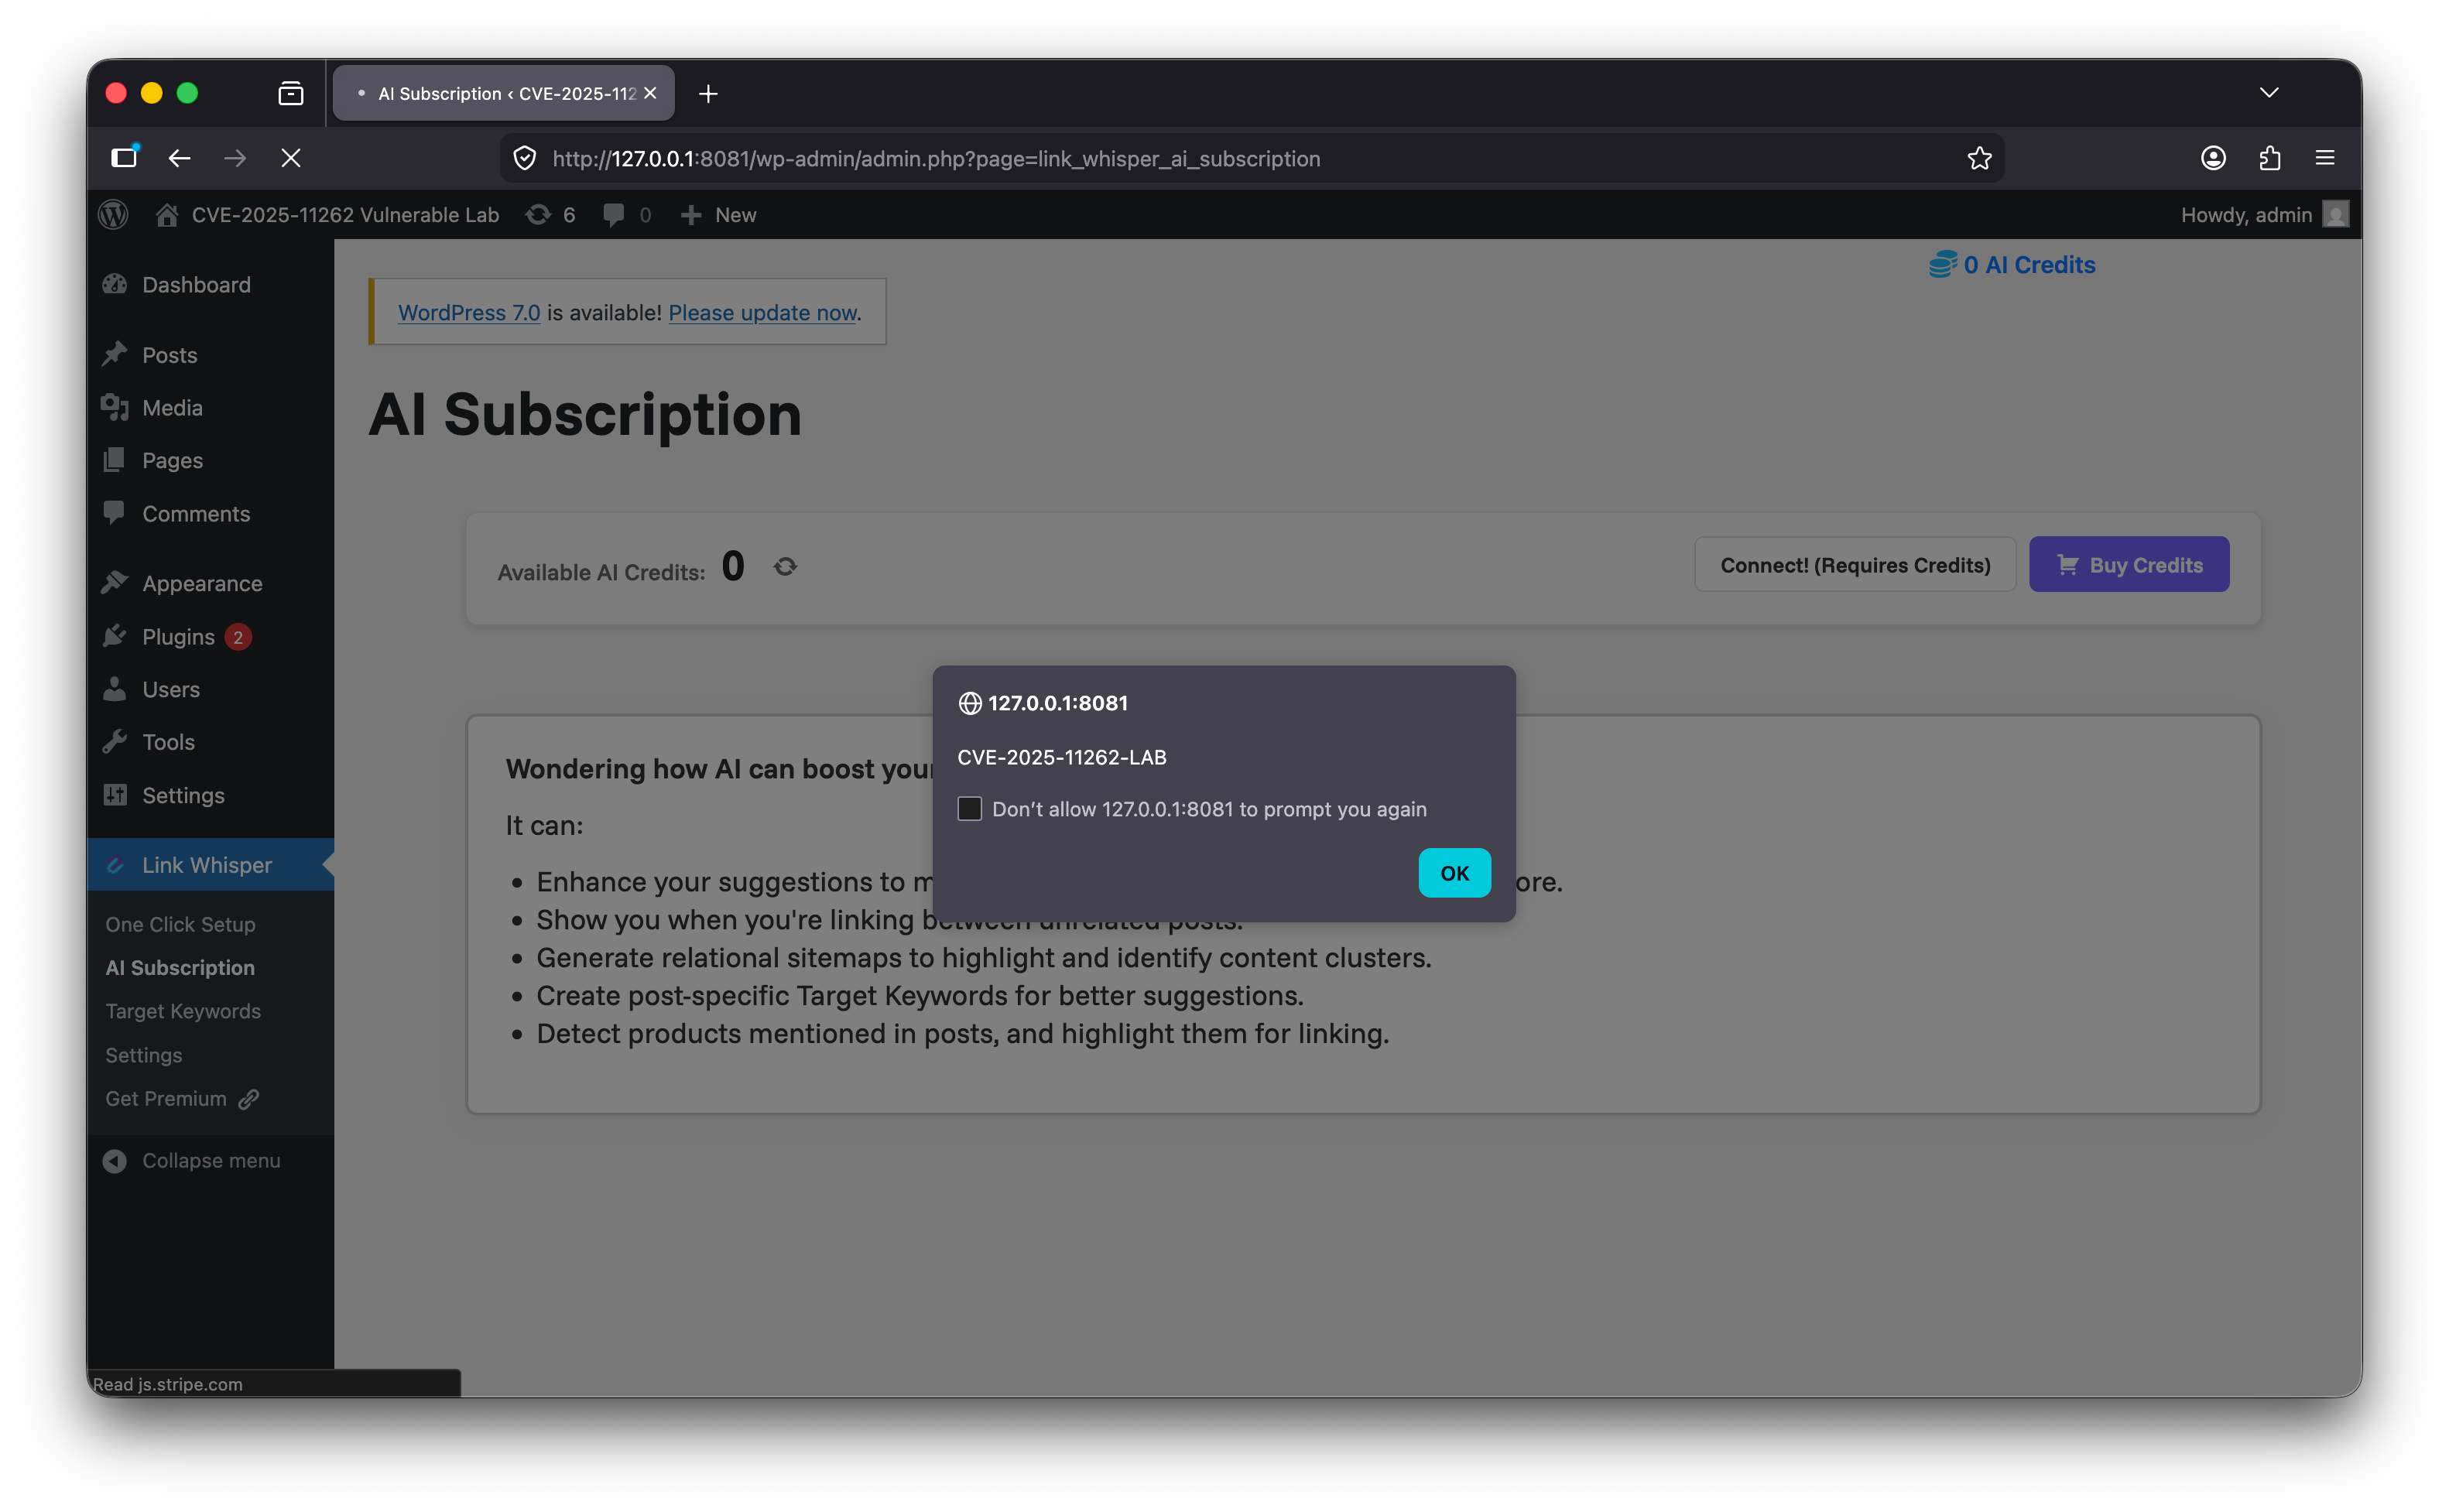 rootdirective-sec/cve-2025-11262-lab
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…
 zaidarif47/cve-2024-42009
Docker-based proof-of-concept for CVE-2024-42009, a stored XSS in Roundcube Webmail. Demonstrates exploitation via crafted HTML emails and includes…
 hackmelocal/cve-2021-24891-simulation
Containerized lab environment to simulate and exploit a DOM-based XSS vulnerability (CVE-2021-24891) in the Elementor WordPress plugin for hands-on…