
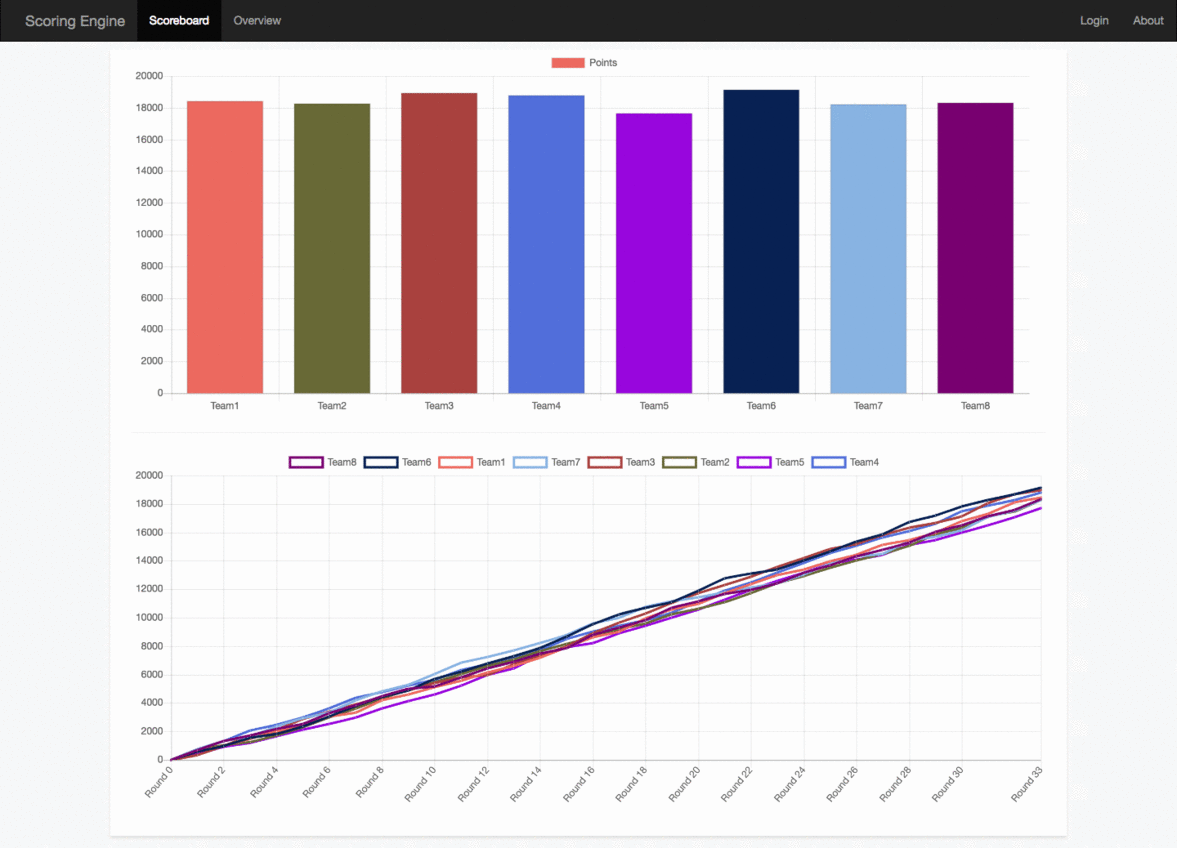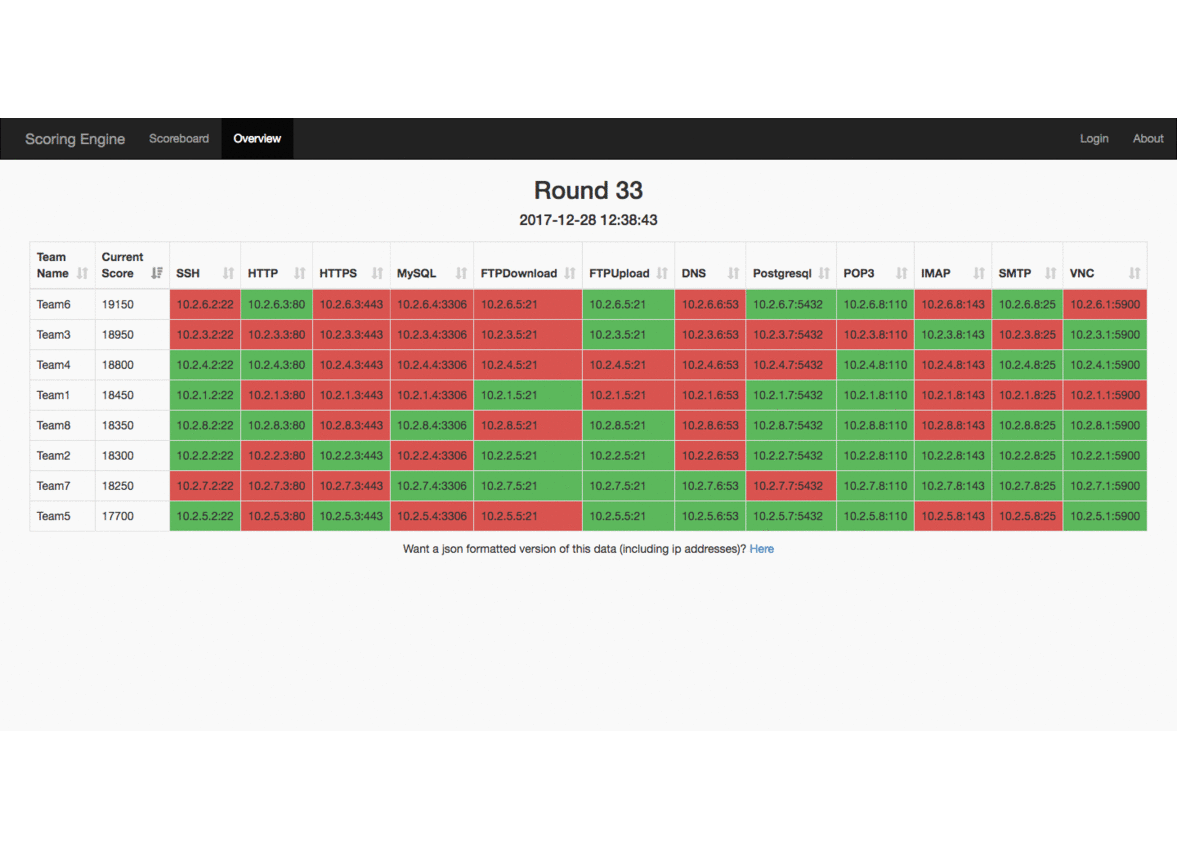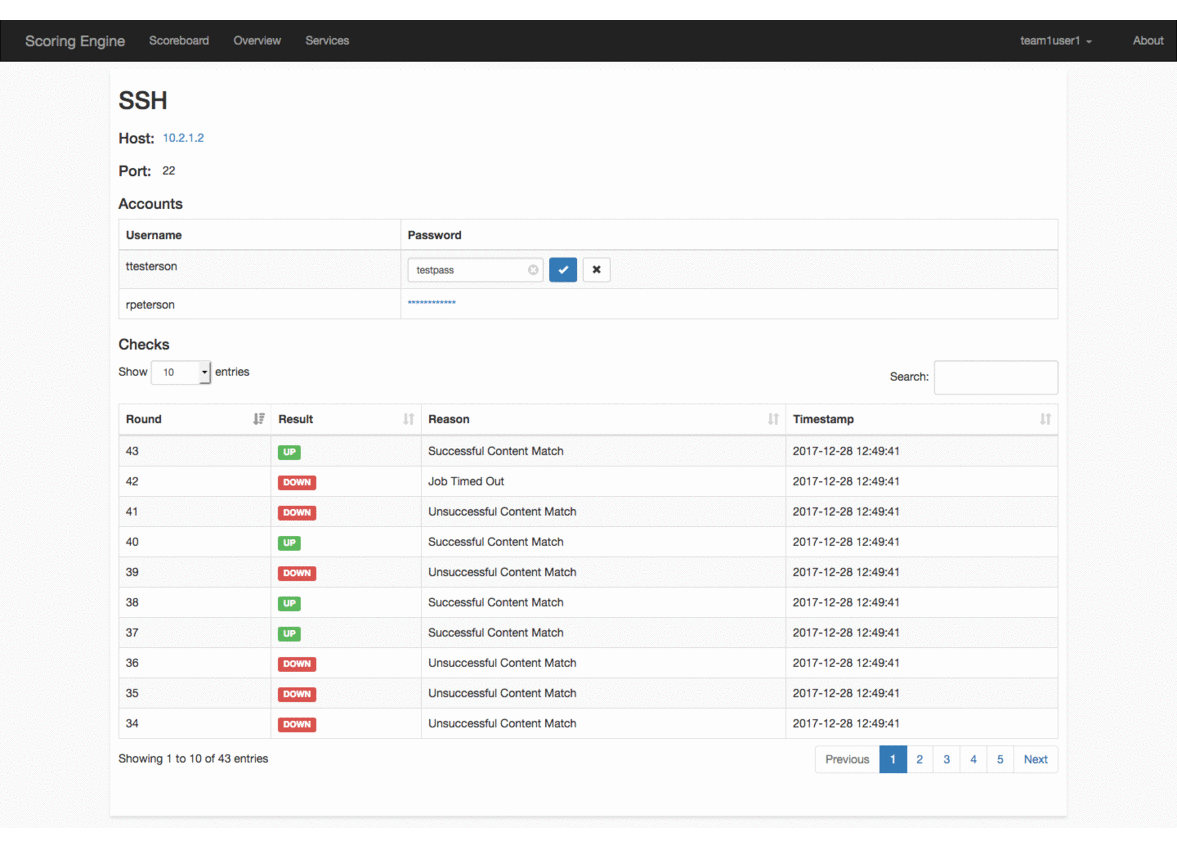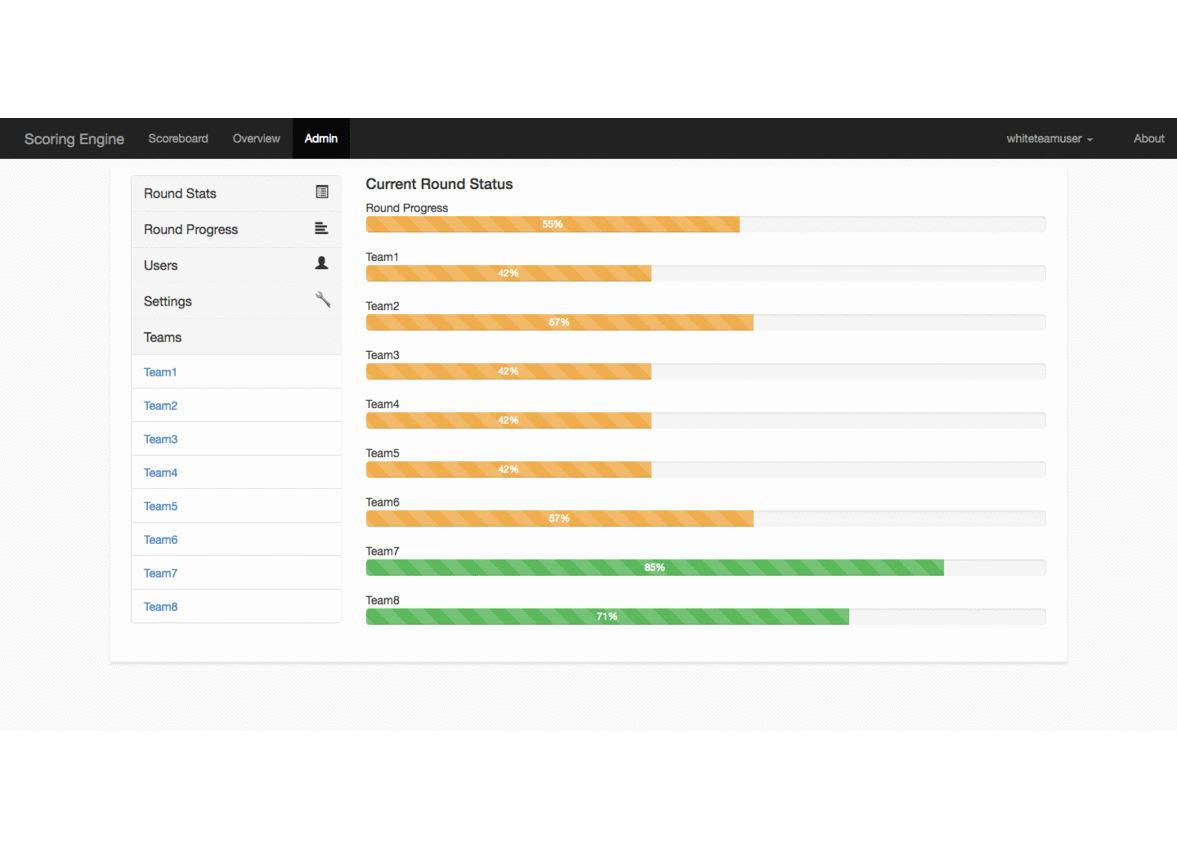
 scoringengine/scoringengine
Scoring Engine for Red/White/Blue Team Competitions
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
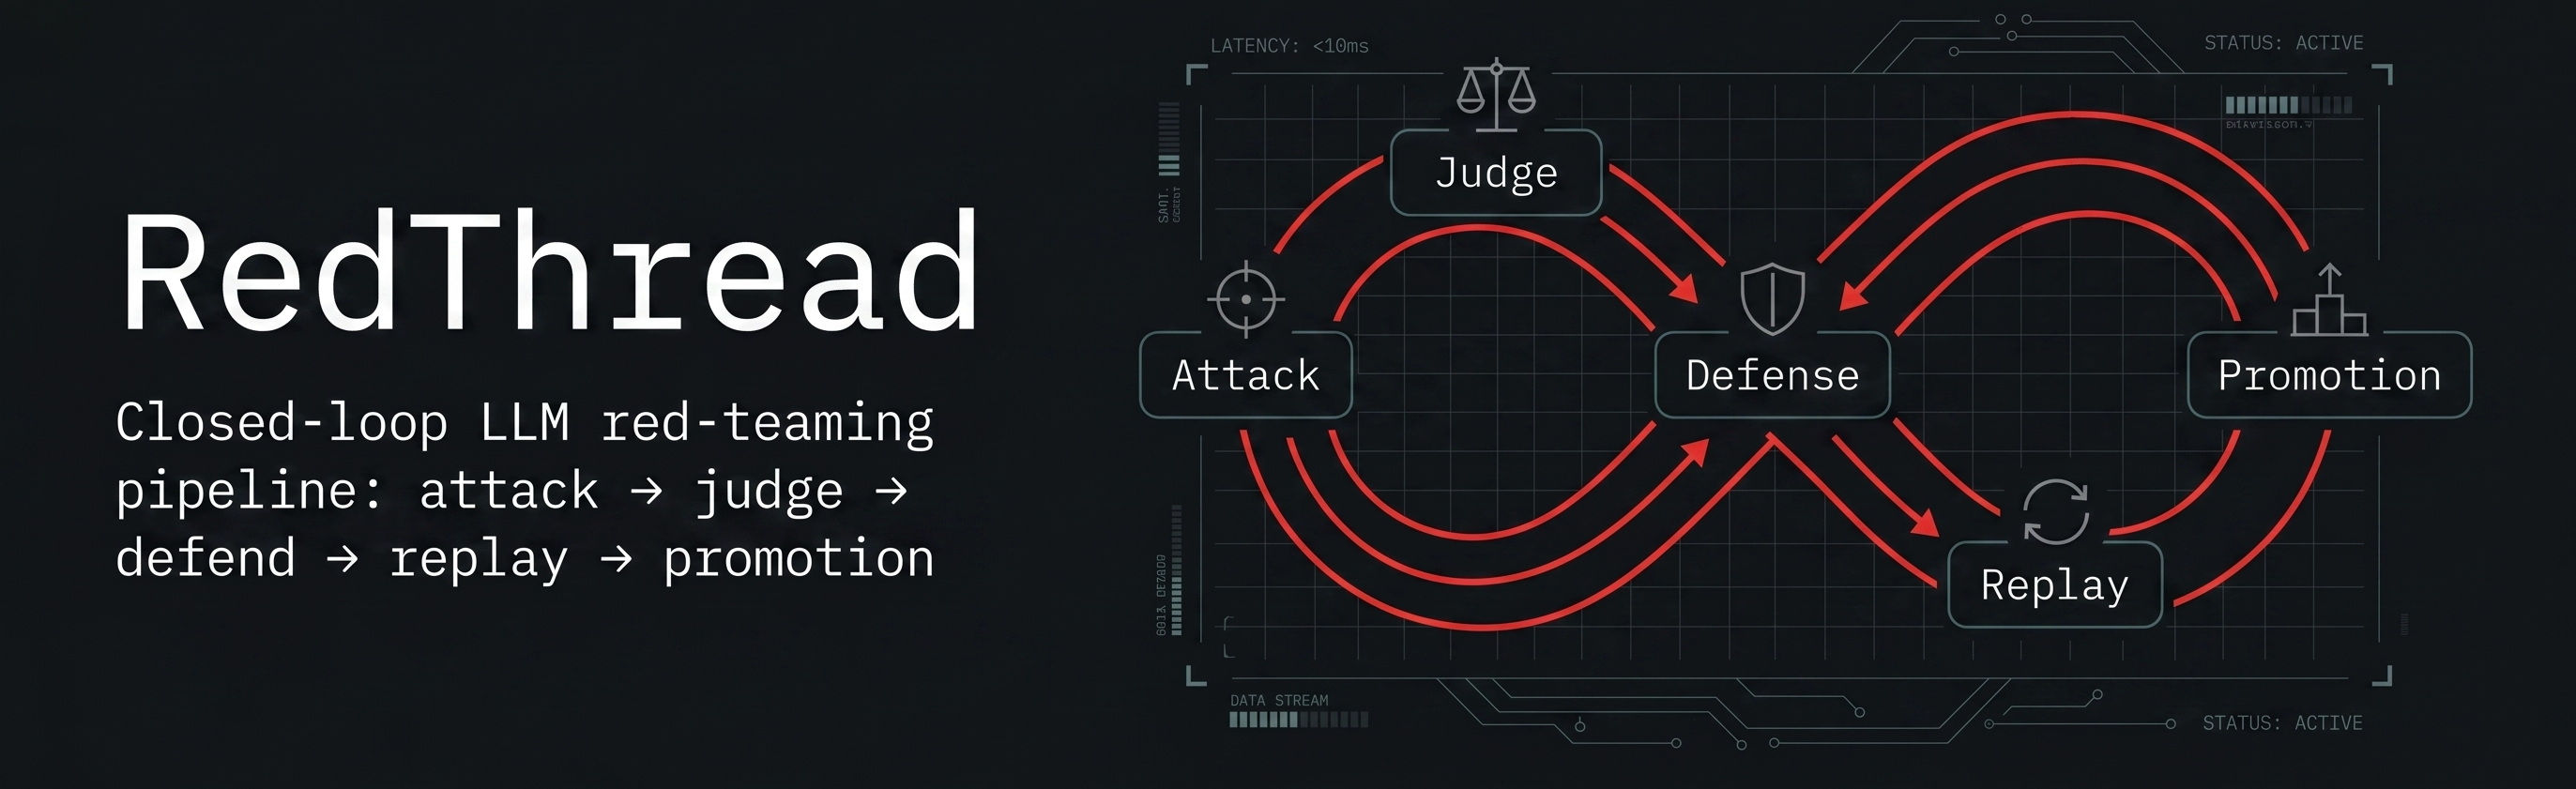 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 ninedeadeyes/s.p.a.r.k--standard-python-ascii-rpg-kit-
Light Weight 2d Ascii RPG Python Game Engine
 gmh5225/cve-2025-6554
Reproduction steps and proof-of-concept for CVE-2025-6554, a V8 engine vulnerability, with setup guides for macOS and Linux using ASAN builds.
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 4auvar/vulnnodeapp
Deliberately vulnerable Node.js web application for practicing exploitation of SQL injection, XSS, IDOR, command injection, XXE, and deserialization…
 t0kx/exploit-cve-2015-1427
Elasticsearch 1.4.0 < 1.4.2 Remote Code Execution exploit and vulnerable container
 wayang1337/cve-2026-11613
Divi Ajax Filter <= 5.1.2 Unauthenticated Local File Inclusion via 'custom_loop_template'
 arax-zaeimi/docker-container-cve-2020-13401
Study on CVE-2020-13401 vulnerability of containers in dockers older than 19.03.11
 rootdirective-sec/cve-2026-55255-lab
Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…
 covepseng/cve-2026-9558-poc
Exploitability PoC for CVE-2026-9558 (SSTI Mautic Theme)
 rootdirective-sec/cve-2026-42647-lab
Docker-based lab for reproducing CVE-2026-42647, an unauthenticated time-based blind SQL injection in the JoomSport WordPress plugin via the sortf…