

CVE-2024-23334
 binaryninja/cve-2024-23334
Expolit for CVE-2024-23334 (aiohttp >= 1.0.5> && <=3.9.1)
educationexploitationlabs-practice+2
binaryninja/cve-2024-23334Expolit for CVE-2024-23334 (aiohttp >= 1.0.5> && <=3.9.1)
 rufflabs/crushftp_cve-2025-31161
Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
 mehedi-hasan-sami98/dvwa-zap-pentest
Web application security assessment of DVWA using OWASP ZAP — vulnerability scanning, RCE (CVE-2012-1823) analysis, and remediation report.
 ramadhanamizudin/lazyweb
LazyWeb is a demonstration web application designed to showcase common server-side application vulnerabilities. Each vulnerability is categorized…
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 artemcyberlab/project-project-chimera-exploiting-a-modern-wordpress-xxe-to-pillage-secrets-
The objective is to conduct a full-scale security assessment of a WordPress-based web application, culminating in a complete server compromise. The…
 yavuzlar/vulnlab
Deliberately vulnerable web application lab for practicing exploitation of SQLi, XSS, CSRF, SSTI, IDOR, XXE, and 15+ other common web security flaws…
 hmlio/vaas-cve-2014-6271
Vulnerability as a service: showcasing CVS-2014-6271, a.k.a. Shellshock
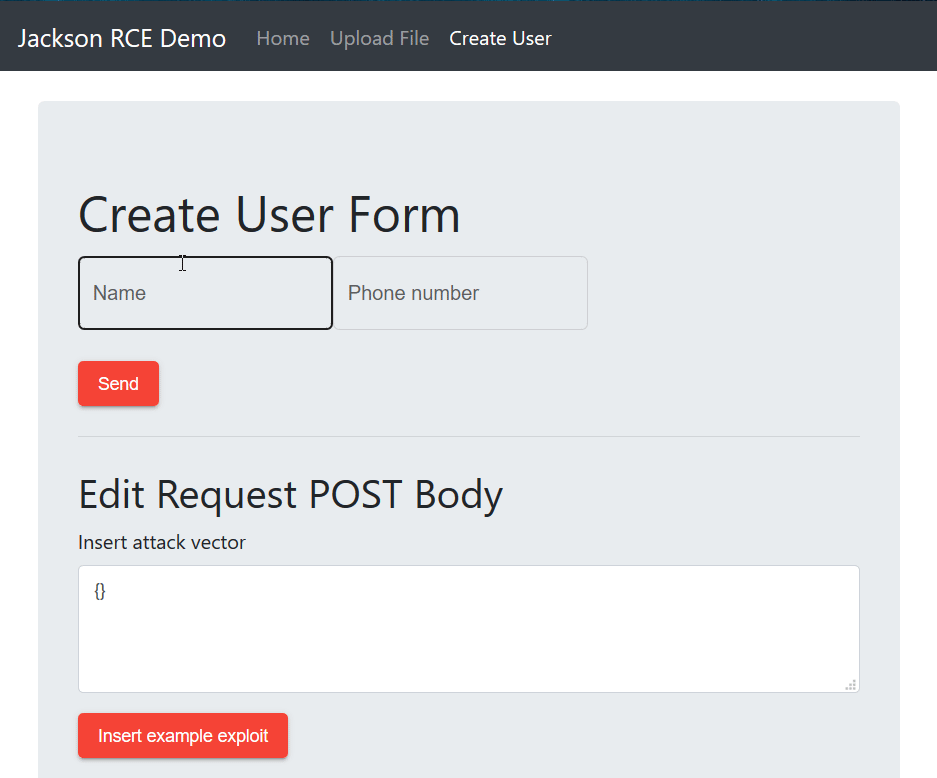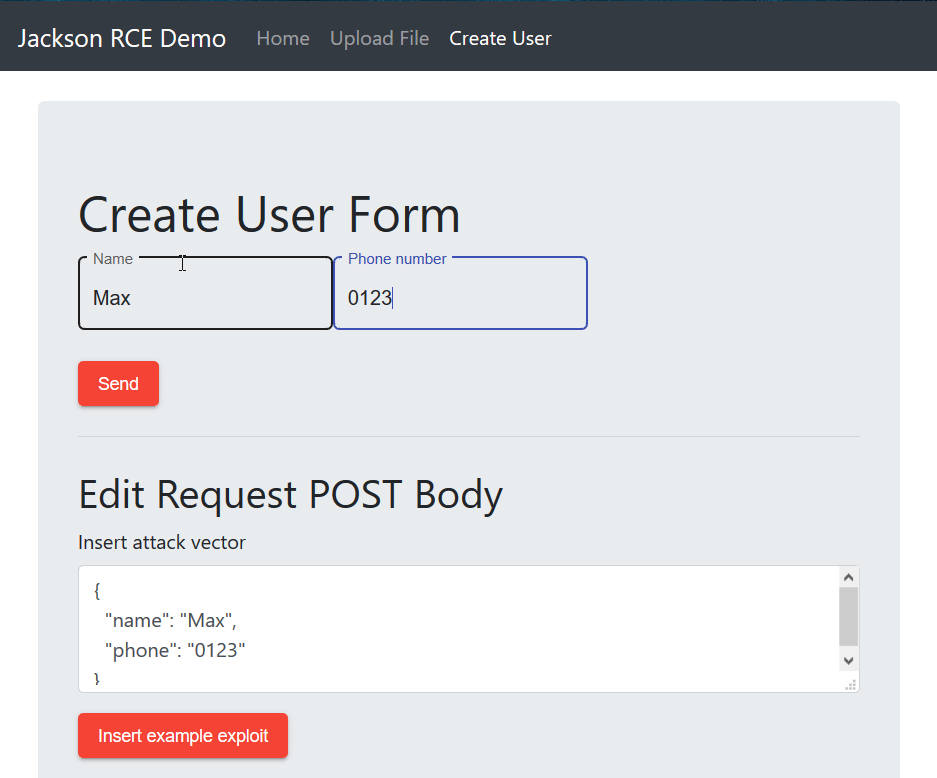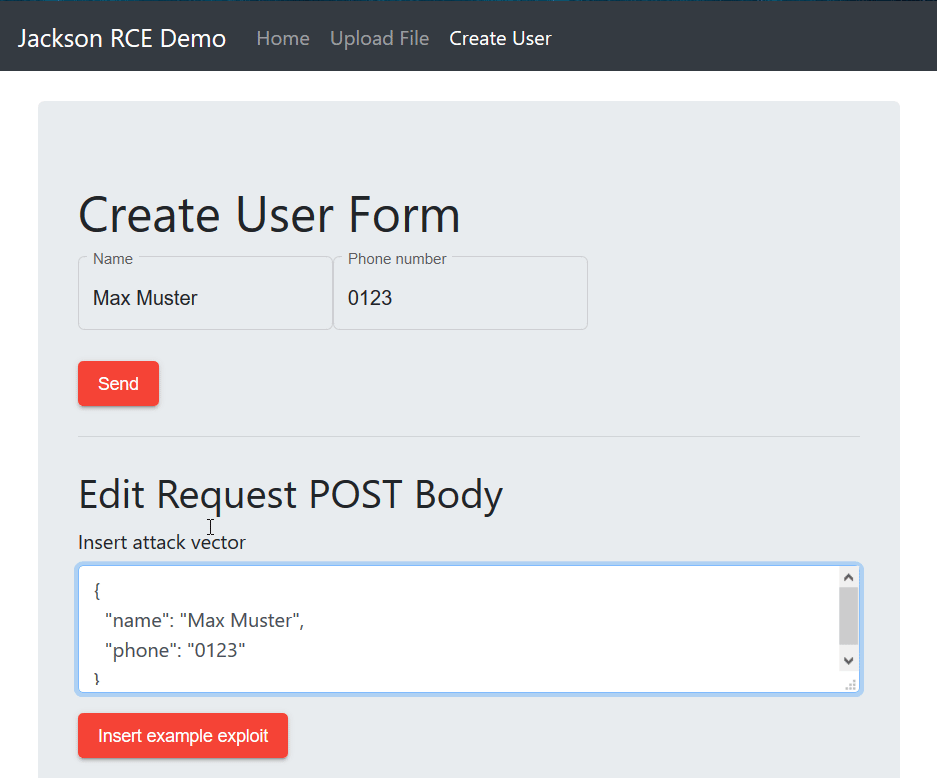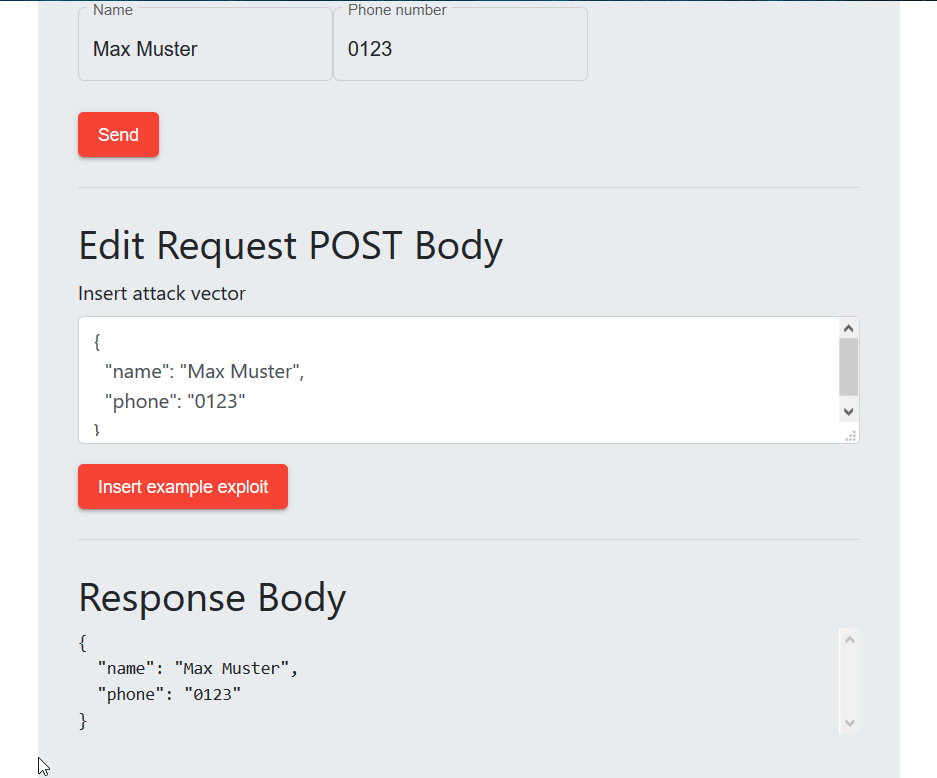 javanxd/demo-exploit-jackson-rce
Exploiting CVE-2017-7525 demo project with Angular7 frontend and Spring.
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 alastair66/cve-2025-29927
Next.js Middleware Bypass Vulnerability
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
 pierfrancescoconti/leaflet-cve-2025-69993
Proof-of-concept for CVE-2025-69993: Cross-Site Scripting in Leaflet's bindPopup() method. Includes advisory, impact analysis, and a demo Angular…
 neerazz/cve-2022-42889
Proof-of-concept application demonstrating CVE-2022-42889 RCE vulnerability in Apache Commons Text 1.9 with reproducible exploit steps for security…
 tadash10/exploiting-cve-2021-44228-log4shell-in-a-banking-environment
Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.
 kazuya256/next-js-auth-bypass
🔓 Next.js Auth Bypass Demo - Educational application demonstrating CVE-2025-29927 middleware authentication bypass vulnerability . ⚠️ For…
 lunasec-io/spring4shell-poc
This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).