
CVE-2026-42945
 yusufdalbudak/cve-2026-42945
Dockerized lab for training on NGINX rewrite vulnerability (CVE-2026-42945) with vulnerable and patched instances, benign test scripts, and…
configuration-auditingctfeducation+3
yusufdalbudak/cve-2026-42945Dockerized lab for training on NGINX rewrite vulnerability (CVE-2026-42945) with vulnerable and patched instances, benign test scripts, and…
 guigui237/exploitation-de-la-vuln-rabilit-cve-2015-5254-
Step-by-step exploitation guide for Apache ActiveMQ CVE-2015-5254 deserialization vulnerability using jmet, with Docker-based lab setup and…
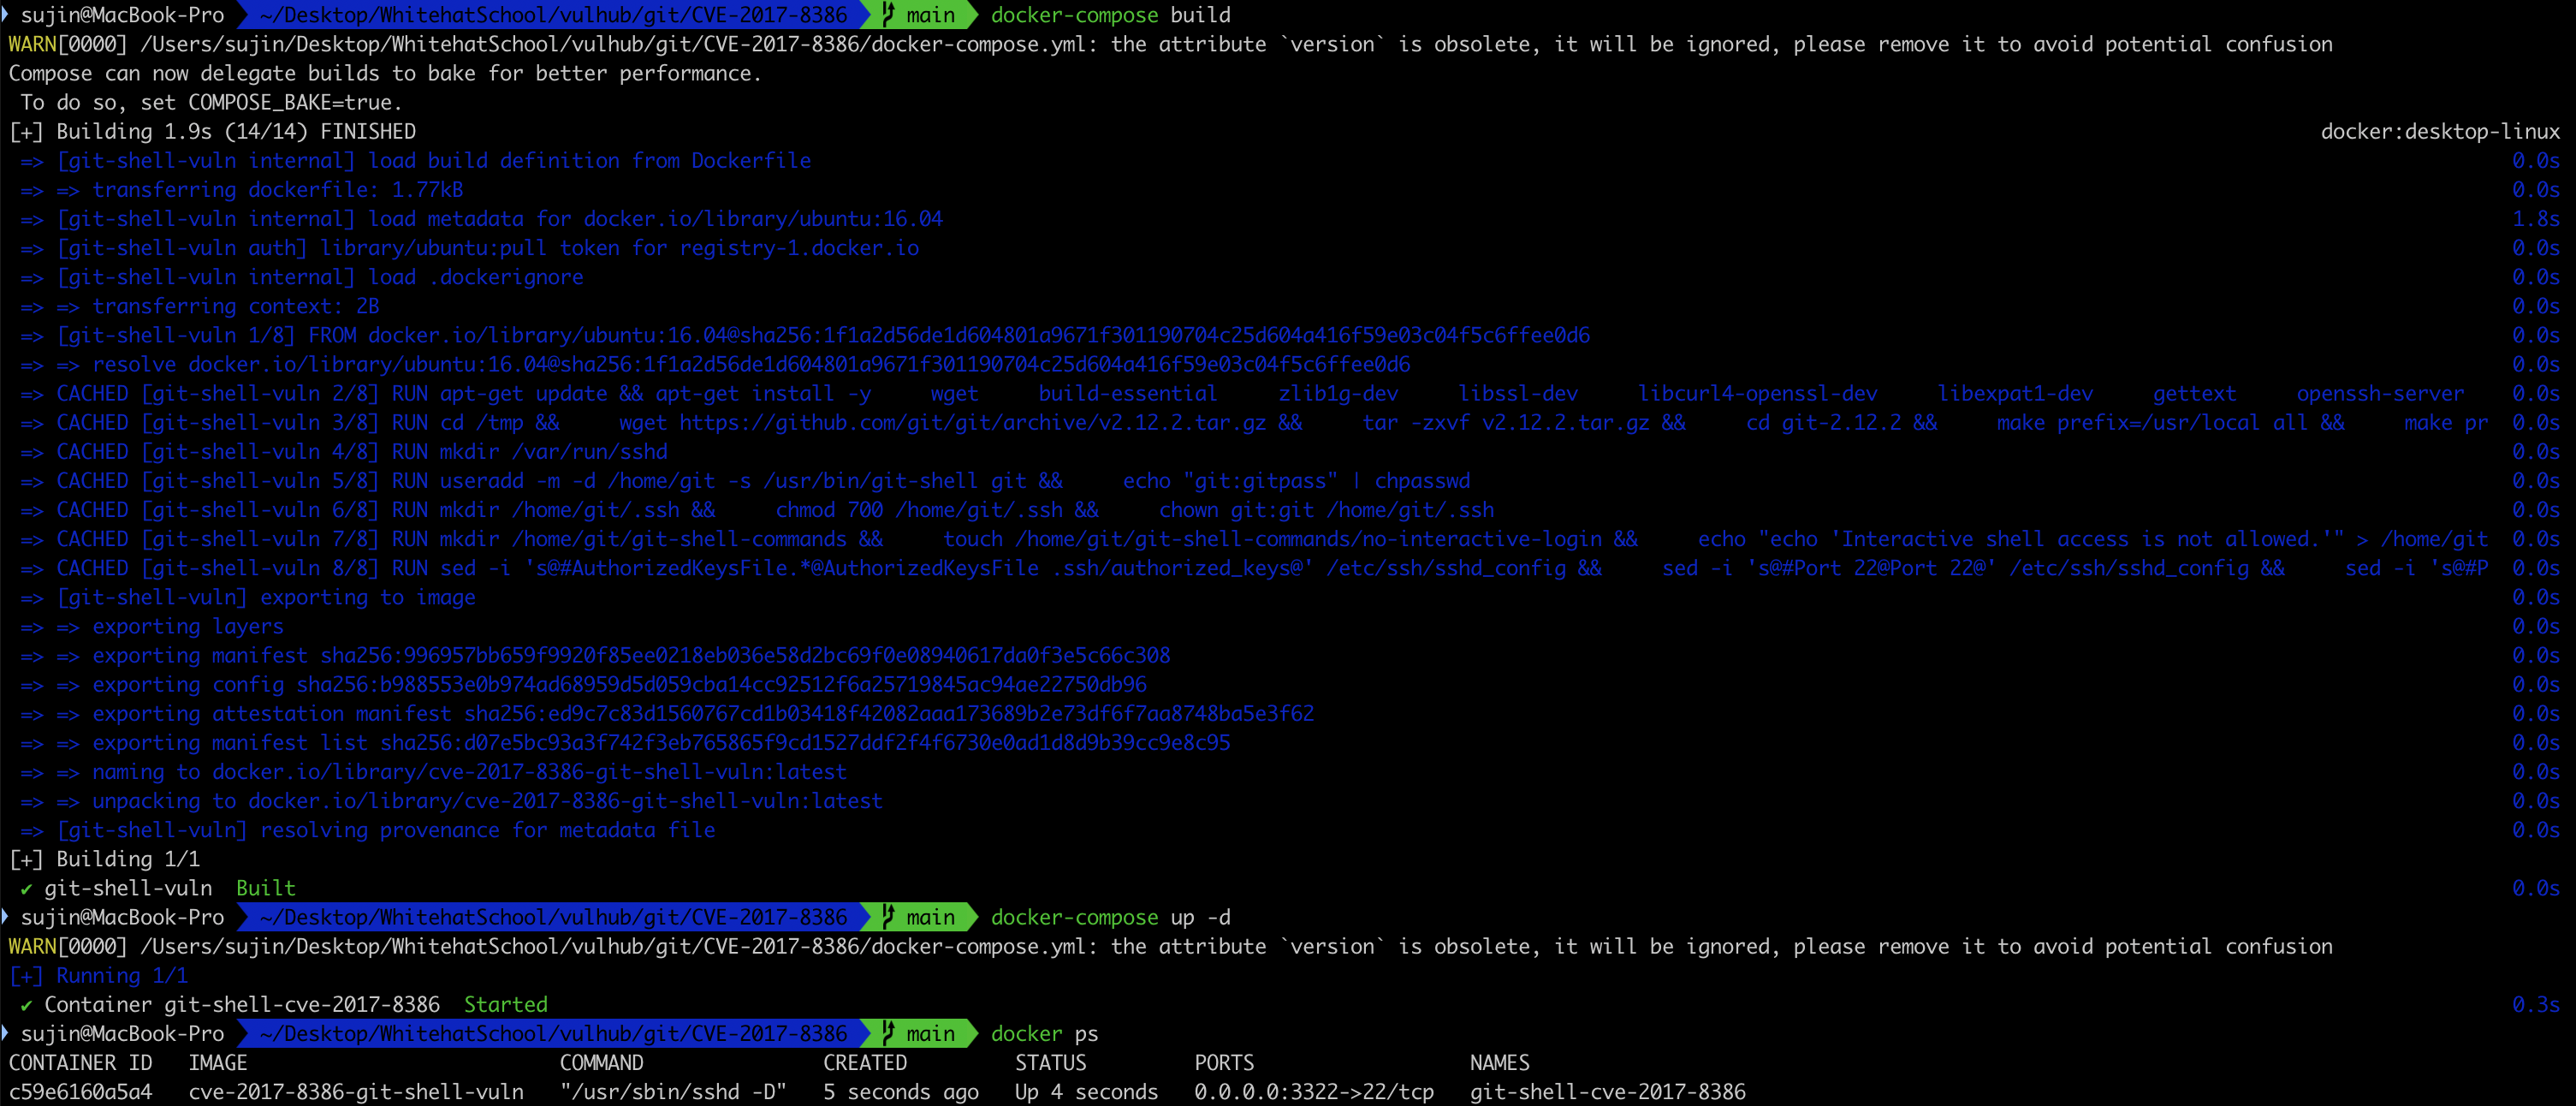 suz1n/whs3_vulhub
PoC for CVE-2017-8386 Git-Shell sandbox bypass vulnerability.
 ptantiku/cve-2015-2208
Docker simulating cve-2015-2208 vulnerability
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)
 kre80r/cve-2025-13486-vuln-setup
Docker test environment for CVE-2025-13486 (ACF Extended RCE). For security research only.
 t0kx/exploit-cve-2016-9920
Roundcube 1.0.0 <= 1.2.2 Remote Code Execution exploit and vulnerable container
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 fullhunt/react2shell-test-server
A test server for demonstrating and testing React2Shell (CVE-2025-55182) vulnerability
 kingsrule50/nessus-vulnerability-scanning-lab
Enterprise vulnerability management on Azure — Terraform-deployed Nessus scanner, credentialed scanning, CVE-2013-3900 remediation with verified…
 mkirahmet/poc-2023-43208
A proof-of-concept exploit for CVE-2023-43208, a remote code execution vulnerability in Mirth Connect before version 4.4.1.
 kuttappu123/cve-2023-30212-lab
Hands-on lab environment for exploiting CVE-2023-30212, a stored XSS vulnerability in OURPHP ≤7.2.0, using Docker containers for safe penetration…
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…
 aash035/cve-2023-30212
Docker-based vulnerable OURPHP lab for reproducing CVE-2023-30212, a reflected XSS vulnerability, with setup instructions and proof-of-concept…
 c-h4ck-0/learn-about-cve-2025-31133-poc
Educational proof-of-concept for CVE-2025-31133, a runc container escape via maskedPaths race condition. Includes lab setup, exploit script, and…
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…