
EXPLOIT-CVE-2024-7804
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
binary-exploitationeducationexploitation+2
joaovicdev/exploit-cve-2024-7804Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
 cr4zyd14m0nd137/lab-for-cve-2018-15133
Ejecución de exploit de deserialización con CVE-2017-5941
 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 redcanaryco/atomic-red-team
Small and highly portable detection tests based on MITRE's ATT&CK.
 p0dalirius/awesome-rce-techniques
Awesome list of step by step techniques to achieve Remote Code Execution on various apps!
 guayoyocyber/cve-2022-22965
Vulnerabilidad RCE en Spring Framework vía Data Binding on JDK 9+ (CVE-2022-22965 aka "Spring4Shell")
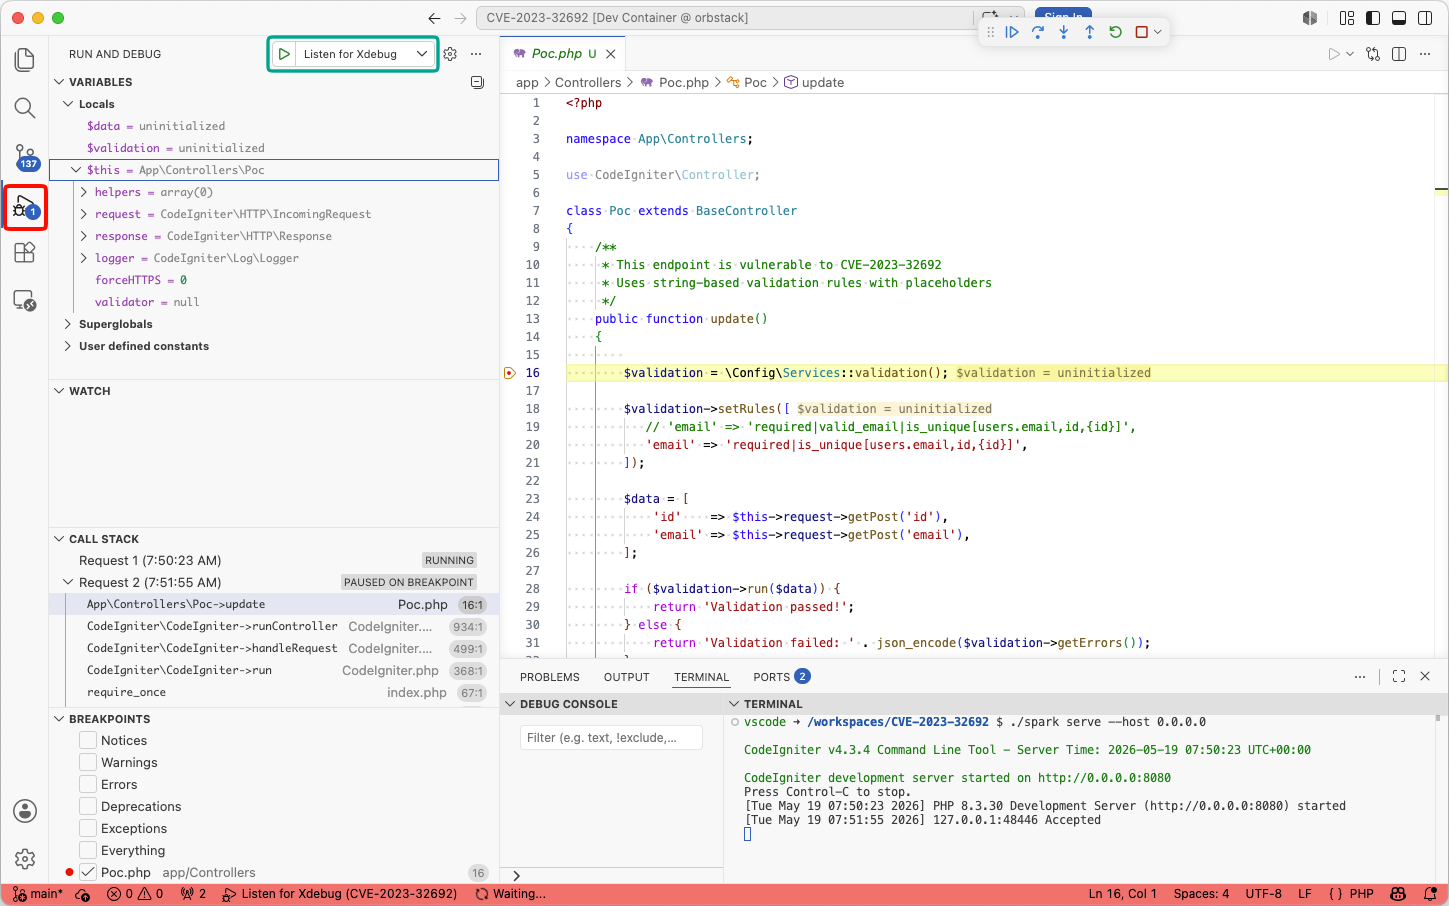 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 indiquarks/vsftpd-cve-2011-2523-lab
Pen Tesing Lab exploiting VSFTPD 2.3.4 backdoor via Metasploit Framework
 meng-security/spring4shell-local-verification-lab
Spring Framework CVE-2022-22965 本地影响条件验证、版本升级修复与复测项目
 johanmv/explotacion-vsftpd-nmap_laboratorio_1
Laboratorio técnico de ciberseguridad donde se realiza reconocimiento de red con Nmap y explotación de la vulnerabilidad CVE-2011-2523 (vsftpd 2.3.4)…