needrestart-sudo-escalate-cve-2024-4890

PoC exploit for CVE-2024-4890: Sudo privilege escalation via neecdrestart (>=3.8). Ethical lab-only. Scripts in Python and C.

PoC exploit for CVE-2024-4890: Sudo privilege escalation via neecdrestart (>=3.8). Ethical lab-only. Scripts in Python and C.

Disclosure pack and PoC for CVE-2026-96512, a sudo NOTBEFORE/NOTAFTER TZ time-window bypass enabling local privilege escalation, with lab…

🔍 Demonstrate the CVE-2025-32463 privilege-escalation flaw in sudo's chroot feature with this minimal, reproducible proof of concept environment.

Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…

Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…

Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…

CVE-2021-3156 (Baron Samedit) Report and Research

A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig

Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…

Exploitation and mitigation analysis of CVE-2021-3156 heap-based buffer overflow in sudo

Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…

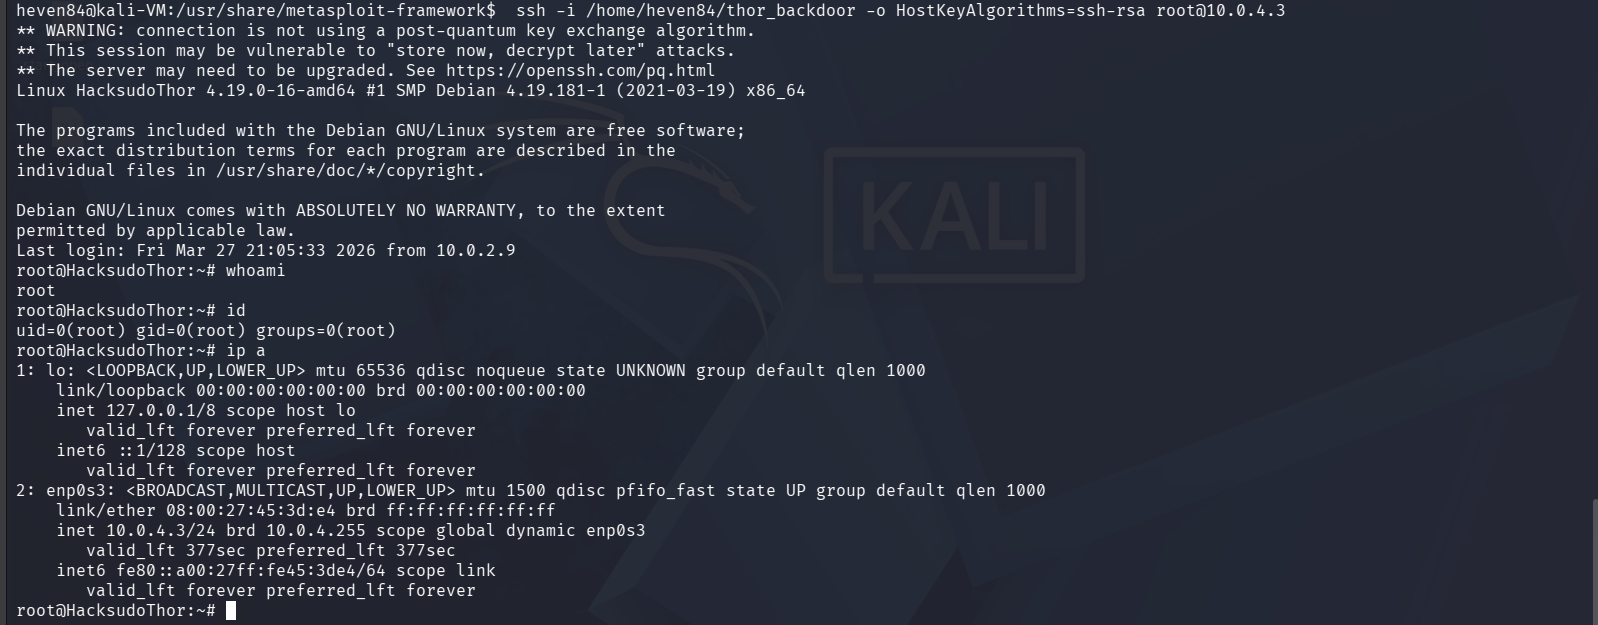
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Proof-of-concept exploit for CVE-2023-42456, demonstrating privilege escalation via sudo NSS library hijacking through chroot injection. Includes…

Docker-based lab environment for reproducing and exploiting CVE-2026-1357, with step-by-step setup and Burp Suite exploitation guidance.

Lab environment and proof-of-concept exploit for CVE-2026-1357, a WordPress plugin vulnerability, with Docker setup and automated exploitation…

Red Team exploitation of CVE-2021-3156 (Baron Samedit) – Heap Buffer Overflow in Sudo leading to Local Privilege Escalation on Ubuntu 20.04

A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".

A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…