
 mhaggis/security-detections-mcp
MCP to help Defenders Detection Engineer Harder and Smarter
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
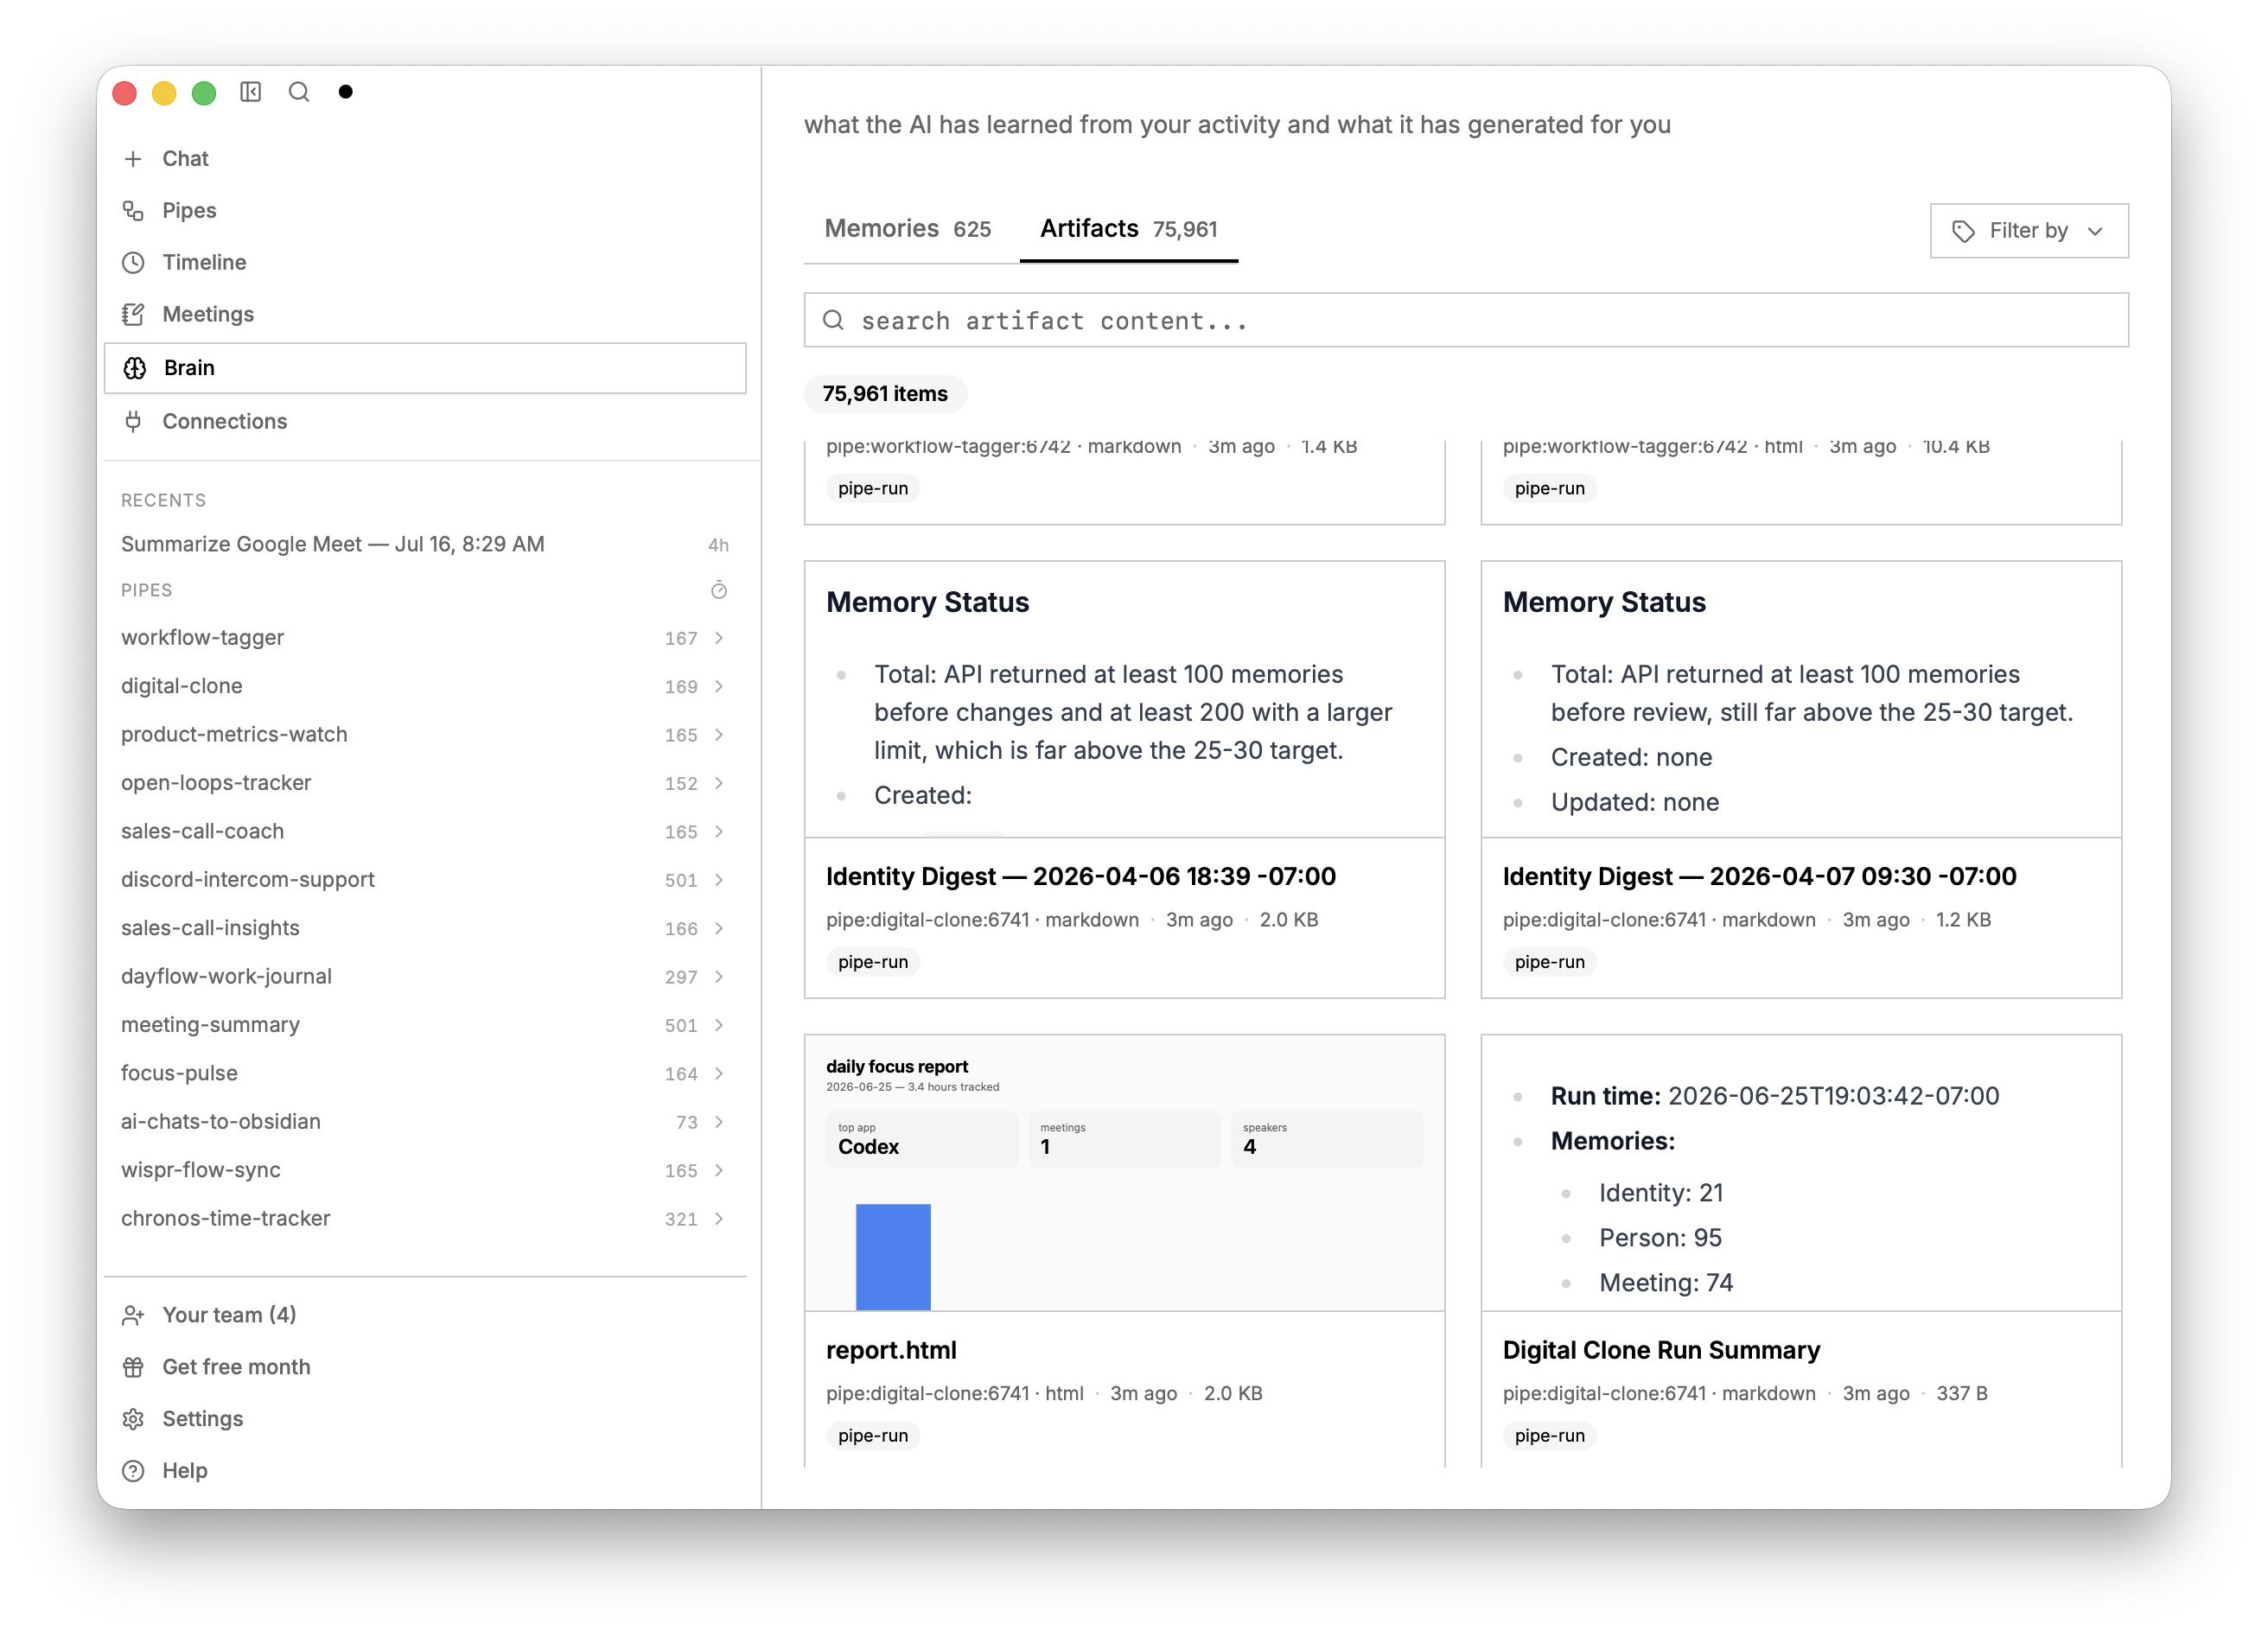 screenpipe/screenpipe
YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 splunk/attack_range
A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
 abraxas/keycloak-saml-redirect-param-split
Loopback PoC for a Keycloak 26.8.1 SAML broker flaw: a percent-encoded duplicate SAMLResponse name bypasses redirect signature verification, allowing…
 abraxas/keycloak-manage-users-composite
Keycloak 26.8.1 Medium 6.6 Remote authenticated auth leftover. A help-desk admin with manage-users can pin a pre-built composite of manage-realm onto…
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 blackhillsinfosec/freelabfriday_labs
This repository contains all lab instructions for the following content: Info Sec Core Skills, SOC Core Skills, ADCD Labs, SOC Analyst Labs, & BnB…
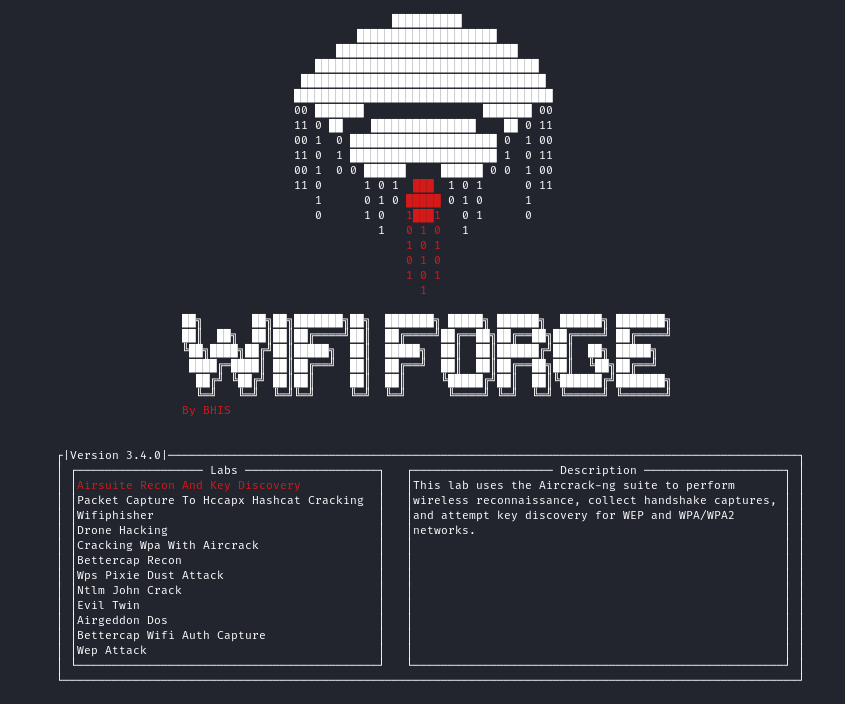 blackhillsinfosec/wififorge
Automated WiFi hacking lab environment using mininet-wifi to simulate wireless attack vectors for pentester training, eliminating hardware overhead.
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
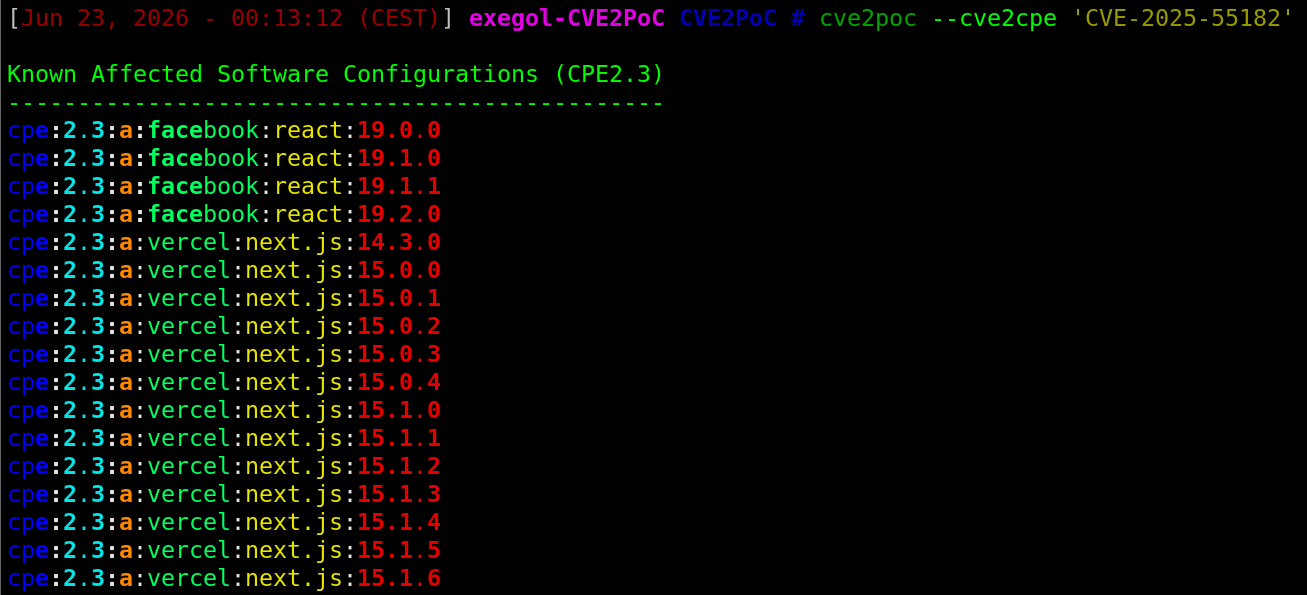 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID