ULTIMATE-CYBERSECURITY-MASTER-GUIDE

This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

Building 70 Projects ranging from beginner to advanced so anyone can — learn from, build upon, use as a reference, or even copy directly. Owned by my…

CVE-2026-50416: Windows 11 KASLR bypass

Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…

Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…

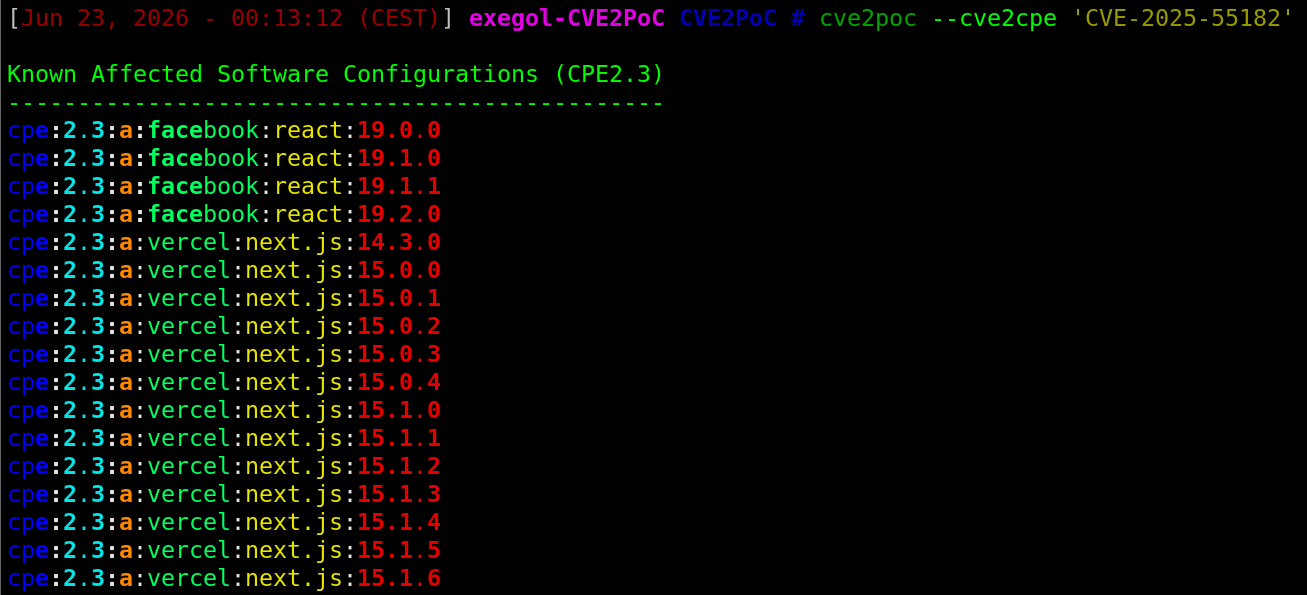
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID

Diagnostic LLM safety benchmark with 3,489 bilingual prompts, an 84-label taxonomy, and prompt-level rubric judging for explainable, fine-grained…

Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…

Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…

Collection of methodology and test case for various web vulnerabilities.

Jellyfin Server 12.2 - High - Remote - IDOR - public playlist ItemIds leftover of GHSA-9x85 then unauth stream

pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - ACB userkey capability URL

Automated WiFi hacking lab environment using mininet-wifi to simulate wireless attack vectors for pentester training, eliminating hardware overhead.

Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…

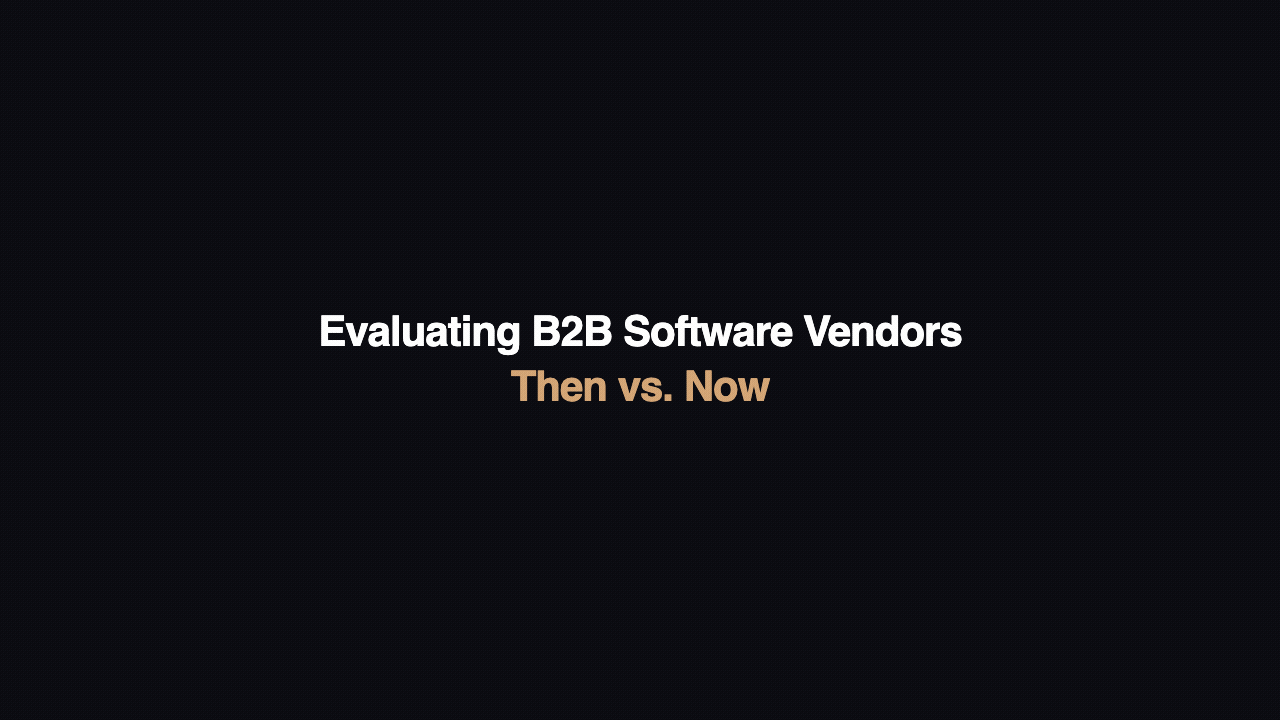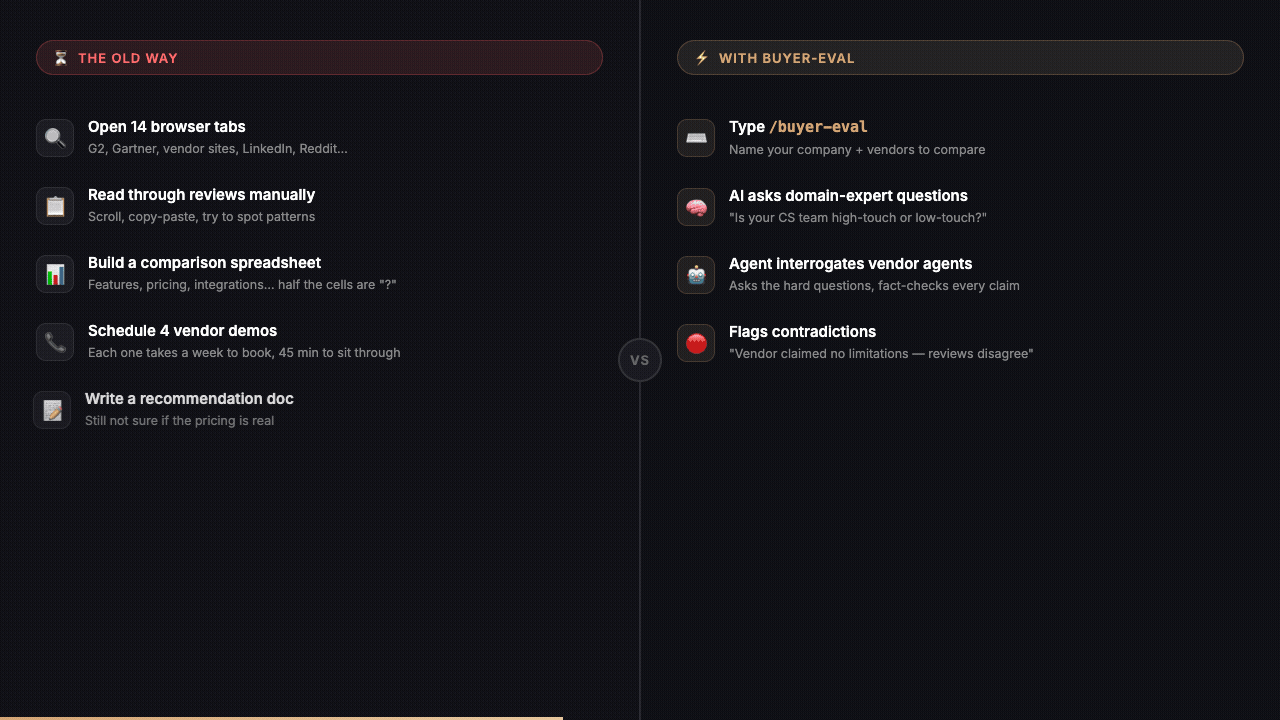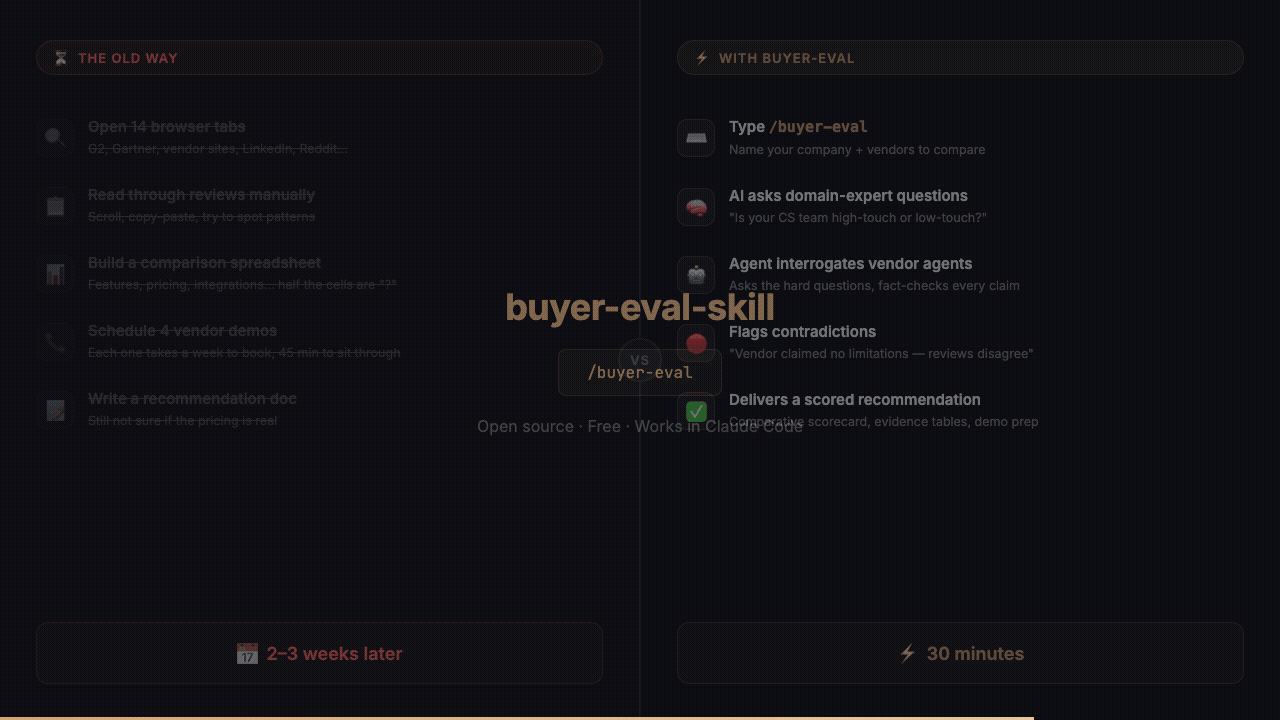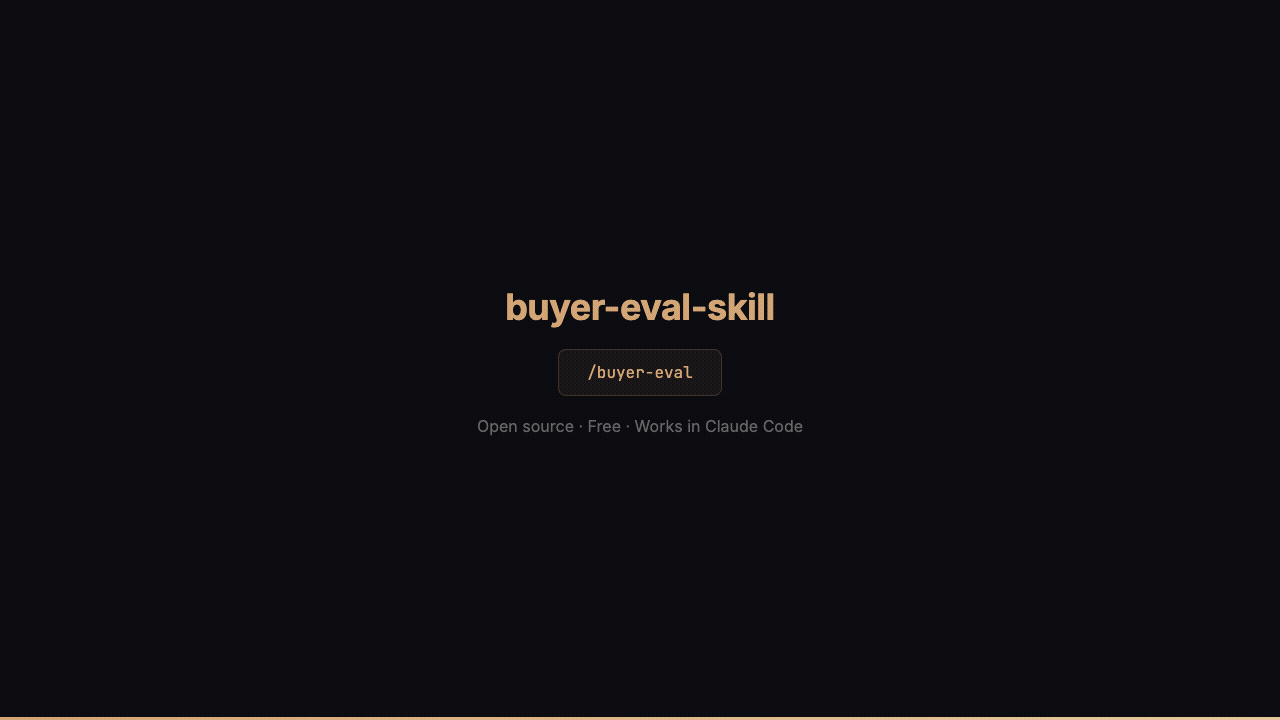
B2B software vendor evaluation skill for Claude Code — domain-expert questions, vendor AI agent conversations, evidence-based scoring

Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…

PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…