
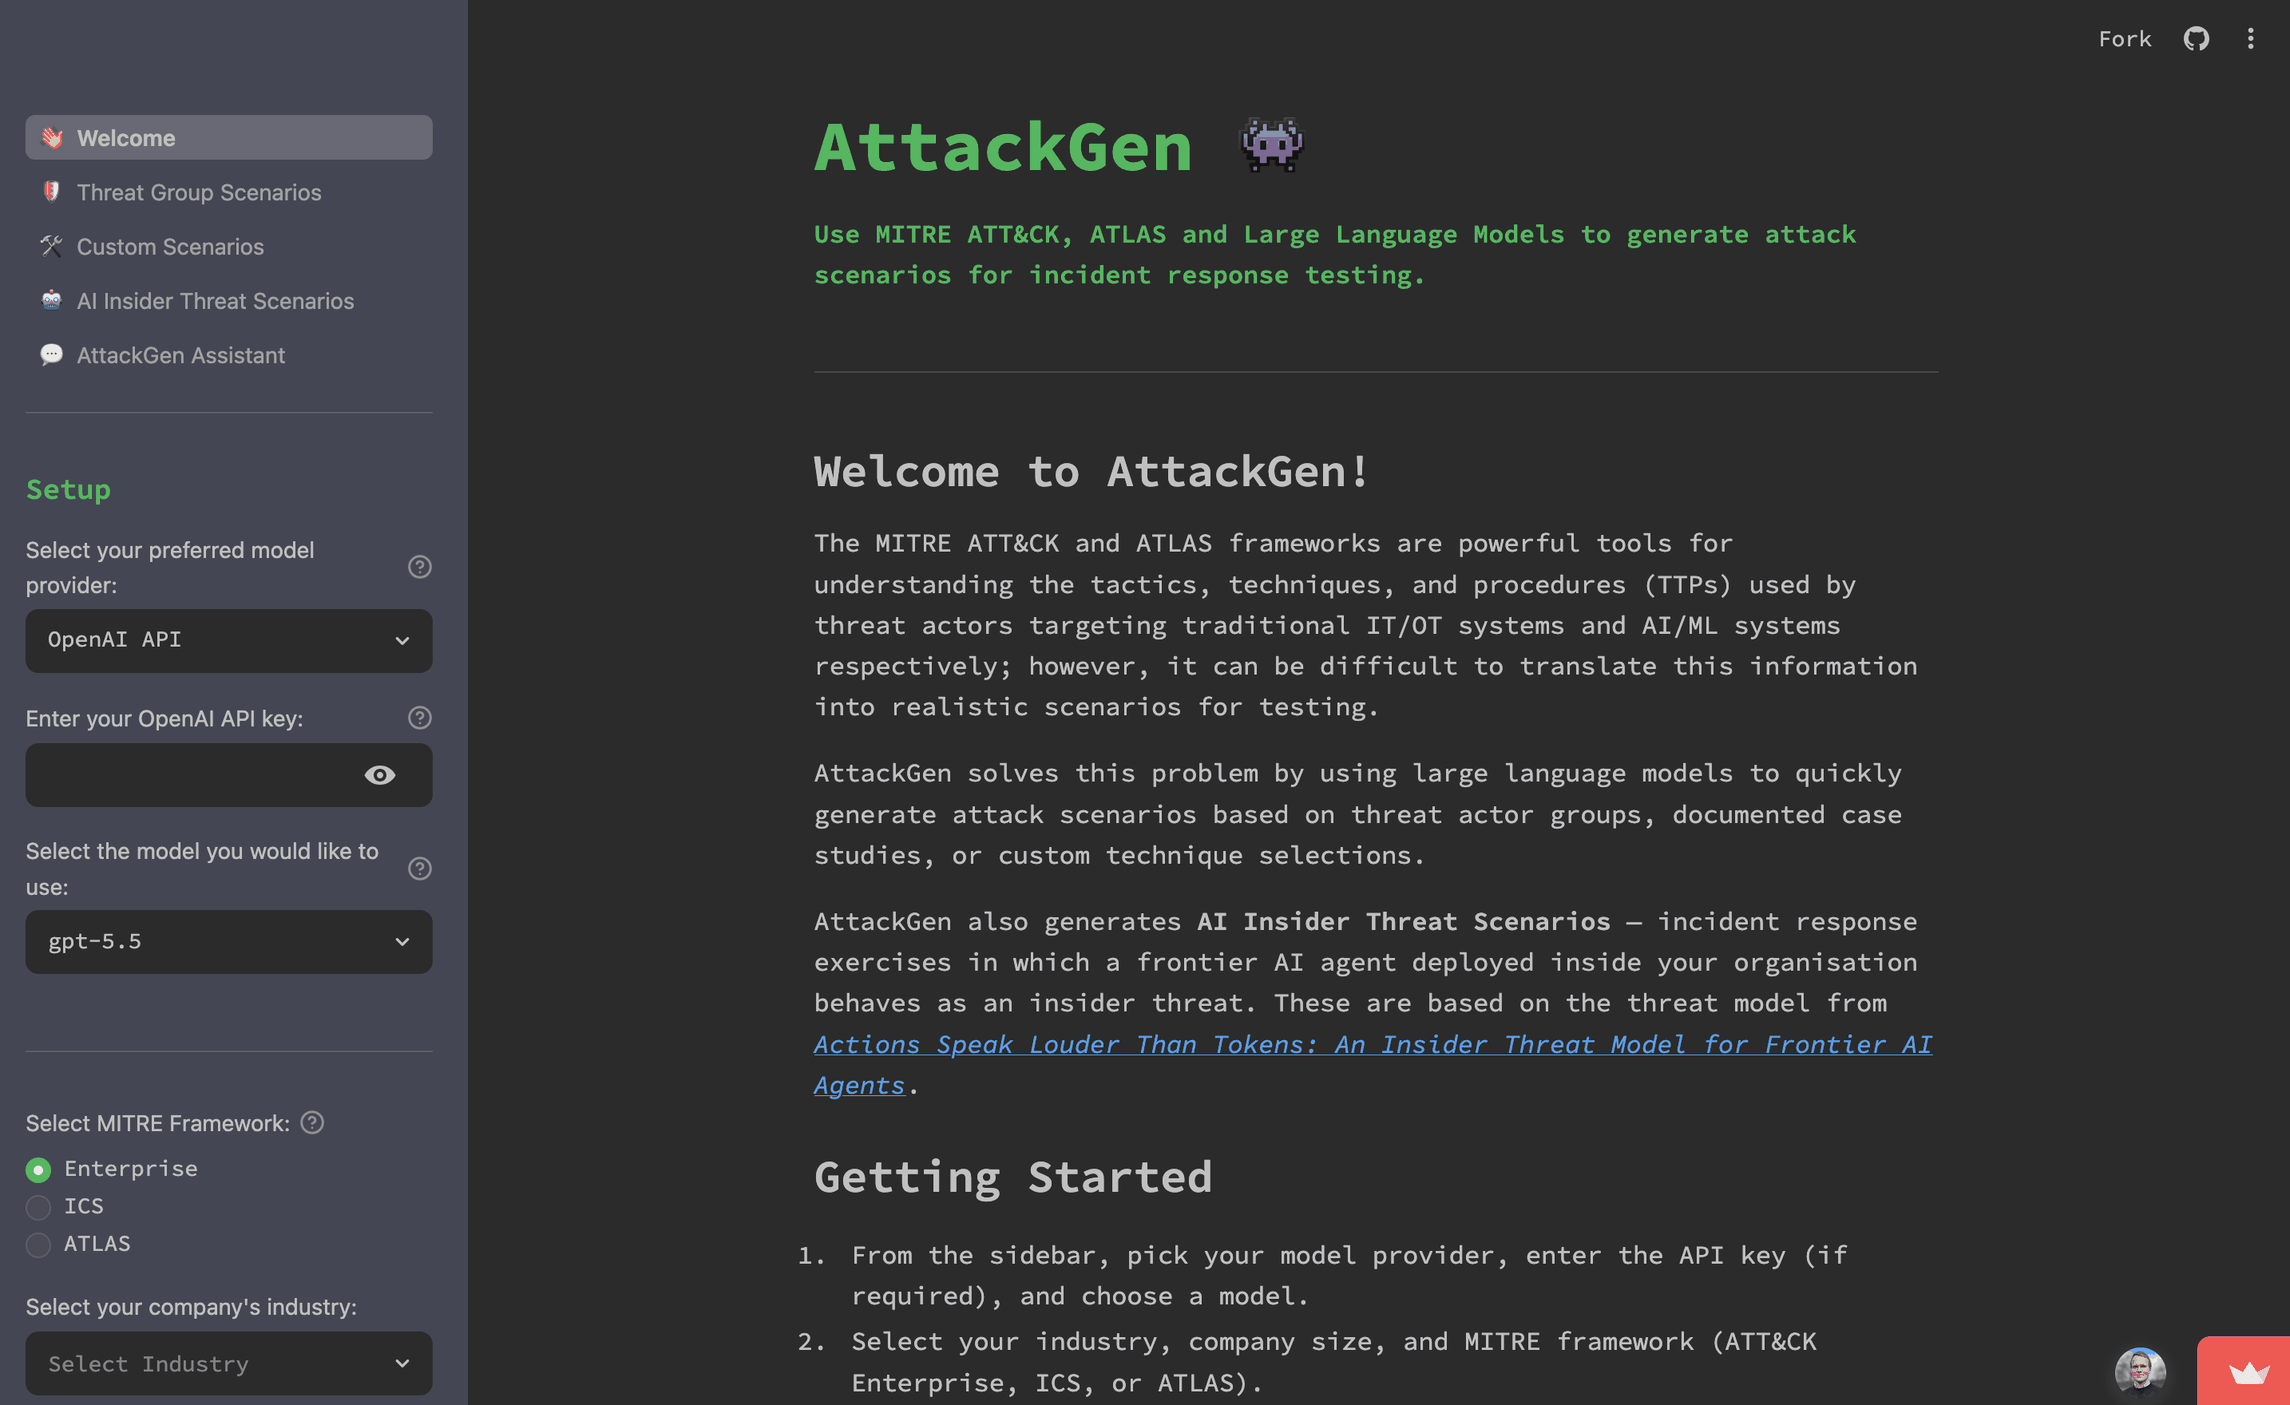
attackgen
 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
ai-securityctfeducation+5
1.2k
mrwadams/attackgenAttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 americooo/pentest-writeups
Kioptrix Level 1 writeup - CVE-2003-0201 Samba trans2open
 thenareshofficial/cve-2021-3129-lab
CVE-2021-3129: Laravel Debug Mode RCE - Complete exploitation lab with Python exploit, Docker container, and security analysis guide.
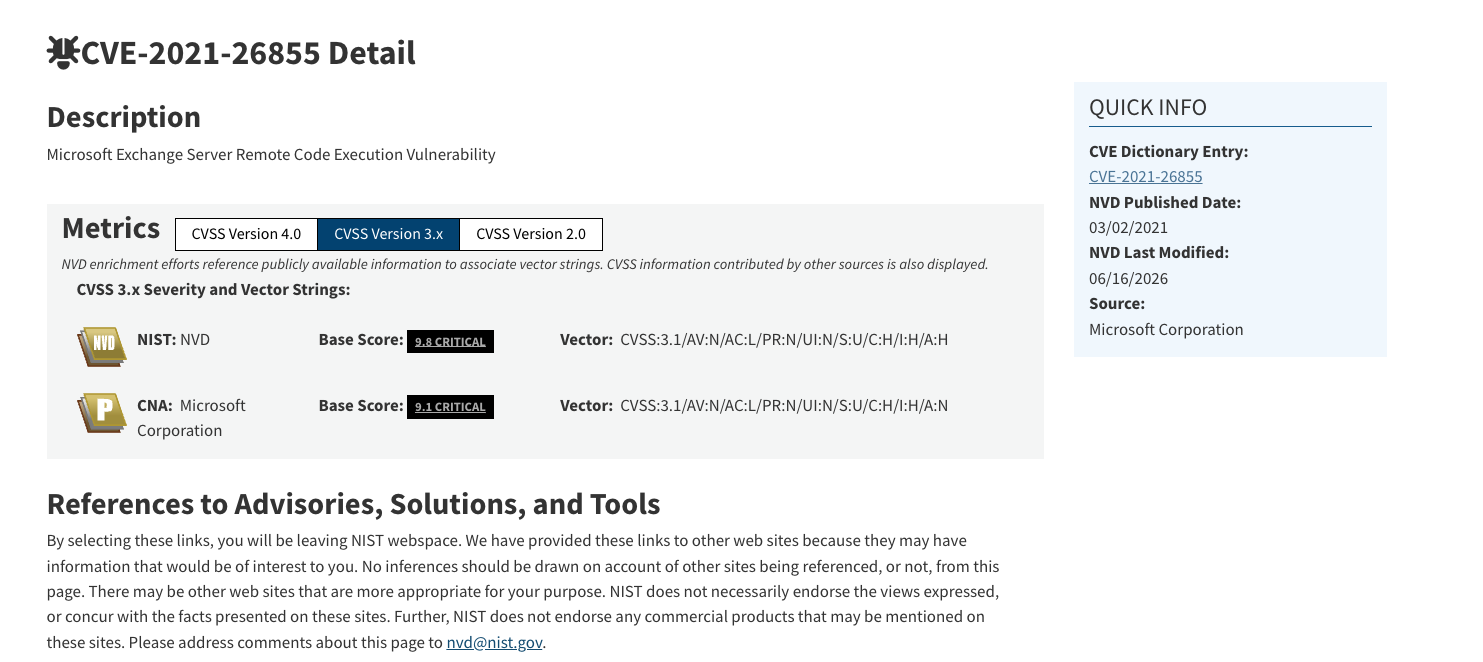 probablysecure/triage-cve-2021-26855-proxylogon---microsoft-exchange-
Hands-on CVE triage lab: analyze NVD entries, decode CVSS vectors, map CWE weaknesses, and contextualize risk for high-profile exploits like…
 haerin-l/poc_cve-2026-46716
Reproducible lab environment for CVE-2026-46716, a critical cross-tenant RCE in Nezha Monitoring via cron API authorization bypass. Includes Nuclei…
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 b-faller/cve-2025-65099
Proof-of-concept exploit for CVE-2025-65099 in Claude Code, demonstrating yarnPath and plugin techniques to achieve code execution in a controlled…
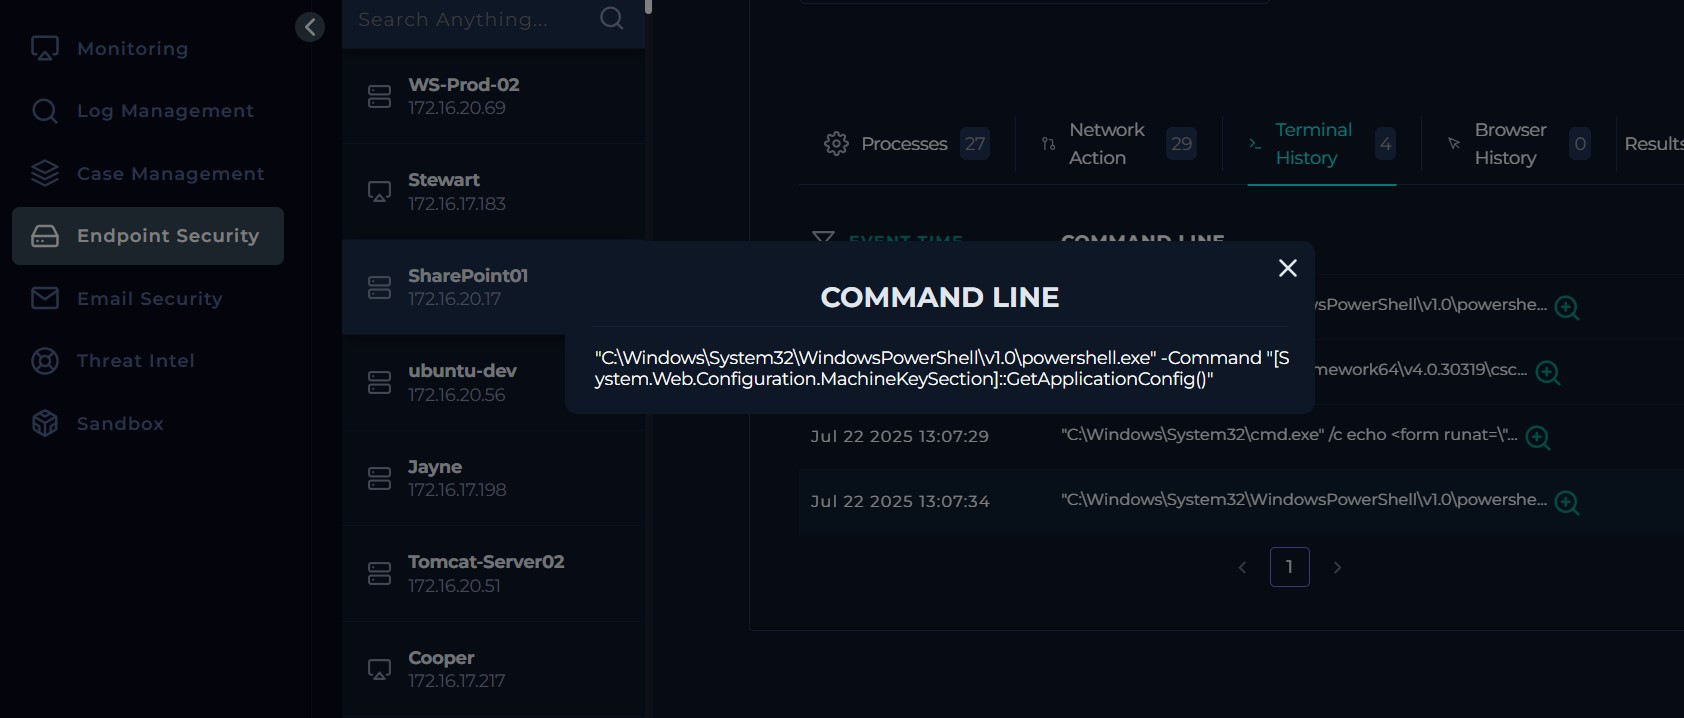 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…
 walidpyh/cve-2025-8088
Proof-of-concept demonstrating Alternate Data Stream (ADS) payload delivery via crafted WinRAR archives for educational research and controlled lab…
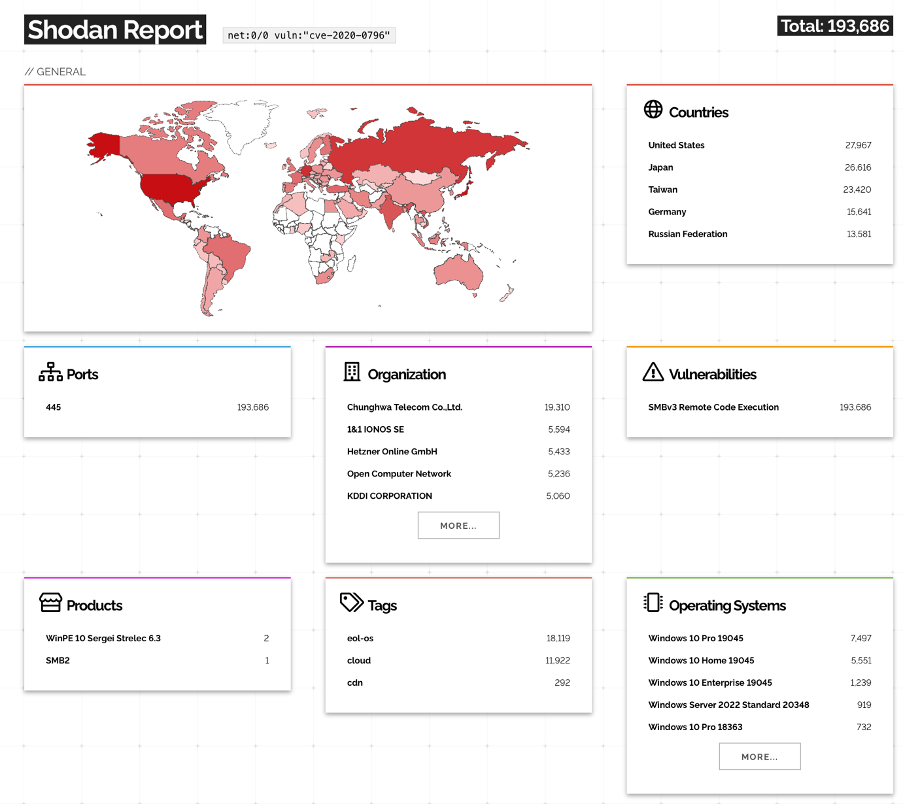 maqeel-git/cve-2020-0796
Analysis and ethical exploitation guide for CVE-2020-0796 (SMBGhost) SMBv3 vulnerability with technical details and practical attack plan.
 valeriot30/cve-2024-3094
A XZ backdoor vulnerability explained in details
 cybervixy/vulnerability-management
NGINX Security Hardening & Vulnerability Remediation Analysis of critical CVEs (CVE-2021-23017, HTTP/2 DoS flaws) in outdated NGINX versions, with…
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…