
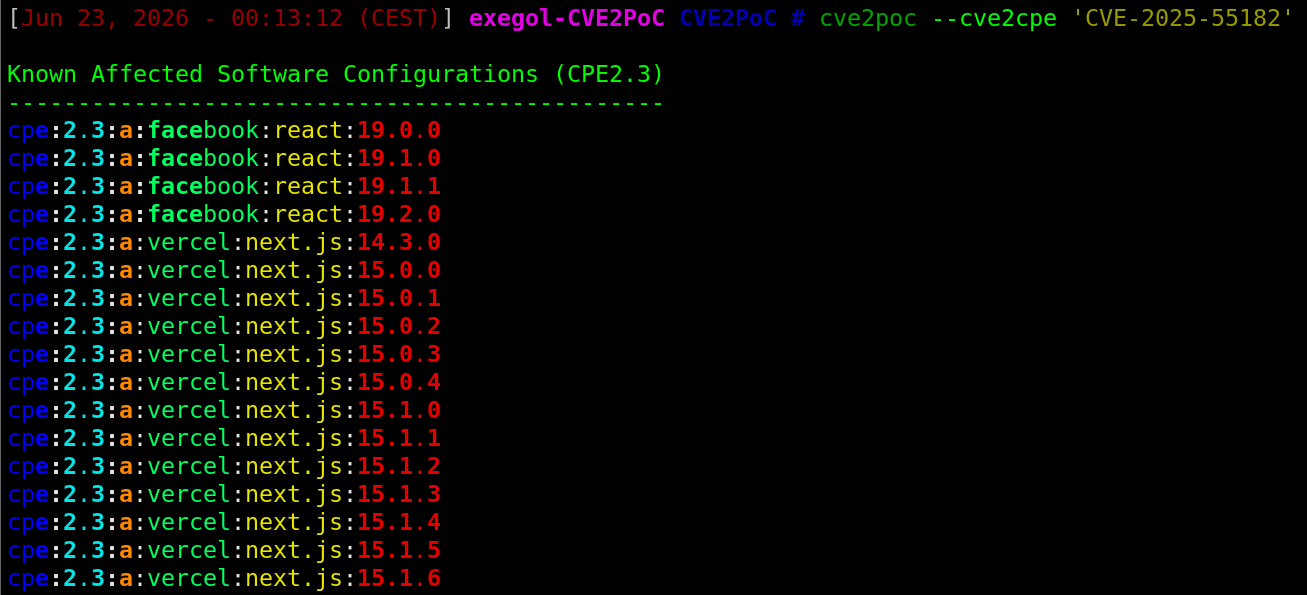
CVE2PoC
 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
educationexploitationinformation-gathering+5
145
0liverflow/cve2pocCVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 qazbnm456/awesome-web-security
🐶 A curated list of Web Security materials and resources.
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 abraxas/vbox-vmdk-sparse-extent
Oracle VM VirtualBox 7.2.20 - High - Local - File read - VMDK sparse FLAT extent path join
 abraxas/spark-connect-archive-fragment
Apache Spark 4.2.0 - High - Remote - File write - Connect archives hash-fragment dest
 abraxas/phpmyadmin-setup-validate
phpMyAdmin 5.2.3 - High - Remote - leftover - setup/validate still reachable
 abraxas/phpmyadmin-pmadb-central-sqli
phpMyAdmin 5.2.3 - High - Remote - SQLi - central columns pmadb query leftover
 abraxas/phpmyadmin-issuperuser
phpMyAdmin 5.2.3 - High - Remote - leftover - isSuperUser check skipped
 abraxas/phpmyadmin-vqb-xss
phpMyAdmin 5.2.3 - High - Remote - XSS - Designer Visual Query Builder
 abraxas/phpmyadmin-importldi
phpMyAdmin 5.2.3 - High - Remote - SQLi - ImportLdi TERMINATED BY leftover
 abraxas/phpmyadmin-csrf-sql
phpMyAdmin 5.2.3 - High - Remote - CSRF - token strip on /sql
 abraxas/openmeetings-chat-user-idor
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - dashboard chatTab-u{id} exports another users private chat
 abraxas/opencart-reward-free-checkout
Proof-of-concept exploit and lab for an OpenCart 4.1.0.4 reward points plus Free Checkout payment bypass, letting an authenticated customer keep…
 abraxas/n8n-function-vm2
Proof-of-concept and lab for an n8n 2.42.0 sandbox escape: hidden Function/FunctionItem nodes execute JS in the main process, giving authenticated…
 abraxas/moodle-grades-gradeitems
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_gradeitems lists hidden grade items
 abraxas/lighttpd-win32-dotdot-space
lighttpd 1.4.85 - High - Remote - Path - native Win32 GET /..%20/ reads outside document-root