
pentest-lab-metasploitable2
 danreis20/pentest-lab-metasploitable2
Laboratório de pentest em rede isolada: enumeração com nmap/nikto e exploração manual do Metasploitable2 (backdoor vsFTPd CVE-2011-2523, bindshell)…
ctfeducationexploitation+7
danreis20/pentest-lab-metasploitable2Laboratório de pentest em rede isolada: enumeração com nmap/nikto e exploração manual do Metasploitable2 (backdoor vsFTPd CVE-2011-2523, bindshell)…
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 momenbasel/htb-writeups
Structured collection of 500+ Hack The Box machine writeups, 400+ challenge solutions, and interactive learning tools including knowledge graphs,…
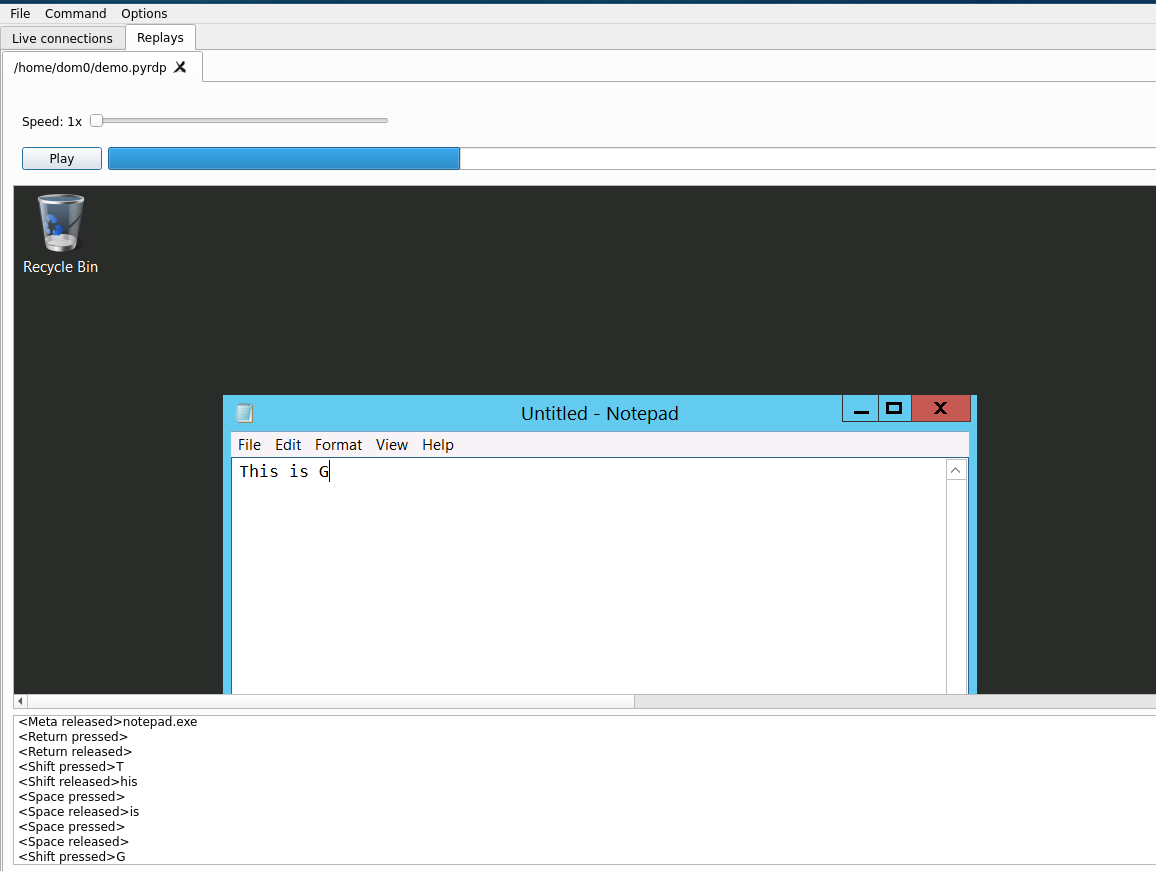 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 speatx/chamilolms-cve-2023-4220
CVE-2023-4220 — Unauthenticated file upload RCE in Chamilo LMS ≤ 1.11.24. OSCP-style and auto exploit.

 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 anlominus/bug-bounty
Bug Bounty ~ Awesomes | Books | Cheatsheets | Checklists | Tools | Wordlists | More
 devinliggins14/smb-pentest-exploiting-cve-2007-2447-on-metasploitable-2
Step-by-step penetration testing lab exploiting Samba CVE-2007-2447 on Metasploitable 2 using Metasploit, demonstrating root compromise, credential…
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters
 nahamsec/resources-for-beginner-bug-bounty-hunters
A list of resources for those interested in getting started in bug bounties