
athena
 athena-os/athena
Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
educationlabs-practicelearning-paths-courses+3
1.3k3 days ago
athena-os/athenaAthena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
 abraxas/pfsense-timezone-phpini
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - timezone php.ini prepend
 abraxas/cve-2026-75650
Disclosure pack and lab reproduction script for CVE-2026-75650, an unauthenticated SSTI RCE in Magento Open Source GraphQL email templates.
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
 learnerxuan/cve-2026-29057-poc
Docker-based lab reproducing CVE-2026-29057 Next.js request smuggling, comparing vulnerable 15.5.12 against patched 15.5.13 with a raw chunked HTTP…
 exdev994/cve-2026-90817
Python PoC for CVE-2026-90817, an unauthenticated REDCap RCE via survey passthrough routing and file-path injection, with a Docker lab and…
 mega-starmie/tomcat-cve-2025-24813-lab
Local reproduction lab for Apache Tomcat CVE-2025-24813, documenting exploitation conditions and AI-assisted verification of the vulnerability.
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
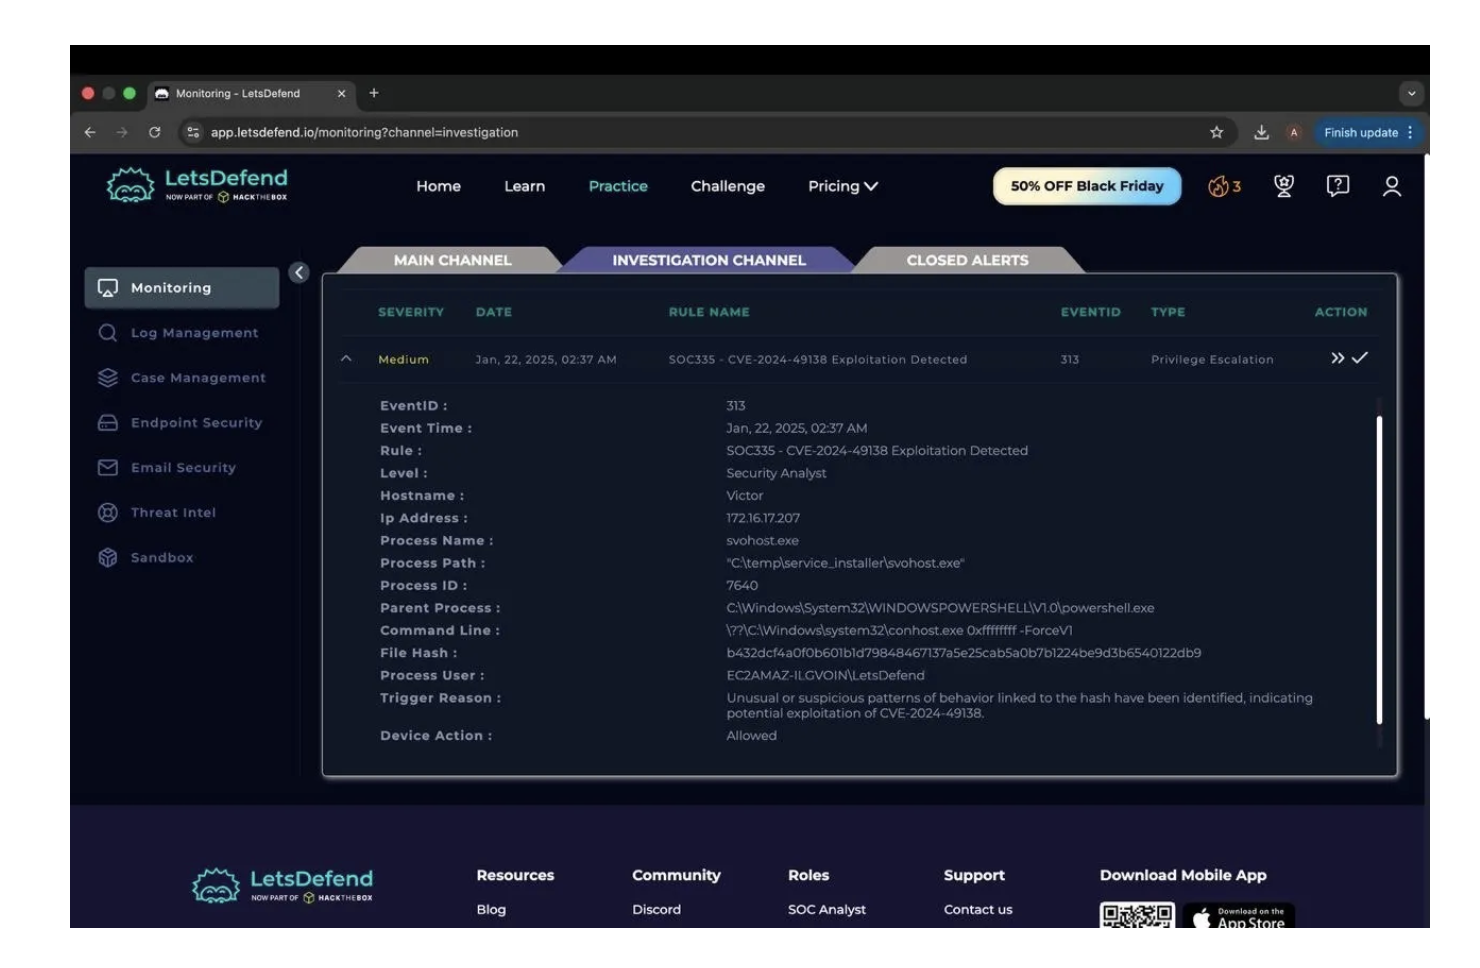 adisasoc/cve-2024-49138-soc-investigation
SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…
 lxxexxbxx/cve-2026-33017
PoC exploit for an unauthenticated RCE in Langflow <=1.8.1, including source-level root cause analysis, AST-aware reverse shell payload, Docker lab,…
 mr-destroyer/cve-2025-55182
Exploit for CVE-2025-55182 enabling remote code execution via prototype pollution in Next.js React Server Components, with command execution and…
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 superman-l/cve-2026-16723
Reproduces fastjson 1.2.83 @JSONType RCE with a vulnerable Spring Boot target and ASM-based payload generator using HTTP or file protocol jar chains.
 aykhan019/cve-2022-1471-jira-lab
Offline CVE-2022-1471 lab: SnakeYAML unsafe deserialization to RCE; compares vulnerable 1.x vs fixed 2.x using a harmless local payload.
 686f6c61/poc-geoleak-cve-2026-52715
PoC funcional de CVE-2026-52715 (GeoLeak): SQLi no autenticada en GEO my WordPress <= 4.5.5 via swlatlng/nelatlng. Laboratorio Docker + exploit…