
DeFiHackLabs
 sunweb3sec/defihacklabs
Reproduce DeFi hacked incidents using Foundry.
curated-resourcesdigital-forensicseducation+4
sunweb3sec/defihacklabsReproduce DeFi hacked incidents using Foundry.
 abraxas/vbox-guestctrl-copyfrom-dotdot
VirtualBox 7.2.20 - High - Local - File write - Guest Control copy-from DOTDOT
 abraxas/sqlite-xfer-auth
SQLite 3.53.4 - High - Local - Privilege leftover - INSERT SELECT xfer skips source READ
 abraxas/mysql-mysqlbinlog-raw-path
MySQL Community Server 26.7.0 - High - mysqlbinlog --raw Rotate path leftover - client file write
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 piecar21/cve-2026-0303
Proof-of-concept and Docker lab for CVE-2026-0303, demonstrating arbitrary code execution in Checkov via an auto-loaded .checkov.yml pointing to an…
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 suspicious Office documents on REMnux using oletools; one matched CVE-2017-11882, the other was inconclusive.
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 abraxas/vbox-ovf-href-dest-escape
VirtualBox 7.2.20 - High - Local - File write - OVF href dest escape
 abraxas/pfsense-api-enroll-json-ssh
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - example-add-devices.py JSON into SSH
 abraxas/opnsense-firmware-mirror-sed
OPNsense 26.7.6 - High - Remote - Privilege leftover - custom firmware mirror sed-skips pkg fingerprints
 abraxas/spark-history-store-path
Apache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID
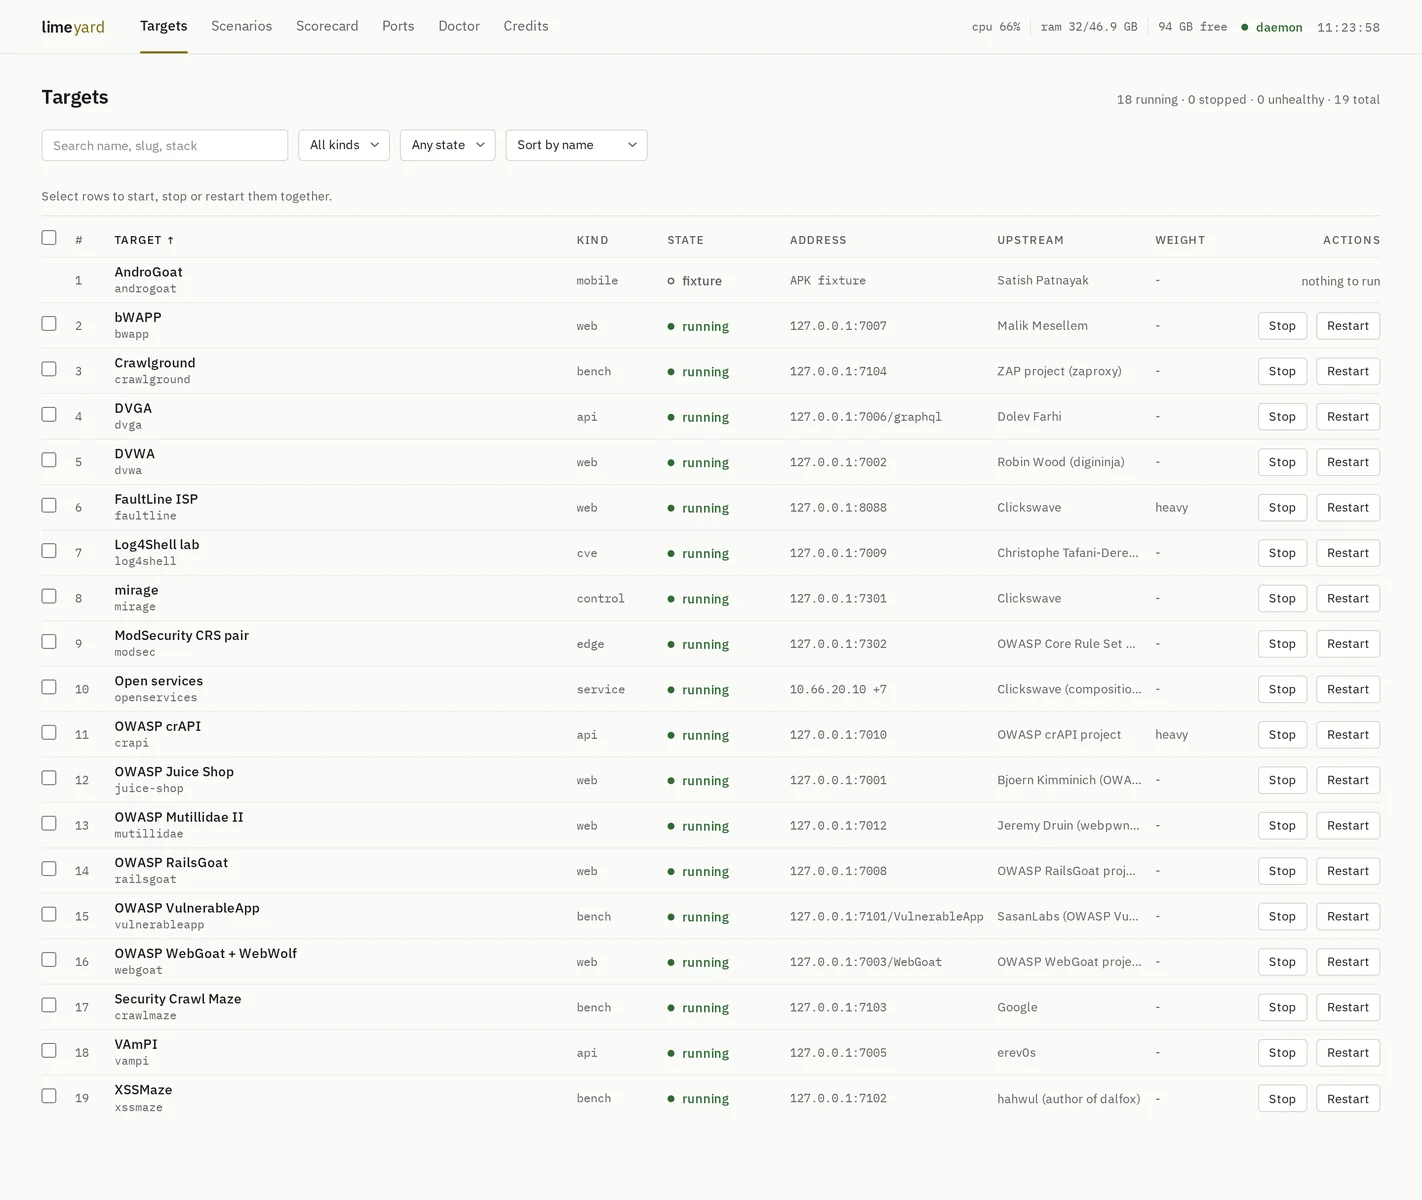 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 nth347/mediawiki-cve-2026-100382
Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…