
CVE-2025-54424
 hophtien/cve-2025-54424
CVE-2025-54424: 1Panel TLS client cert bypass enables RCE via forged CN 'panel_client' using a bundled scanning and exploitation tool. Affected: <=…
educationexploitationlabs-practice+3
hophtien/cve-2025-54424CVE-2025-54424: 1Panel TLS client cert bypass enables RCE via forged CN 'panel_client' using a bundled scanning and exploitation tool. Affected: <=…
 ashardev002/cve-2025-32463_chwoot
🔍 Demonstrate the CVE-2025-32463 privilege-escalation flaw in sudo's chroot feature with this minimal, reproducible proof of concept environment.
 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 abhaybansal16/cve-2025-55182-lab
Docker-based lab reproducing CVE-2025-55182 (React2Shell), an unauthenticated RCE in React Server Components Flight Protocol, with PoC exploit and…
 shivammittal2403/cve-2025-57819-freepbx-range
Isolated educational FreePBX-compatible cyber range for CVE-2025-57819 (CWE-89/CWE-288). Docker lab — not official Sangoma FreePBX.
 mega-starmie/tomcat-cve-2025-24813-lab
Local reproduction lab for Apache Tomcat CVE-2025-24813, documenting exploitation conditions and AI-assisted verification of the vulnerability.
 jailbreakdotparty/dirtyzero
Simple customization toolbox, utilizing CVE-2025-24203. Supports iOS 16.0 - iOS 18.3.2.
 ritinify/cve-2025-29927-poc
Proof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…
 mr-destroyer/cve-2025-55182
Exploit for CVE-2025-55182 enabling remote code execution via prototype pollution in Next.js React Server Components, with command execution and…
 mattiacervelli/cve-2025-24893_analysis
Self-contained Docker lab that reproduces CVE-2025-24893, an unauthenticated SSTI-to-RCE in XWiki SolrSearch, and compares vulnerable vs patched…
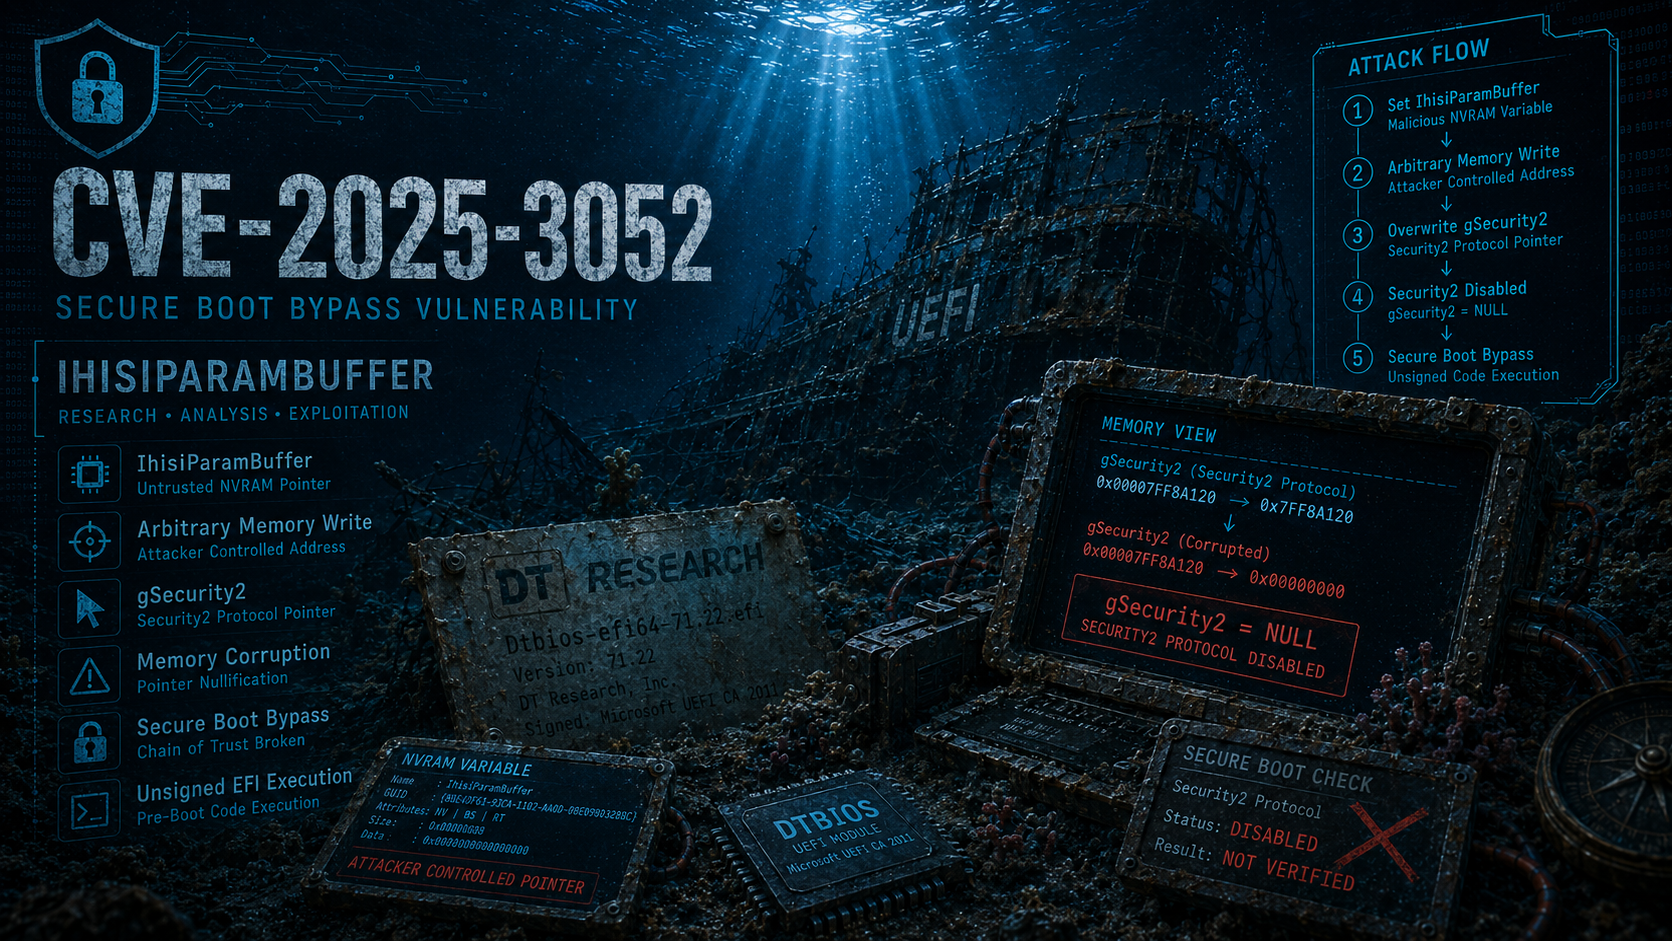 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
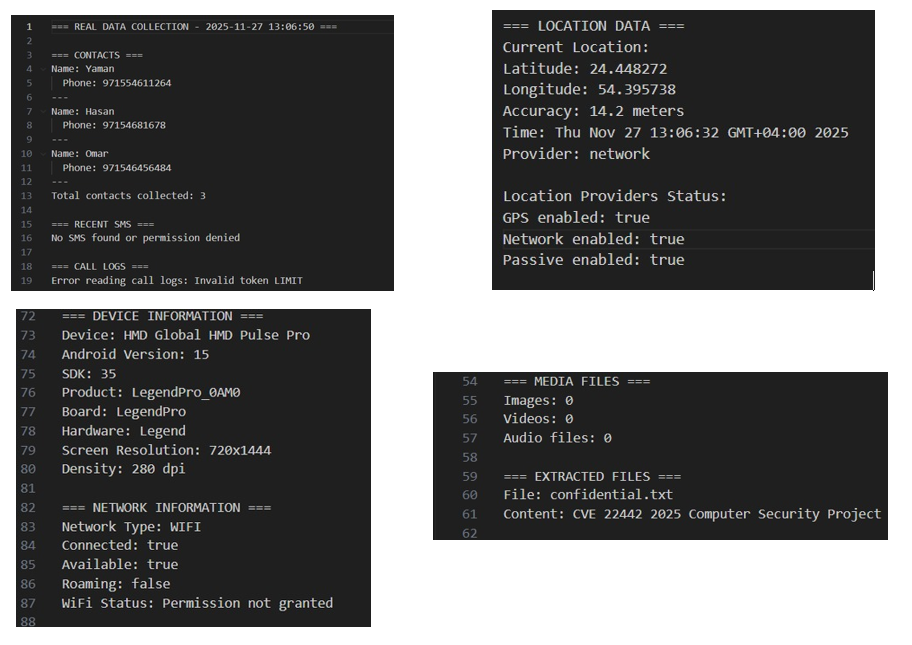 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 anusha-khan29/cve-2025-70149-sql-injection
Security research project — SQL Injection vulnerability exploitation and mitigation
 jtmh37/apache-tomcat-cve-2025-24813-lab
ICT279 Vulnerability Detection and Mitigation Project using CVE-2025-24813 in an Internet Banking Environment
 xdezen/cve-2025-8110
Python proof-of-concept for CVE-2025-8110, demonstrating arbitrary file write to RCE in Gogs via symlink and API, with educational lab usage.
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…