ULTIMATE-CYBERSECURITY-MASTER-GUIDE

This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

LazyWeb is a demonstration web application designed to showcase common server-side application vulnerabilities. Each vulnerability is categorized…

PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…

Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…

Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

A vulnerable version of Rails that follows the OWASP Top 10

Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…

Web and mobile application security training platform

Demonstration of the expression language (EL) injection vulnerability CVE-2018-14667 using the photoalbum lab under Jboss application server

The vulnerable application that will teach you how to hack WebSockets

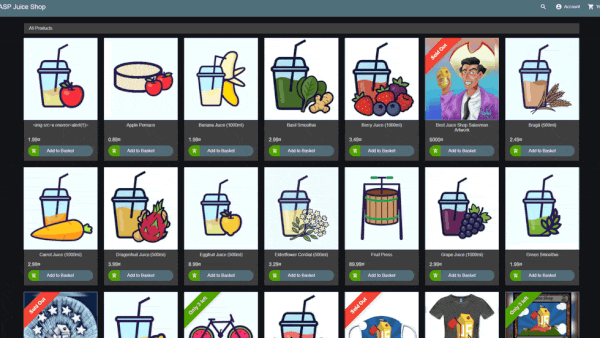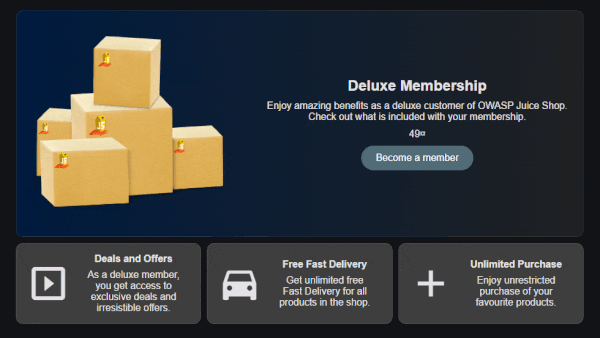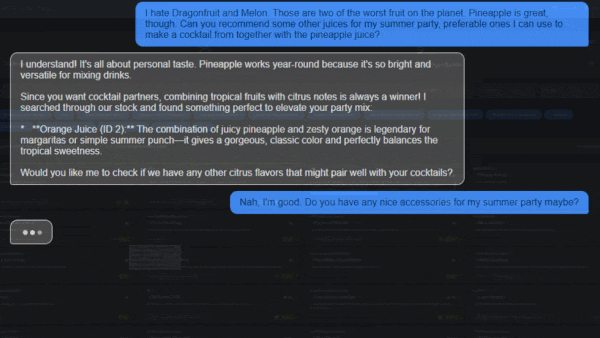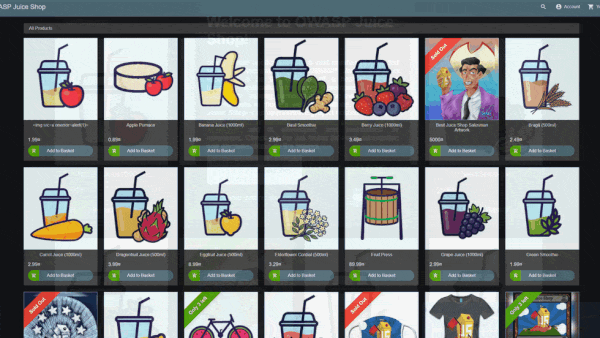
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…

Demonstrates a padding oracle attack against AES-CBC encryption using a vulnerable Flask decrypt endpoint and a Python exploit script to decrypt…

Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).

CVE Reproduction: cve-2026-0770-langflow_rce_reproduction

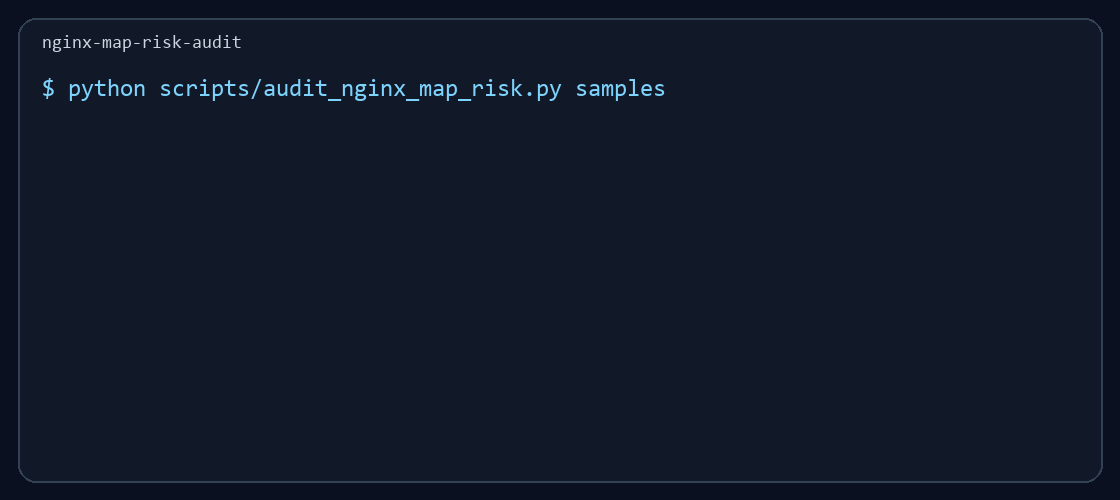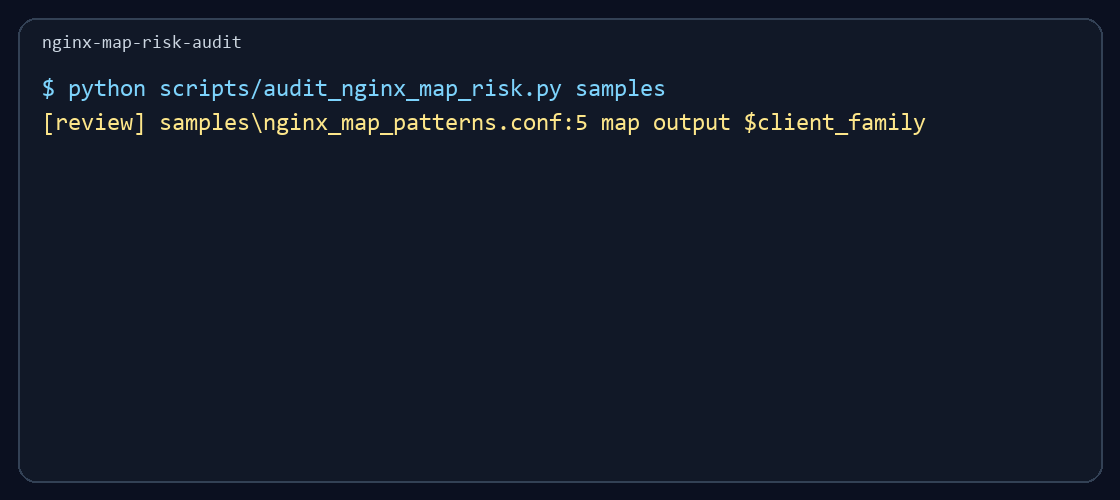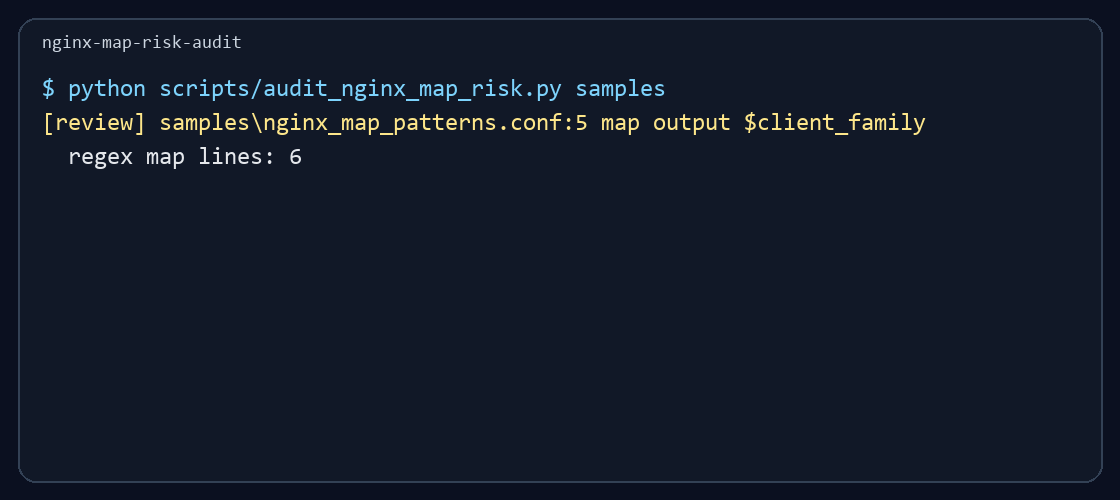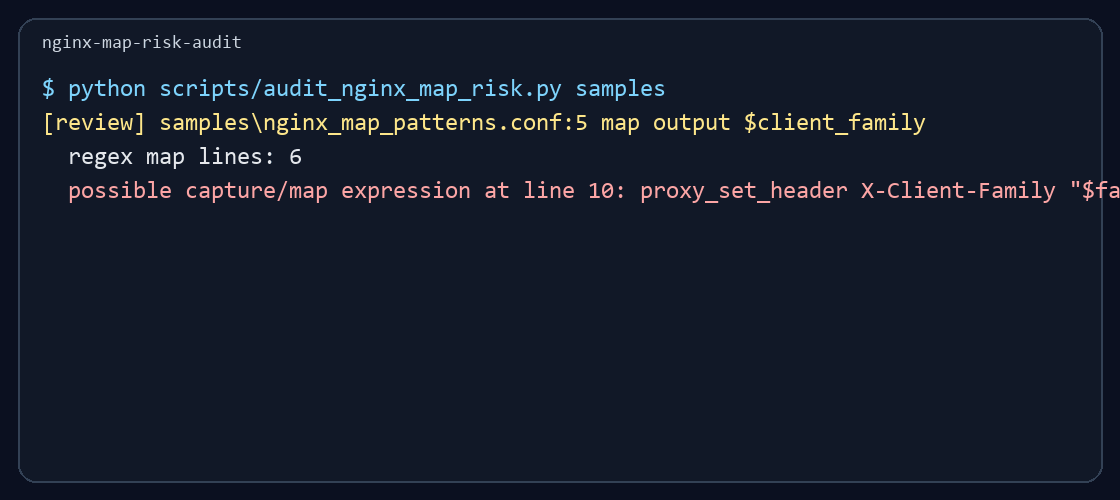
Defensive NGINX CVE-2026-42533 map regex risk audit with config scanner, Splunk/Defender notes, and lab evidence.

Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…

CTF challenge container with a Next.JS middleware vulnerability (CVE-2025-29927) for practicing man-in-the-middle attacks and API exploitation.