

Web-App-PenTesting
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
educationlabs-practicepenetration-testing+4
sarthak4126/web-app-pentestingWeb application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
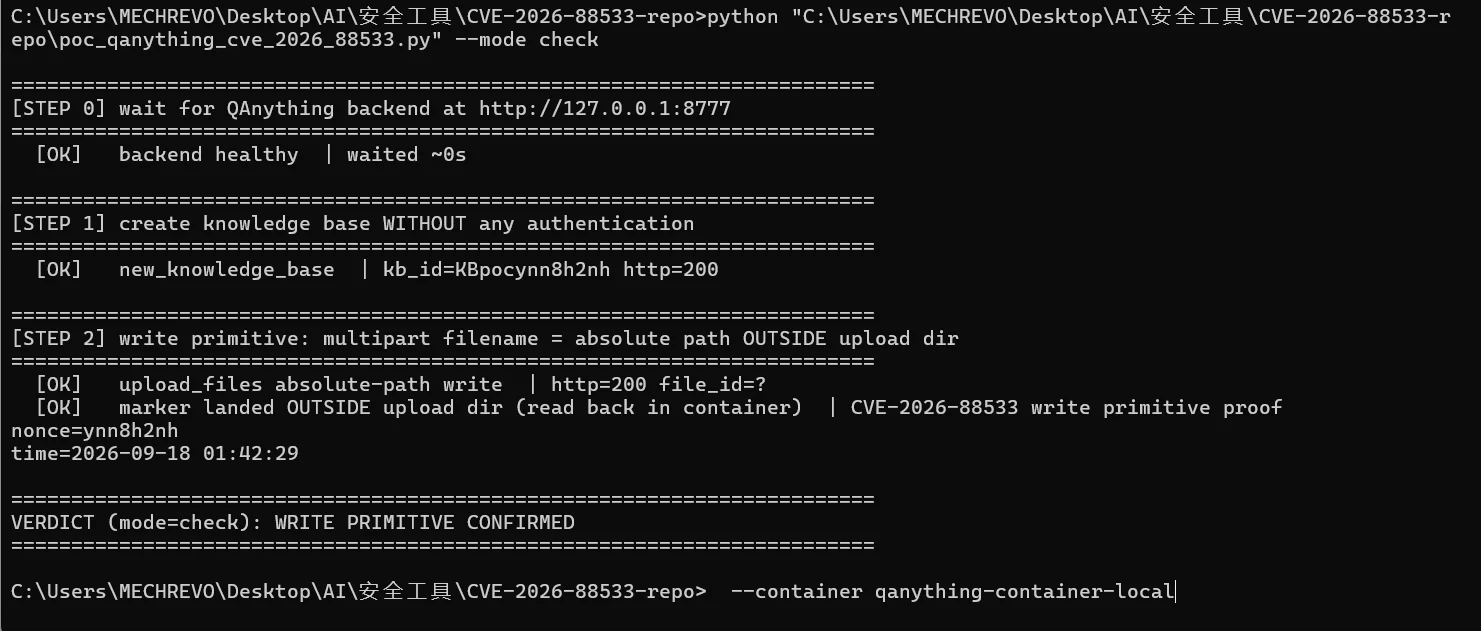 hemlock-lyk/cve-2026-88533
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…
 dinosn/cve-2026-32475-elementor-pro-lab
A/B Docker lab + PoC for CVE-2026-32475 (Elementor Pro Forms unauthenticated arbitrary file upload -> RCE via validation/move loop desync)
 k0nnect/cve-2026-21440-writeup-poc
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing
 nullwhisper/cve-2026-14282
GoDAM WordPress plugin <= 1.12.2 unauthenticated file upload RCE (CVE-2026-14282)
 imbas007/cve-2026-63223-poc
CVE-2026-63223 PoC — CodeIgniter 4 is_image/mime_in File Upload RCE (CVSS 9.8). Unauthenticated remote code execution via unrestricted file upload…
 hurrrraaaa/cve-2021-21972
Isolated lab research writeup for VMware vCenter Server CVE-2021-21972, covering unauthenticated arbitrary file upload to RCE, Nmap-based detection,…
 halilkirazkaya/cve-2026-1357
CVE-2026-1357 — WPvivid Backup & Migration ≤ 0.9.123 Unauthenticated RCE Exploit
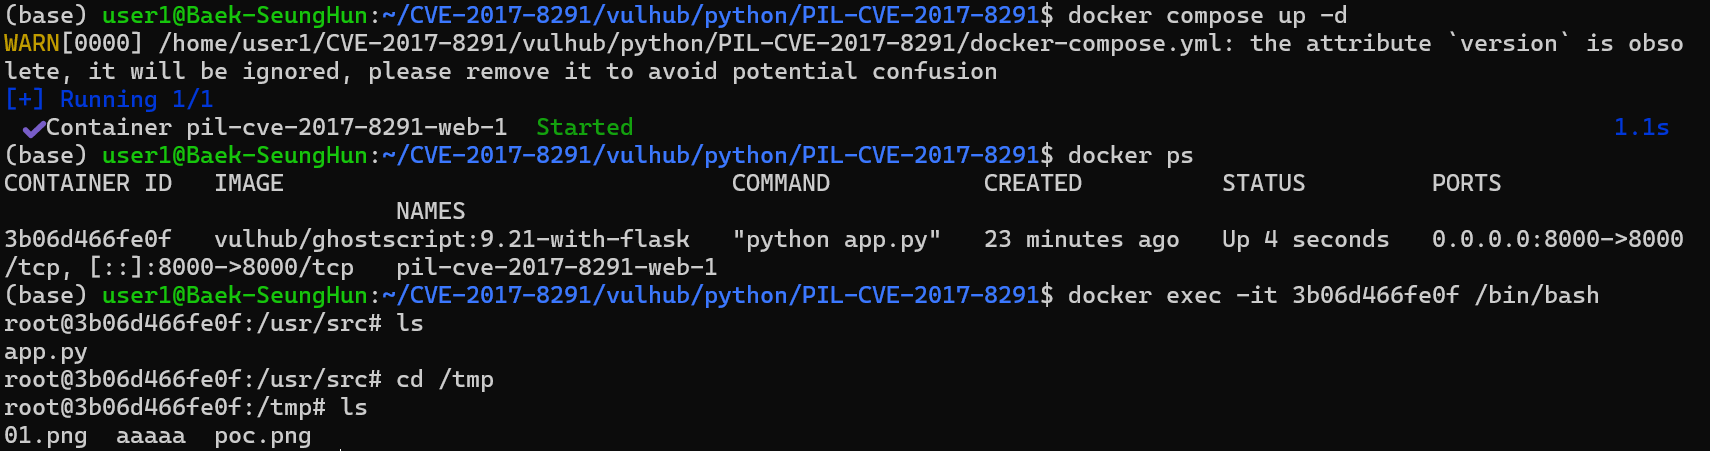 shun1403/pil-cve-2017-8291-study
Educational lab demonstrating CVE-2017-8291 (PIL/GhostScript RCE) via crafted EPS file upload with PNG extension, including Docker setup and PoC…
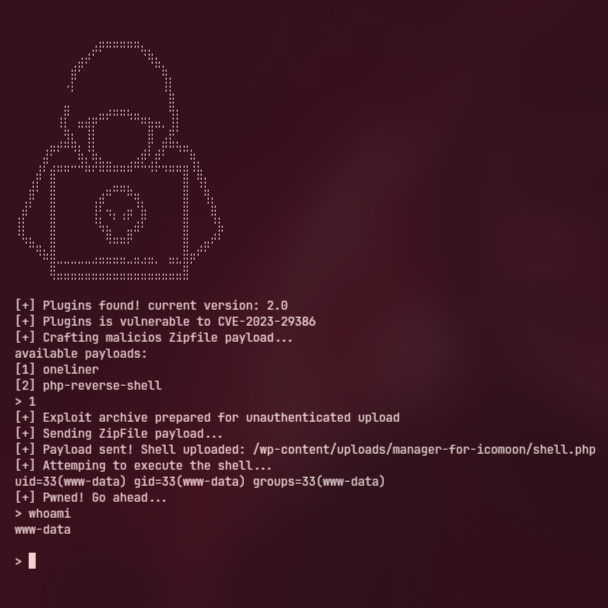 vigilante-1337/cve-2023-29386
PoC CVE-2023-29386 — Manager for Icomoon < 2.1 - Unauthenticated Arbitrary File Upload
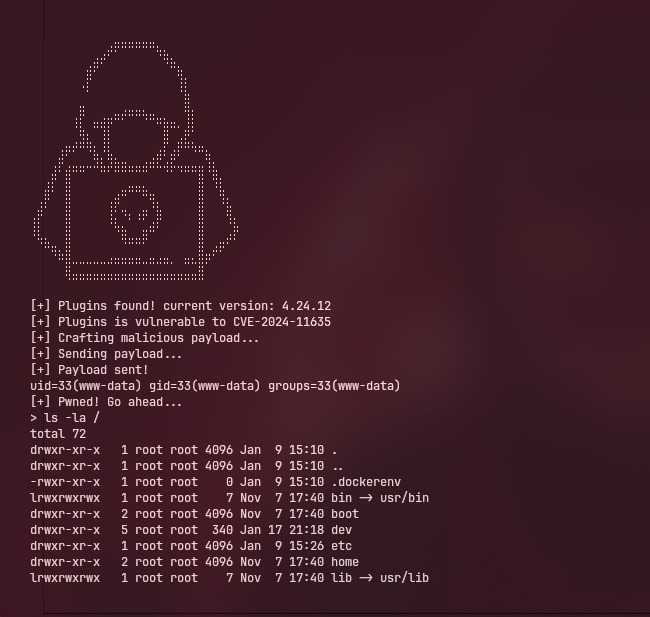 vigilante-1337/cve-2024-11635
The WordPress File Upload plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 4.24.12 via the…
 lingchul/cve_poc_test
PoC exploit for CVE-2019-13086 targeting SQL injection and file upload vulnerabilities in CSZ CMS. Includes experimental setup and reproduction code…
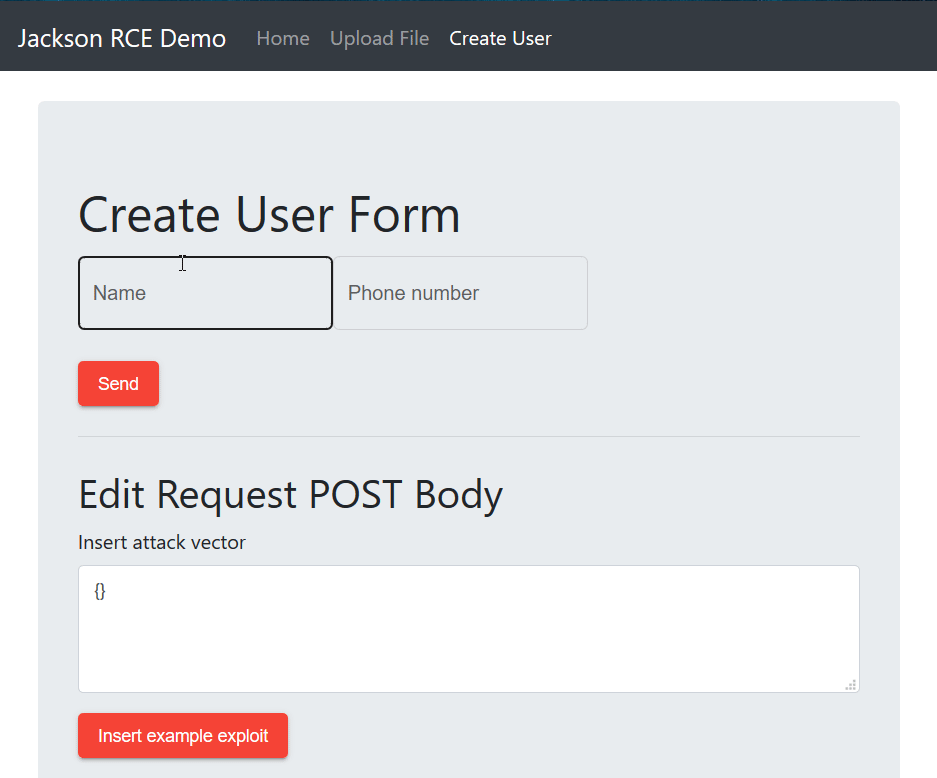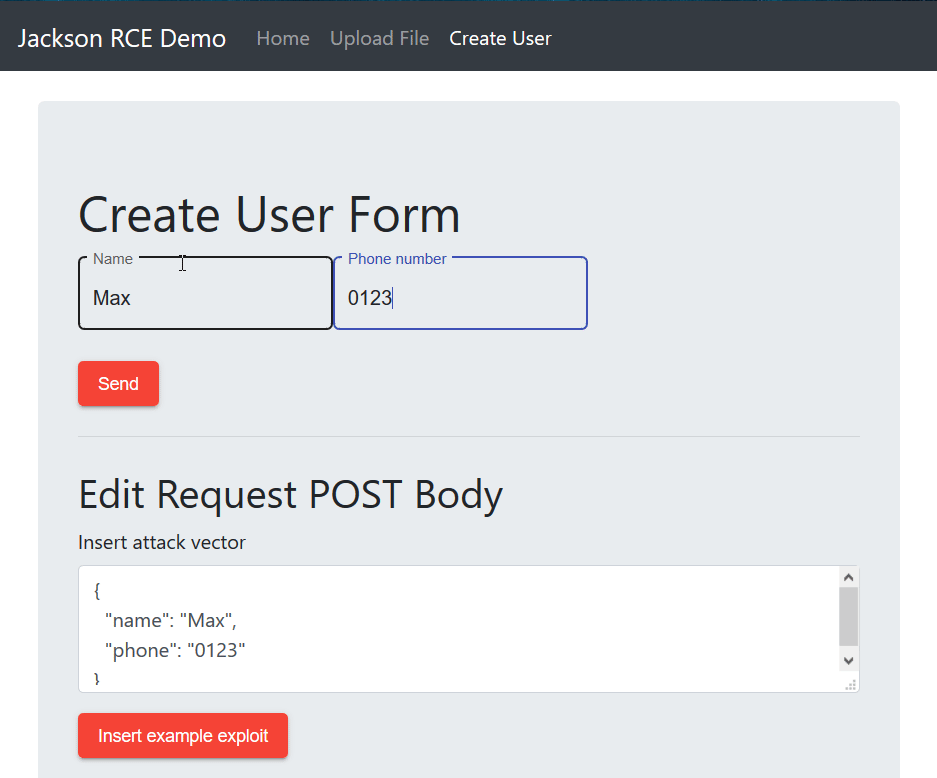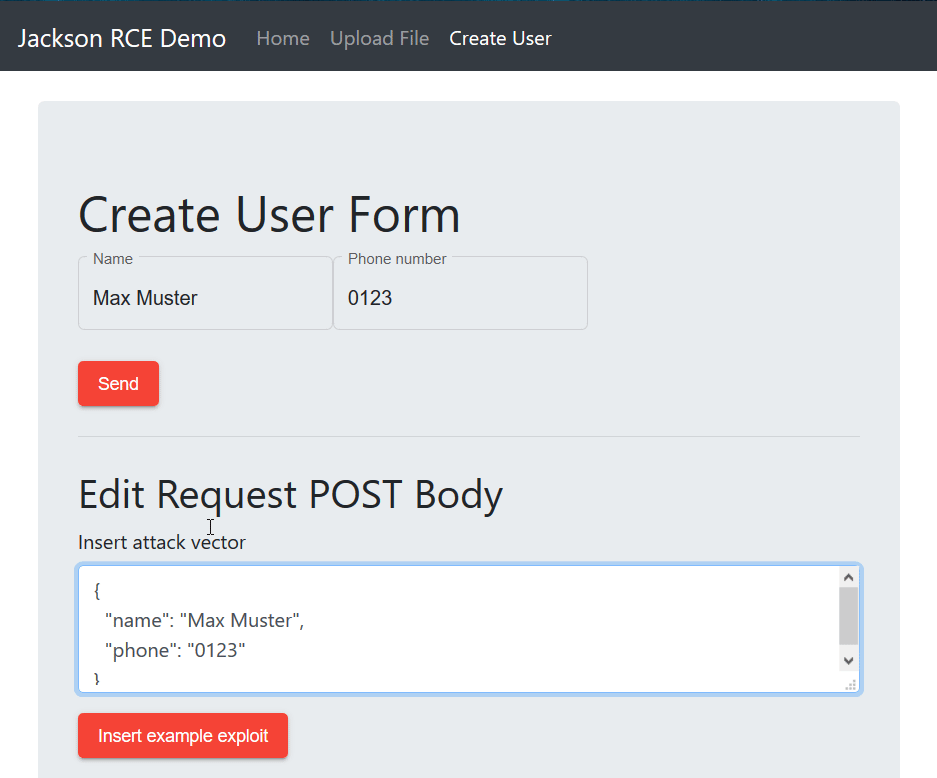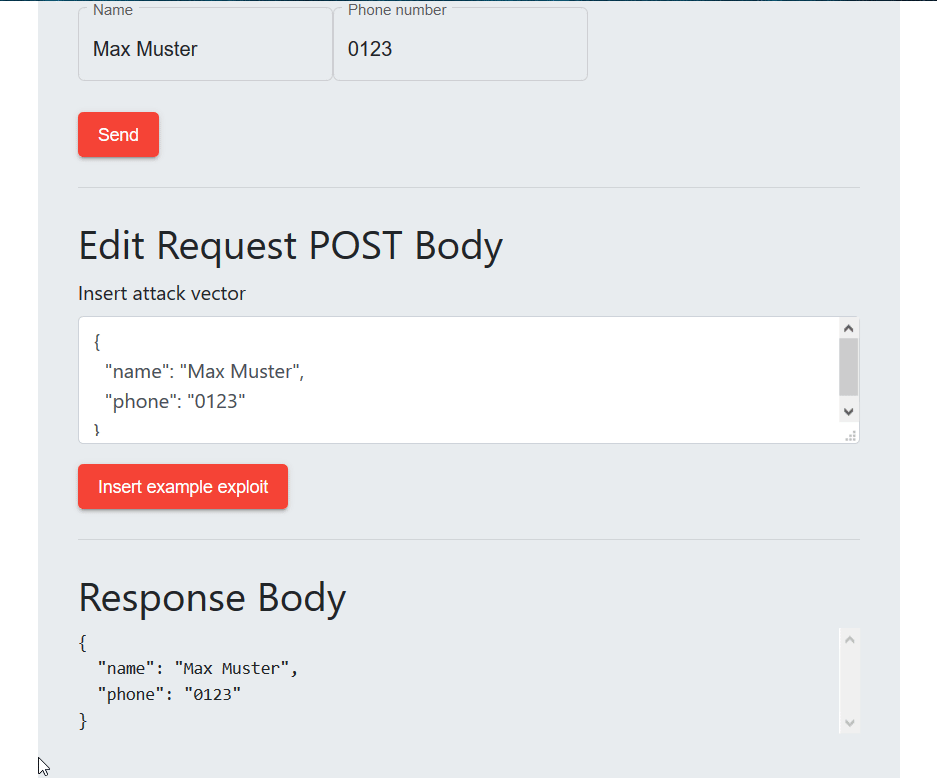 javanxd/demo-exploit-jackson-rce
Exploiting CVE-2017-7525 demo project with Angular7 frontend and Spring.
 imbios/lab-cve-2025-3515
CVE-2025-3515 WordPress lab for Drag and Drop Multiple File Upload for CF7: Dockerized PoC & Nuclei testing
 imbios/lab-cve-2016-15042
CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1
 rootdirective-sec/cve-2026-5718-lab
Local Docker lab demonstrating CVE-2026-5718 arbitrary file upload in a WordPress plugin, with vulnerable and patched services for side-by-side…
 rootdirective-sec/cve-2026-3844-lab
Local Docker lab for reproducing CVE-2026-3844, an unauthenticated arbitrary file upload to RCE in the WordPress Breeze Cache plugin. Compares…