
CVE-2026-87902
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
exploitationlabs-practicepenetration-testing+5
3
vulpecuna/cve-2026-87902Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 zsxen/cve-2025-1974
Windows 11-first educational lab for studying CVE-2025-1974 in ingress-nginx. Provides safe attack emulation and defense validation with local…
 penguincabinet/cve-2024-4367-hands-on
Hands-on lab to learn CVE-2024-4367 (Firefox PDF.js RCE) with PoC generation, vulnerable browser launch, and patched version verification.
 ninedeadeyes/s.p.a.r.k--standard-python-ascii-rpg-kit-
Light Weight 2d Ascii RPG Python Game Engine
 guillaume-risch/cve-2023-29357-sharepoint
Proof-of-concept exploit for CVE-2023-29357 targeting SharePoint, with automated Vagrant lab environment for testing and education.
 mkirahmet/poc-2023-43208
A proof-of-concept exploit for CVE-2023-43208, a remote code execution vulnerability in Mirth Connect before version 4.4.1.
 shun1403/cve-2017-8291
Docker-based lab demonstrating CVE-2017-8291 (GhostButt) exploitation via Python PIL/Pillow EPS image processing, with a vulnerable web application…
 daniilorchikov/pil-cve-2017-8291
Educational PoC for CVE-2017-8291 (GhostButt) demonstrating remote command execution via Python PIL/Pillow EPS image processing with GhostScript…
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 b-abderrahmane/cve-2021-44228-playground
Docker-based lab to validate CVE-2021-44228 (Log4Shell) in Java apps, test mitigations, and simulate RCE via LDAP and HTTP payloads.
 fuchiuebusi-lab/nginx-ui-cve-2026-42221-cve-2026-42238-
Docker-based lab environment to verify and exploit two unauthenticated API vulnerabilities (CVE-2026-42221, CVE-2026-42238) in nginx-ui, with patched…
 speatx/chamilolms-cve-2023-4220
CVE-2023-4220 — Unauthenticated file upload RCE in Chamilo LMS ≤ 1.11.24. OSCP-style and auto exploit.
 0xless/cve-2022-44900-demo-lab
Demo webapp vulnerable to CVE-2022-44900
 ckrielle/cve-2019-16784-poc
A Proof of Concept exploit for the PyInstaller CVE-2019-16783
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
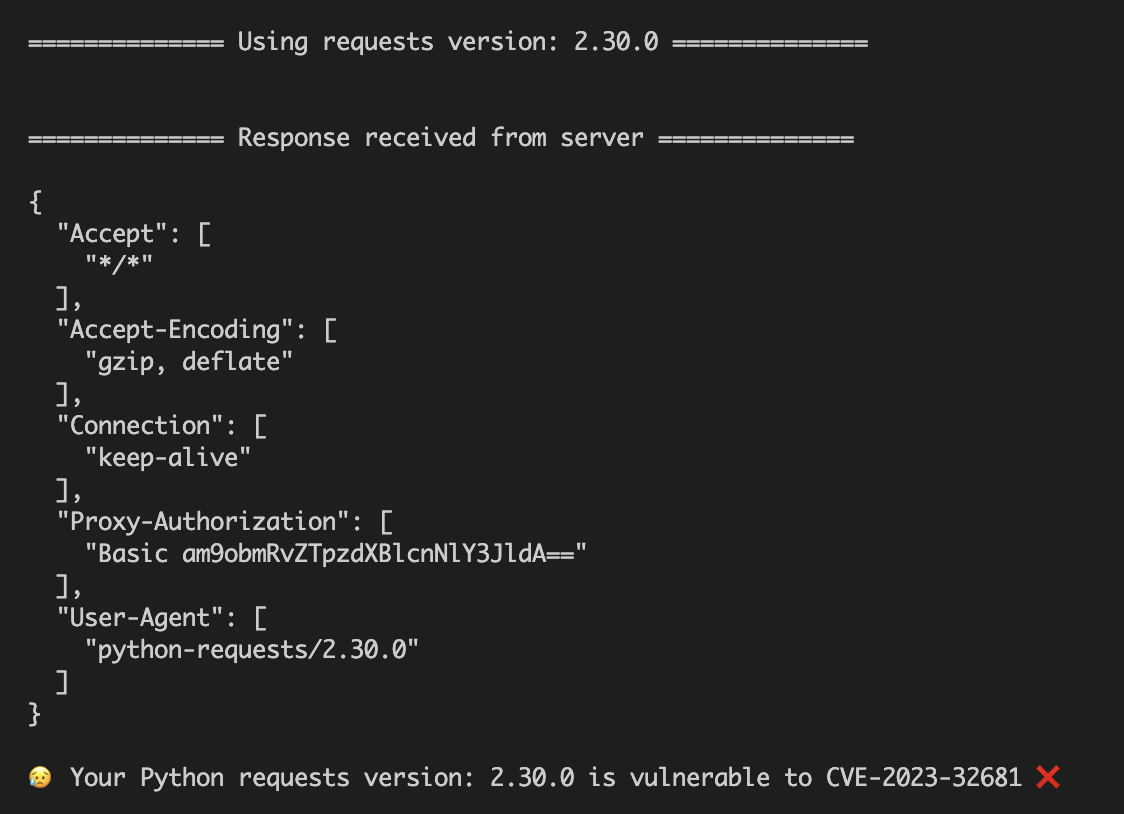 hardikmodha/poc-cve-2023-32681
POC for the CVE-2023-32681